
HashcatRosetta
 bandrel/hashcatrosetta
Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
ai-securityeducationhash-analysis+4
7
bandrel/hashcatrosettaHashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
 cylock11/cve-list
A collection of CVE exploits, including Python PoCs and README files with instructions for reproducing and exploiting each vulnerability.
 vudangducminh/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel race condition enabling unprivileged writes to read-only files and privilege…
 pvharmo2/gha-lab-d14c91f1bb
Security-research lab: reproduction of CVE-2025-58371 (GitHub Actions command injection via PR title in Discord PR Notifier), snapshot of…
 tcollins-hashicorp/vault-cve-2026-5006-audit
Audit and educational toolkit for CVE-2026-5006, a Vault templated-policy slash-injection vulnerability. Includes a read-only audit script generating…
 minhhk68/cve-2026-12513
Technical advisory and proof-of-concept for CVE-2026-12513, an unauthenticated arbitrary file deletion via path traversal in Shared Files WordPress…
 saykino/cve-2025-56218
Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…
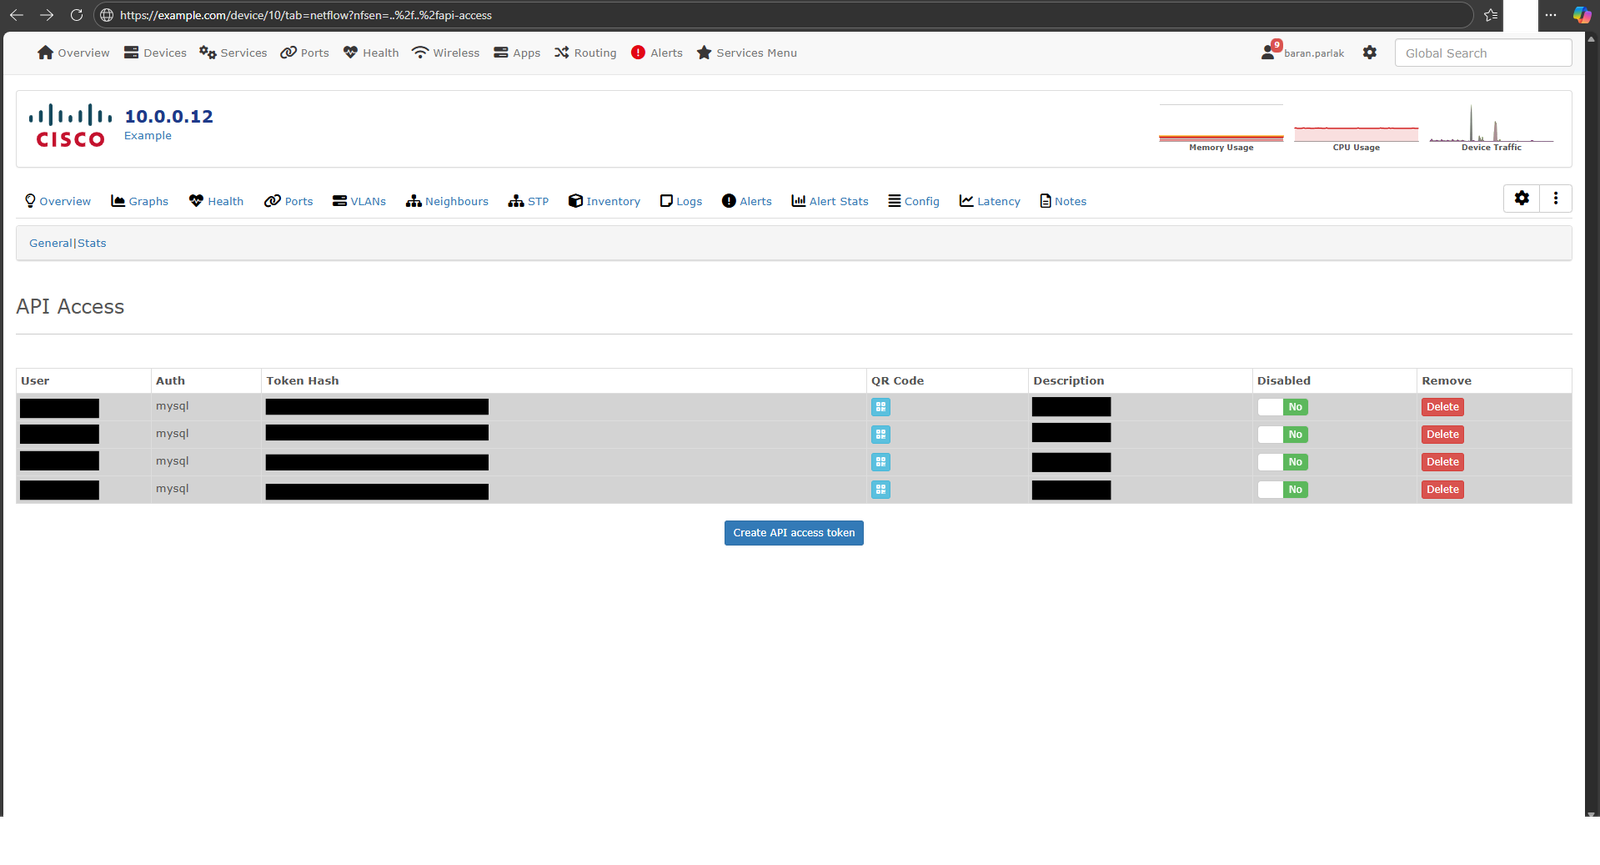 parlakbarann/cve-2026-30480
Proof-of-concept for CVE-2026-30480, a Local File Inclusion vulnerability in LibreNMS NFSen module, demonstrating path traversal to include arbitrary…
 mksundaram69/cve-2024-34102
Proof-of-concept exploit for CVE-2024-34102, a critical XML entity injection in Magento, enabling exfiltration of sensitive files and unauthorized…
 k0nnect/cve-2026-21440-writeup-poc
poc and writeup for cve-2026-21440: a critical path traversal vulnerability in @adonisjs/bodyparser allowing arbitrary file writing
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
 cnf409/cve-2026-34036
Proof-of-concept script demonstrating an authenticated local file inclusion (LFI) vulnerability in Dolibarr via the objectdesc parameter, allowing…
 alpinine/cve-2026-1312-testing
Reproduction environment for CVE-2026-1312 with Docker-based setup and automated execution script for vulnerability testing and analysis.
 alexb616/weblate-cve-2026-24126
Proof-of-concept exploit for CVE-2026-24126, an arbitrary file read in Weblate via SSH host argument injection, allowing authenticated admins to read…
 mkway/cve-2026-3304
Reproduction lab for CVE-2026-3304, a Multer async fileFilter race condition causing disk exhaustion via orphaned temp files. Includes vulnerable and…
 lyesh4ck/cve-2025-8081-elementor
Proof-of-concept exploit for CVE-2025-8081, an arbitrary file read in Elementor WordPress plugin, allowing authenticated admins to read sensitive…
 george0papasotiriou/cve-2026-22187-bio-formats-unsafe-java-deserialization-via-.bfmemo
Bio-Formats ≤ 8.3.0 performs unsafe Java deserialization of attacker-controlled .bfmemo cache files during image processing; crafted .bfmemo can…
 haomin-yu/cve-2024-13176-timing-analysis
Instrumented analysis and reproducibility materials for ECDSA timing leakage in OpenSSL CVE-2024-13176