

AgentStalker
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
ai-securitycode-analysisdynamic-analysis-sandboxing+7
132
gach0ng/agentstalkerEnd-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
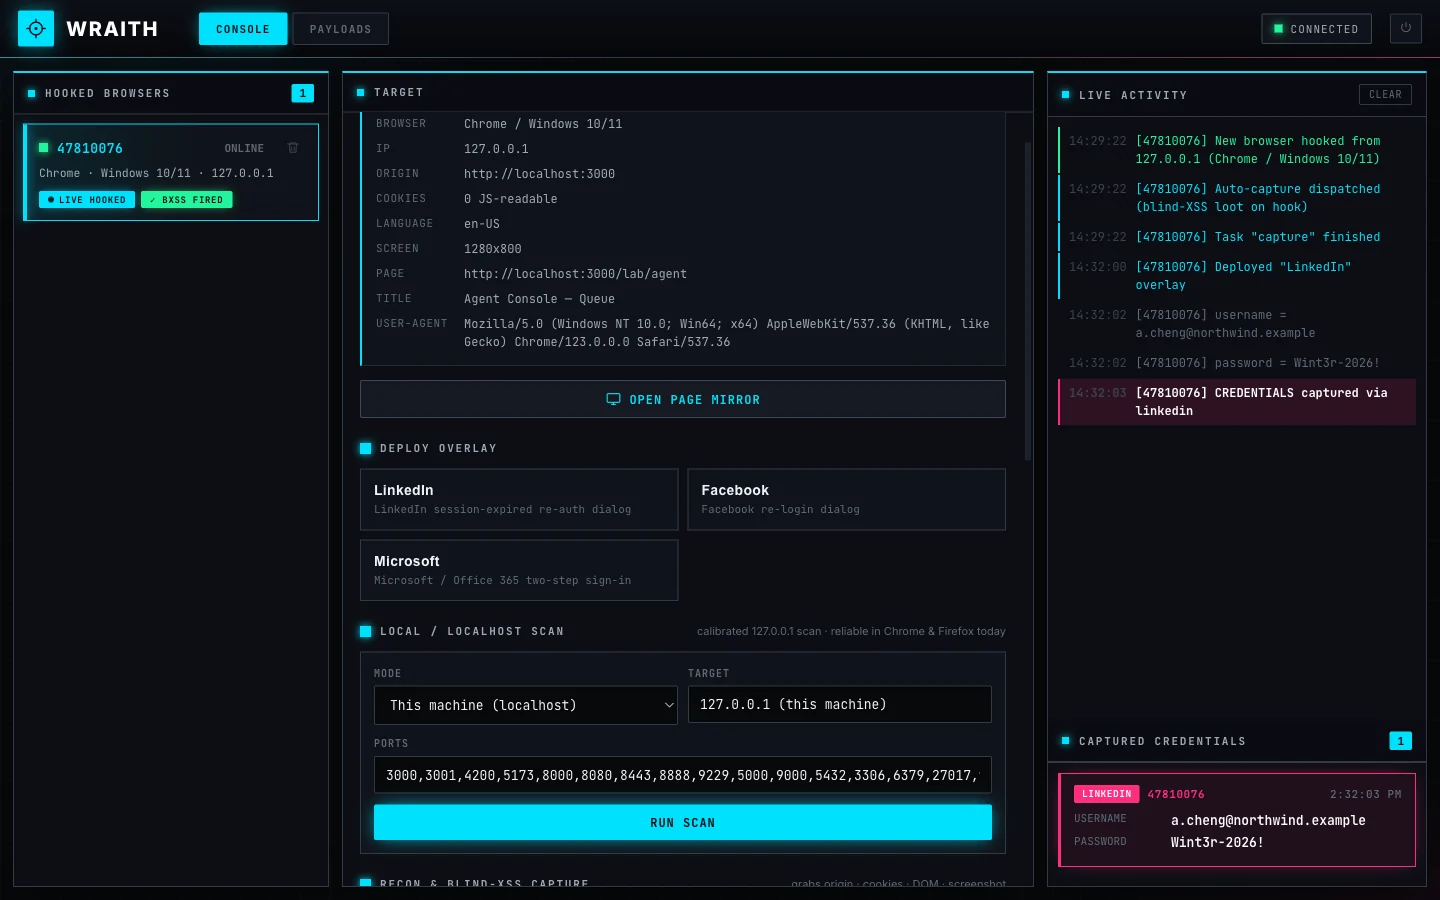 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 joaovicdev/exploit-cve-2024-7804
Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
 redpack-kr/ashwesker-cve-2026-21440
Proof-of-concept exploit for CVE-2026-21440, a critical path traversal in AdonisJS multipart uploads enabling arbitrary file write and remote code…
 pl4tyz/cve-2026-33701-unsafe-deserialization-in-opentelemetry-java-agent-rmi-instrumentation
Technical analysis of CVE-2026-33701, an unsafe deserialization vulnerability in OpenTelemetry Java Agent RMI instrumentation, including exploit…
 adriangigliotti/cve-2026-666
Educational proof-of-concept for CVE-2026-666, a remote code execution vulnerability in ShadowWeb Framework's deserialization, with technical details…
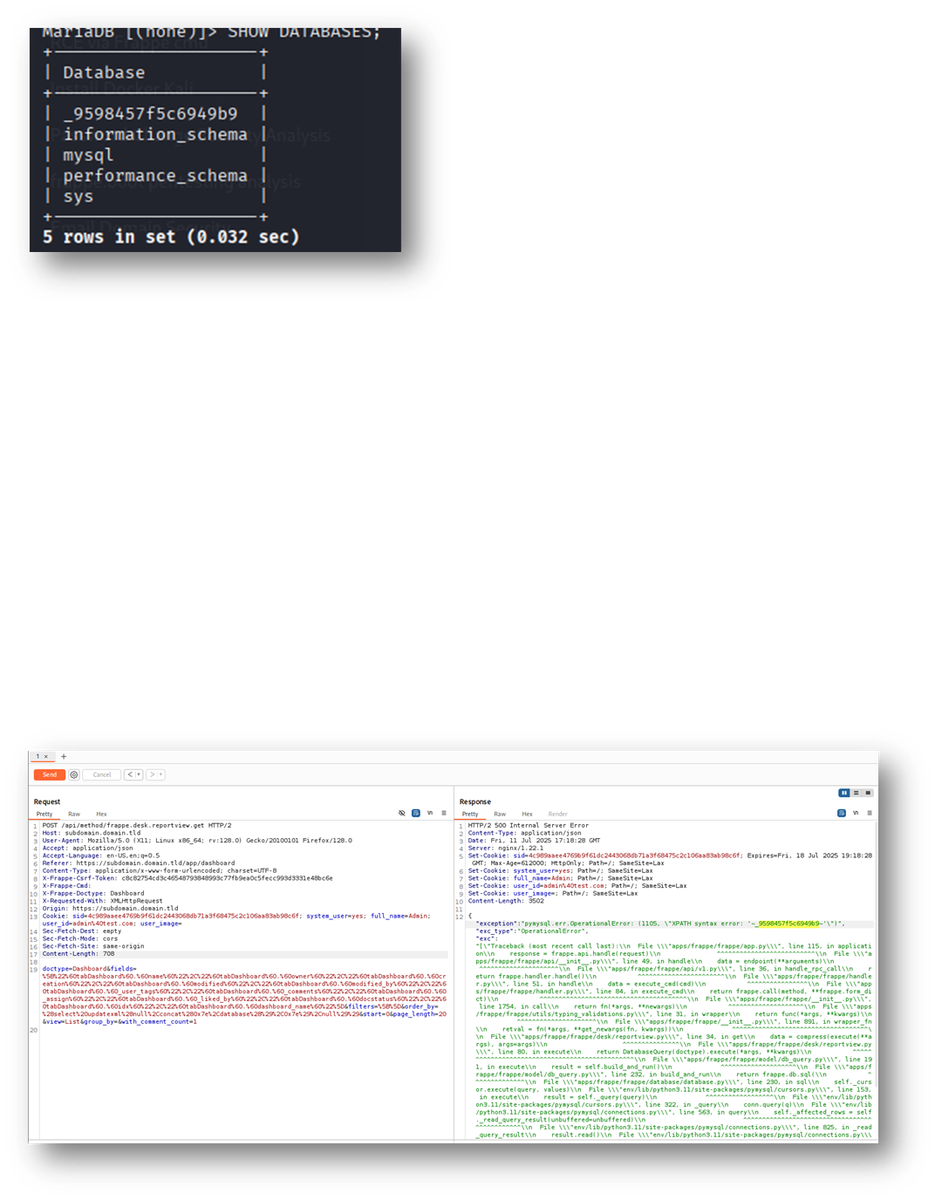 moalali/cve-2025-56381
ERPNEXT v15.67.0 was discovered to contain multiple SQL injection vulnerabilities in the /api/method/frappe.desk.reportview.get endpoint via the…
 pulentoski/cve-2026-31431
Modular framework for researching and exploiting a Linux kernel privilege escalation vulnerability using AF_ALG and page cache injection to modify…
 gmh5225/aether-c2-framework
🛠️ Explore custom C2 TTPs with Aether-C2-Framework, focusing on lightweight Rust implants and stealthy transport stacks to reduce forensic…
 p0dalirius/awesome-rce-techniques
Awesome list of step by step techniques to achieve Remote Code Execution on various apps!
 smokeme/airstrike
Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
 george0papasotiriou/cve-2026-21011-log4j-style-jndi-injection-in-custom-logger-simulated-
Simulates CVE-2026-21011, a Log4j-style JNDI injection in a custom logger: parses ${jndi:...} patterns and demonstrates LDAP-triggered remote code…
 math-x-io/cve-2024-54152
PoC exploit for Angular Expressions sandbox escape (CVE-2024-54152) achieving RCE via malicious expression. Includes Docker environment and payload…
 bw3ll/jop_rocket
This framework enables user to discover JOP gagdets and can automate building a complete JOP chain to bypass DEP. JOP ROCKET is the ultimate solution…
 eqstlab/cve-2026-34220
SQL Injection vulnerability in MikroORM