
CVE-2026-70376
 ilhomjonr/cve-2026-70376
Advisory and Python PoC for Pluck CMS CSRF: fail-open Referer check plus double-extension upload enables webshell deployment and remote code…
educationexploitationpenetration-testing+3
ilhomjonr/cve-2026-70376Advisory and Python PoC for Pluck CMS CSRF: fail-open Referer check plus double-extension upload enables webshell deployment and remote code…
 iltosec/chyrp-lite-rce-poc
CVE-2026-53767 + CVE-2026-53768 - Authenticated RCE in Chyrp Lite ≤ 2026.01 via uploads_path blocklist bypass and missing extension validation
 hunt-benito/e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout
PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…
 george0papasotiriou/cve-2026-4040-race-condition-in-file-upload-leading-to-rce
Reproduces CVE-2026-4040: Flask upload server with TOCTOU race condition and exploit script demonstrating arbitrary remote code execution.
 ywh-jfellus/cve-2026-65761
Proof of Concept for CVE-2026-65761 - EasyStore Pro Unauthenticated SQL Injection via `filter_sortby`
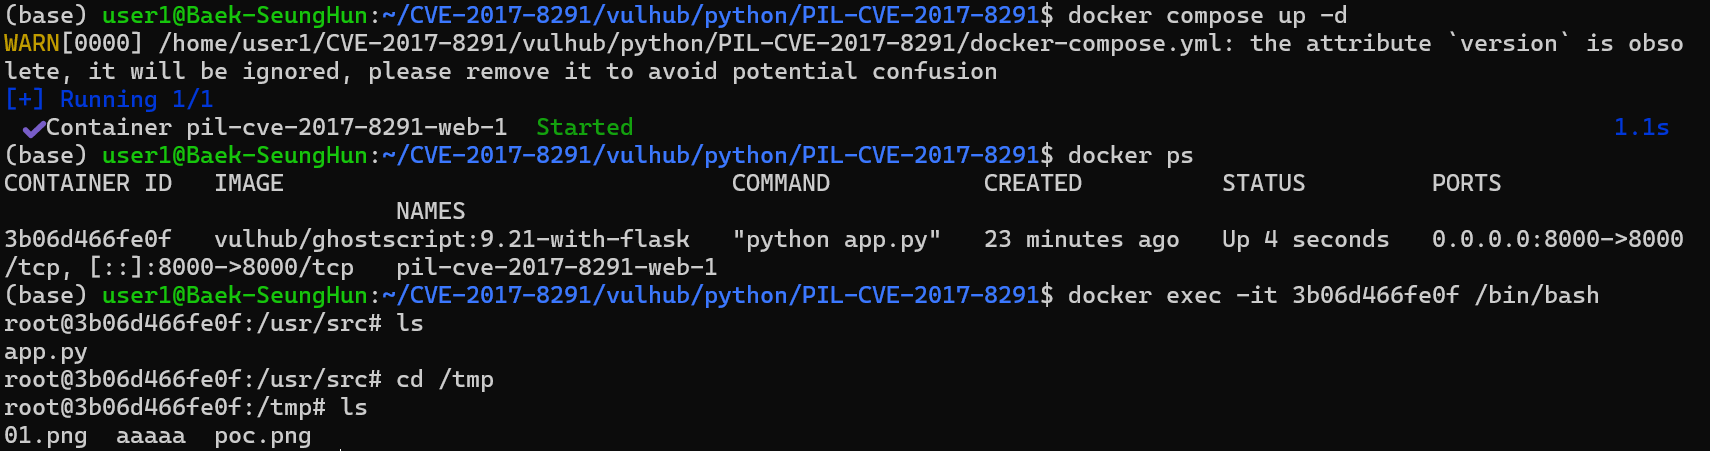 shun1403/pil-cve-2017-8291-study
Educational lab demonstrating CVE-2017-8291 (PIL/GhostScript RCE) via crafted EPS file upload with PNG extension, including Docker setup and PoC…
 xxconi/cve-2026-46275
Python exploit for CVE-2026-46725, achieving unauthenticated remote code execution in TYPO3 ceselector extension via PHP object injection and Monolog…
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 xiaopeng-ye/react2shell-detector
A Chrome extension for detecting React2Shell vulnerabilities (CVE-2025-55182 & CVE-2025-66478) in web applications
 sho-luv/react2shell
CVE-2025-55182 security test kit: CLI scanner + Chrome extension + Nuclei templates + Docker lab.
 e1tex/python-cve-2020-25213
Python Interactive Exploit for WP File Manager Vulnerability. The File Manager (wp-file-manager) plugin before 6.9 for WordPress allows remote…

 ywh-jfellus/cve-2026-48907
PoC for CVE-2026-48907 - Joomla! JCE extension < 2.9.99.5 unauthenticated RCE
 k3ystr0k3r/cve-2026-48907
CVE-2026-48907 – Joomla JCE Unauthenticated Remote Code Execution (RCE)
 shinthink/cve-2026-13001
Podlove Podcast Publisher Unauthenticated File Upload RCE via is_image() vs extract_file_extension() Mismatch | CVSS 9.8
 exerrdev/cve-2024-9264-fixed
Fixed proof-of-concept exploit for CVE-2024-9264, a critical Grafana RCE via DuckDB SQL expressions. Executes reverse shell using corrected shellfs…
 mishra0230/cve-2023-38831
CVE-2023-38831 - WinRAR