

Awesome-WAF
 0xinfection/awesome-waf
Everything about Web Application Firewalls (WAFs) from Security Standpoint! 🔥
curated-resourceseducationwaf-bypass+1
7.6k1 month ago
0xinfection/awesome-wafEverything about Web Application Firewalls (WAFs) from Security Standpoint! 🔥
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 mr-xn/burpsuite-collections
有关burpsuite的插件(非商店),文章以及使用技巧的收集(此项目不再提供burpsuite破解文件,如需要请在博客mrxn.net下载)---Collection of burpsuite plugins (non-stores), articles and tips for using…
 fa-pengfei/ngwaf
First iteration of ML based Feedback WAF
 hulh122/cve-2025-55182
Detailed technical analysis and proof-of-concept exploit for CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol. Covers path…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
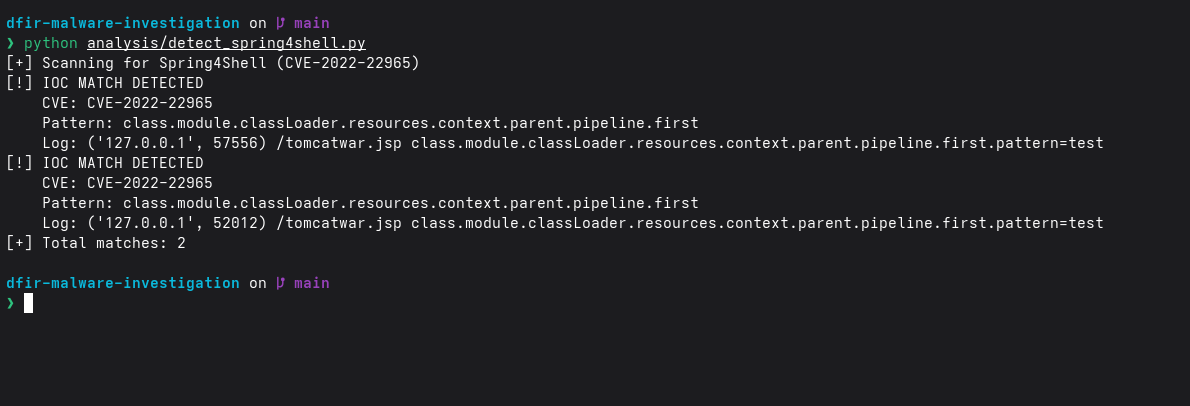 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 puliczek/cve-2021-44228-poc-log4j-bypass-words
🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks
 ceh-aditya-raj/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, demonstrating unauthenticated RCE in Next.js App Router via server-side object injection in React Server…
 acharaf06/cve-2017-5638-attack-and-defense
Docker-based security lab demonstrating Apache Struts2 S2-045 (CVE-2017-5638) exploitation and defense, featuring vulnerable and patched applications…
 jas502n/log4j2-cve-2021-44228
CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…
 moeinfatehi/xss_vulnerability_challenges
Dockerized PHP application providing hands-on XSS vulnerability challenges and bypass examples, including WAF, blacklist, and JavaScript validation…
 cybertechajju/cve-2025-55184-poc-expolit
Professional-grade Denial of Service (DoS) exploitation framework for CVE-2025-55184 targeting React Server Components. Features 8 attack modes, WAF…
 nithylesh/web-application-firewall-
This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…
 sahmsec/cve-2026-1357
Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration leading to remote code execution.…