awesome-linux-attack-forensics-purplelabs

This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.

This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.

Azazel is a userland rootkit based off of the original LD_PRELOAD technique from Jynx rootkit. It is more robust and has additional features, and…

eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…

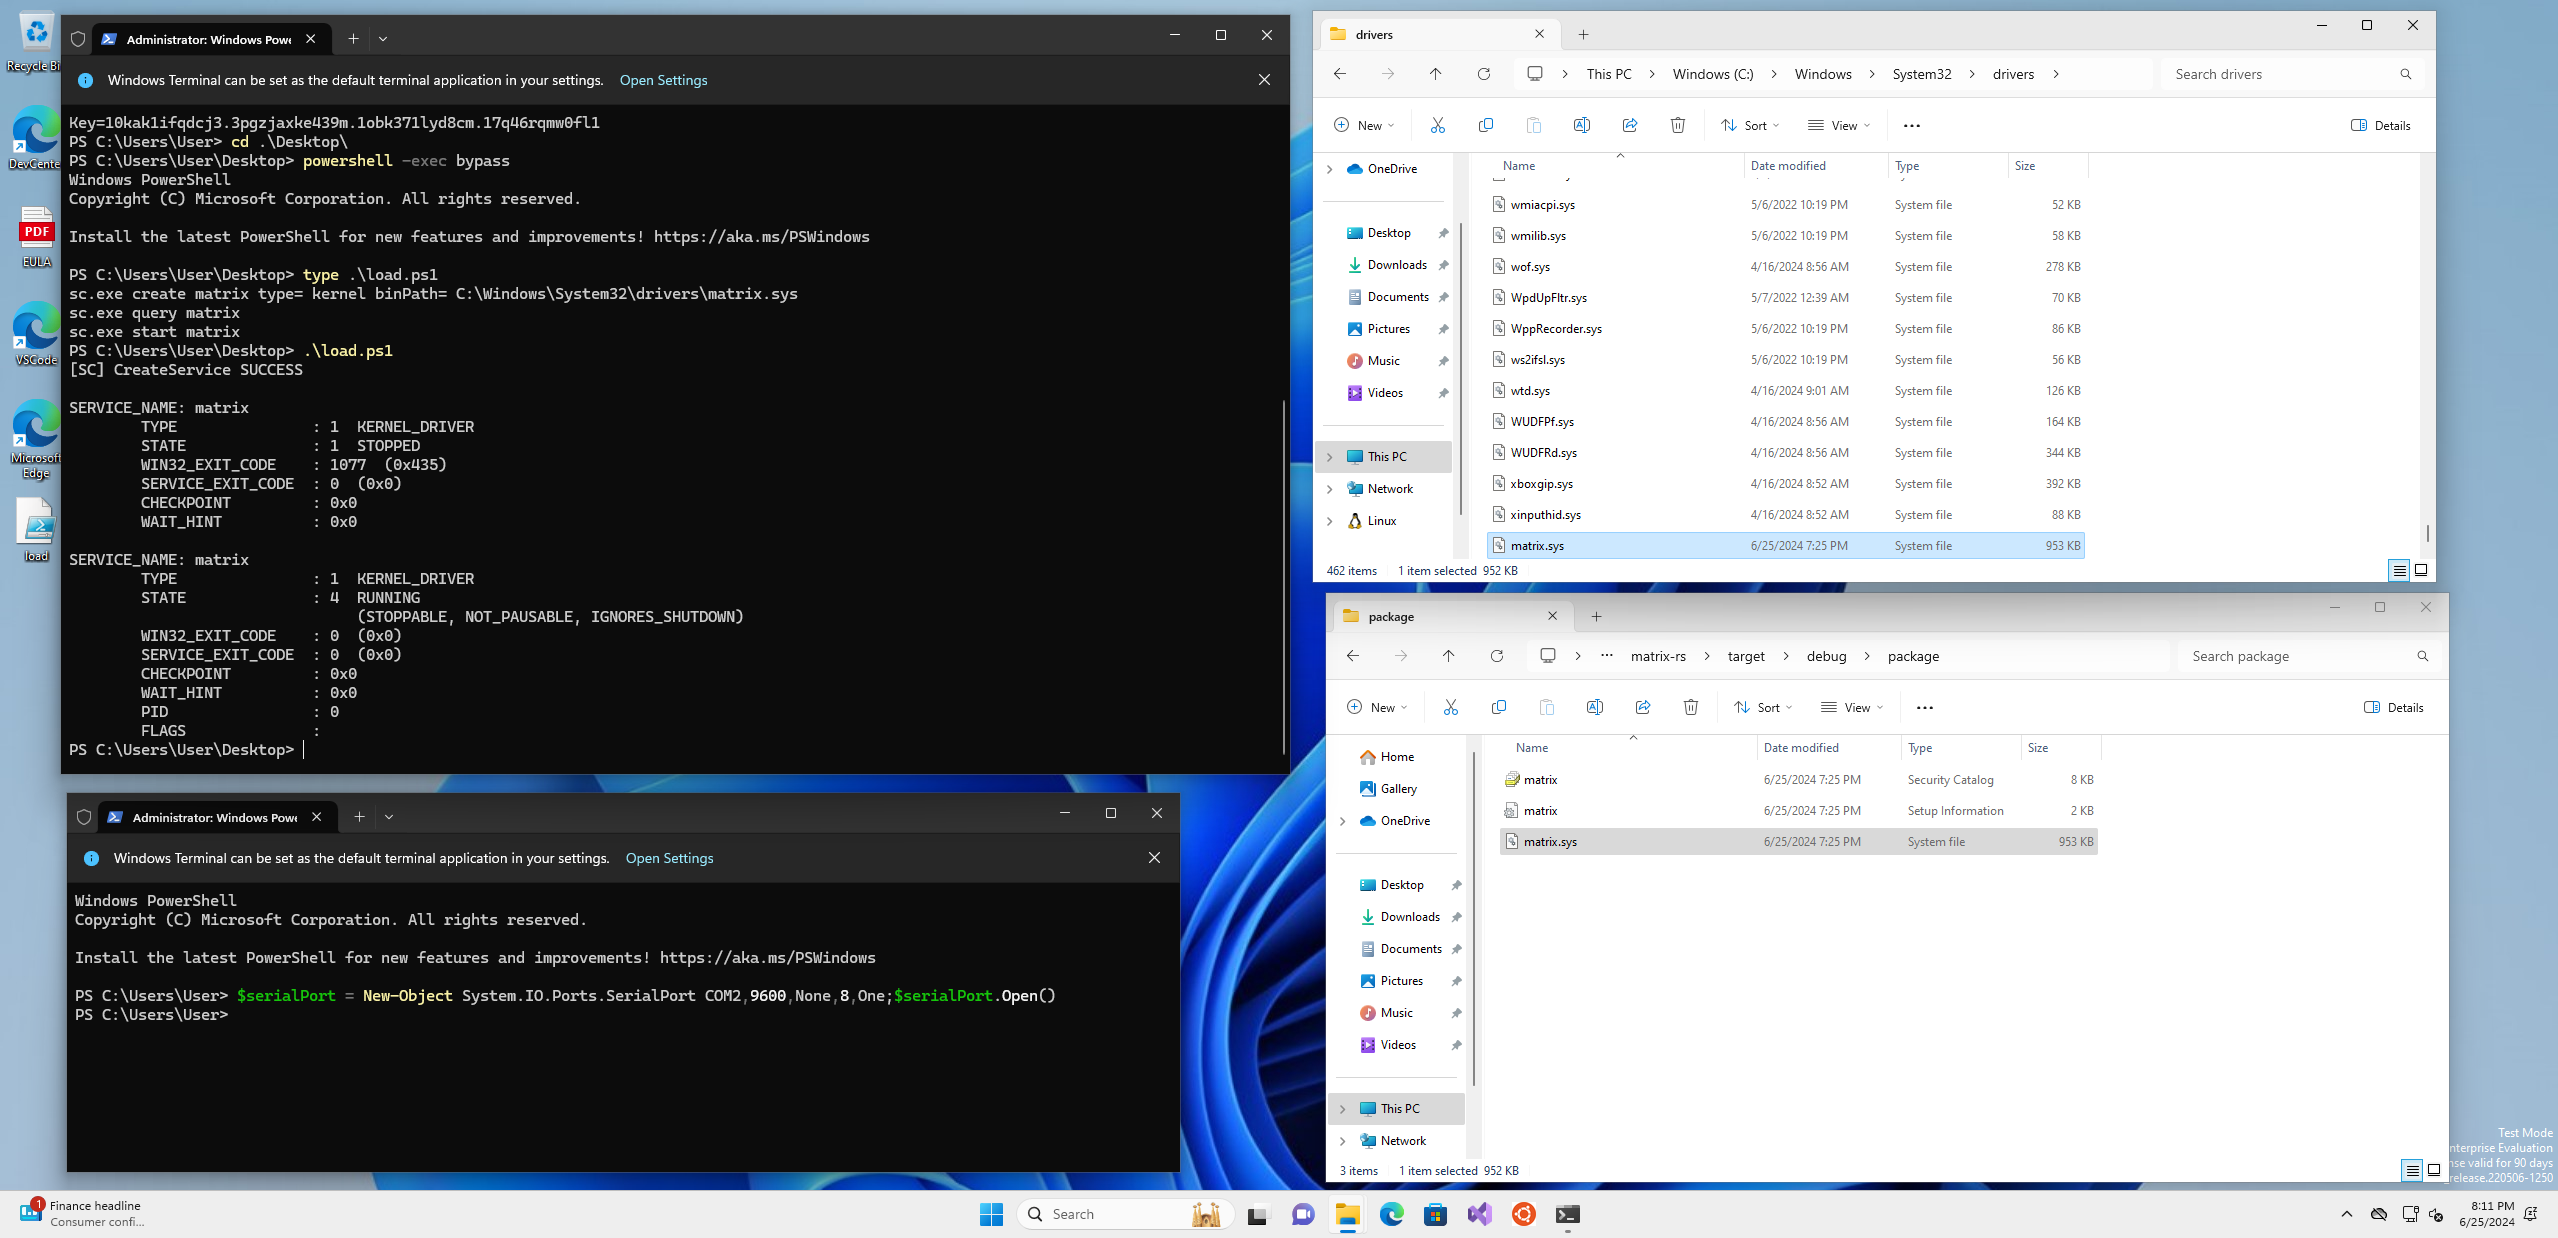
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)

A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.

Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.

A Linux eBPF rootkit with a backdoor, C2, library injection, execution hijacking, persistence and stealth capabilities.

PoCs for Kernelmode rootkit techniques research.

Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection

Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…

Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…

Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…

Mac OS X rootkit - for learning purposes

Detection of rootkit file hiding activities through analysis of shifts in kernel function execution times.