

securityonion
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
anomaly-detectionanti-botdefensive-tools+9
4.9k
security-onion-solutions/securityonionOpen-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 farisv/appledos
Messing Apple devices on the network with CVE-2018-4407 (heap overflow in bad packet handling)
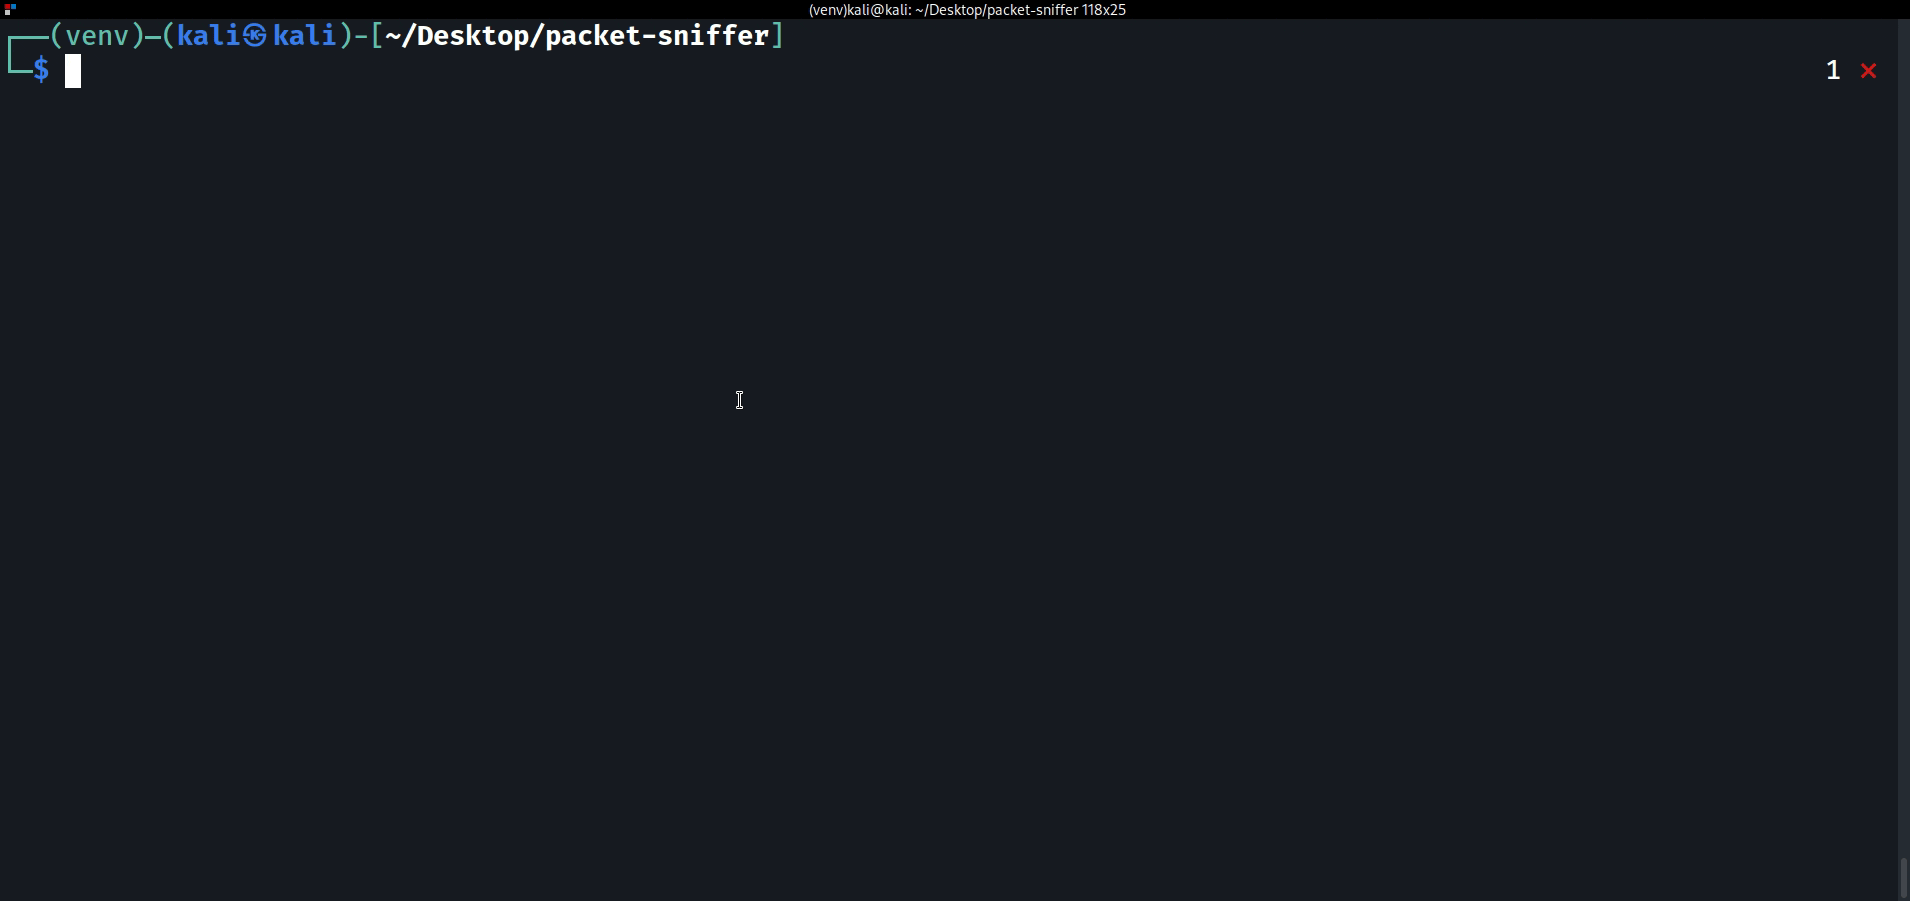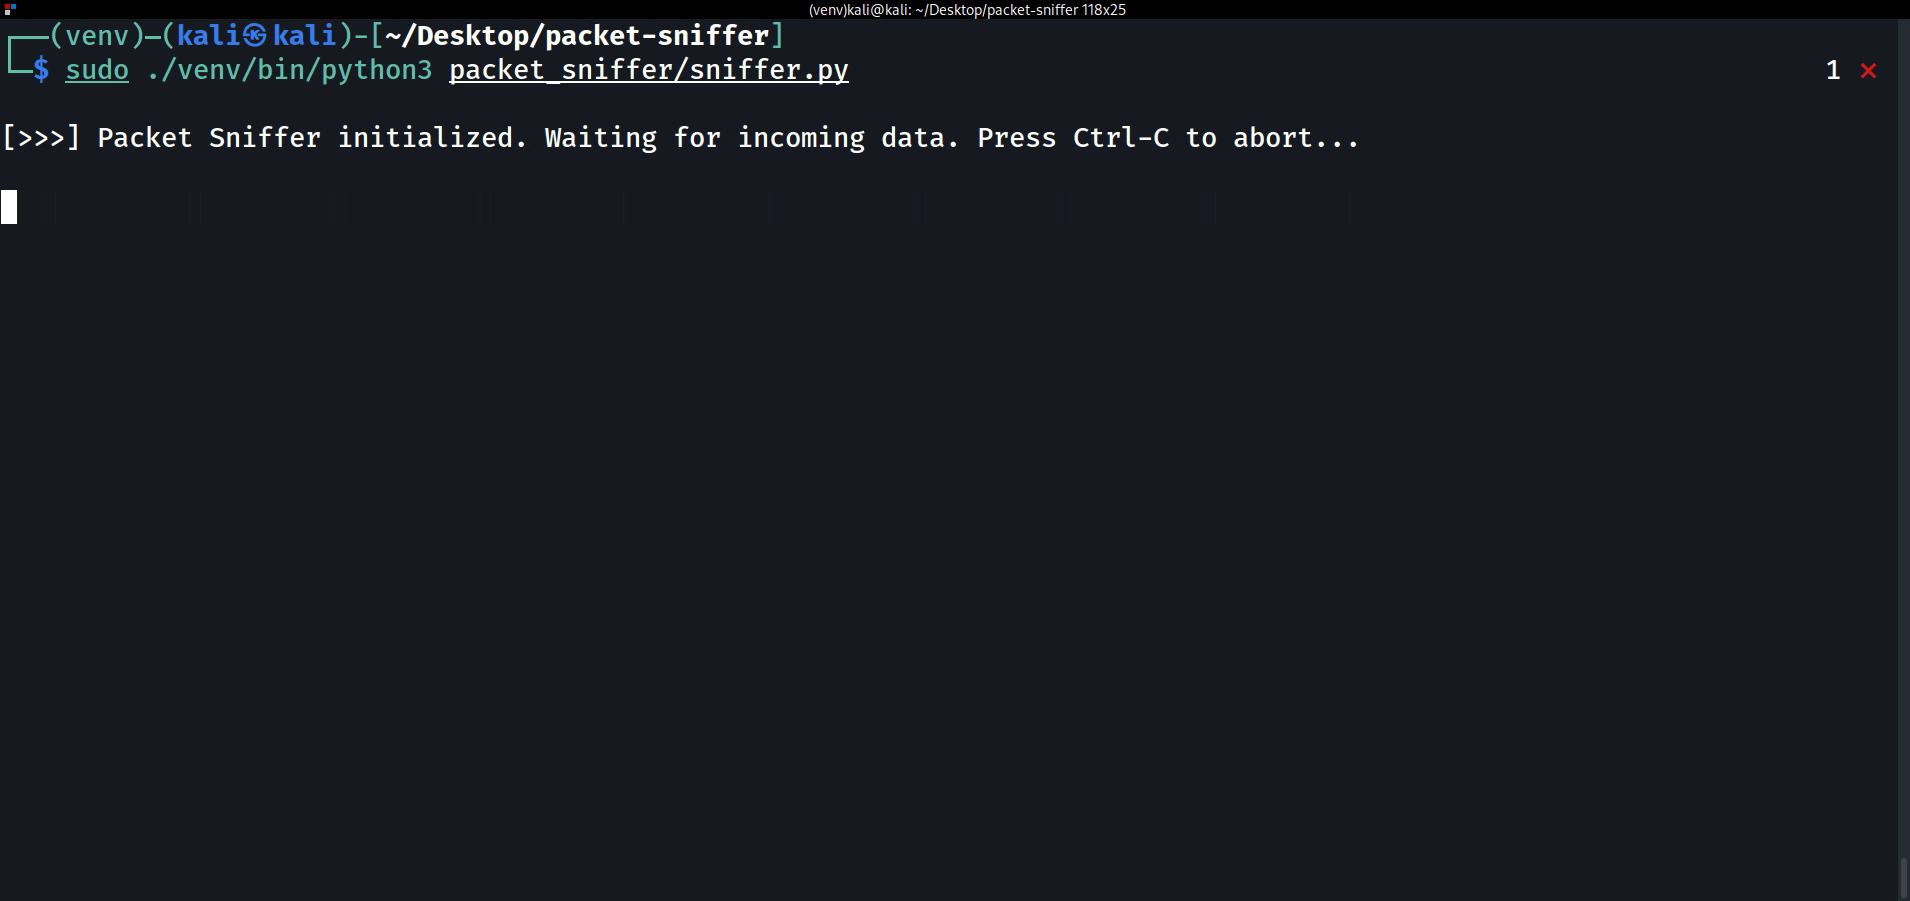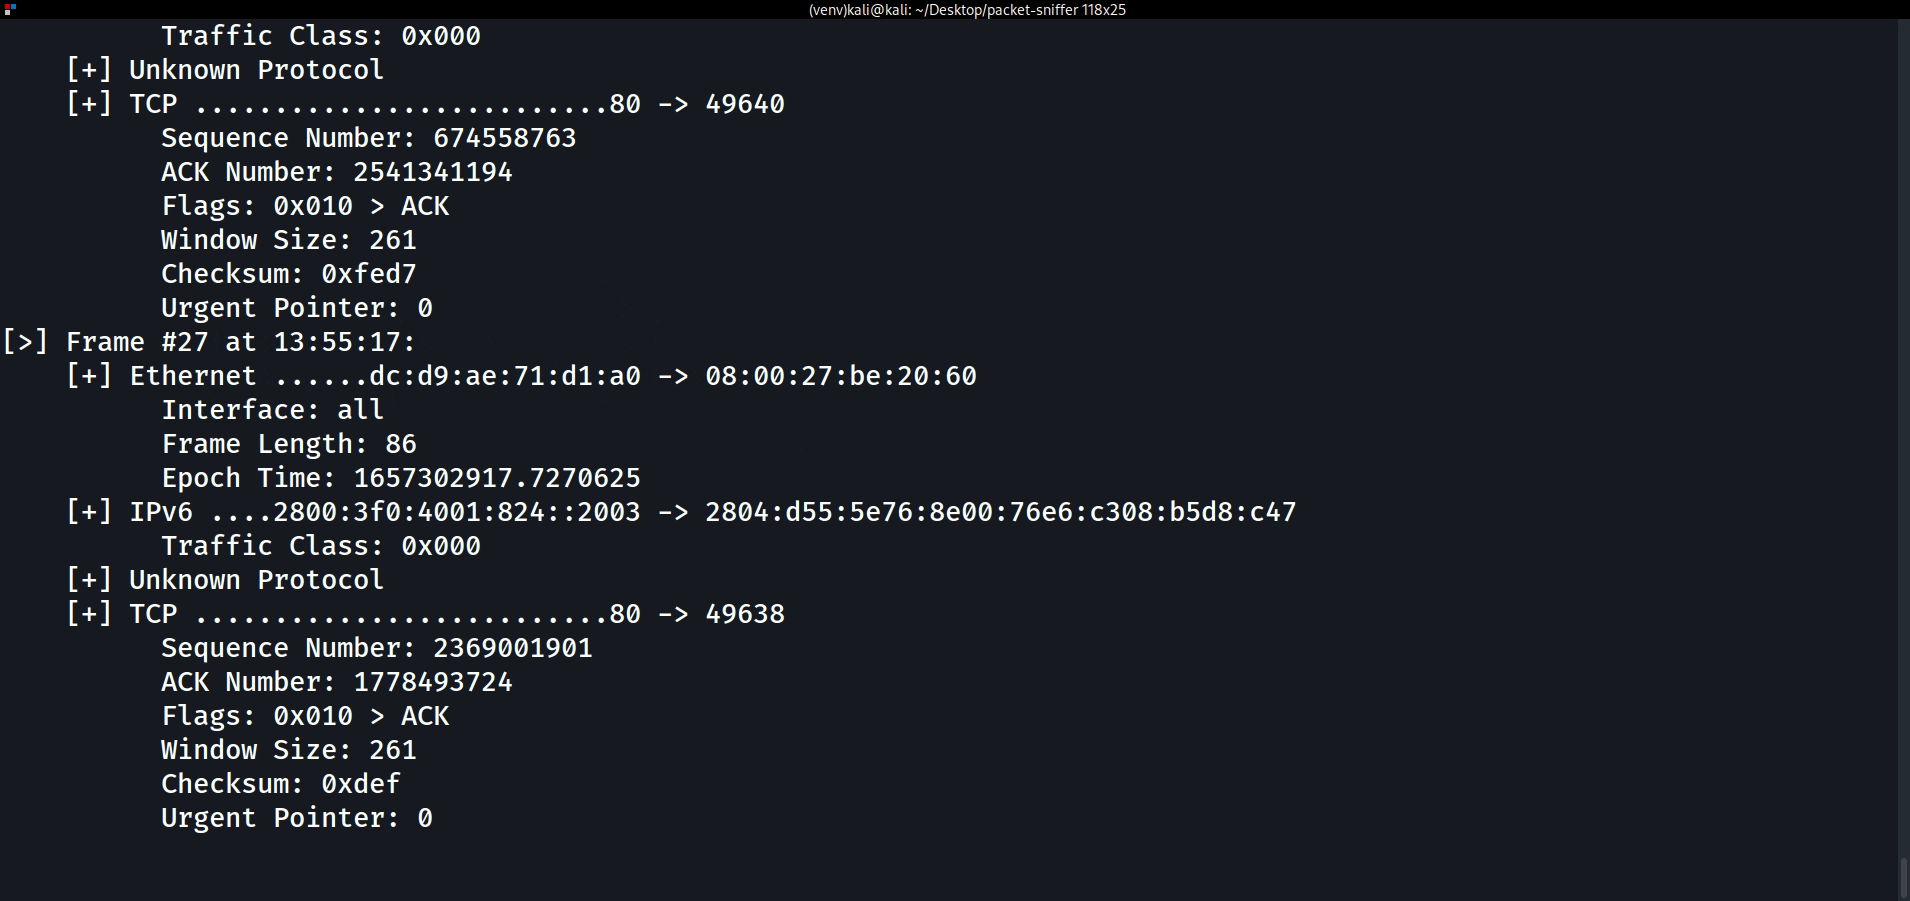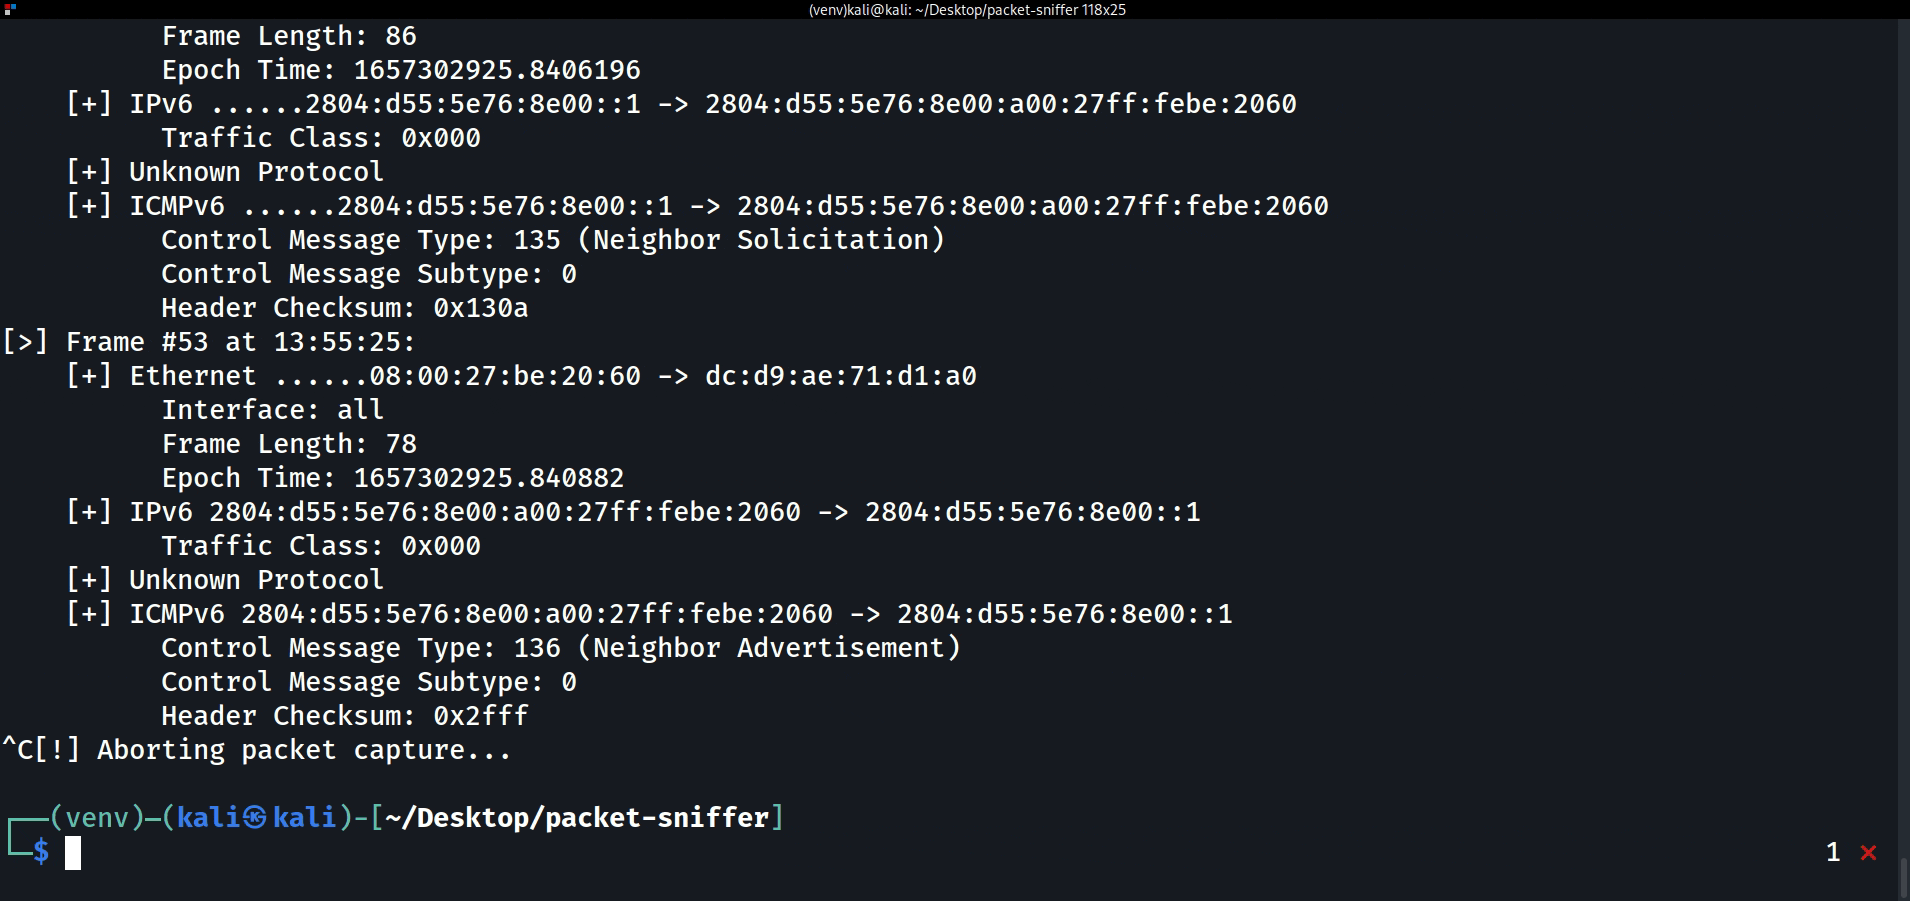 eonraider/packet-sniffer
Raw socket-based network packet sniffer that captures and disassembles TCP/IP packets from network interfaces for security analysis and educational…
 shramos/polymorph
Polymorph is a real-time network packet manipulation framework with support for almost all existing protocols
 kamal-marouane/cve-2022-21907
Vulnerability in HTTP Protocol Stack Enabling Remote Code Execution and Potential System Crash.
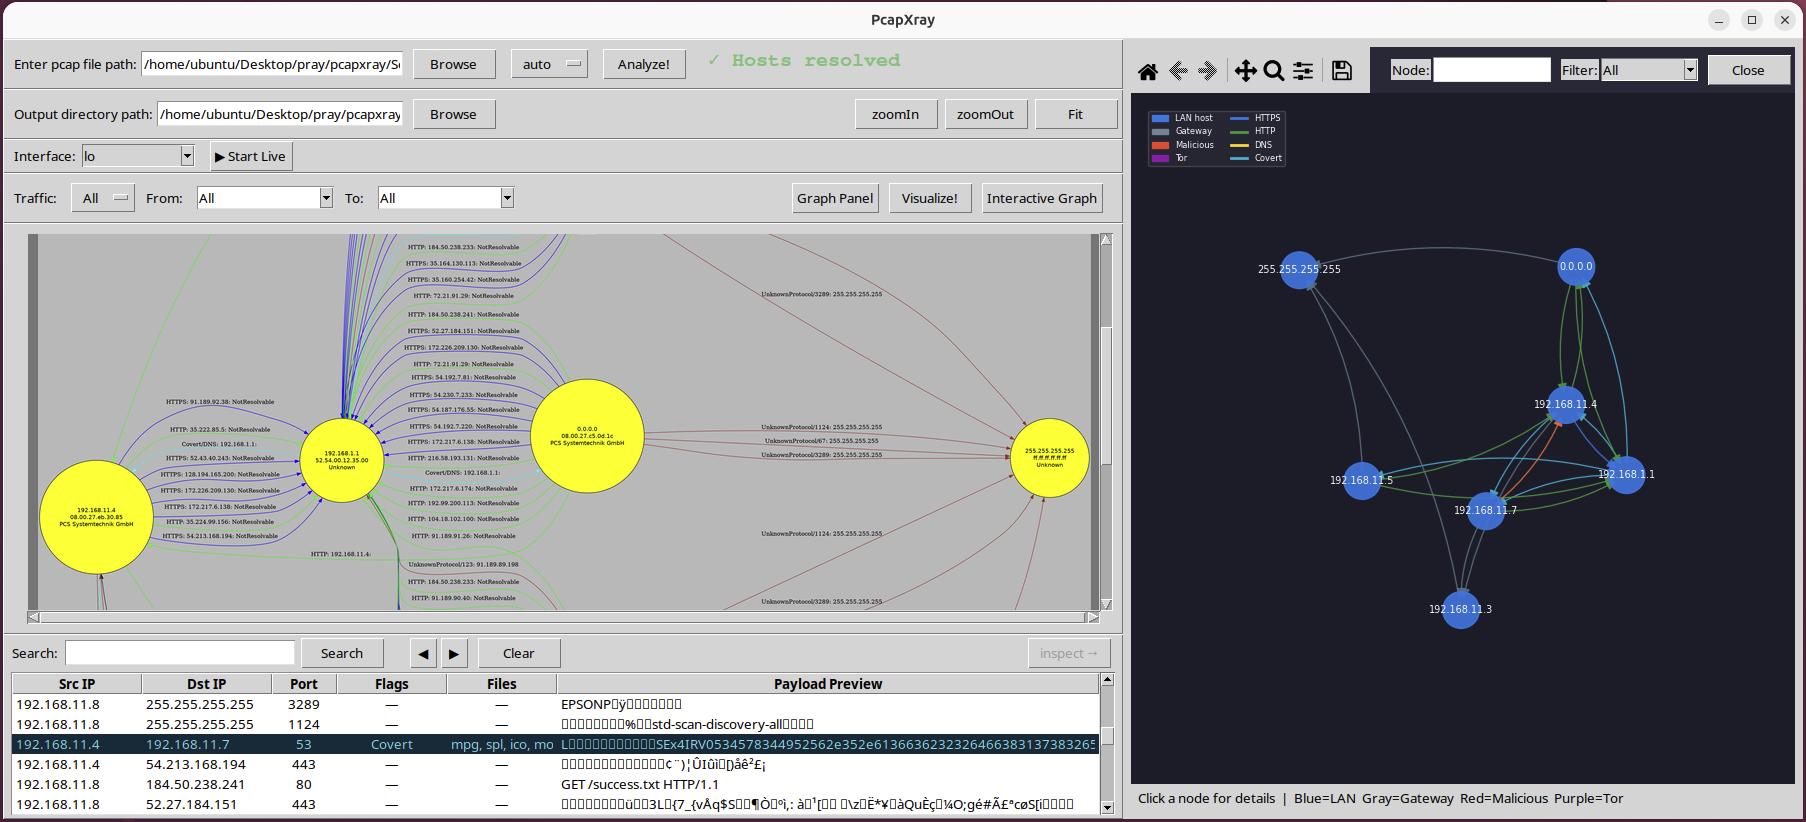 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
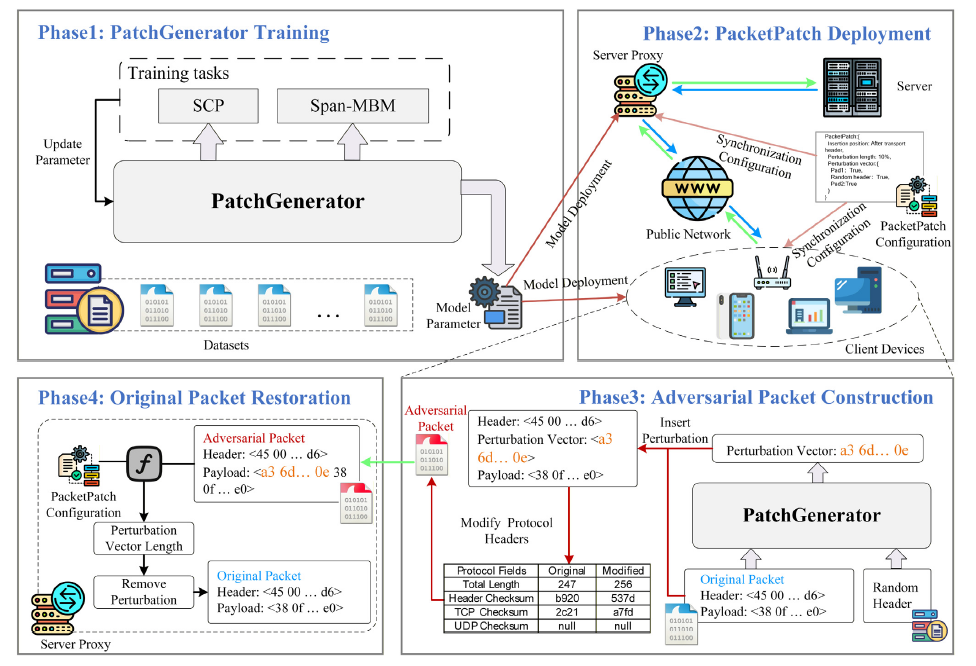 xuyw-seu/packetpatch
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.
 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 jlinebau/cve-2025-55315-scanner-monitor
Quick and Simple Scripts to Scan for Vulnerable Servers and Packet Level Monitors
 apipia/log4j-pcap-activity
A fun activity using a packet capture file from the log4j exploit (CVE-2021-44228)
 abiral-timalsina/cyber-defenders-lab-
My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
 l3onkers/fuxios
Modernized Python 3 exploit PoC for CVE-2016-4631 targeting iOS devices. Features network scanning, malformed IP/TCP payload generation, and packet…
 themalwareguardian/cve-2021-27289
CVE-2021-27289: Playback Protection Bypass on Ksix Zigbee devices
 george0papasotiriou/cve-2026-6060-quic-handshake-amplification-via-address-validation-bypass
Educational Python PoC for a QUIC address-validation bypass that triggers handshake amplification, including vulnerable server simulation and attack…
 george0papasotiriou/cve-2026-2222-mqtt-broker-connect-packet-heap-overflow
Demonstrates CVE-2026-2222 heap overflow in MQTT CONNECT packet handling with a simulated vulnerable broker and proof-of-concept exploit code for…
 alexsvobo/nhi-zero-trust-bypass
Demonstrates a real-world zero-trust bypass by exploiting BIND CVE-2025-40775 to disrupt DNS, break secret rotation, and expose static credentials in…
 simoesctt/-ctt-nsp-convergent-time-theory---network-stack-projection-cve-2026-24858-
A Proof-of-Concept demonstrating the application of 3D Navier-Stokes CTT formulations to packet flow optimization and defensive bypass.
 martinvks/cve-2022-45059-demo
Interactive demo of CVE-2022-45059 Varnish Cache request smuggling vulnerability. Includes Spring Boot web app, vulnerable proxy, automated victim…