
CVE-2026-41940-analysis
 oguz-kagan-akar/cve-2026-41940-analysis
Technical analysis of the cPanel/WHM auth bypass
authentication-authorizationeducationexploitation+5
oguz-kagan-akar/cve-2026-41940-analysisTechnical analysis of the cPanel/WHM auth bypass
 aau-network-security/haaukins
A Highly Accessible and Automated Virtualization Platform for Security Education
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.
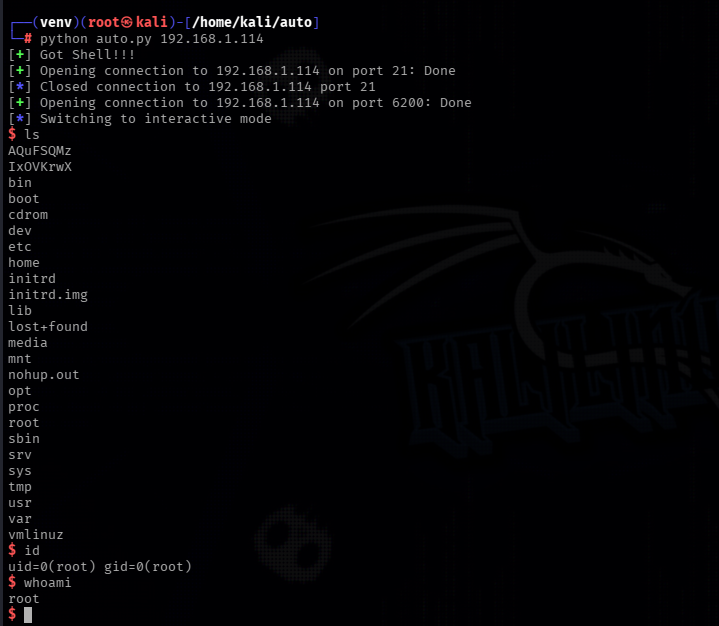 jun41ds2709/vsftpd-2.3.4-exploit
Python exploit for the vsFTPd 2.3.4 backdoor (CVE-2011-2523).
 antogit-sys/cve-2007-5962
vsftpd 2.0.5 - 'CWD' (Authenticated) Remote Memory Consumption
 redpack-kr/cve-2024-5243-pwn2own-toronto-2023
Pre-authentication Remote Code Execution exploit for TP-Link Omada ER605 router via DDNS client daemon (cmxddnsd)
 coby-nguyen/document-linux-privilege-escalation
Exploiting the vulnerability called "Dirty_Sock" (CVE-2019-7304) in the REST API for Canonical's snapd daemon.
 themalwareguardian/cve-2007-1567
Classic stack-based buffer overflow in War FTP Daemon 1.65 demonstrating old-school remote code execution through malformed FTP commands.
 mdusmandasthaheer/cve-2025-32433
Proof-of-concept exploit for CVE-2025-32433, a pre-authentication RCE in Erlang/OTP SSH daemon. Includes Python script to send crafted SSH channel…
 t0kx/exploit-cve-2015-3306
ProFTPd 1.3.5 - (mod_copy) Remote Command Execution exploit and vulnerable container
 lutfifakee-project/cve-2026-41651
Local privilege escalation exploit targeting PackageKit's TOCTOU race condition (CVE-2026-41651). Escalates from unprivileged user to root via polkit…
 amir-hy/cve-2022-42475
FortiOS buffer overflow vulnerability
 lamaper/cve-2026-52199
Proof-of-concept exploit for CVE-2026-52199: unauthenticated remote code execution via exposed ADB daemon on UZ801 4G LTE router. Includes…