
CVE-2018-1207-better
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
binary-exploitationeducationembedded-systems-security+5
hironull/cve-2018-1207-betterReverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 cao-wuhui/cve-2025-69720
Advisory for CVE-2025-69720: stack-based buffer overflow in GNU ncurses infocmp (CWE-121)
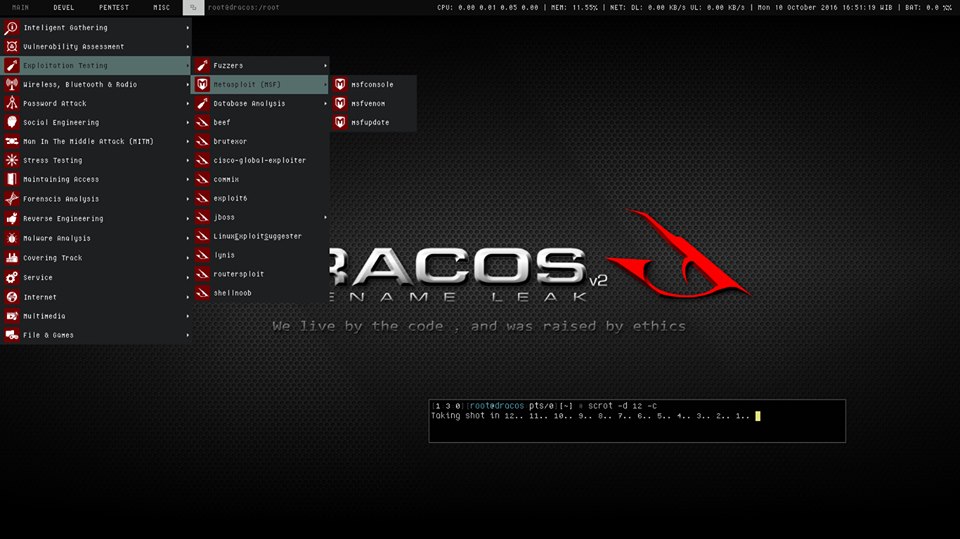 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
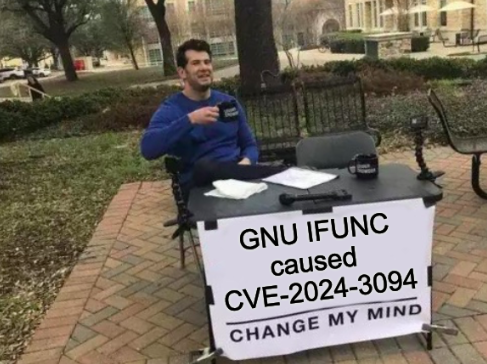 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 cumakurt/tscan
Python-based scanner that detects and exploits CVE-2026-24061 telnetd authentication bypass, enabling root shell access on vulnerable GNU Inetutils…
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.
 supermagnum/gr-qradiolink
GNU Radio out-of-tree (OOT) module for QRadioLink blocks.
 nonamecoder/cve-2022-27254
Proof-of-concept demonstrating RF replay attack on Honda's remote keyless entry system (CVE-2022-27254) using HackRF One and GNU Radio for signal…
 mr-zapi/cve-2026-24061
Nuclei template for detecting CVE-2026-24061, a critical telnet argument injection in GNU inetutils telnetd allowing unauthenticated root access.
 ish3ng0m4/cve-2026-24061-telnetd
CVE-2026-24061 GNU Inetutils Telnetd Authentication Bypass
 0xmoga/cve-2023-4911-lab
Docker-based CVE-2023-4911 lab for analyzing glibc ld.so buffer overflow and developing a local privilege escalation exploit with GDB debugging.
 ekomssavior/telnet_scan
scanner/exploiter CVE-2026-24061 & CVE-2026-32746
 jakeswiz/telnet-inetutils-auth-bypass-cve-2026-24061
This is a simple PoC that allows you to highlight the severity of the ongoing and actively exploited Telnet bug that is going on right now. Why…
 chocapikk/cve-2026-24061
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) with Docker lab setup and Go PoC. Exploits NEW-ENVIRON…
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 obrunolima1910/cve-2026-24061
🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.
 gabs-hub/cve-2026-24061_lab
Educational Docker lab demonstrating CVE-2026-24061, an authentication bypass in GNU telnetd allowing root access via argument injection in the USER…