

snapchange
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
debuggersdynamic-analysis-sandboxingdynamic-code-analysis+3
4712 years ago
awslabs/snapchangeLightweight fuzzing of a memory snapshot using KVM
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
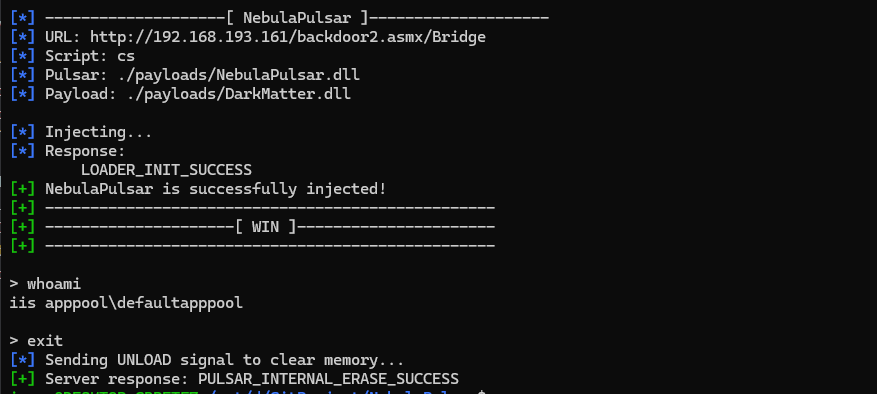 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
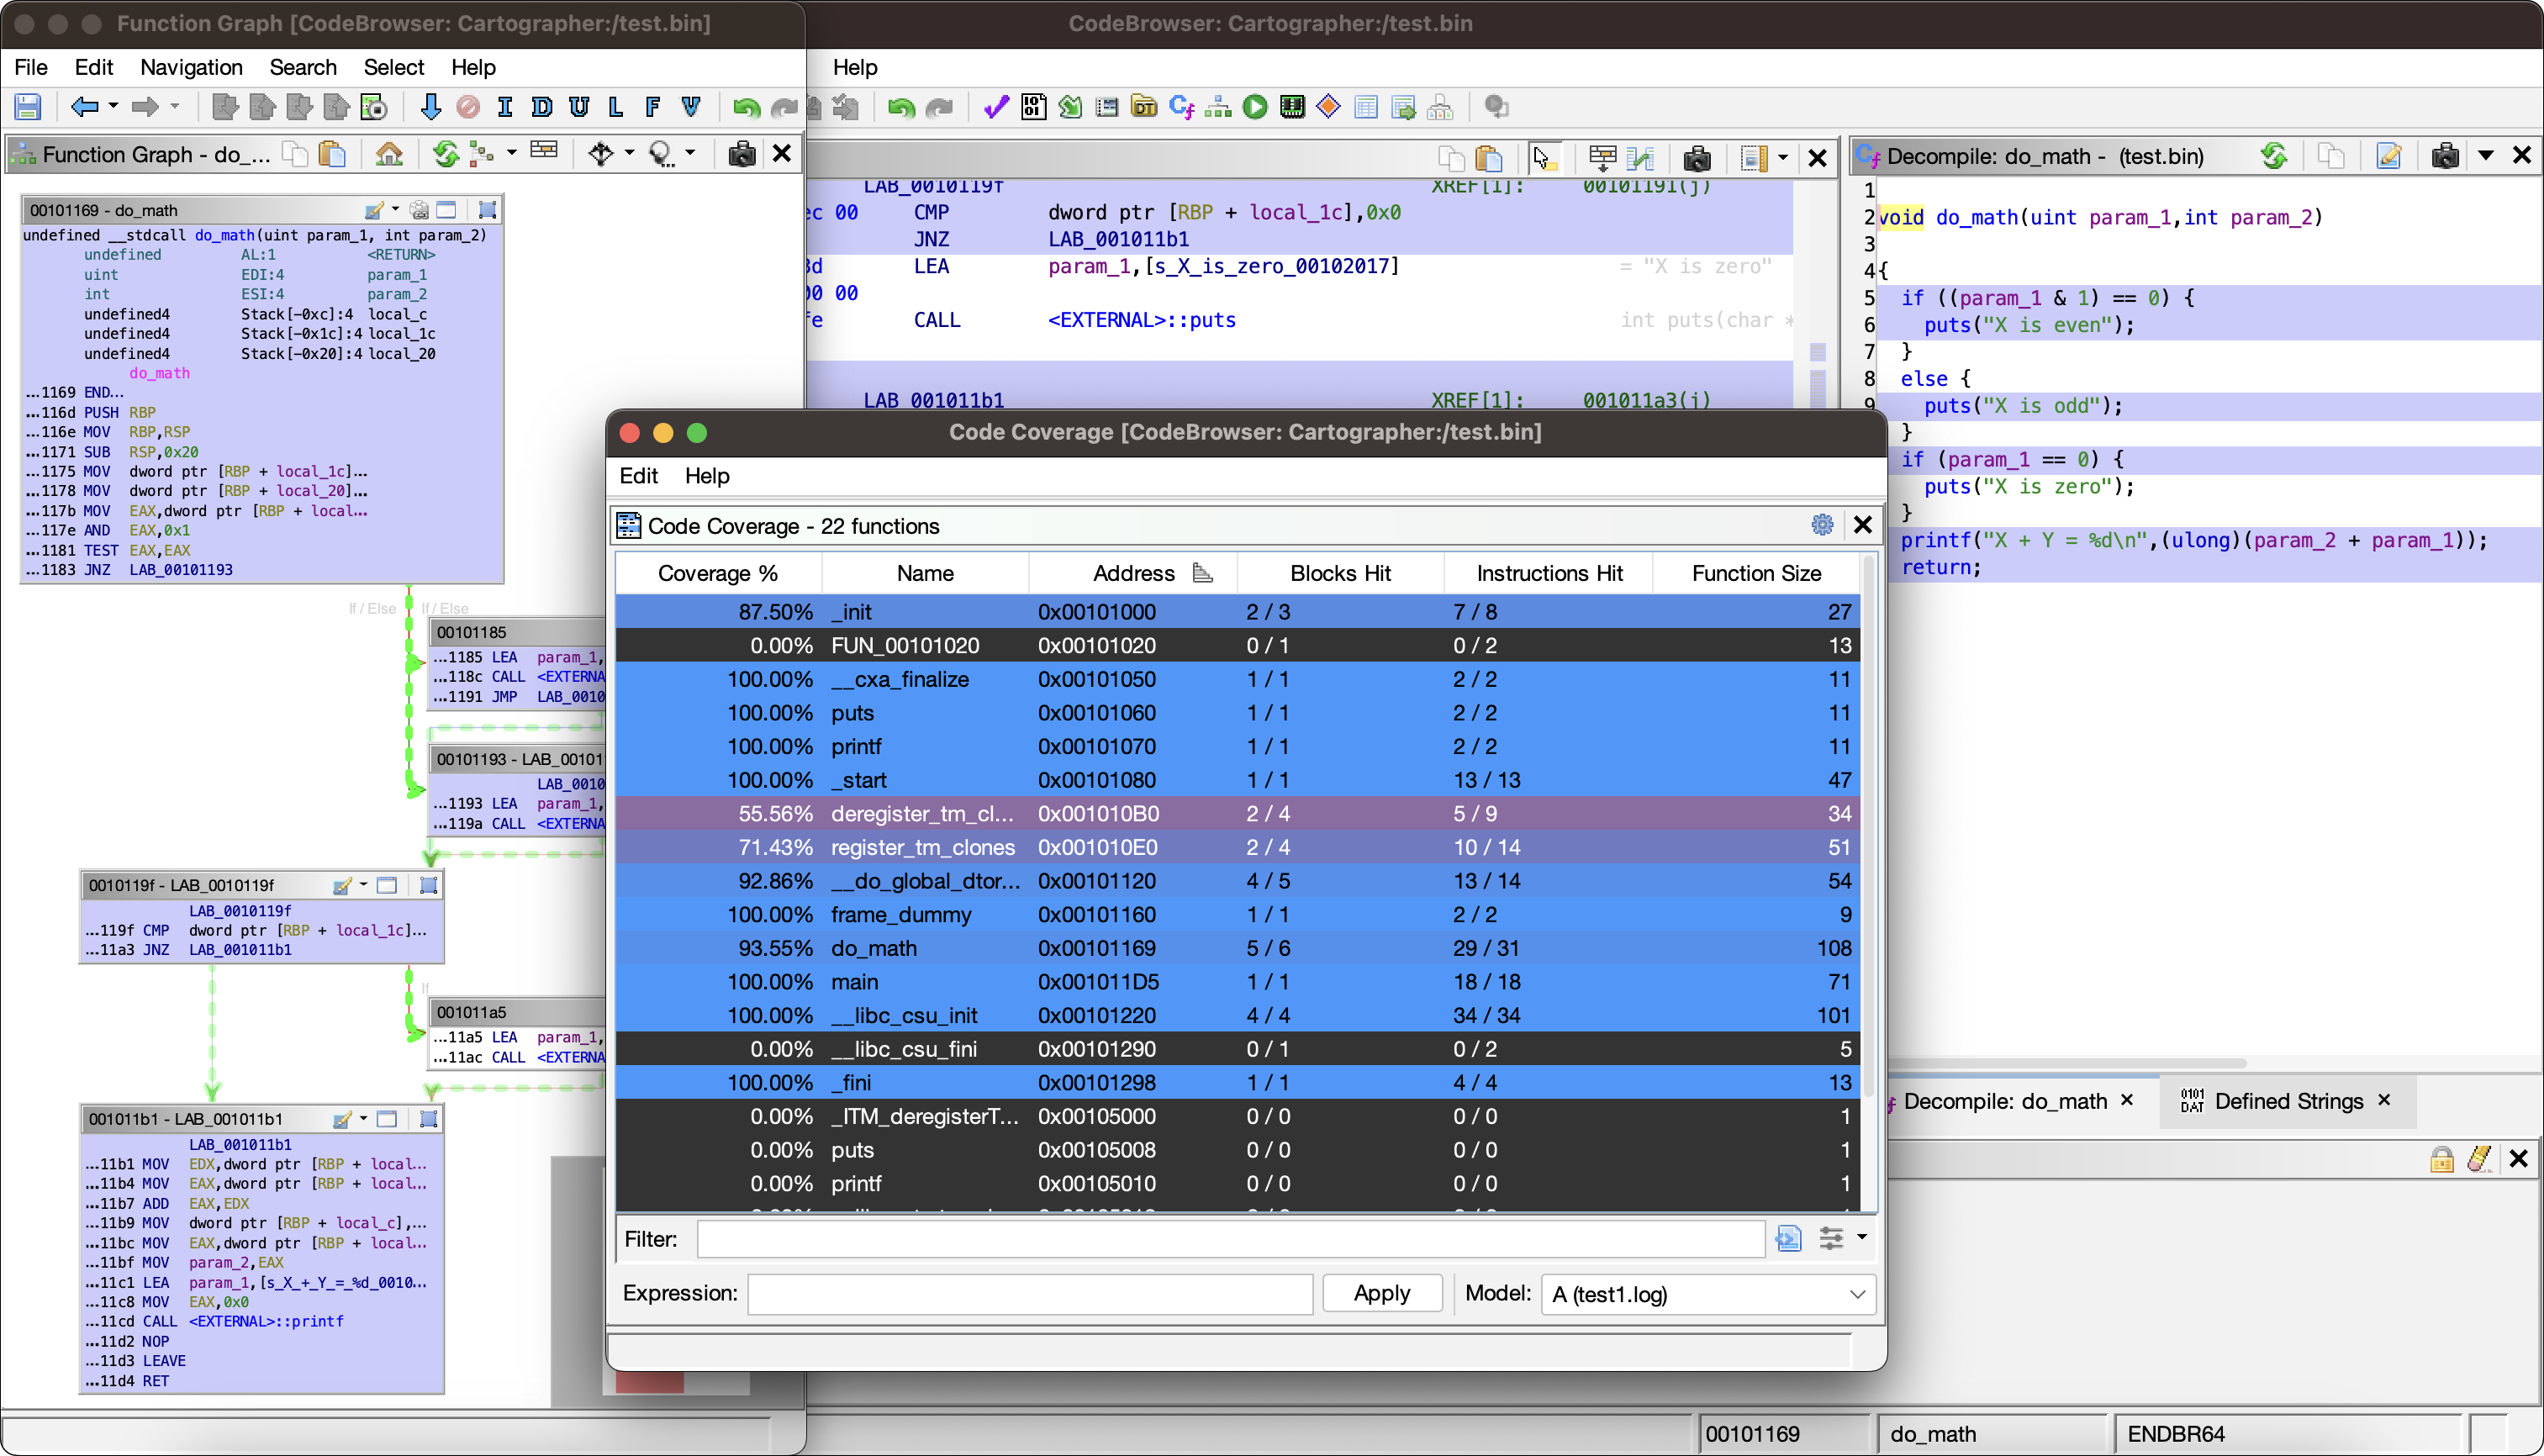 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra