x-stream__xstream_CVE-2021-21345_1-4-15

Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.

Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…

A security scanner for your LLM agentic workflows

Linux Kernel Sanitizers, fast bug-detectors for the Linux kernel


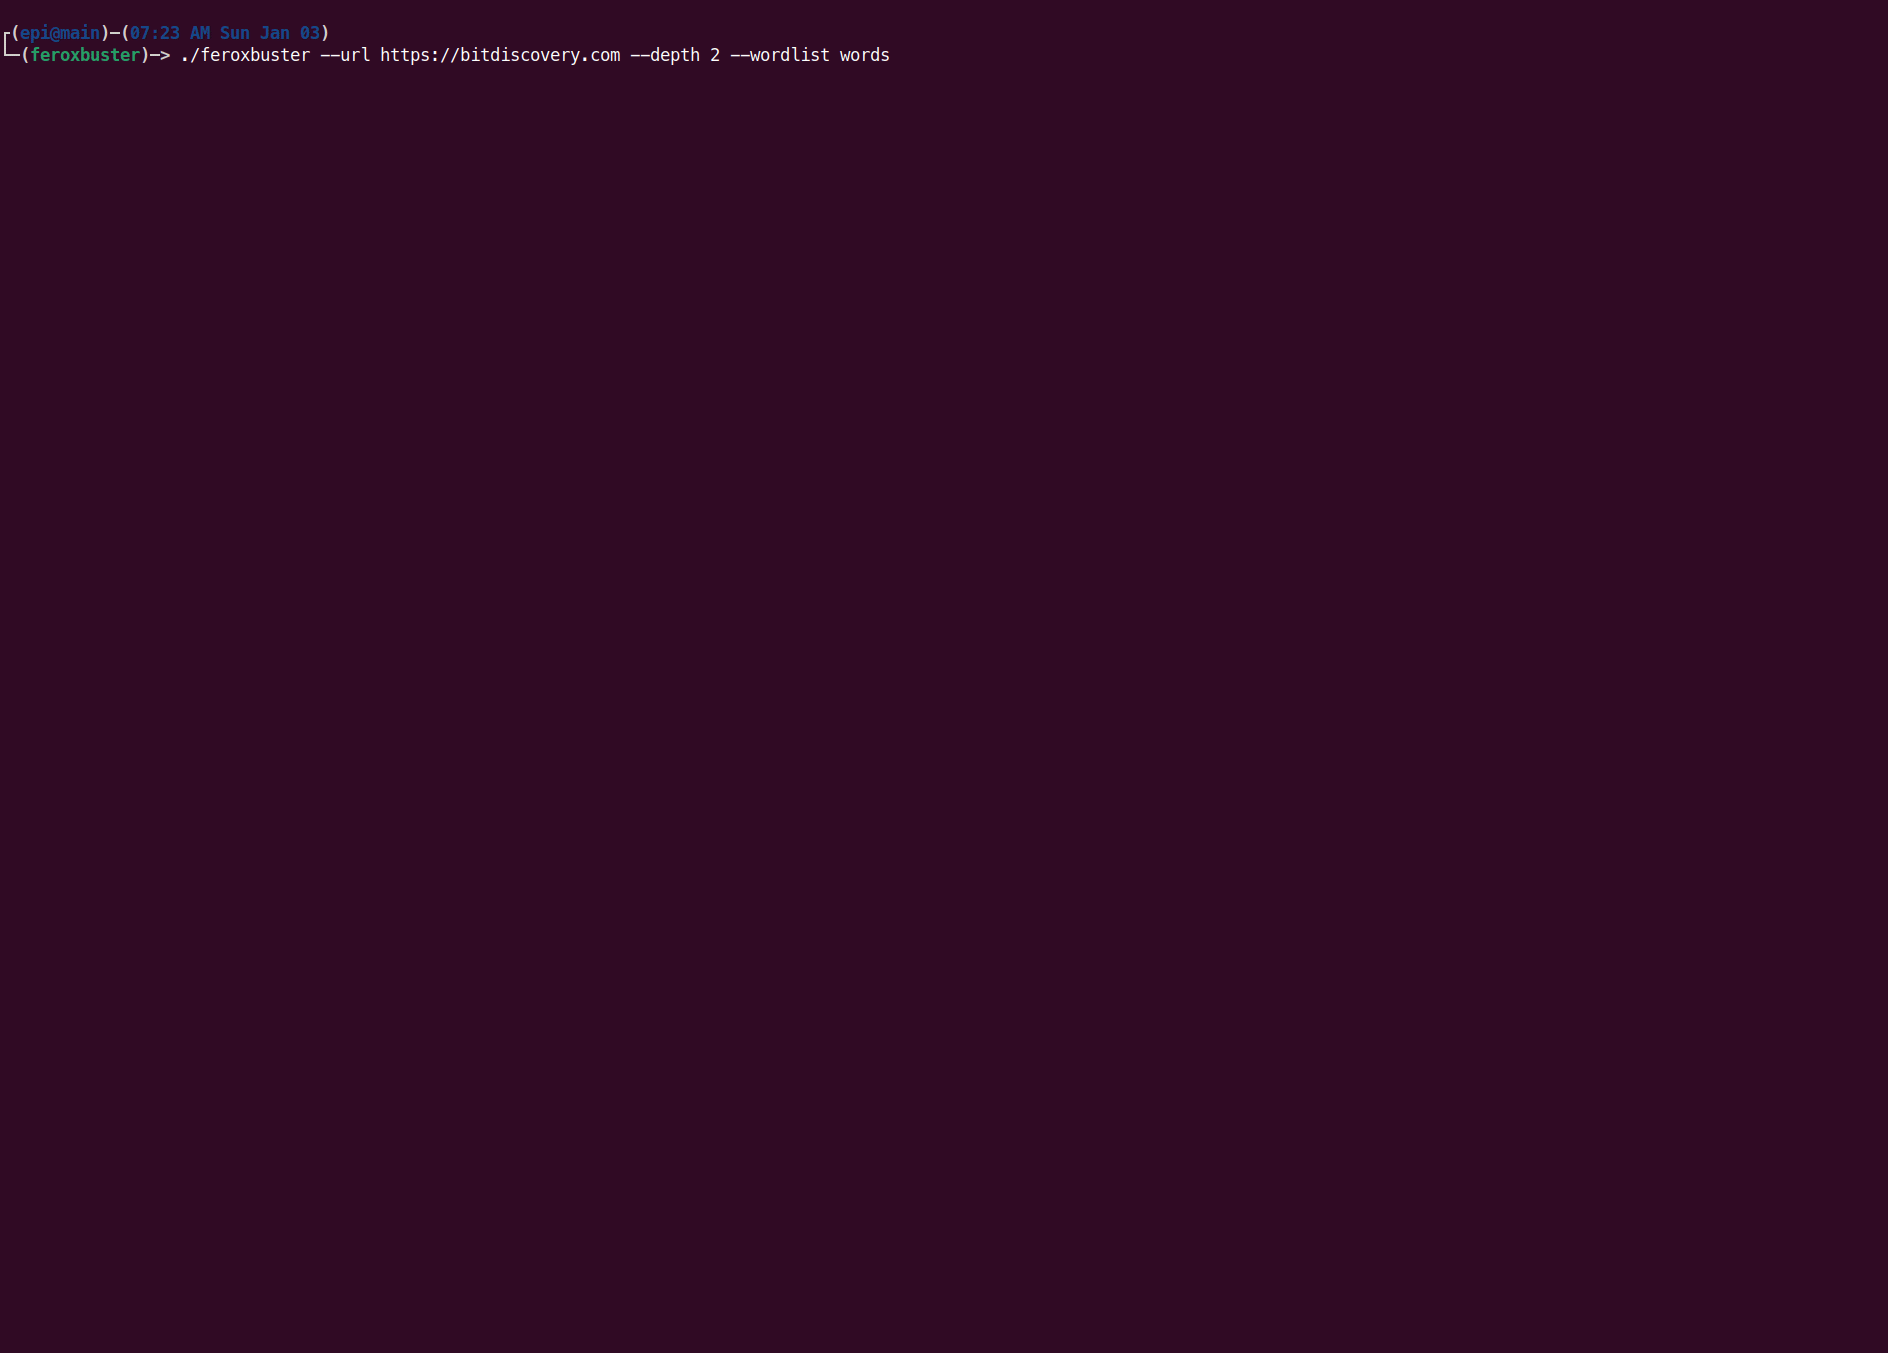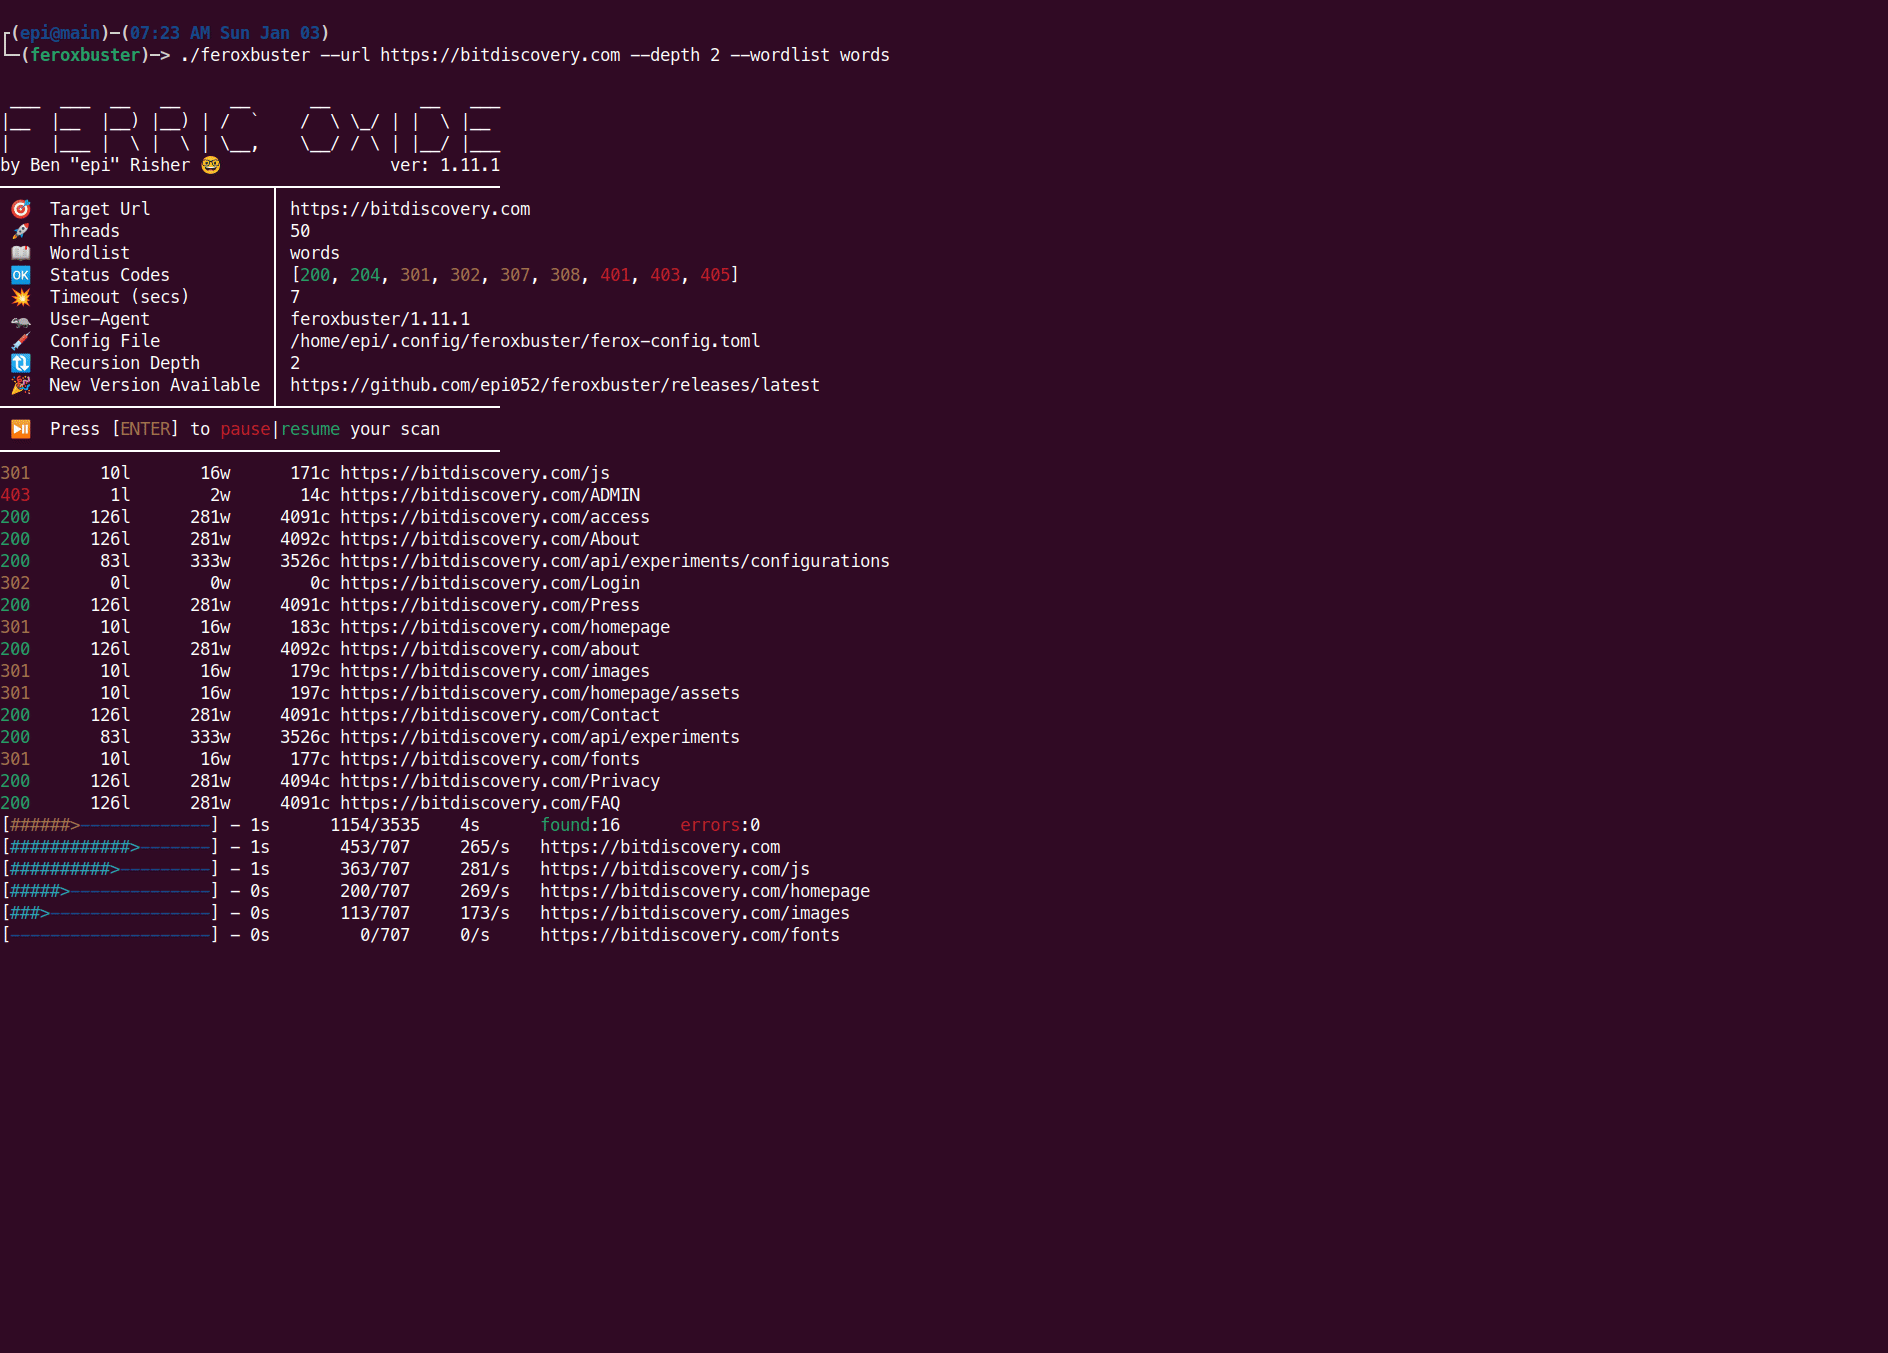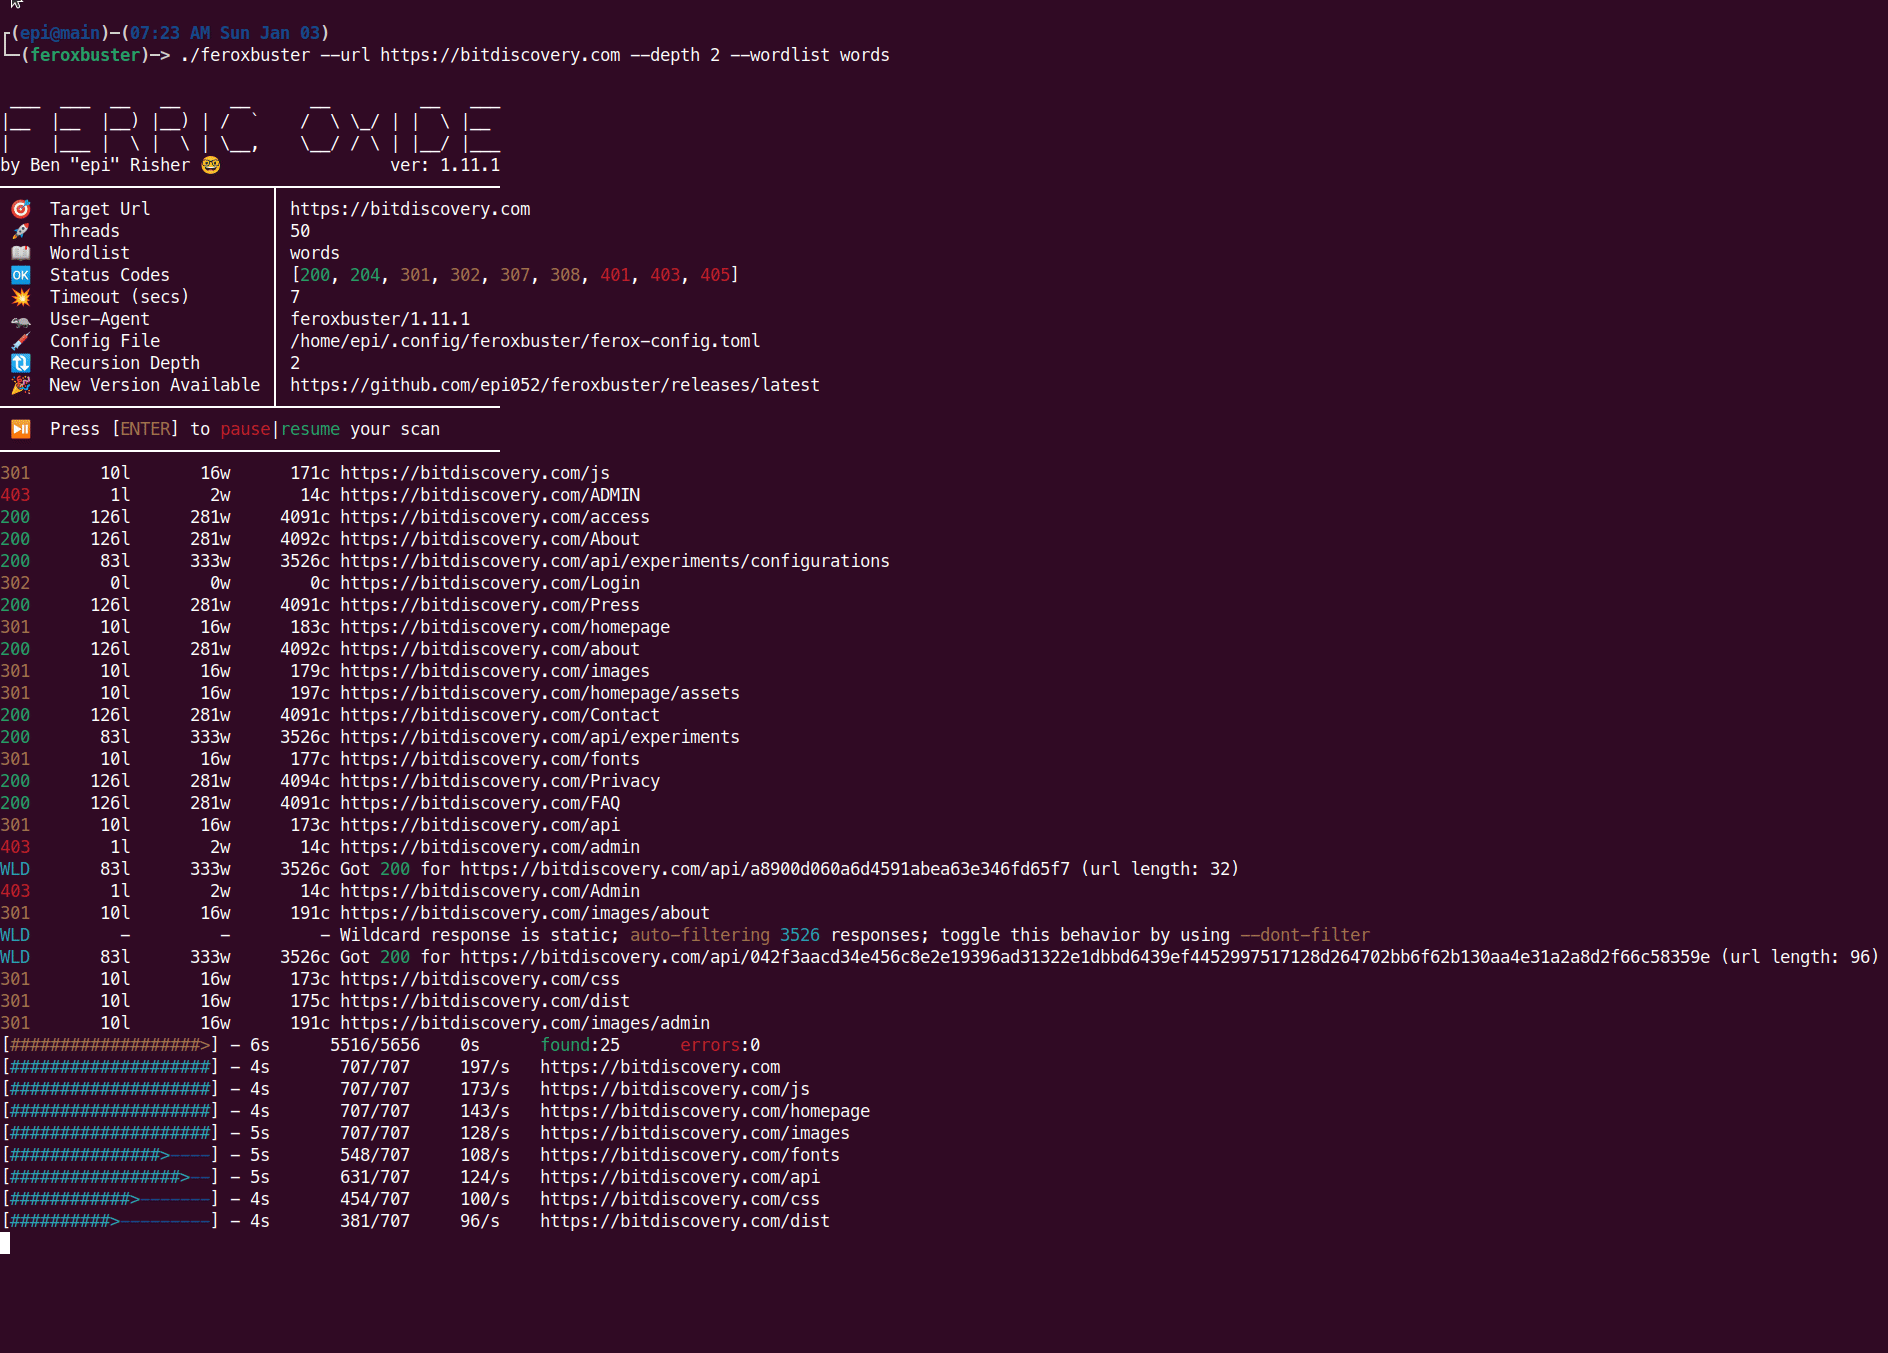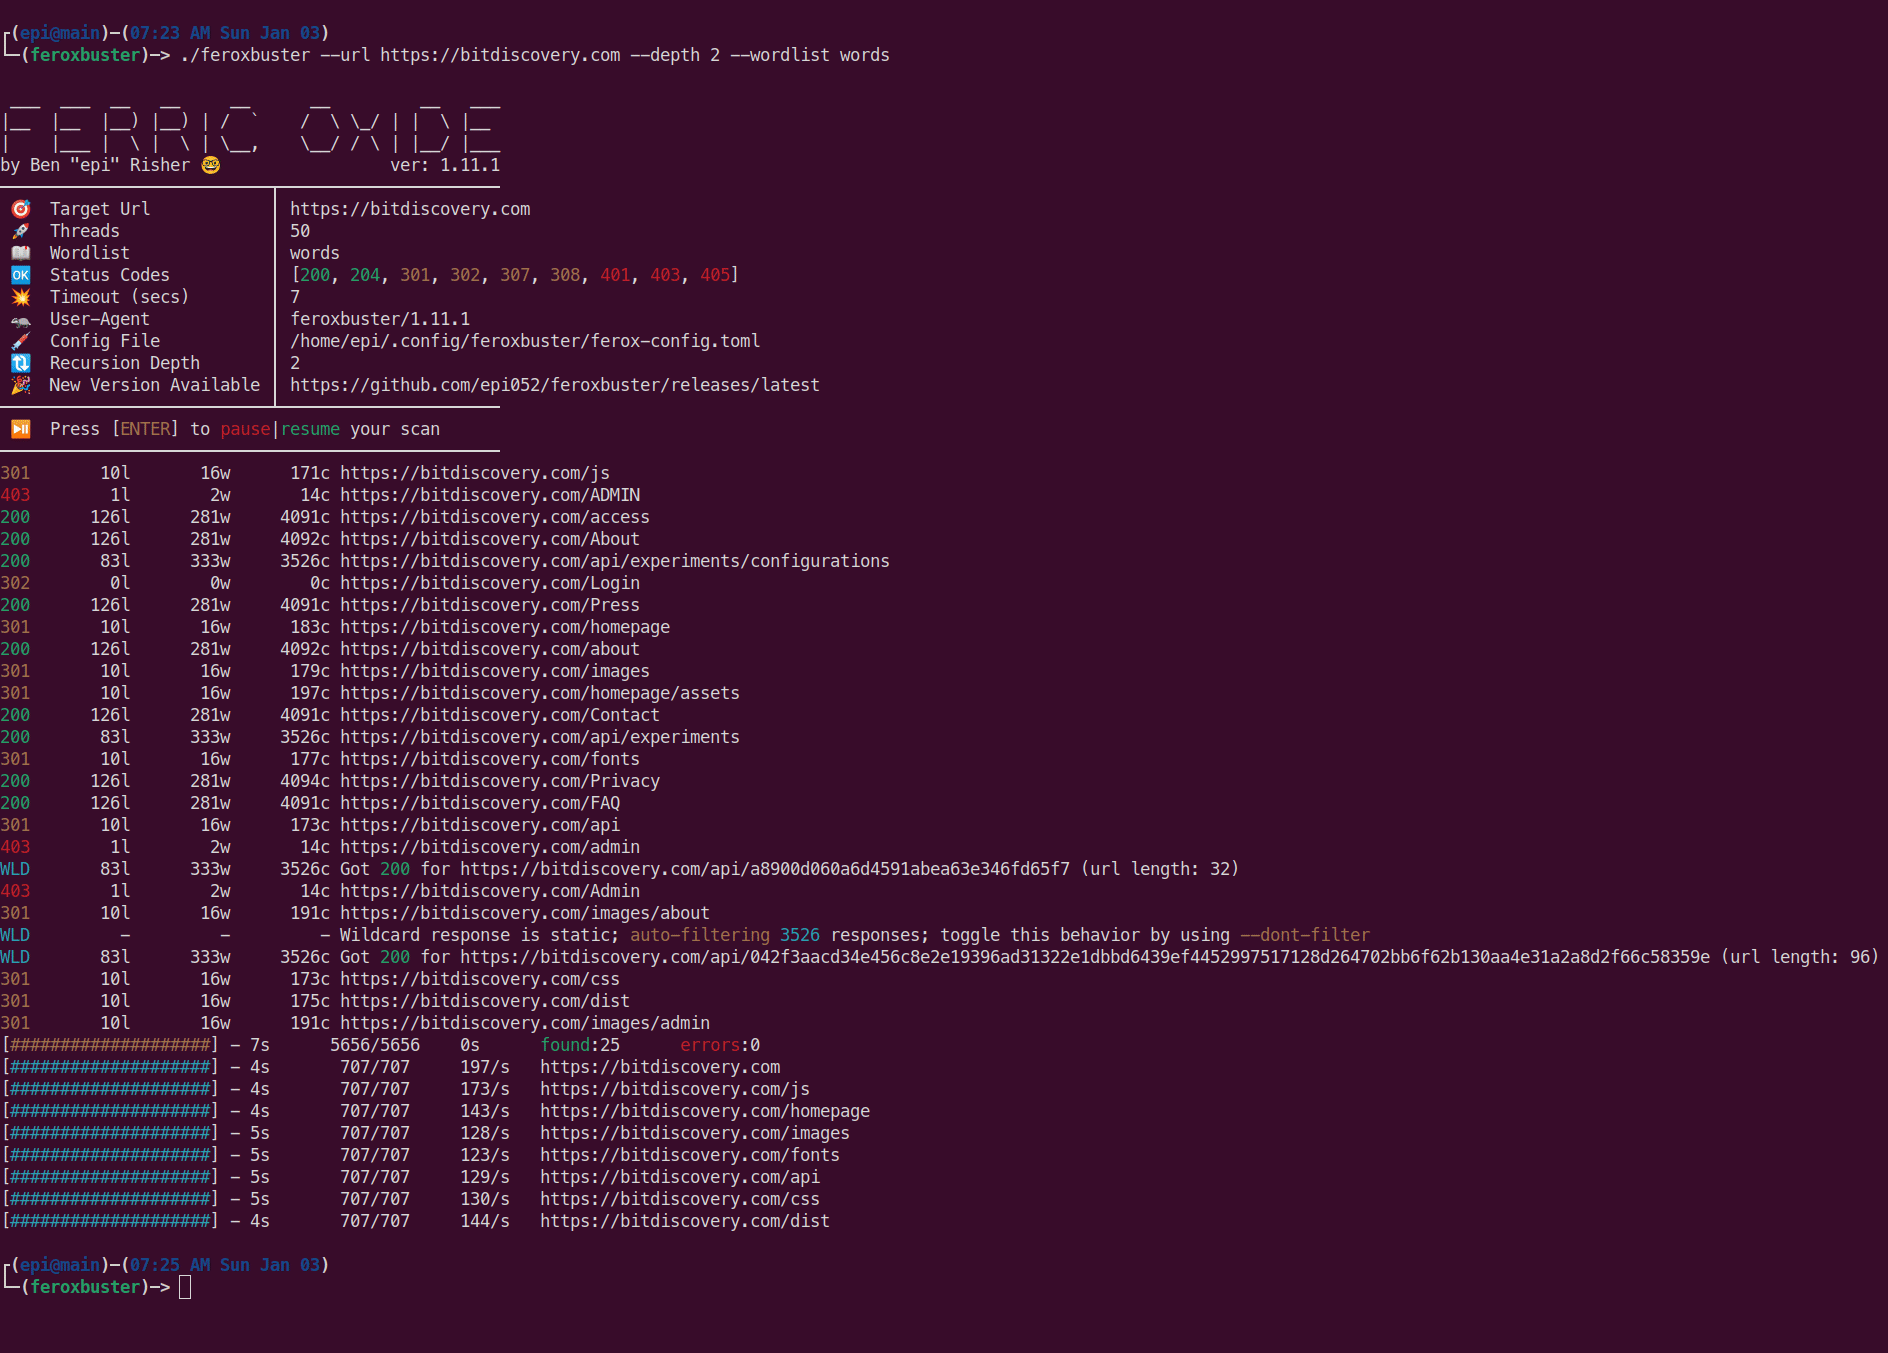
A fast, simple, recursive content discovery tool written in Rust.

Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…

Web vulnerability scanner written in Python3

jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…

Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…

Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…

Detect, analyze and uniquely identify crashes in Windows applications

A PoC Java Stager which can download, compile, and execute a Java file in memory.

GUI Burp Plugin to ease discovering of security holes in web applications

A native APK and DEX decompiler written in Rust

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.

Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…

CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU