delve
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
code-analysisdebuggersdynamic-code-analysis+1
25.0k
go-delve/delveSource-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 avast/yari
YARI is an interactive debugger for YARA Language.
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 lmacken/pyrasite
Inject code into running Python processes
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
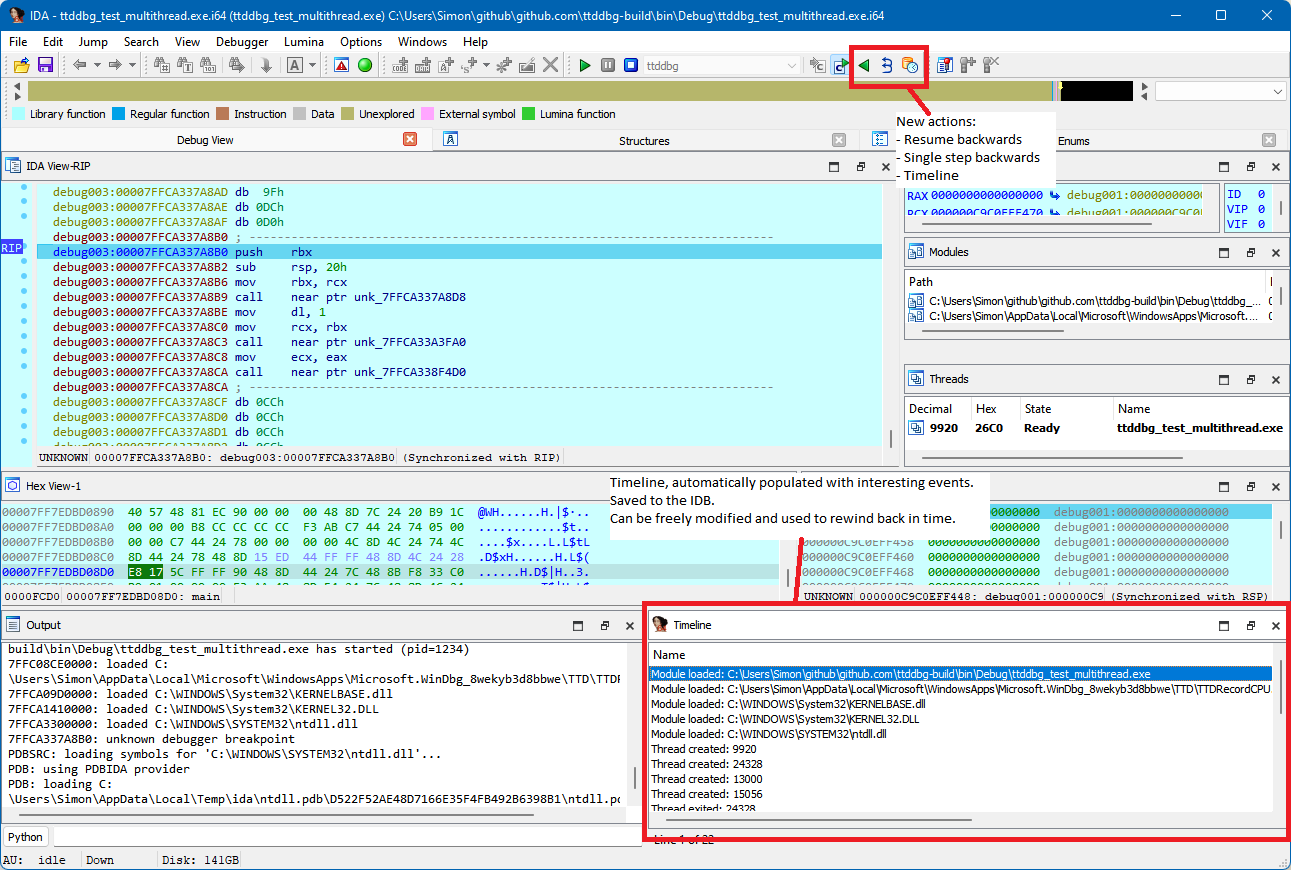 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
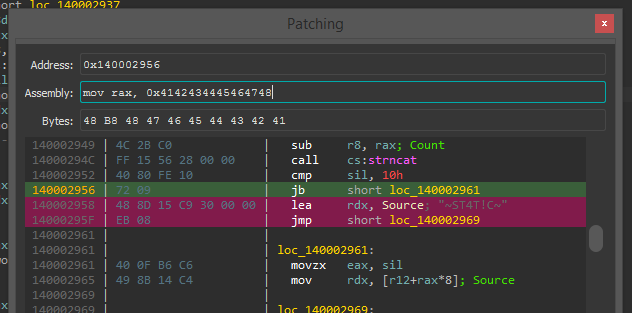 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
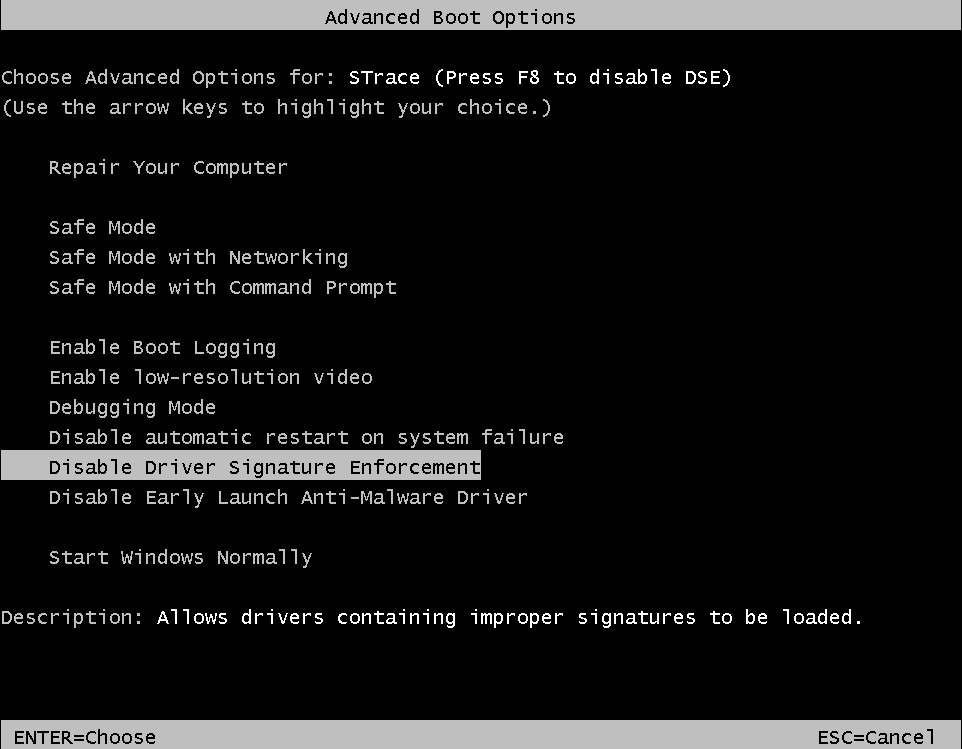 mandiant/strace
A DTrace on Windows Reimplementation
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API