

gf
 tomnomnom/gf
A wrapper around grep, to help you grep for things
code-analysisdynamic-code-analysisgeneral-purpose-utilities+7
tomnomnom/gfA wrapper around grep, to help you grep for things
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
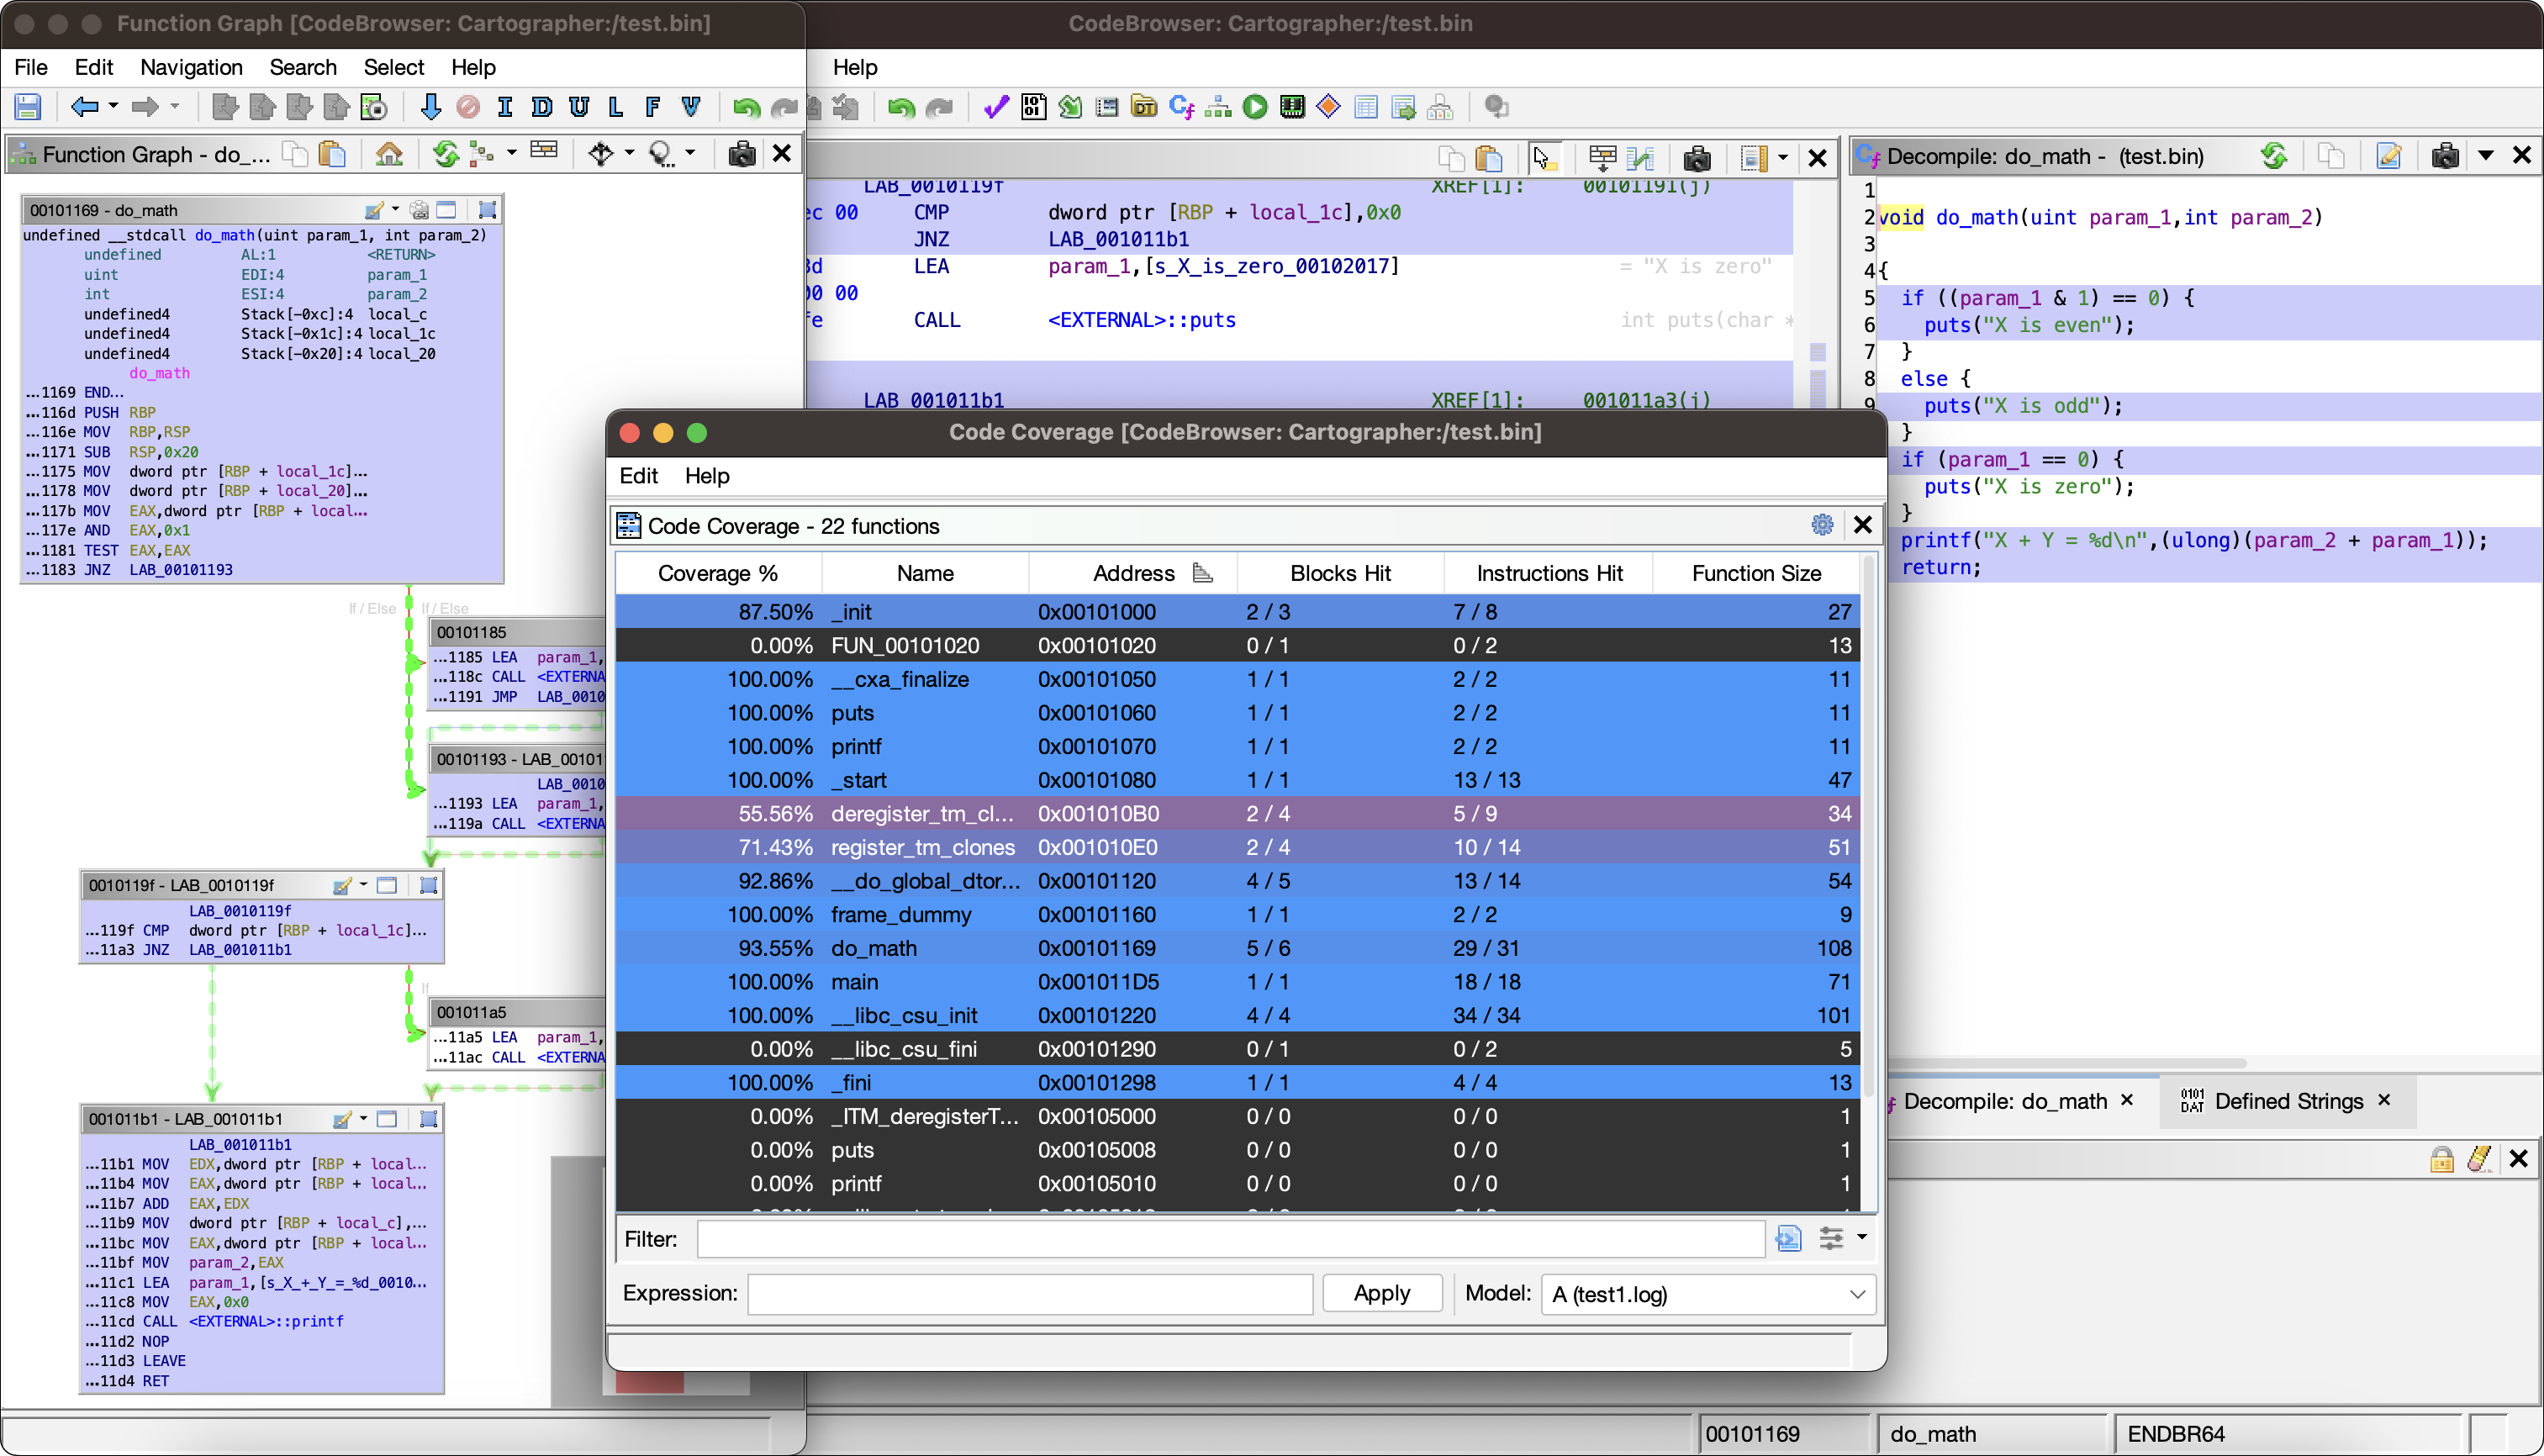 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
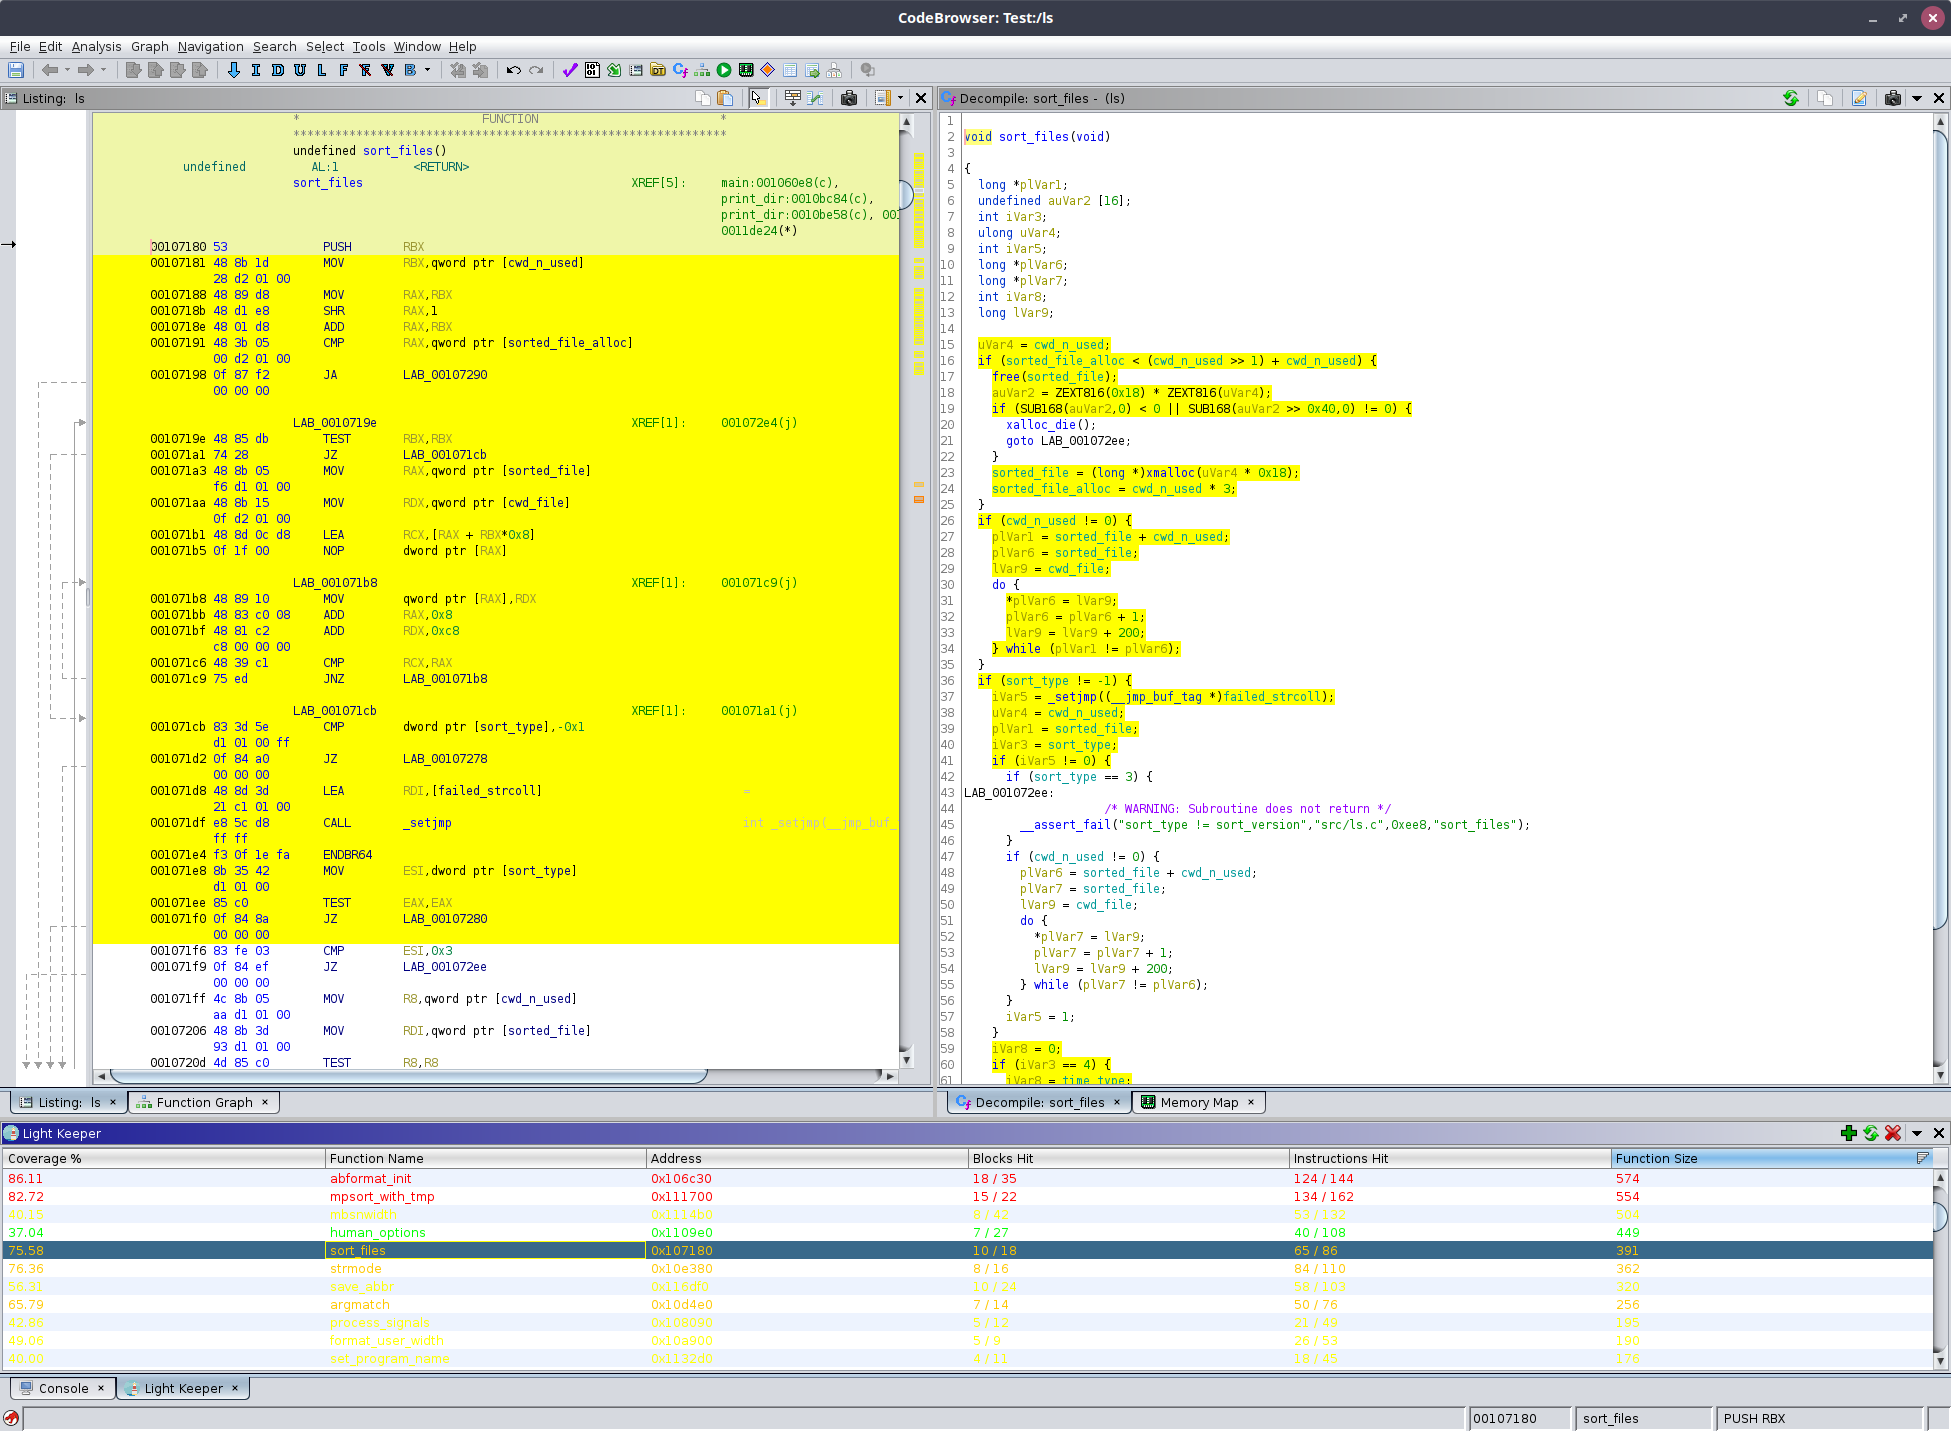 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
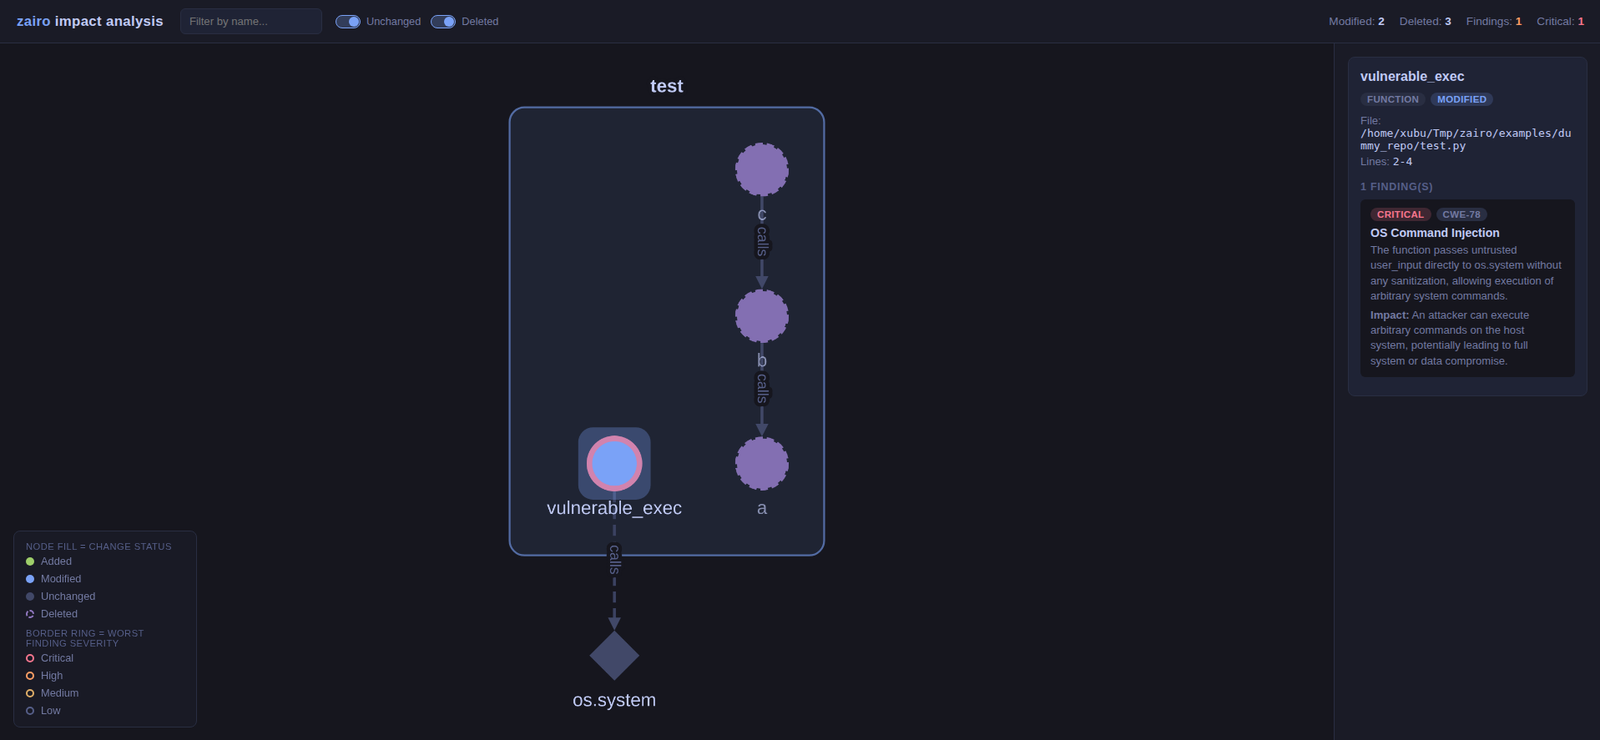 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)
 eset/malware-research
Code written as part of our various malware investigations
 neurosaki987/tvm-recover
Devirtualizes Tencent VM .tvm0 sections: lifts VM handlers to guest-level listings and LLVM IR, recovers CFG and dispatch, and patches recovered code…
 lmacken/pyrasite
Inject code into running Python processes
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface