
STrace
 mandiant/strace
A DTrace on Windows Reimplementation
debuggersdynamic-code-analysisincident-response+2
mandiant/straceA DTrace on Windows Reimplementation
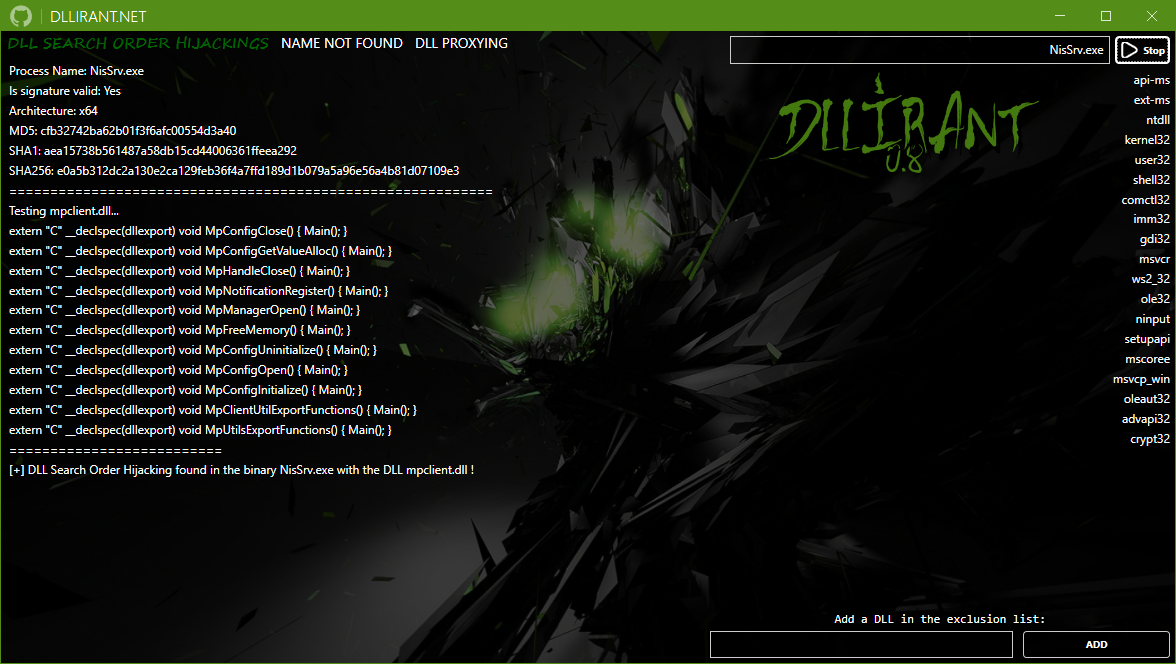 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
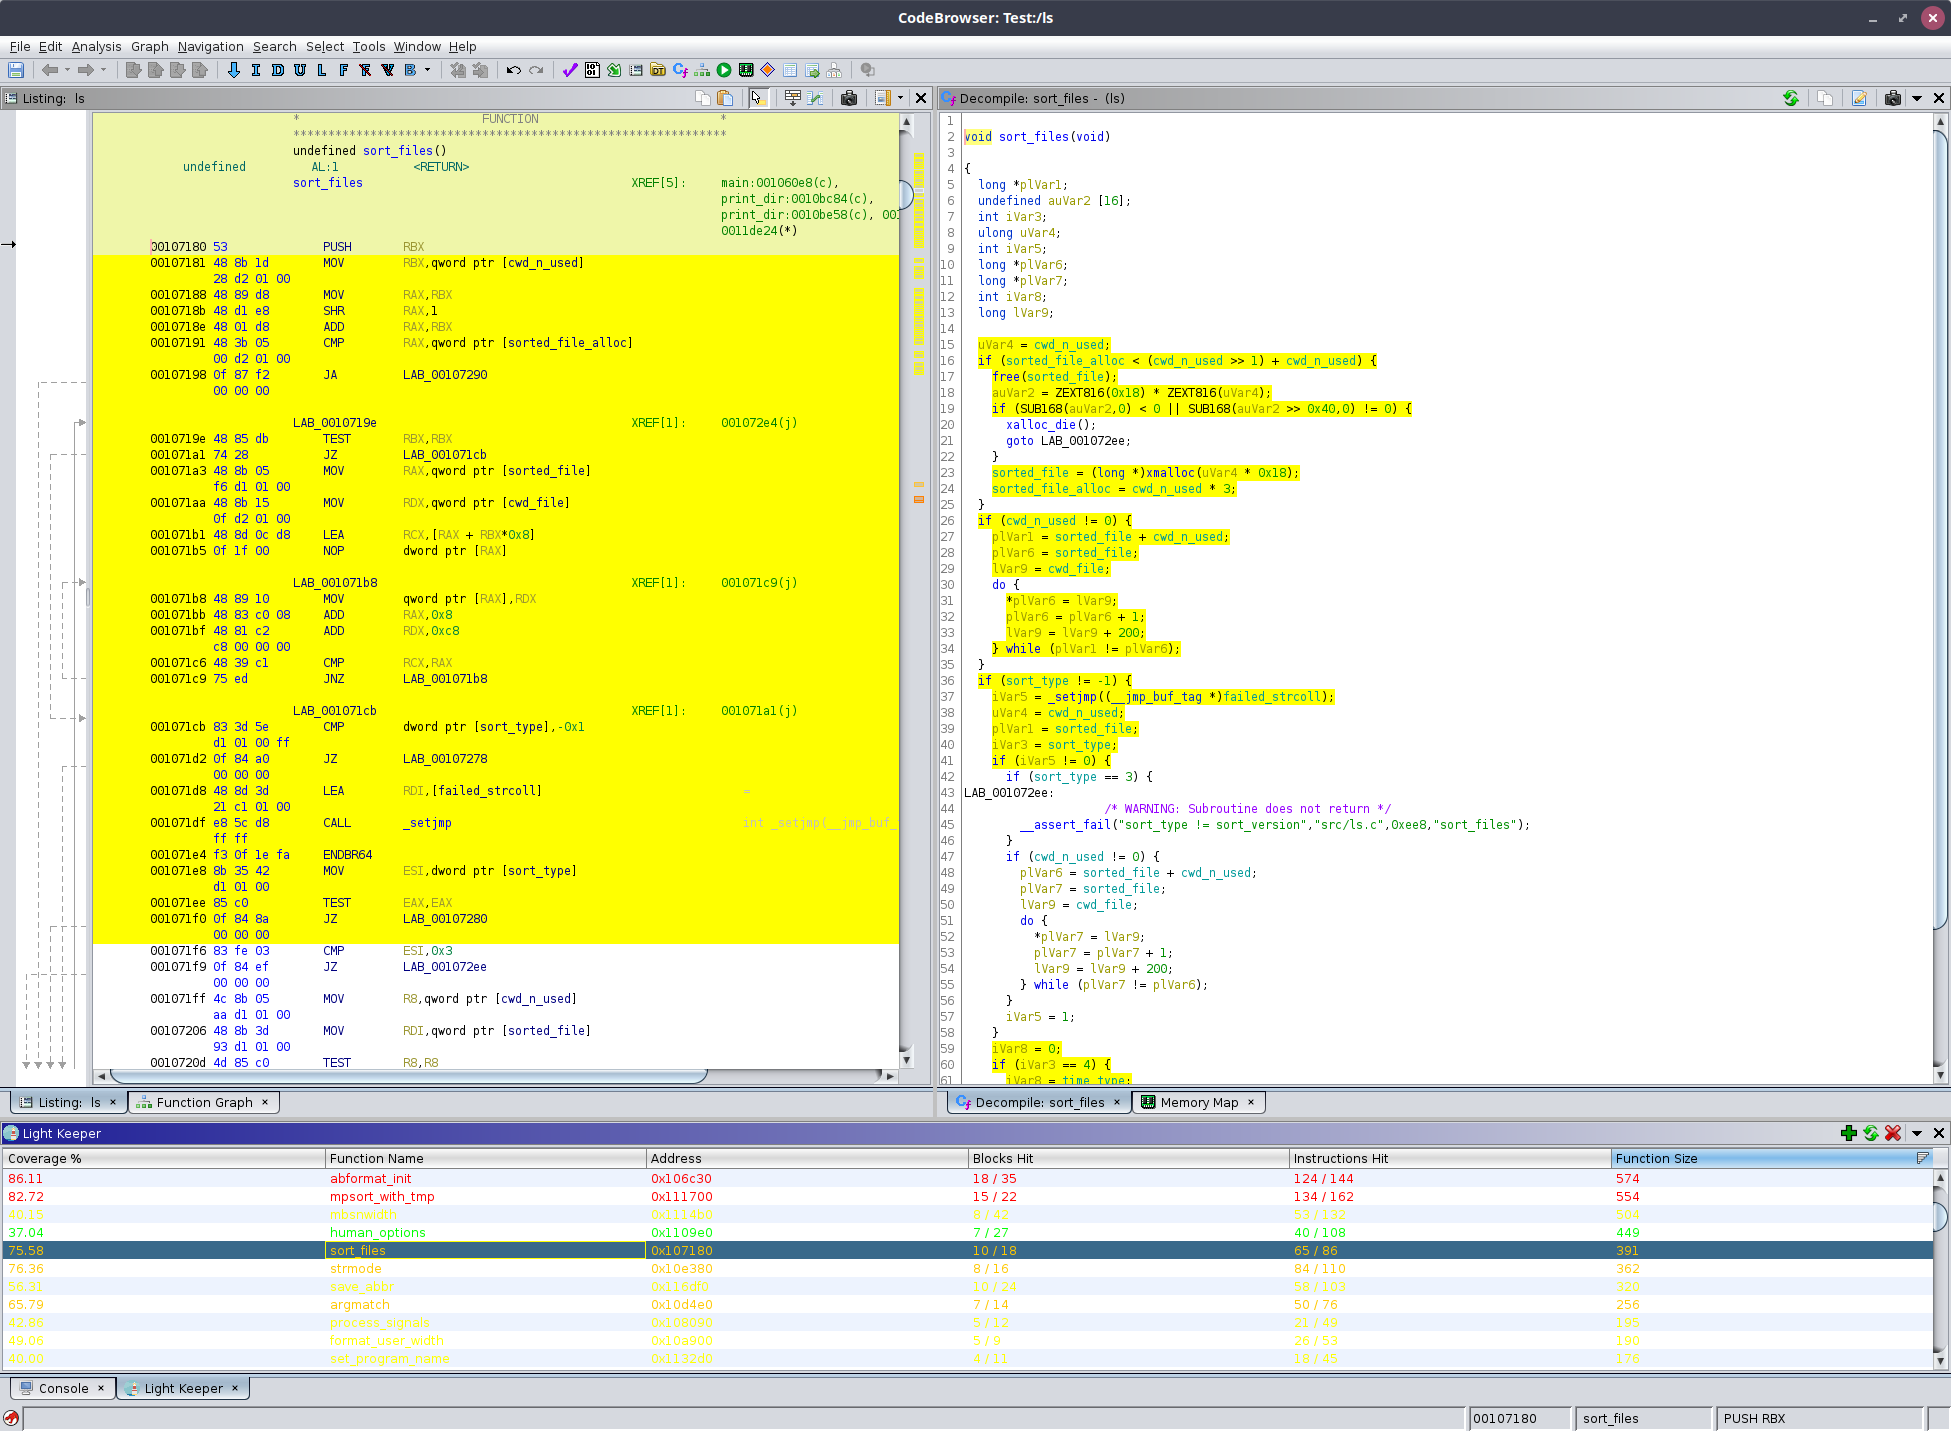 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 binsec/xyntia
Xyntia, the black-box deobfuscator
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU
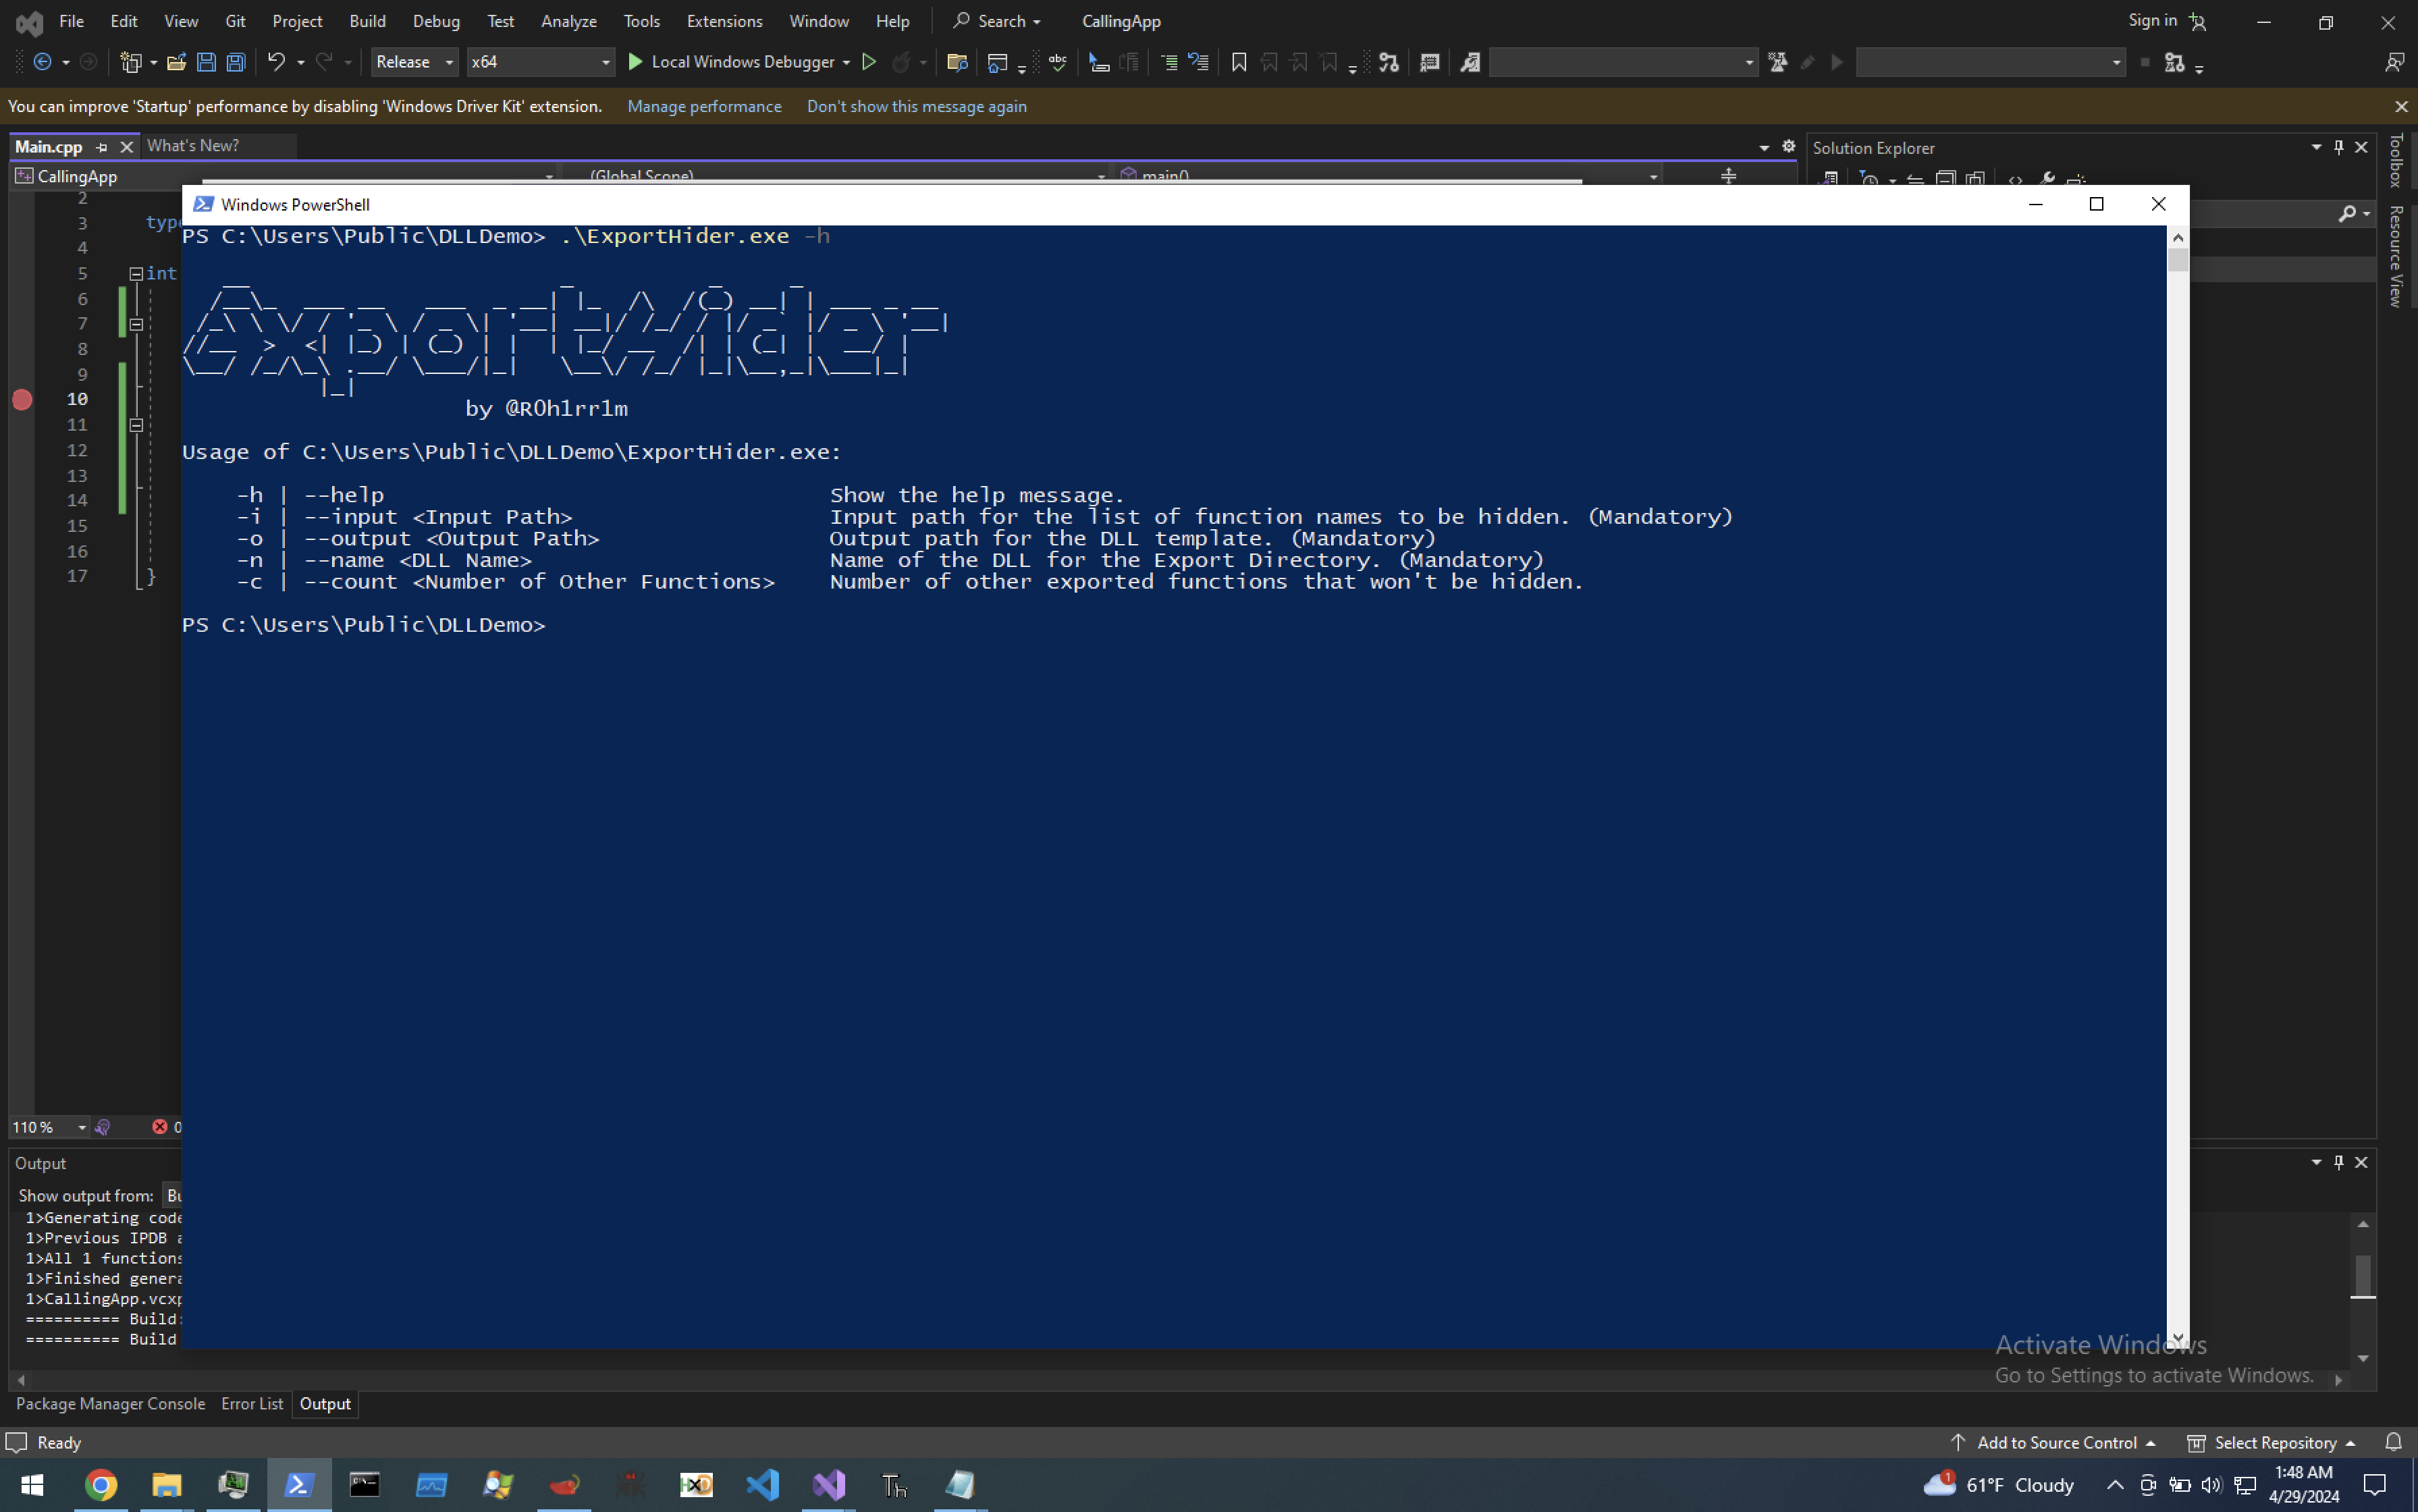 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
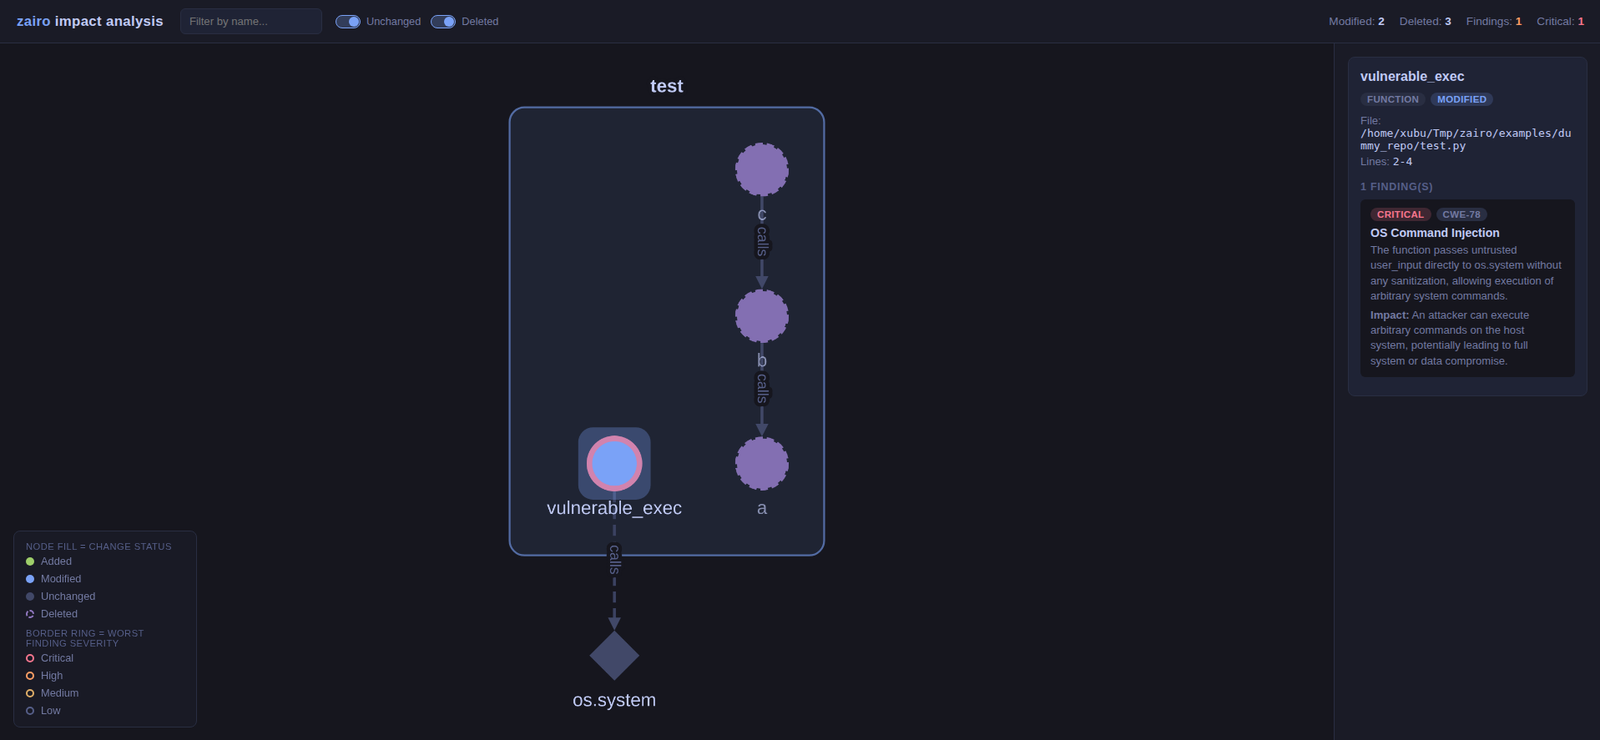 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
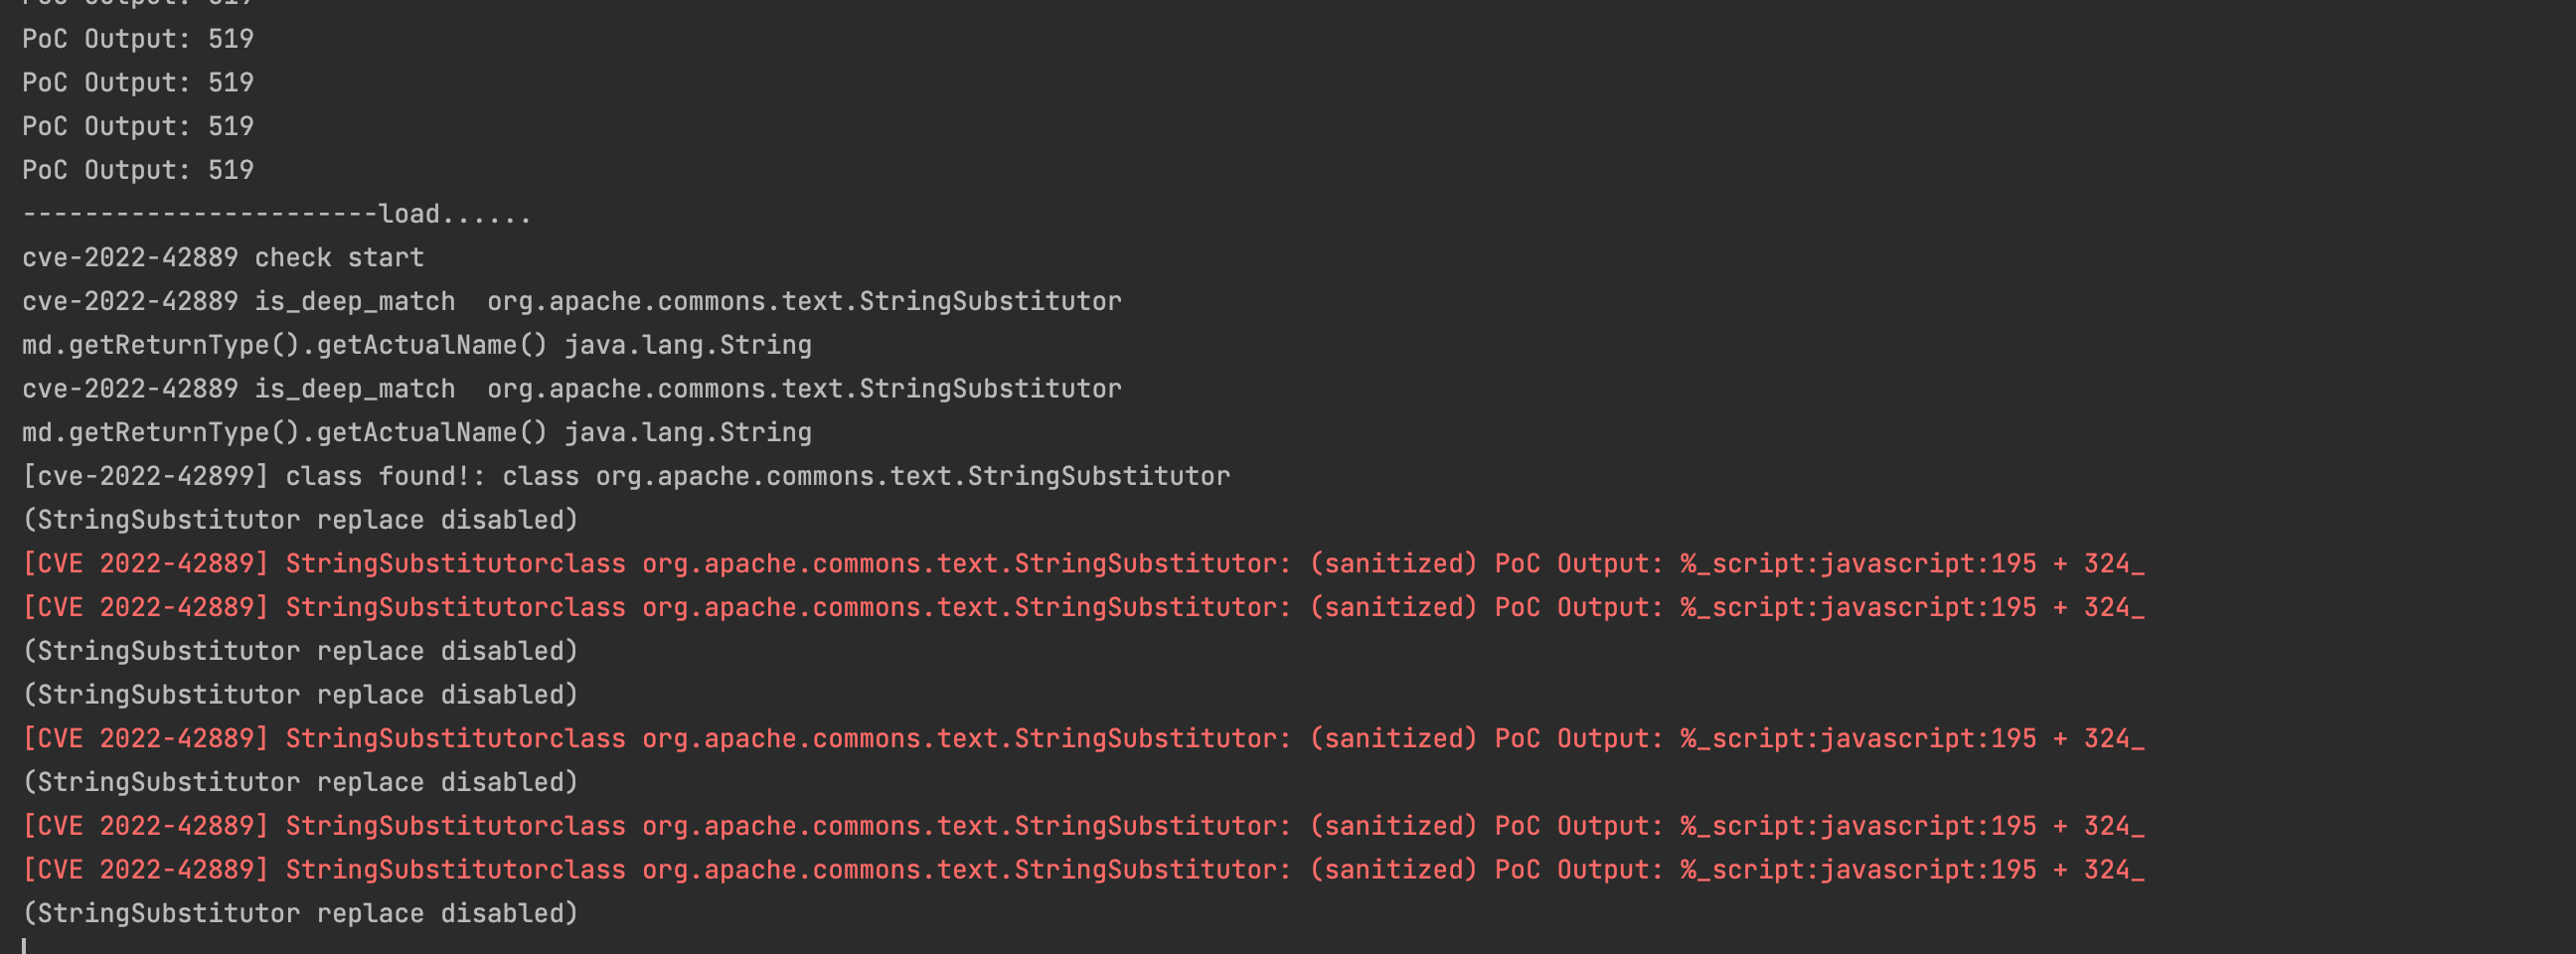 uk0/cve-2022-42889-intercept
通过 jvm 启动参数 以及 jps pid进行拦截非法参数
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…