
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
70 results
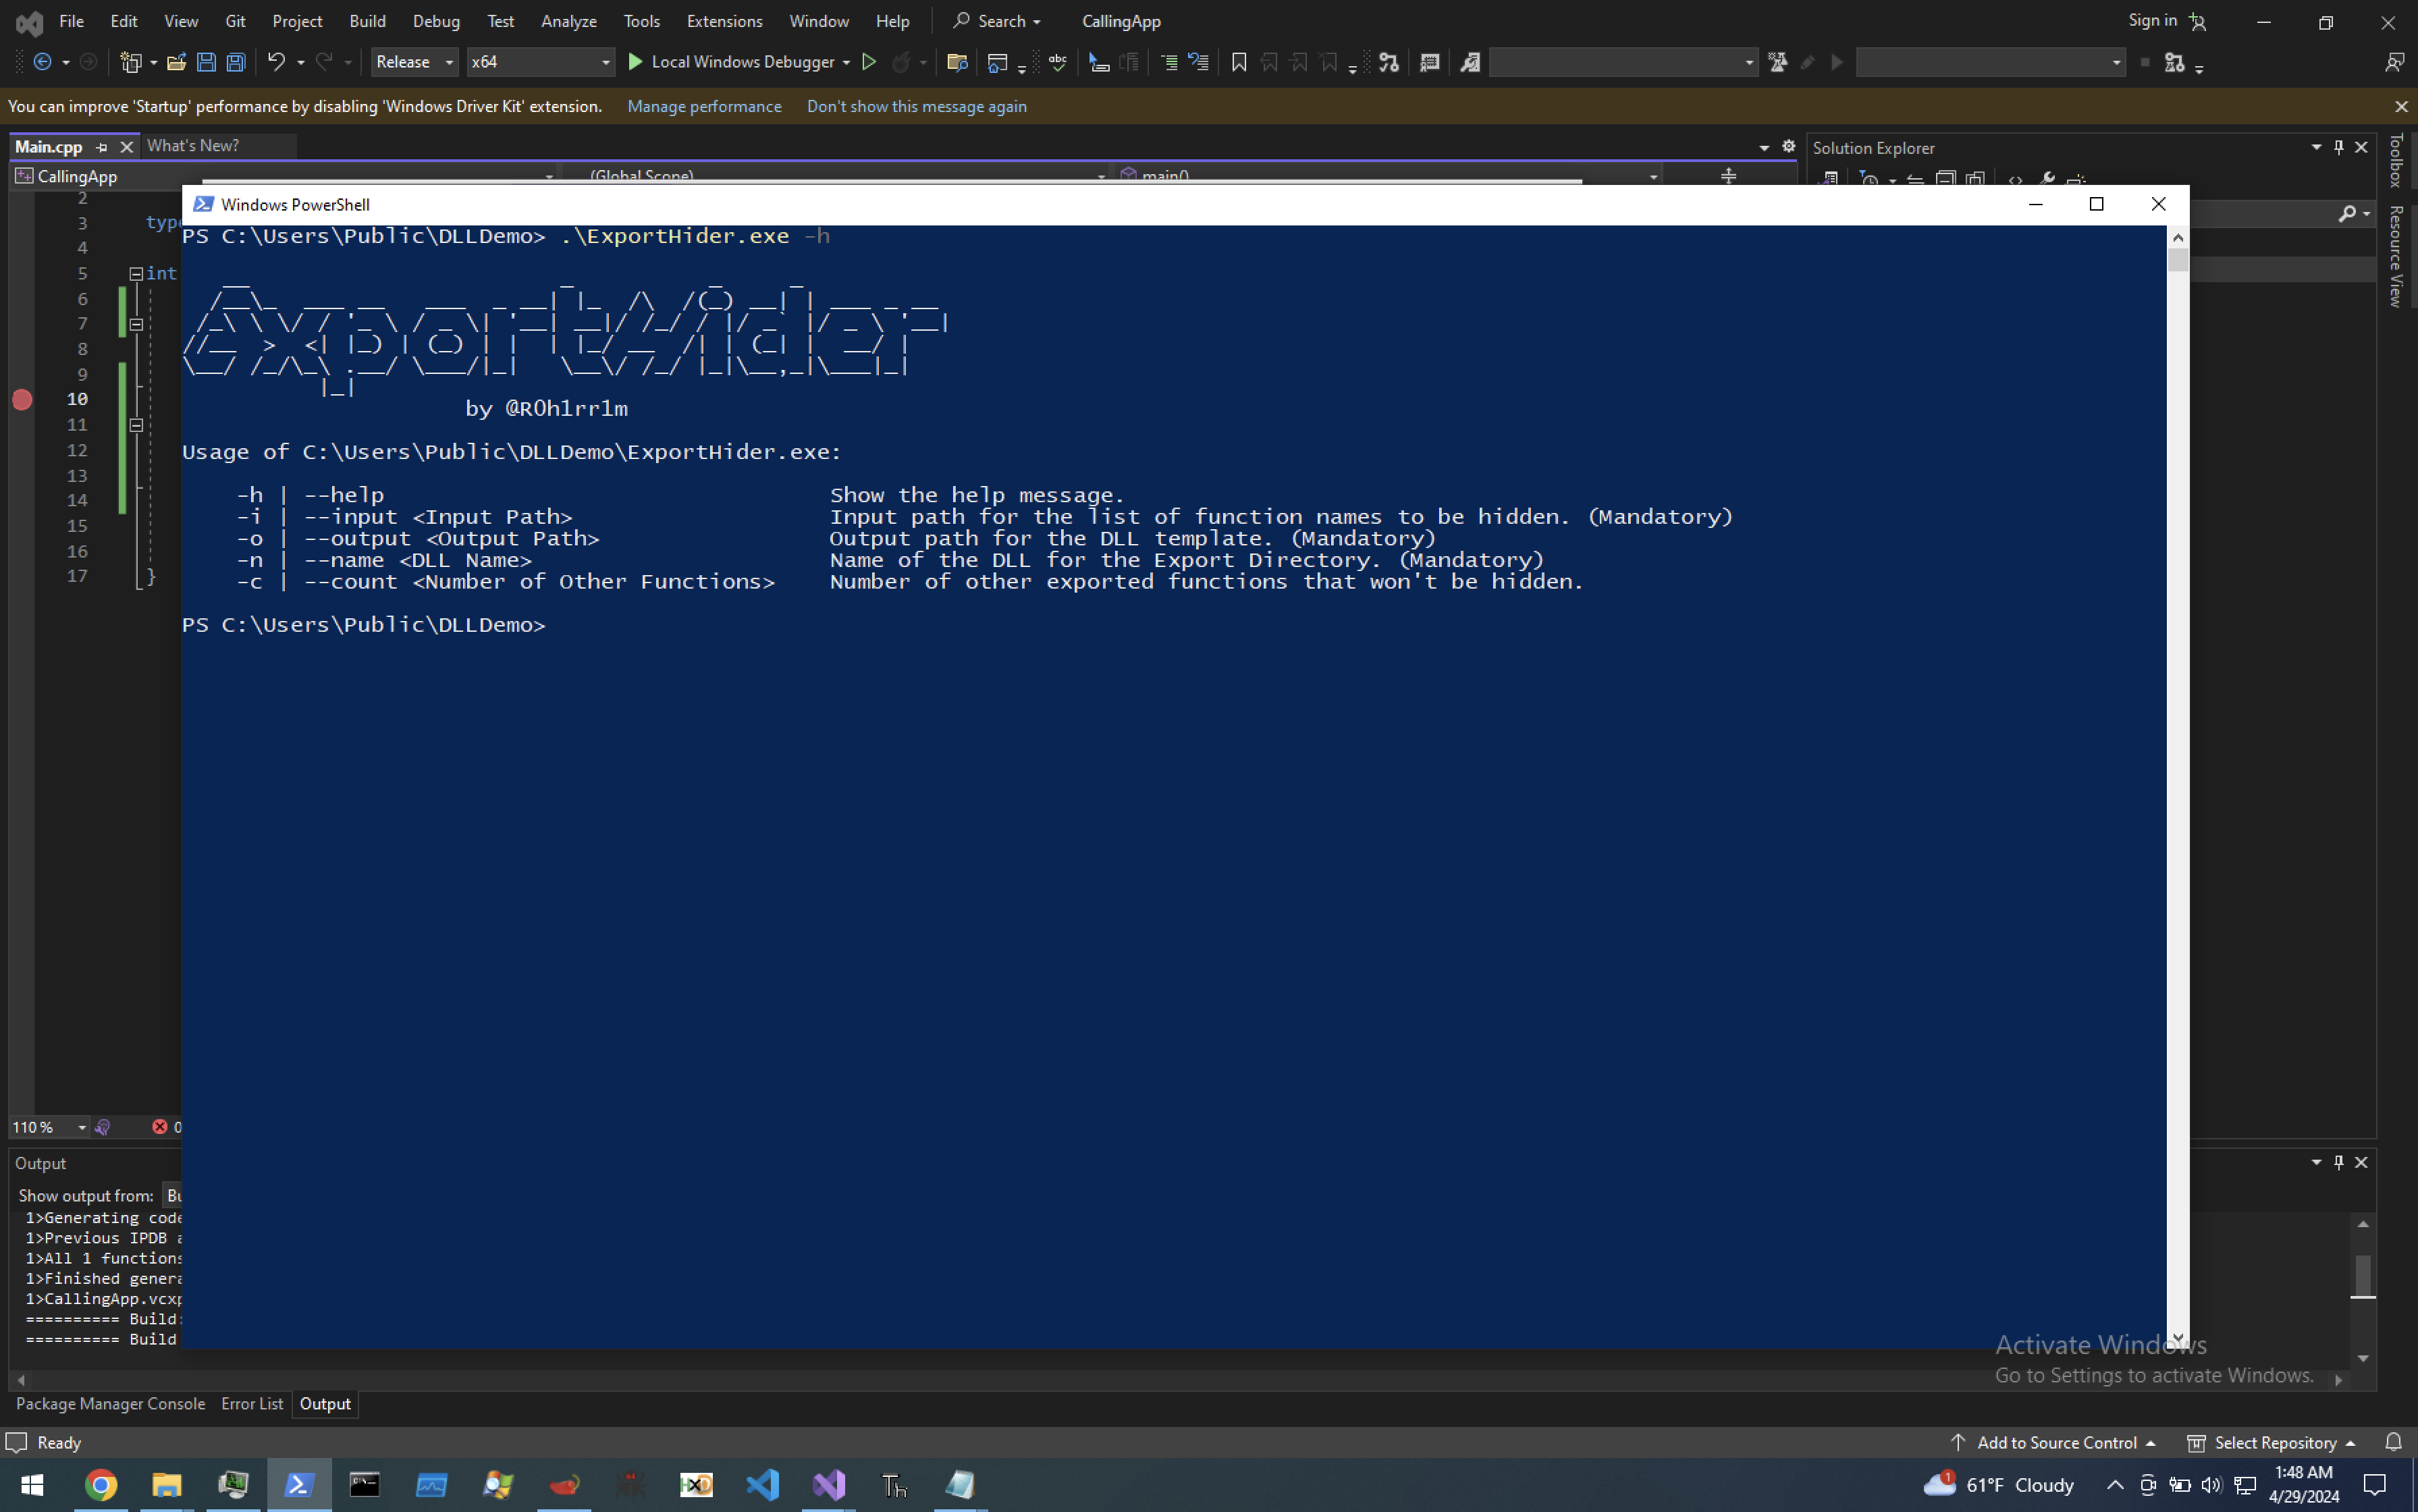
ExportHider preview

ExportHider

GitHubfrkngksl/exporthider

ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
binary-analysisdynamic-code-analysisexploitation+4
36
5 months ago
ghidra_stack_strings preview

ghidra_stack_strings

GitHubzxgio/ghidra_stack_strings

A script to detect stack-strings by using emulation (leveraging Unicorn)
binary-analysisdynamic-code-analysismalware-analysis+1
3510 months ago
dapr preview

dapr

GitHubnccgroup/dapr

Driver Attack Platform for Linux

android-securitybinary-exploitationdebuggers+5
197 years ago
pesieve-go preview

pesieve-go

GitHubhasherezade/pesieve-go

Golang bindings for PE-sieve

binary-analysisdynamic-code-analysismalware-analysis+1
432 years ago
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

android-securitycryptographydynamic-analysis-sandboxing+8
1028 days ago
Veridiff preview

Veridiff

GitHubveridiff/veridiff

Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
binary-analysisbinary-exploitationcode-analysis+7
65 days ago
android_demystification_toolbox preview

android_demystification_toolbox

GitHubnccgroup/android_demystification_toolbox

ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
android-securitybinary-analysiscode-analysis+5
82 years ago
mauidll preview

mauidll

GitHubbishopfox/mauidll

Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
android-securitybinary-analysisdynamic-code-analysis+4
112 days ago
ptrace preview

ptrace

GitHubwhatswrongandwhy/ptrace

Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
binary-analysisdebuggersdynamic-code-analysis+2
2 months ago
frida-stalker-NtStrace preview

frida-stalker-NtStrace

GitHubgmh5225/frida-stalker-ntstrace

frida-stalker based system call tracer on windows(x64).
binary-analysisdebuggersdynamic-analysis-sandboxing+4
33 years ago
DocViewerExploitApp preview

DocViewerExploitApp

GitHubtinopreter/docviewerexploitapp

This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
android-securitybinary-exploitationdynamic-code-analysis+6
1 year ago
de4dot preview
Archived

de4dot

GitHubde4dot/de4dot

.NET deobfuscator and unpacker.

binary-analysisdynamic-code-analysismalware-analysis+2
7.4k6 years ago
ddc preview

ddc

GitHubejfkdev/ddc

DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
android-securitybinary-analysiscode-analysis+6
3257 days ago
vmp2 preview
Archived

vmp2

GitHubaftermathlabs/vmp2

Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
binary-analysiscode-analysisdynamic-code-analysis+3
13110 months ago
peafl64 preview
Archived

peafl64

GitHubsentinel-one/peafl64

Static Binary Instrumentation tool for Windows x64 executables
binary-analysisdynamic-code-analysisfuzzing+2
2061 year ago
path-auditor preview
Archived

path-auditor

GitHubgoogle/path-auditor

Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…

binary-analysisdynamic-code-analysisexploitation+3
2505 years ago
Previous1234Next