
windbg_js_scripts
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
binary-analysisdebuggersdynamic-code-analysis+3
2442 years ago
hugsy/windbg_js_scriptsToy scripts for playing with WinDbg JS API
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 binsec/xyntia
Xyntia, the black-box deobfuscator
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
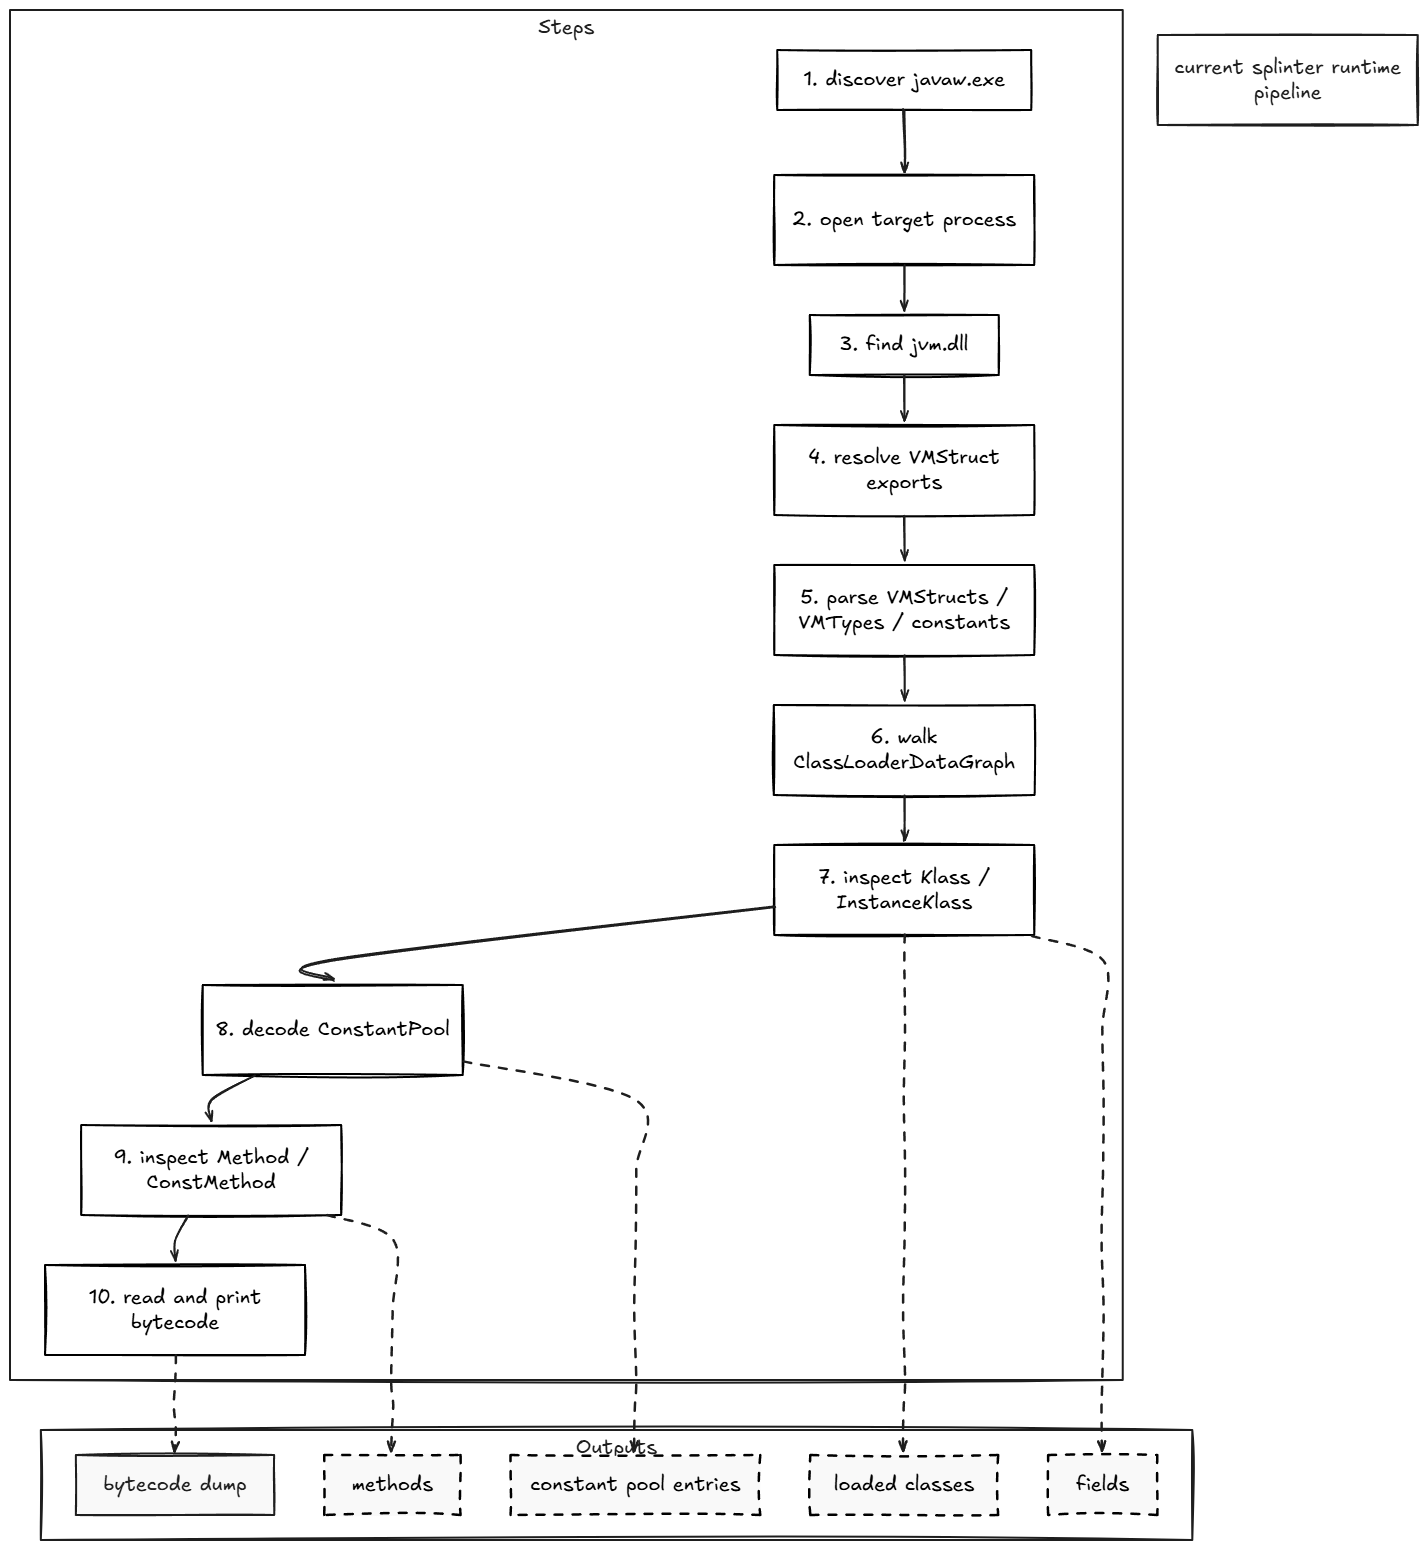 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
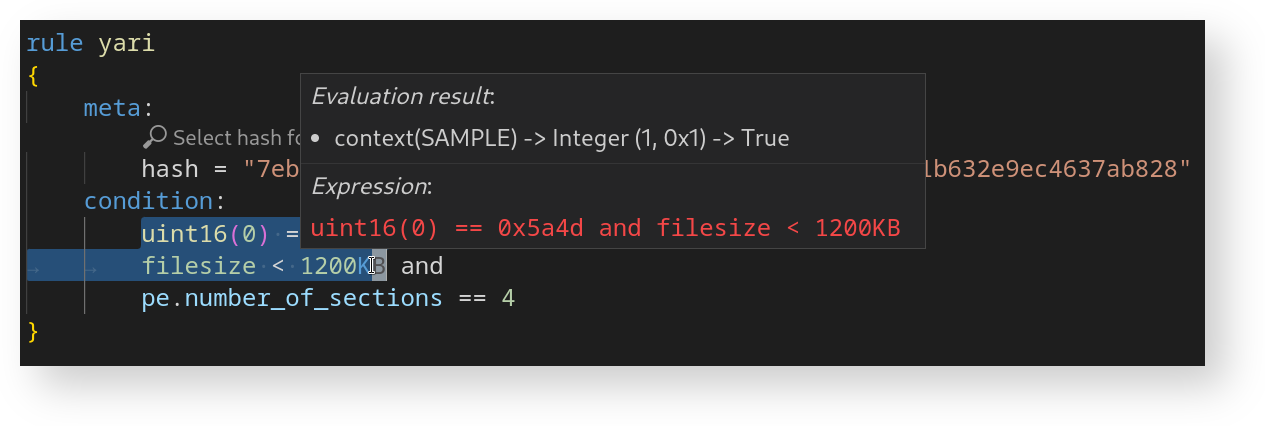 avast/yari
YARI is an interactive debugger for YARA Language.
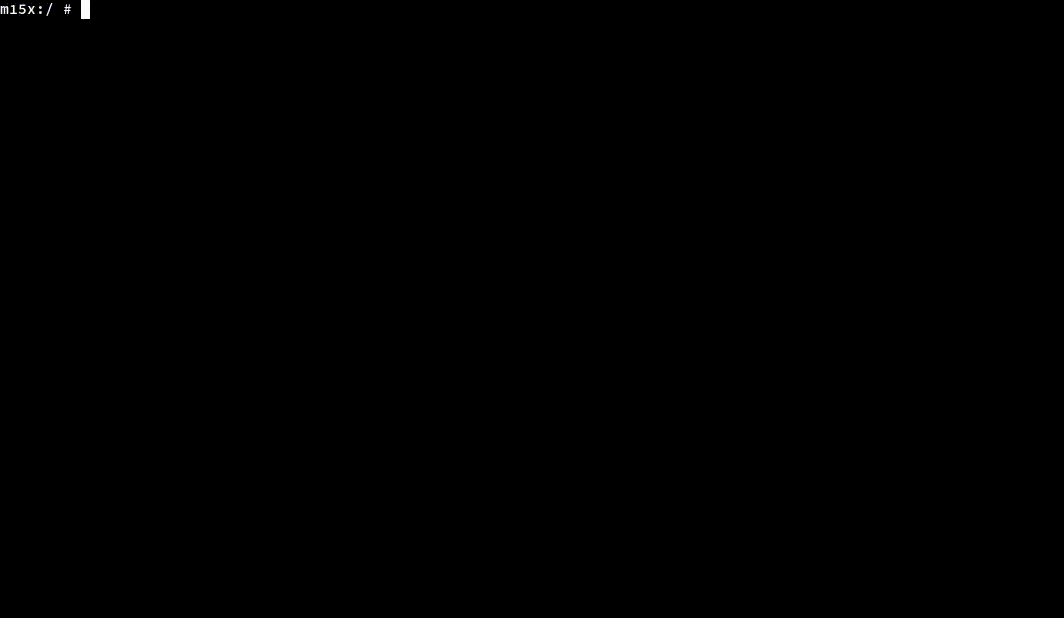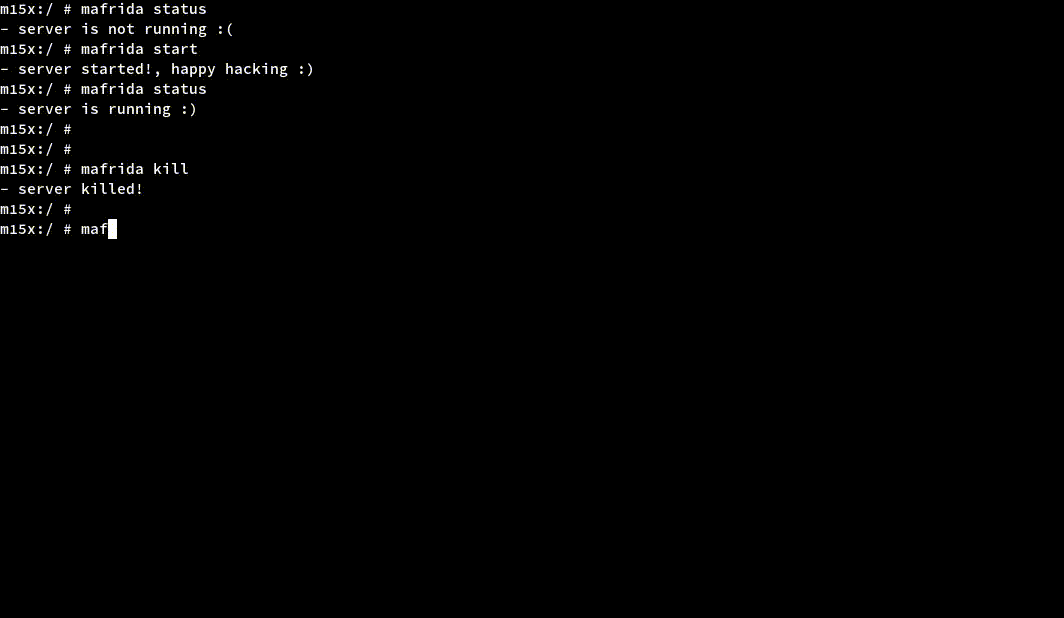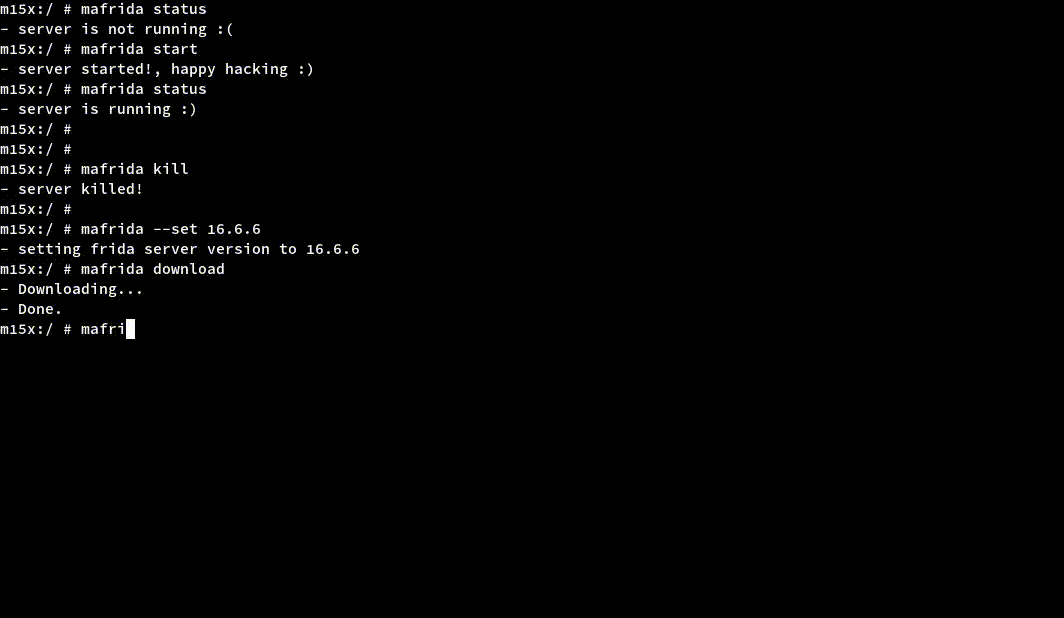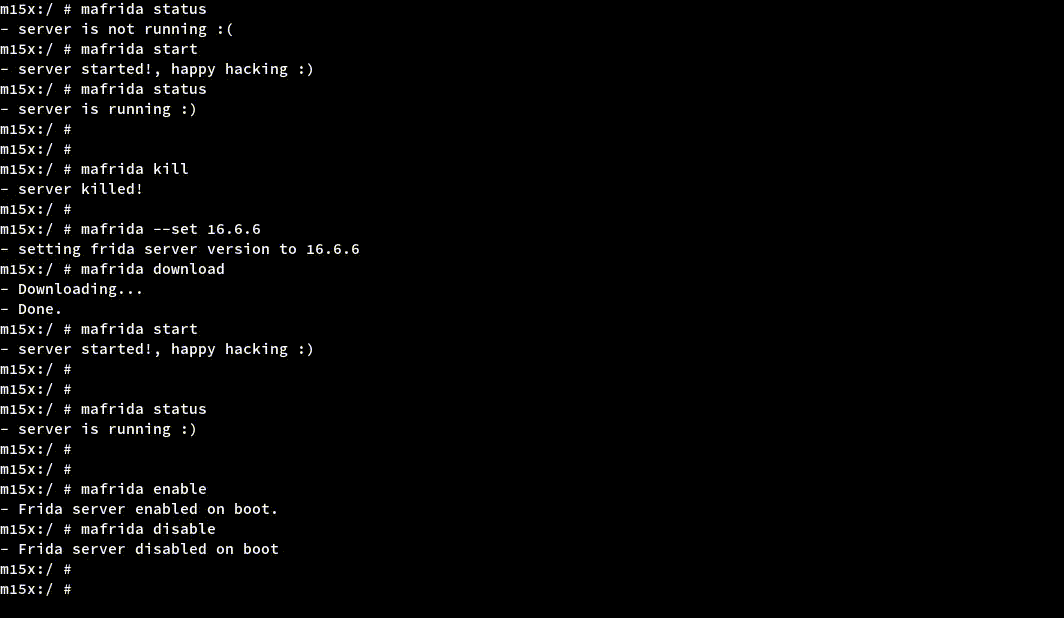 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
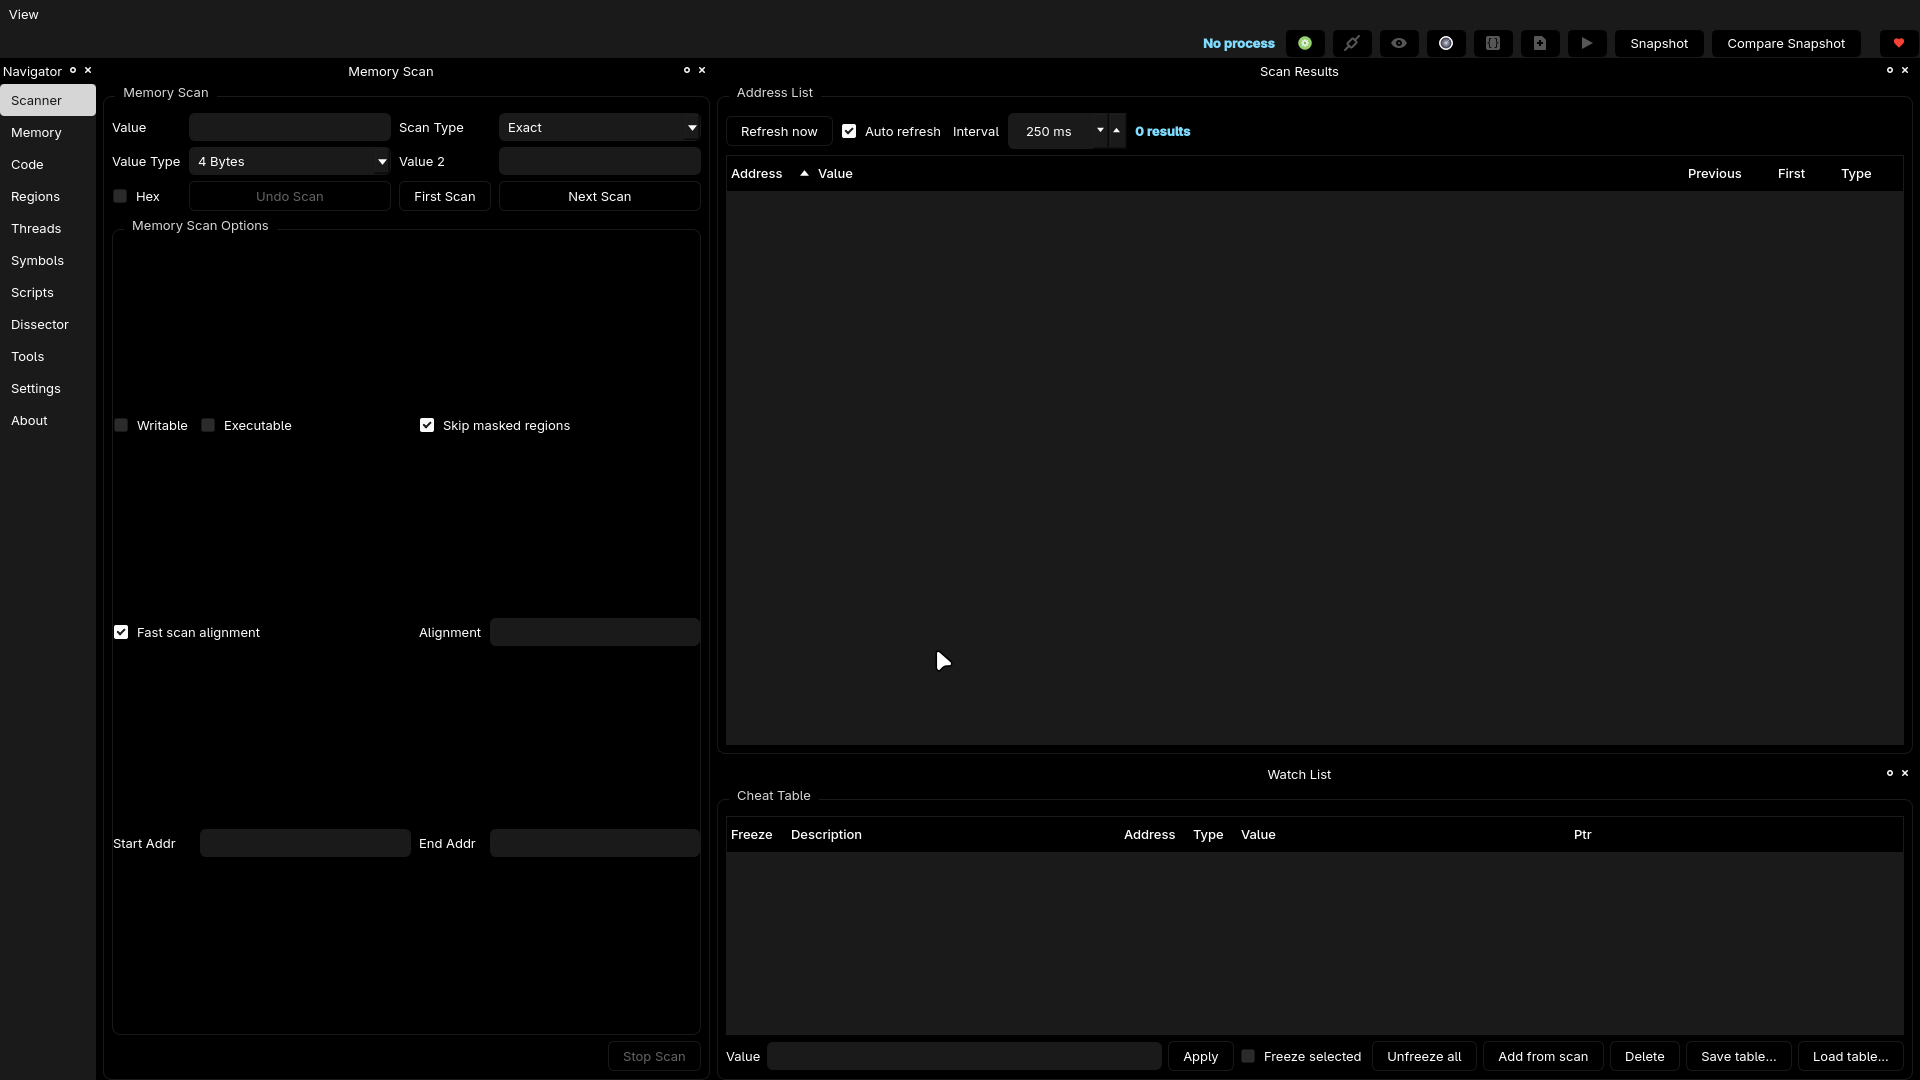 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…