
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
56 results
lightkeeper preview

lightkeeper

GitHubworksbutnottested/lightkeeper

Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.

binary-analysiscode-analysisdynamic-code-analysis+1
76
3 months ago
dezlock-dump preview

dezlock-dump

GitHubdougwithseismic/dezlock-dump

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
binary-analysisdebuggersdynamic-code-analysis+6
876 months ago
fnprint preview

fnprint

GitHub1rhino2/fnprint

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
binary-analysisdynamic-code-analysisfirmware-analysis+3
445 days ago
yari preview

yari

GitHubavast/yari

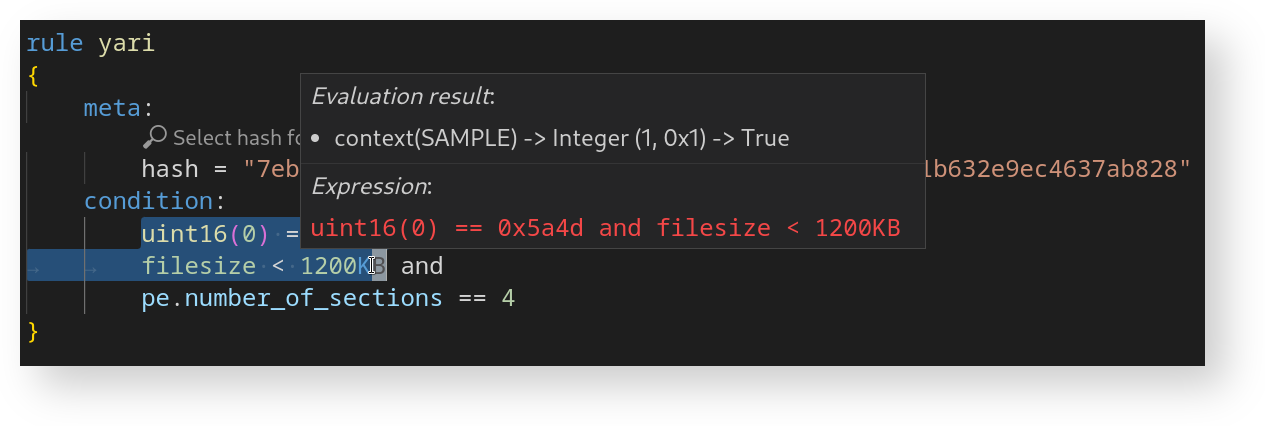
YARI is an interactive debugger for YARA Language.
binary-analysiscode-analysisdebuggers+2
901 year ago
ComfyEngine preview

ComfyEngine

GitHubkashithecomfy/comfyengine

ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
binary-analysisdebuggersdynamic-code-analysis+5
628 months ago
MaFrida preview

MaFrida

GitHubtheshinigami/mafrida

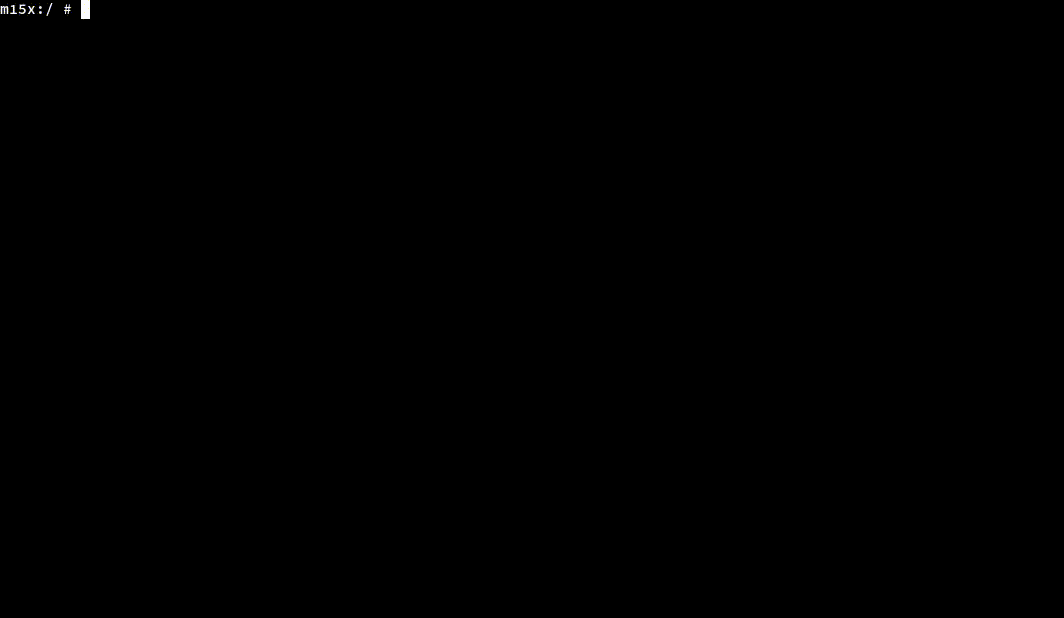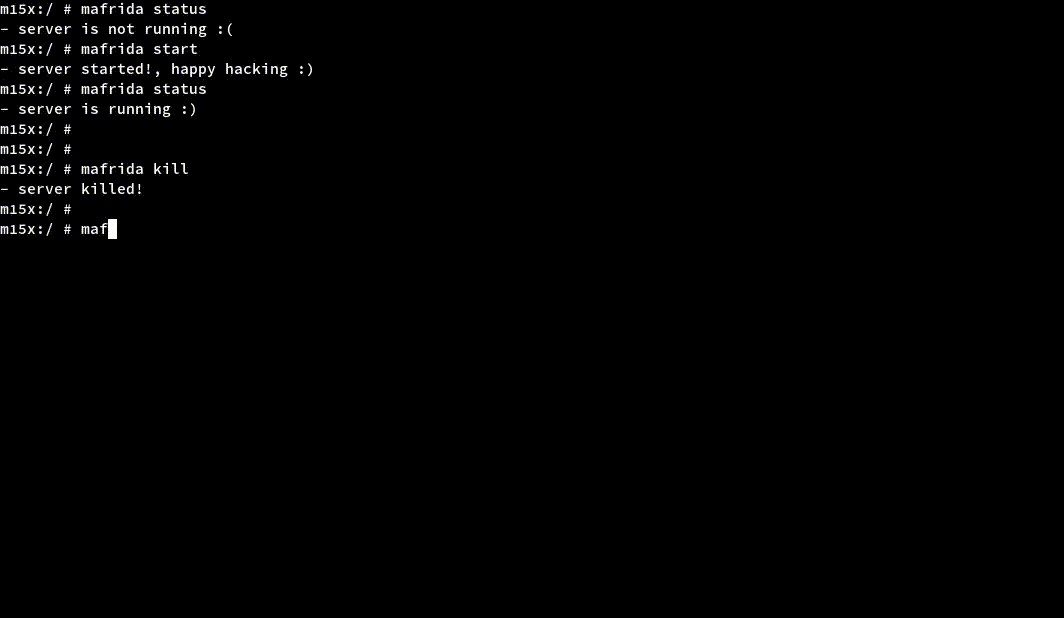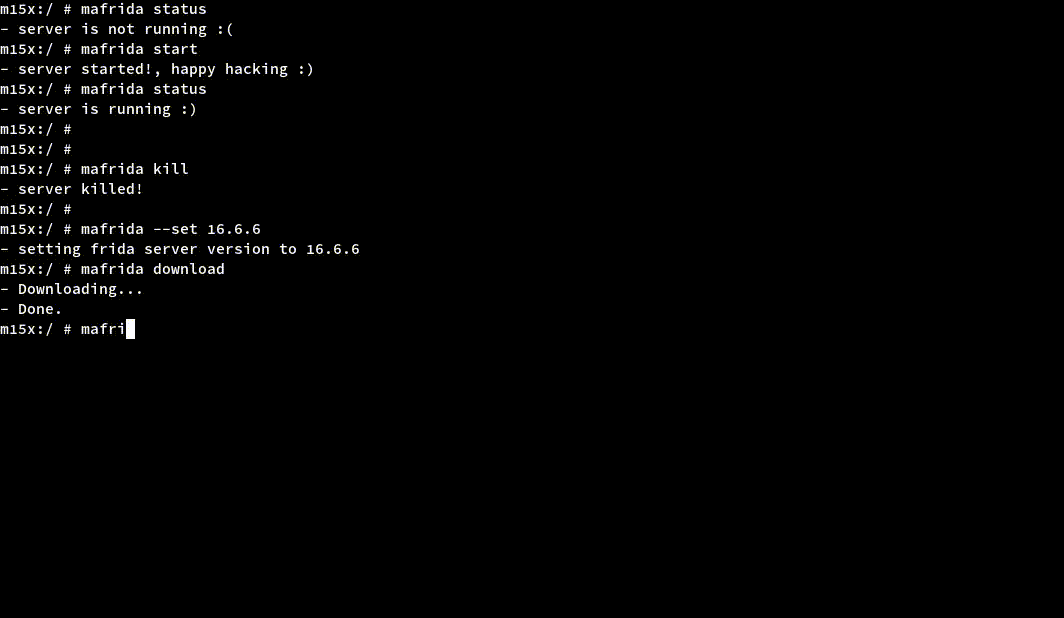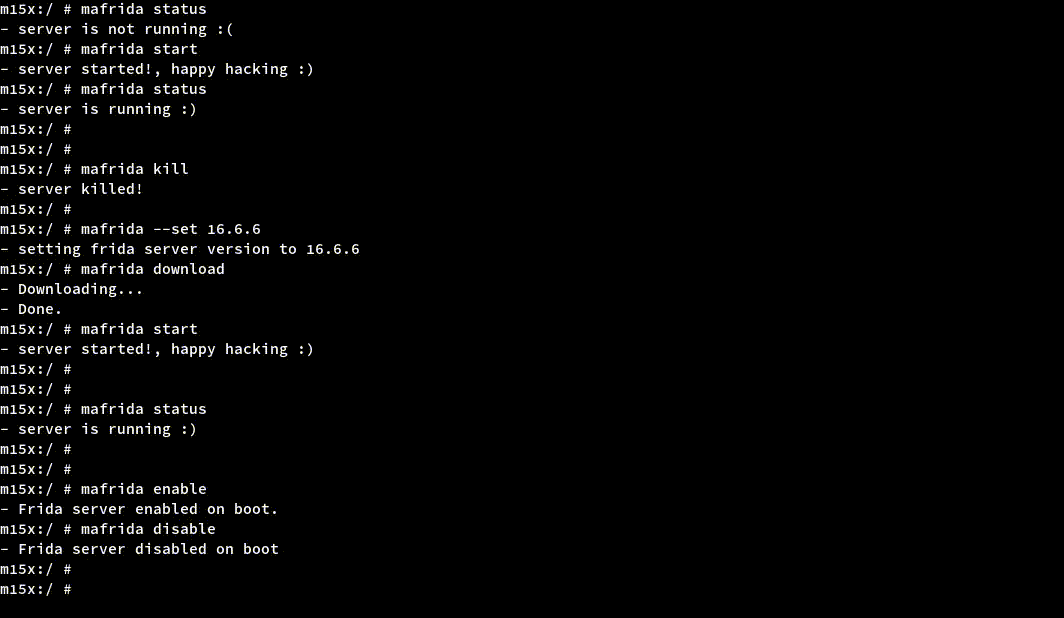
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
android-securitydynamic-analysis-sandboxingdynamic-code-analysis+5
402 months ago
ifuncd-up preview

ifuncd-up

GitHubrobertdfrench/ifuncd-up

GNU IFUNC is the real culprit behind CVE-2024-3094
binary-analysisdynamic-code-analysiseducation+5
614 months ago
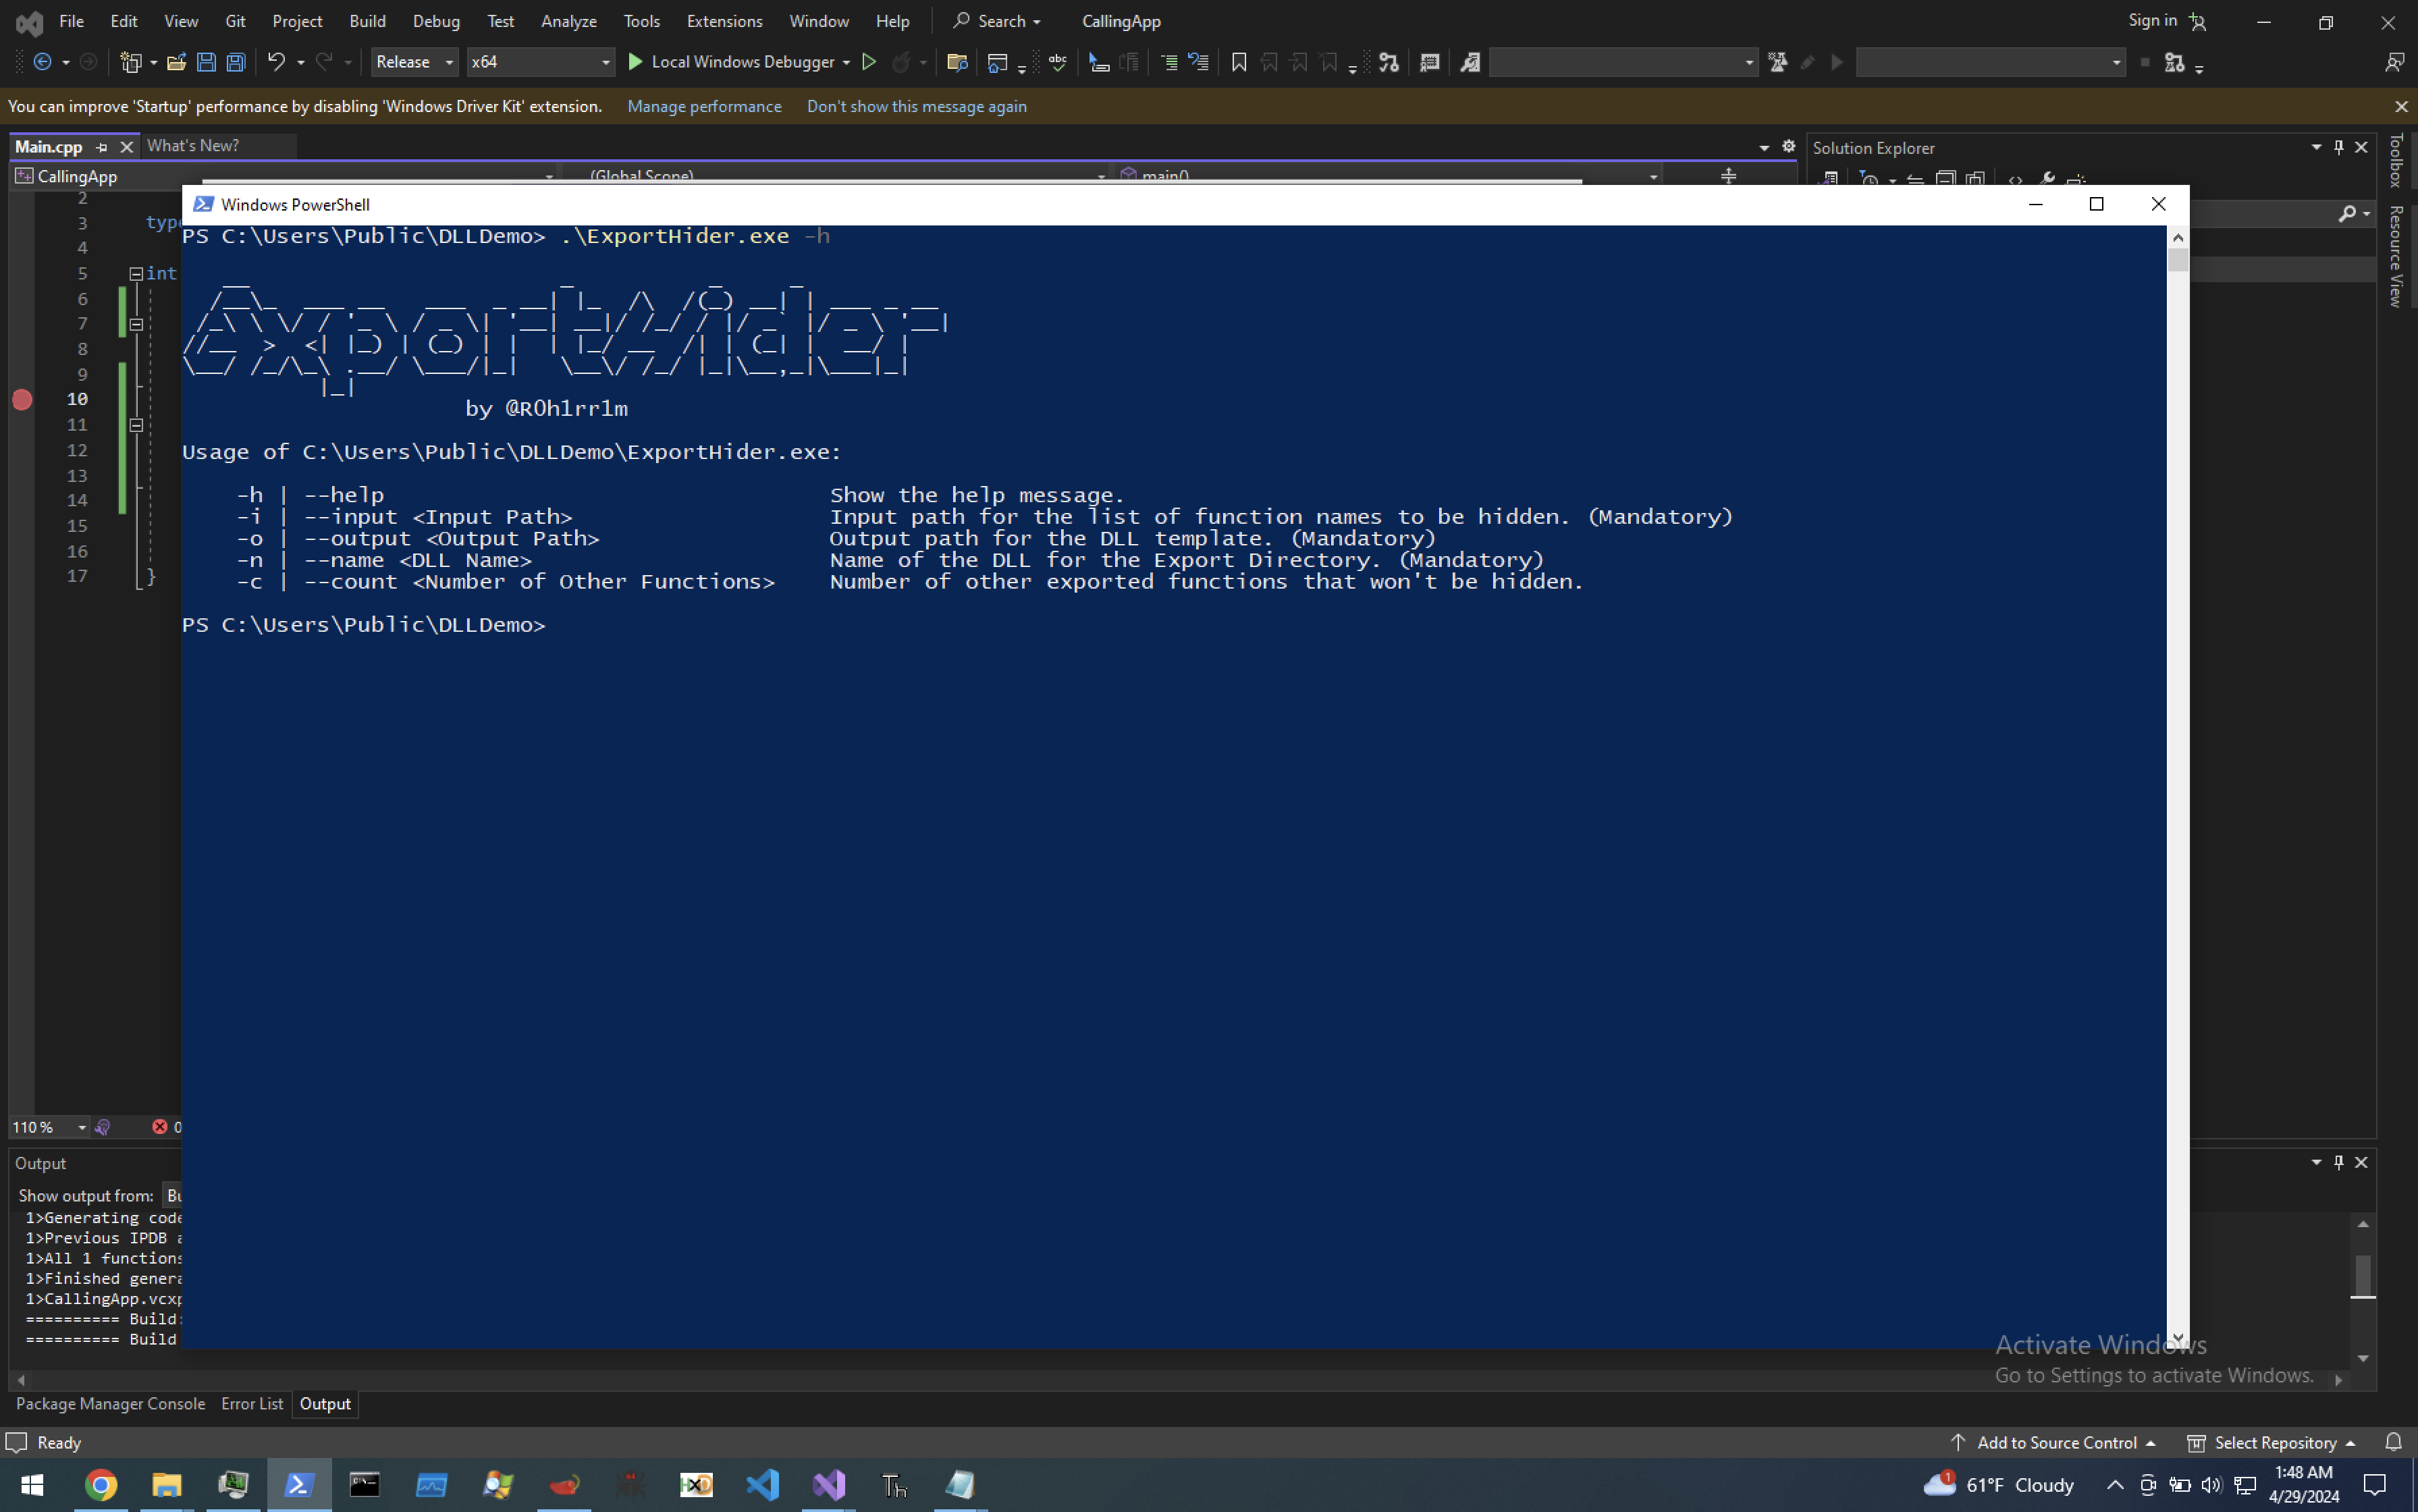
ExportHider preview

ExportHider

GitHubfrkngksl/exporthider

ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.

binary-analysisdynamic-code-analysisexploitation+4
335 months ago
ida_bochs_windows preview

ida_bochs_windows

GitHubtherealdreg/ida_bochs_windows

Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
binary-analysisdebuggersdynamic-code-analysis+1
623 years ago
dapr preview

dapr

GitHubnccgroup/dapr

Driver Attack Platform for Linux

android-securitybinary-exploitationdebuggers+5
196 years ago
ghidra_stack_strings preview

ghidra_stack_strings

GitHubzxgio/ghidra_stack_strings

A script to detect stack-strings by using emulation (leveraging Unicorn)
binary-analysisdynamic-code-analysismalware-analysis+1
359 months ago
pesieve-go preview

pesieve-go

GitHubhasherezade/pesieve-go

Golang bindings for PE-sieve
binary-analysisdynamic-code-analysismalware-analysis+1
432 years ago
android_demystification_toolbox preview

android_demystification_toolbox

GitHubnccgroup/android_demystification_toolbox

ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
android-securitybinary-analysiscode-analysis+5
82 years ago
one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow preview

one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow

GitHubhunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow

Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
android-securitydynamic-code-analysiseducation+3
1 month ago
ptrace preview

ptrace

GitHubwhatswrongandwhy/ptrace

Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
binary-analysisdebuggersdynamic-code-analysis+2
1 month ago
DocViewerExploitApp preview

DocViewerExploitApp

GitHubtinopreter/docviewerexploitapp

This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
android-securitybinary-exploitationdynamic-code-analysis+6
1 year ago
de4dot preview
Archived

de4dot

GitHubde4dot/de4dot

.NET deobfuscator and unpacker.

binary-analysisdynamic-code-analysismalware-analysis+2
7.4k6 years ago
vmp2 preview
Archived

vmp2

GitHubaftermathlabs/vmp2

Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…

binary-analysiscode-analysisdynamic-code-analysis+3
13210 months ago
Previous1234Next