
sleigh
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
binary-analysiscode-analysisdynamic-code-analysis+4
191
lifting-bits/sleighCMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
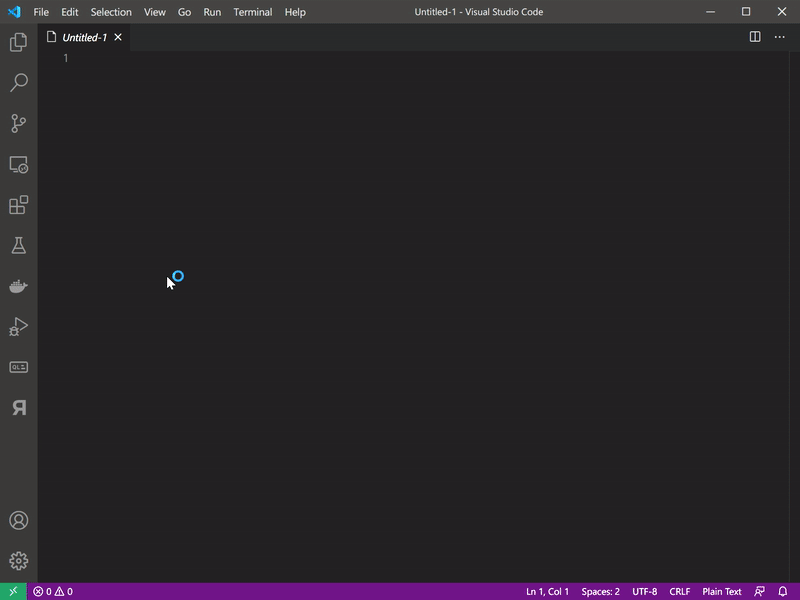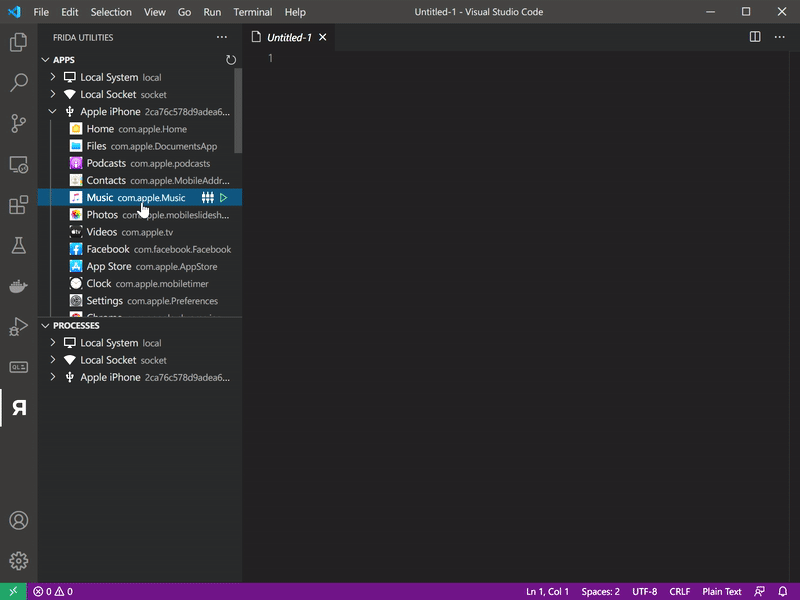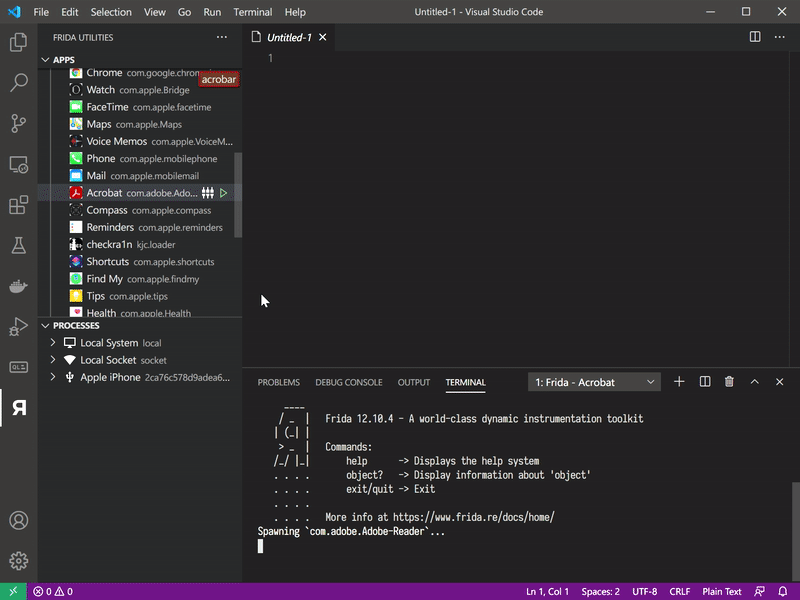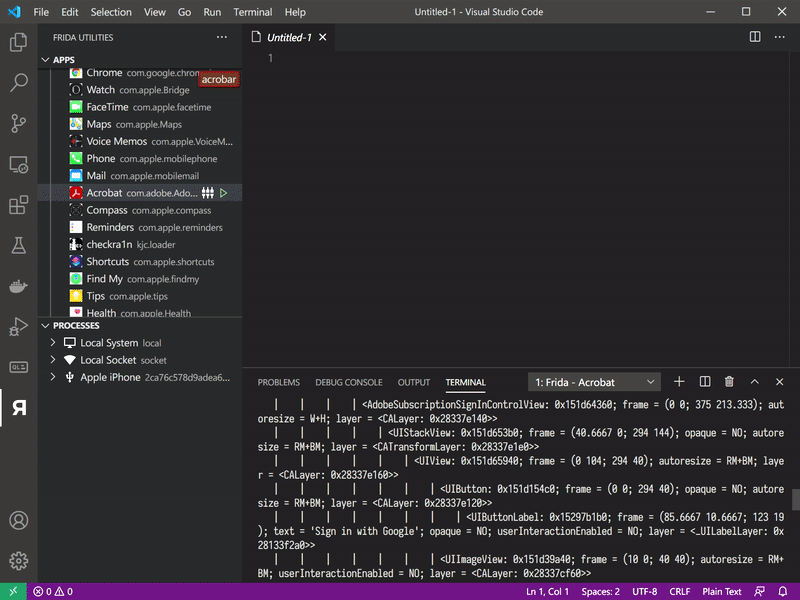 chichou/vscode-frida
Unofficial frida extension for VSCode
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 urbanadventurer/whatweb
Next generation web scanner
 google/buzzer
eBPF fuzzer toolchain for generating random eBPF programs and validating kernel verifier/runtime behavior. Supports coverage-guided fuzzing and…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
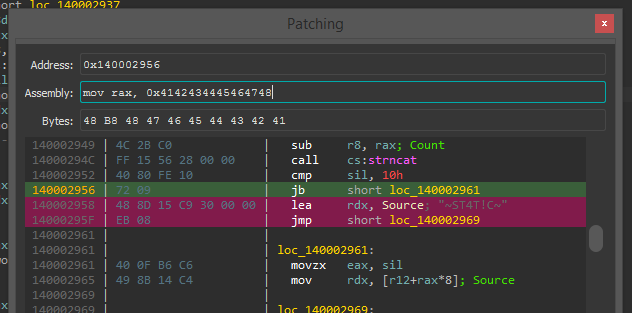 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
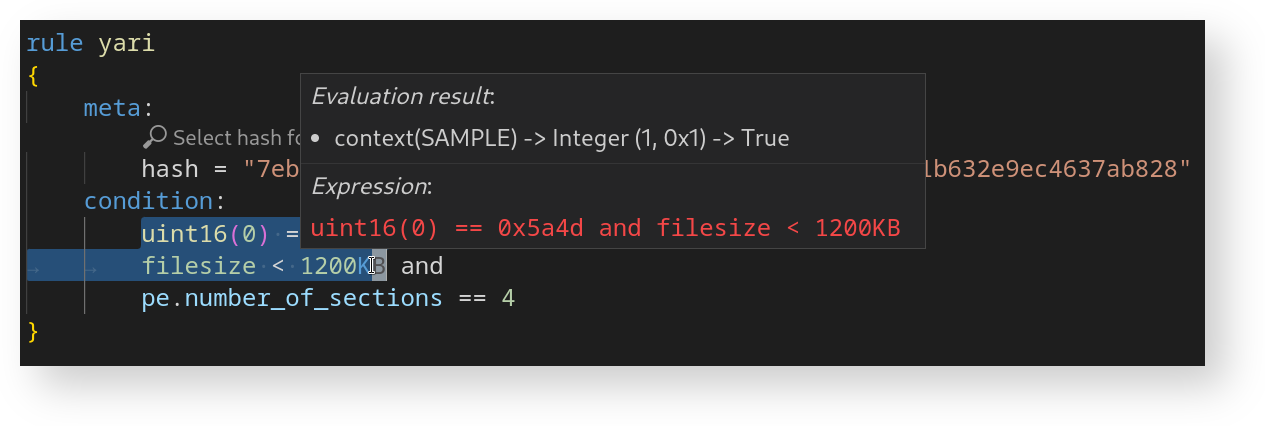 avast/yari
YARI is an interactive debugger for YARA Language.