
apiscope
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
kaisonox/apiscopeAn API hooking framework for intercepting and monitoring Windows applications
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
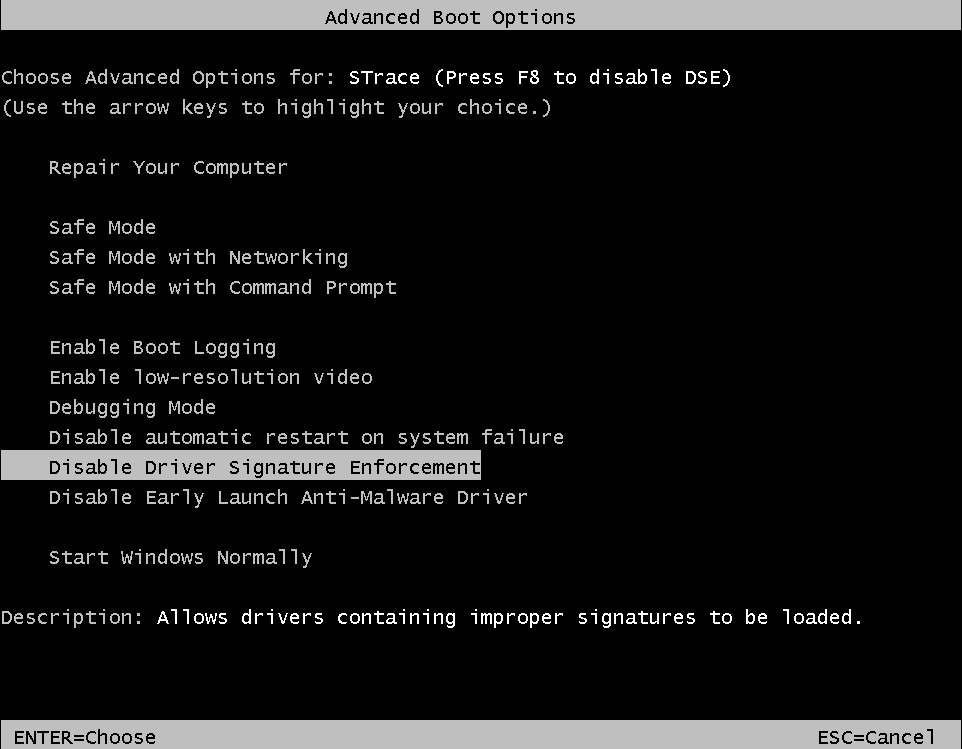 mandiant/strace
A DTrace on Windows Reimplementation
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI