

 urbanadventurer/whatweb
Next generation web scanner
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 eset/malware-research
Code written as part of our various malware investigations
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
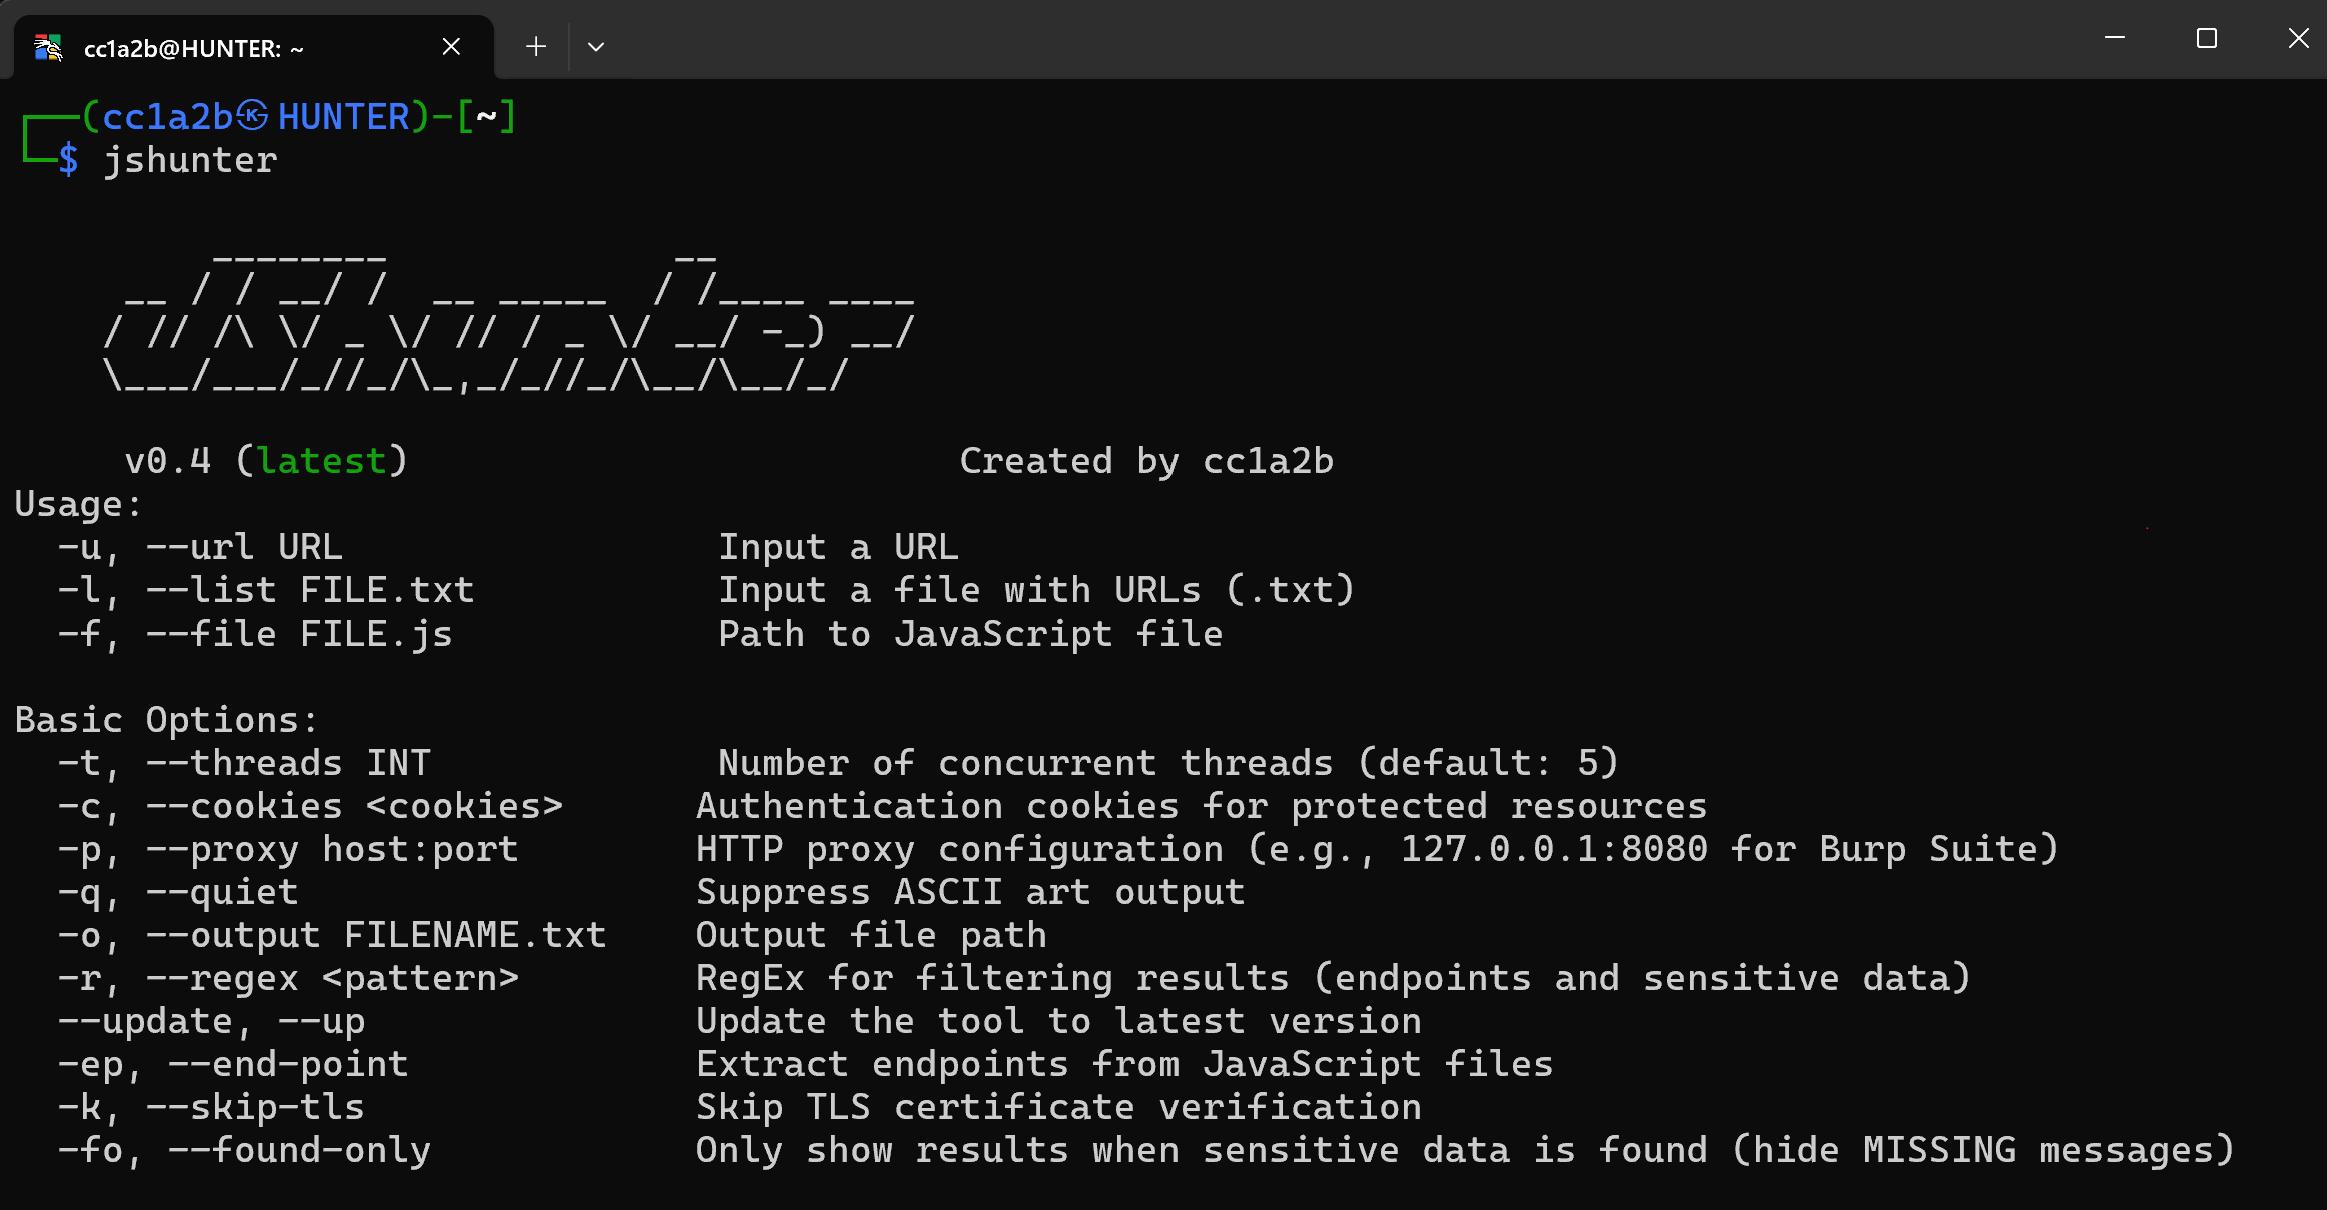 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 google/buzzer
eBPF fuzzer toolchain for generating random eBPF programs and validating kernel verifier/runtime behavior. Supports coverage-guided fuzzing and…
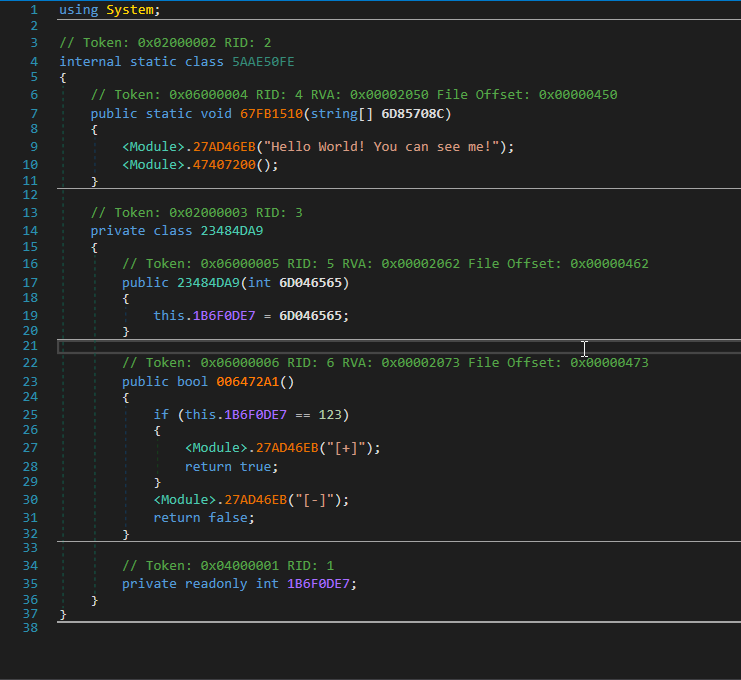 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…