

Brovan
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
166
advdebug/brovanUser-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
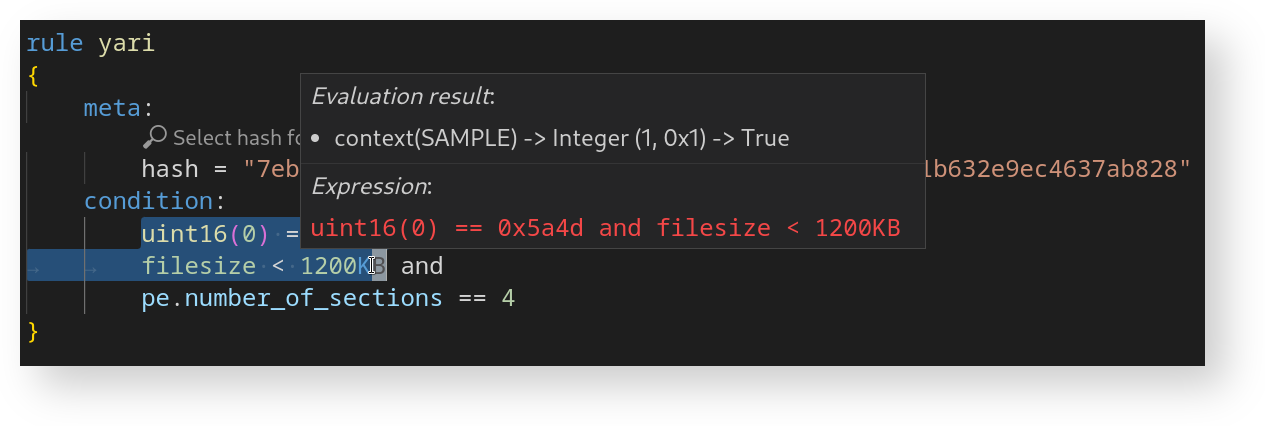 avast/yari
YARI is an interactive debugger for YARA Language.
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
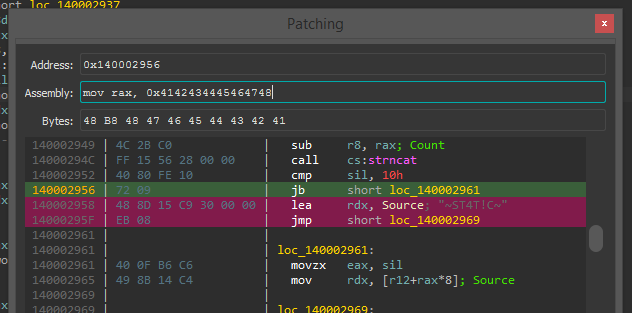 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API