
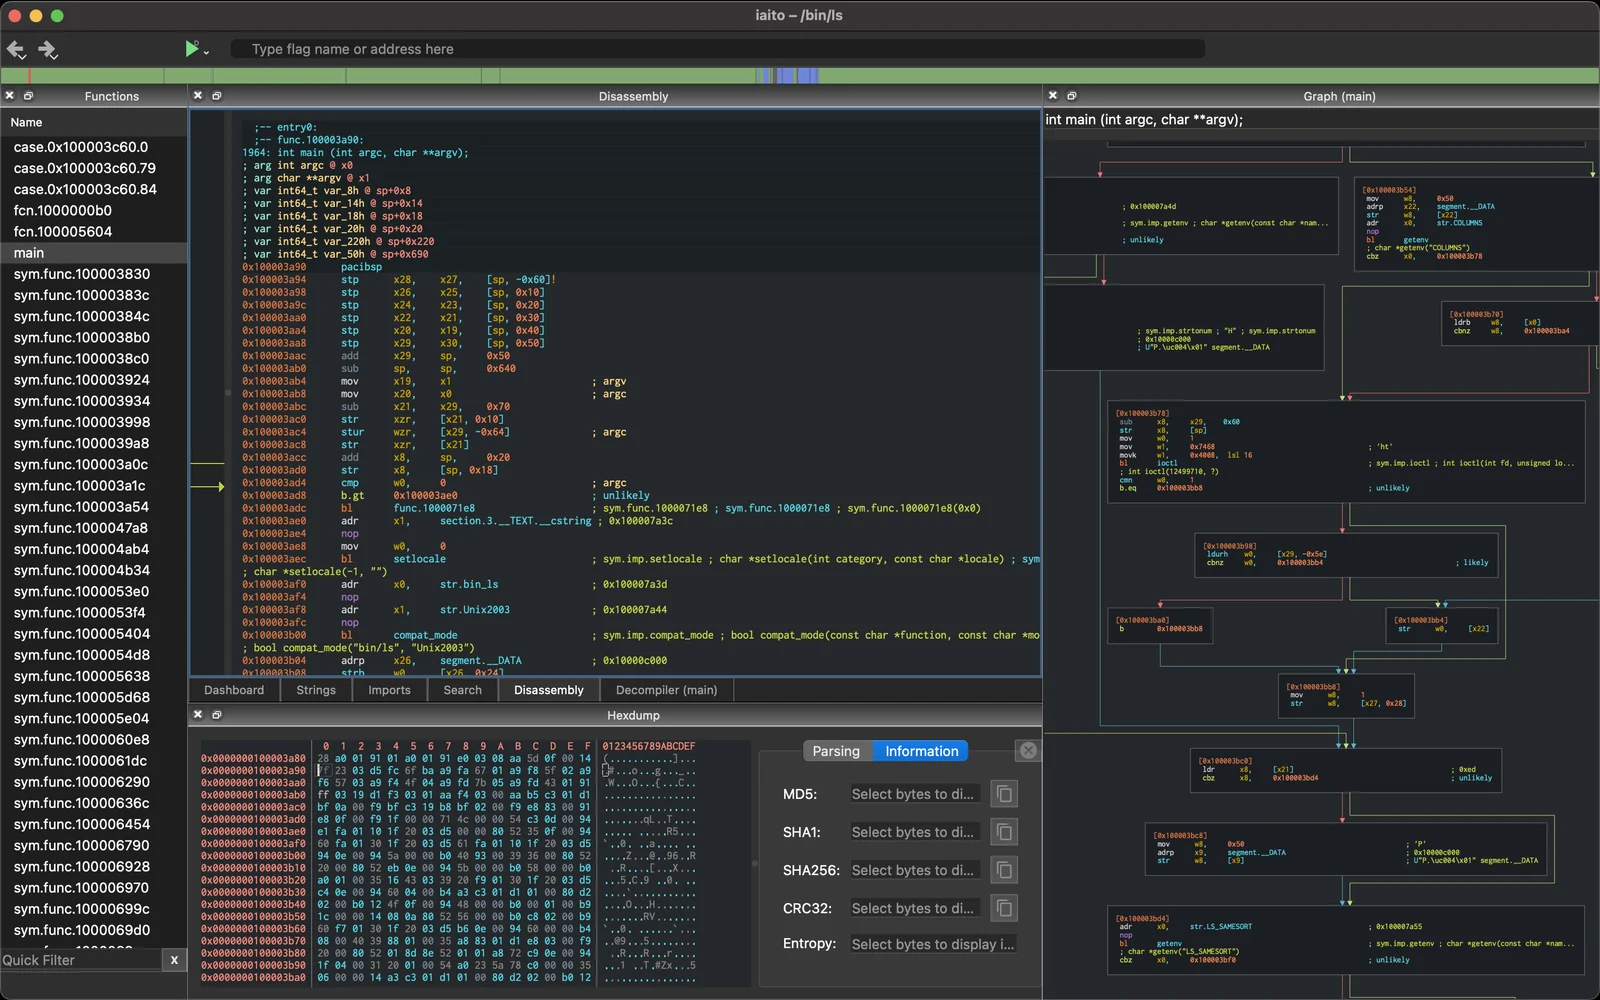
iaito
 radareorg/iaito
Qt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
binary-analysisbinary-exploitationdebuggers+5
1.7k
radareorg/iaitoQt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
 ph4ntom-rev/ph4ntom-ida-bridge
Secure local REST, CLI, MCP, and agent bridge for IDA Pro 9.x
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
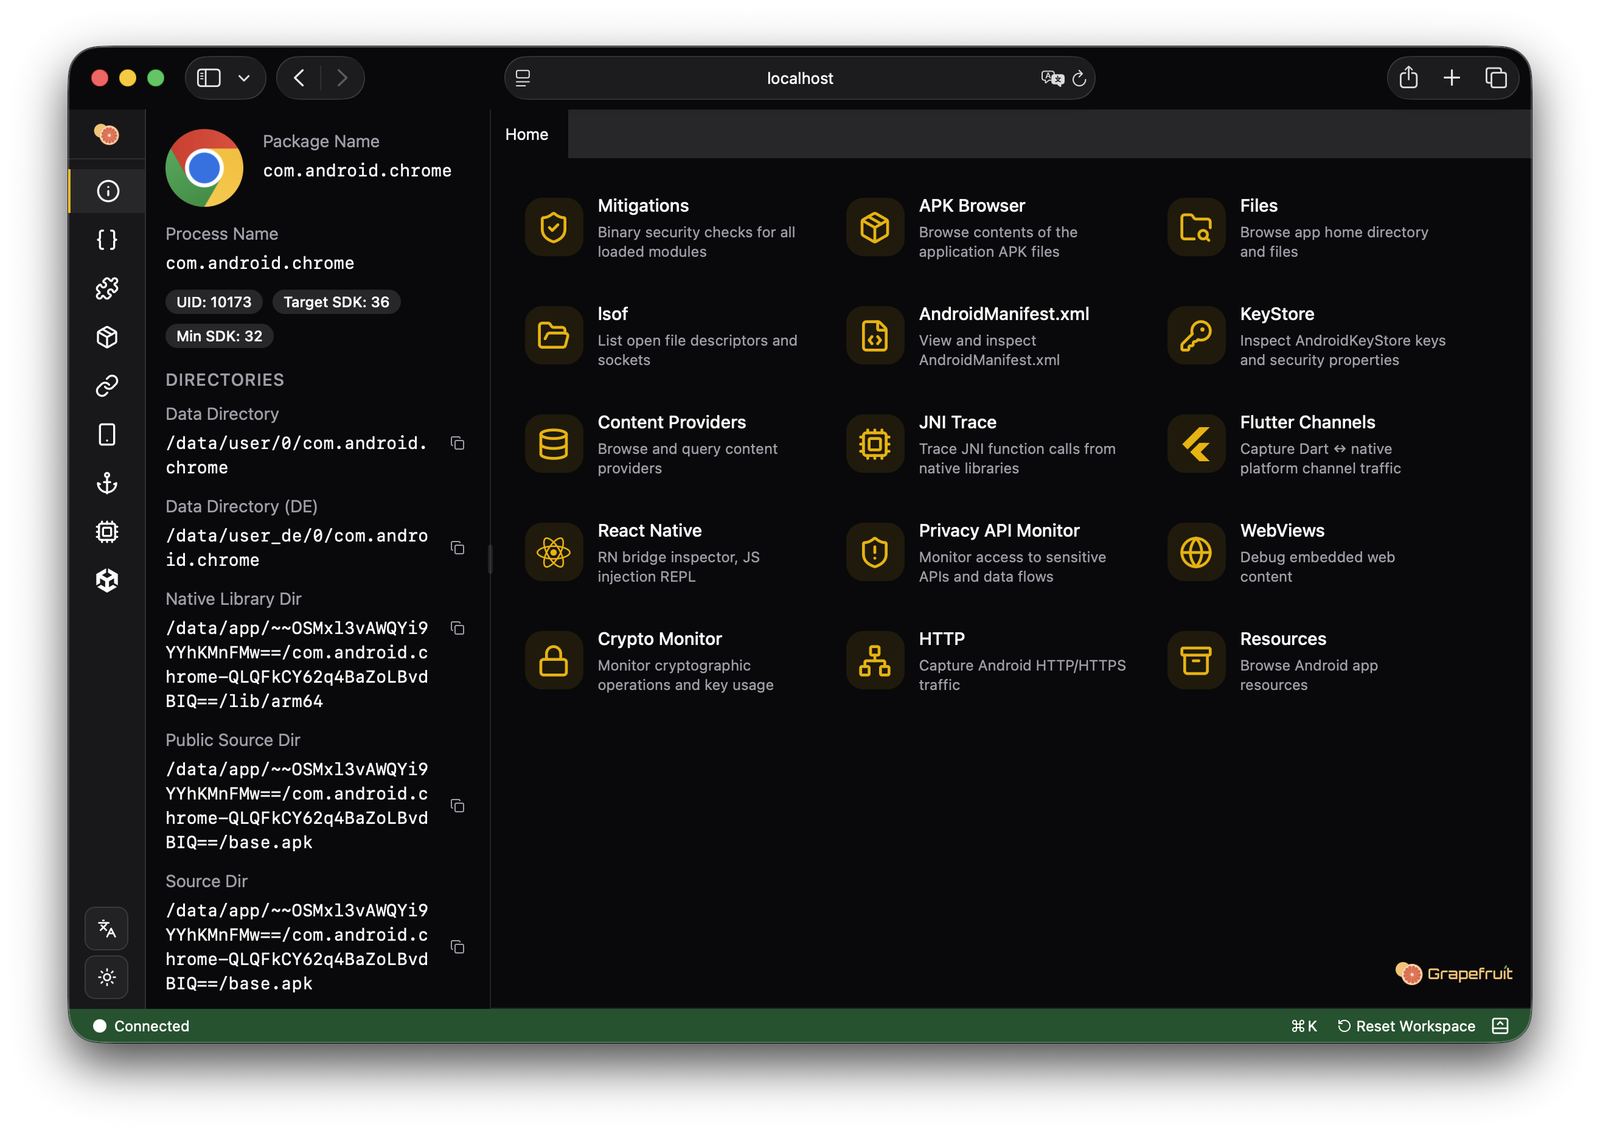 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
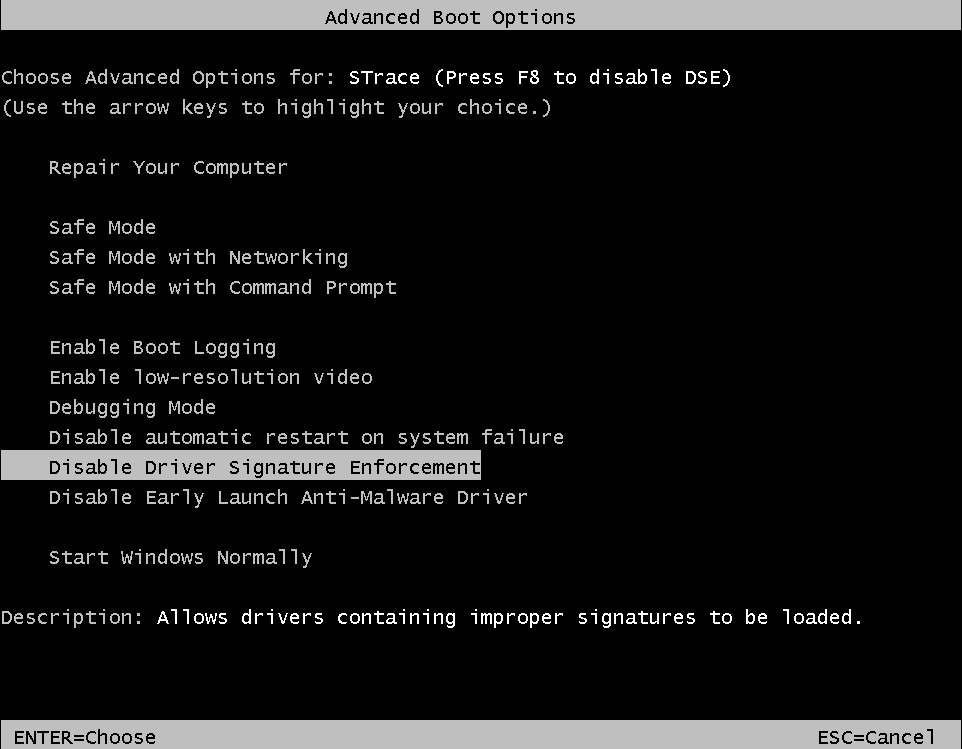 mandiant/strace
A DTrace on Windows Reimplementation
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
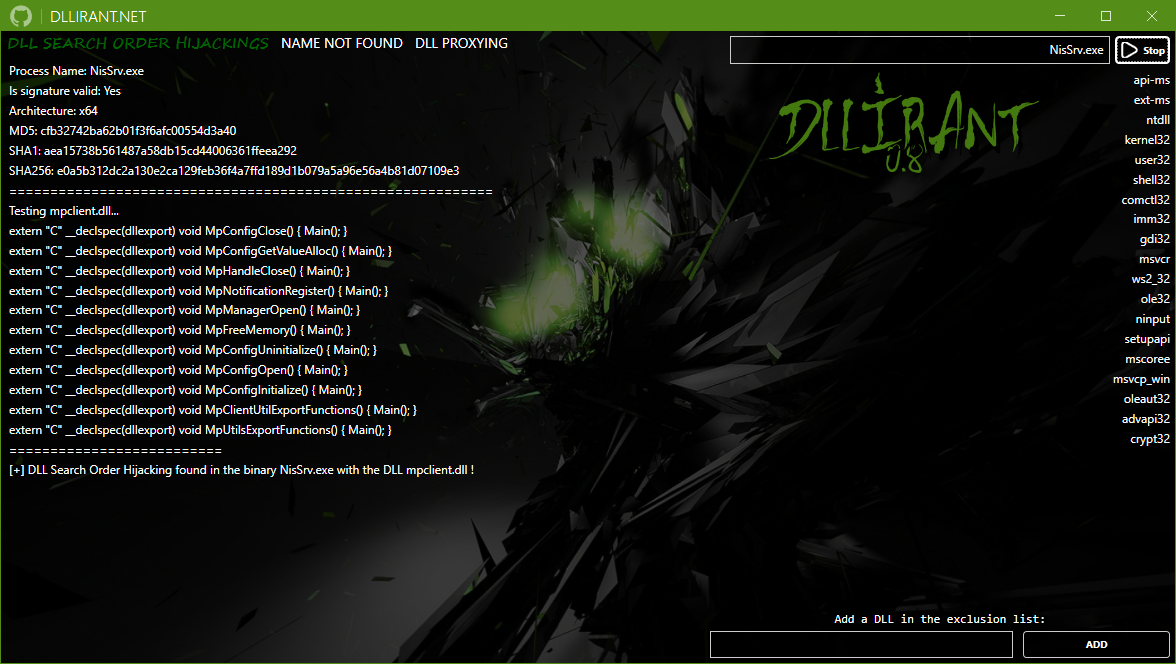 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer