
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
261 results
sniffglue preview

sniffglue

GitHubkpcyrd/sniffglue

Secure multithreaded packet sniffer

dns-analysisdynamic-analysis-sandboxingfuzzing+3
1.3k5 months ago
norimaci preview

norimaci

GitHubmnrkbys/norimaci

Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…
dynamic-analysis-sandboxingforensicsmalware-analysis
716 years ago
flare-fakenet-ng preview

flare-fakenet-ng

GitHubmandiant/flare-fakenet-ng

FakeNet-NG - Next Generation Dynamic Network Analysis Tool
dynamic-analysis-sandboxingmalware-analysisnetwork-security+2
2.2k4 months ago
speakeasy preview

speakeasy

GitHubmandiant/speakeasy

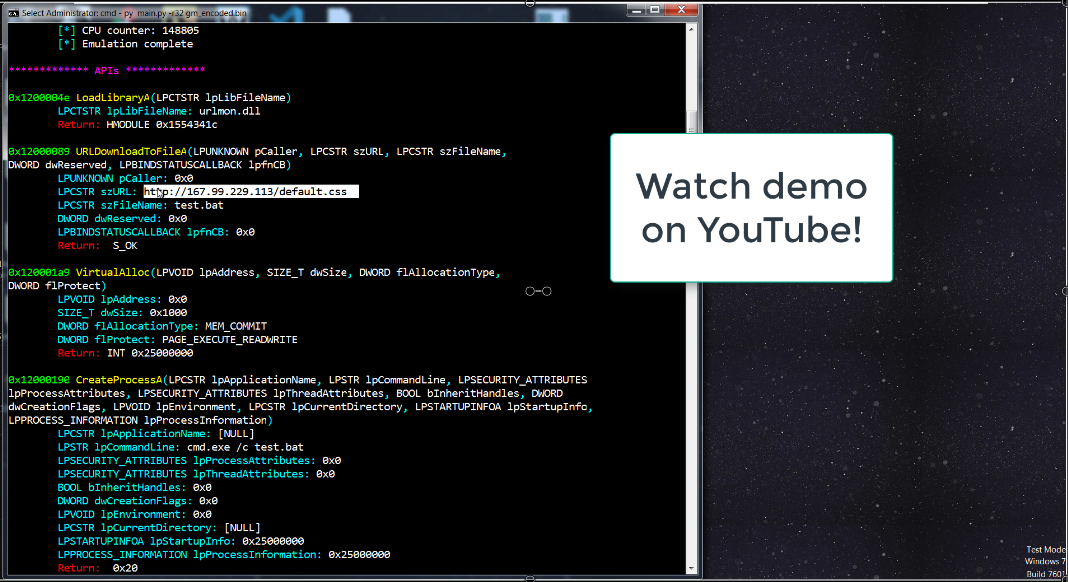
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…

binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2.1k1 day ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
debuggersdigital-forensicsdisk-forensics+7
252 months ago
imaginaryC2 preview

imaginaryC2

GitHubfelixweyne/imaginaryc2

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…

command-and-controldigital-forensicsdynamic-analysis-sandboxing+5
4463 years ago
markdown-exfil-tester preview

markdown-exfil-tester

GitHubtrerb/markdown-exfil-tester

Black-box test whether an LLM chatbot is vulnerable to markdown/HTML exfil (CVE-2025-32711 class). Spins up a sink, sends payloads, renders in…
ai-securityctfdynamic-analysis-sandboxing+6
5 months ago
sharem preview

sharem

GitHubbw3ll/sharem

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…

ai-securitybinary-analysisdebuggers+5
4916 months ago
ptcpdump preview

ptcpdump

GitHubmozillazg/ptcpdump

eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
cloud-securitycontainer-securitydigital-forensics+5
1.3k3 days ago
droidbox preview

droidbox

GitHubpjlantz/droidbox

Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
android-securitydynamic-analysis-sandboxinginformation-gathering+2
8106 years ago
peetch preview

peetch

GitHubquarkslab/peetch

eBPF-based toolkit for sniffing network traffic, extracting OpenSSL TLS keys, and intercepting/decrypting TLS 1.2 connections in real time using…
dynamic-analysis-sandboxingnetwork-securitypacket-sniffing-analysis
2102 years ago
AntiVE-BehaviorWatch preview

AntiVE-BehaviorWatch

GitHubnirvanaon/antive-behaviorwatch

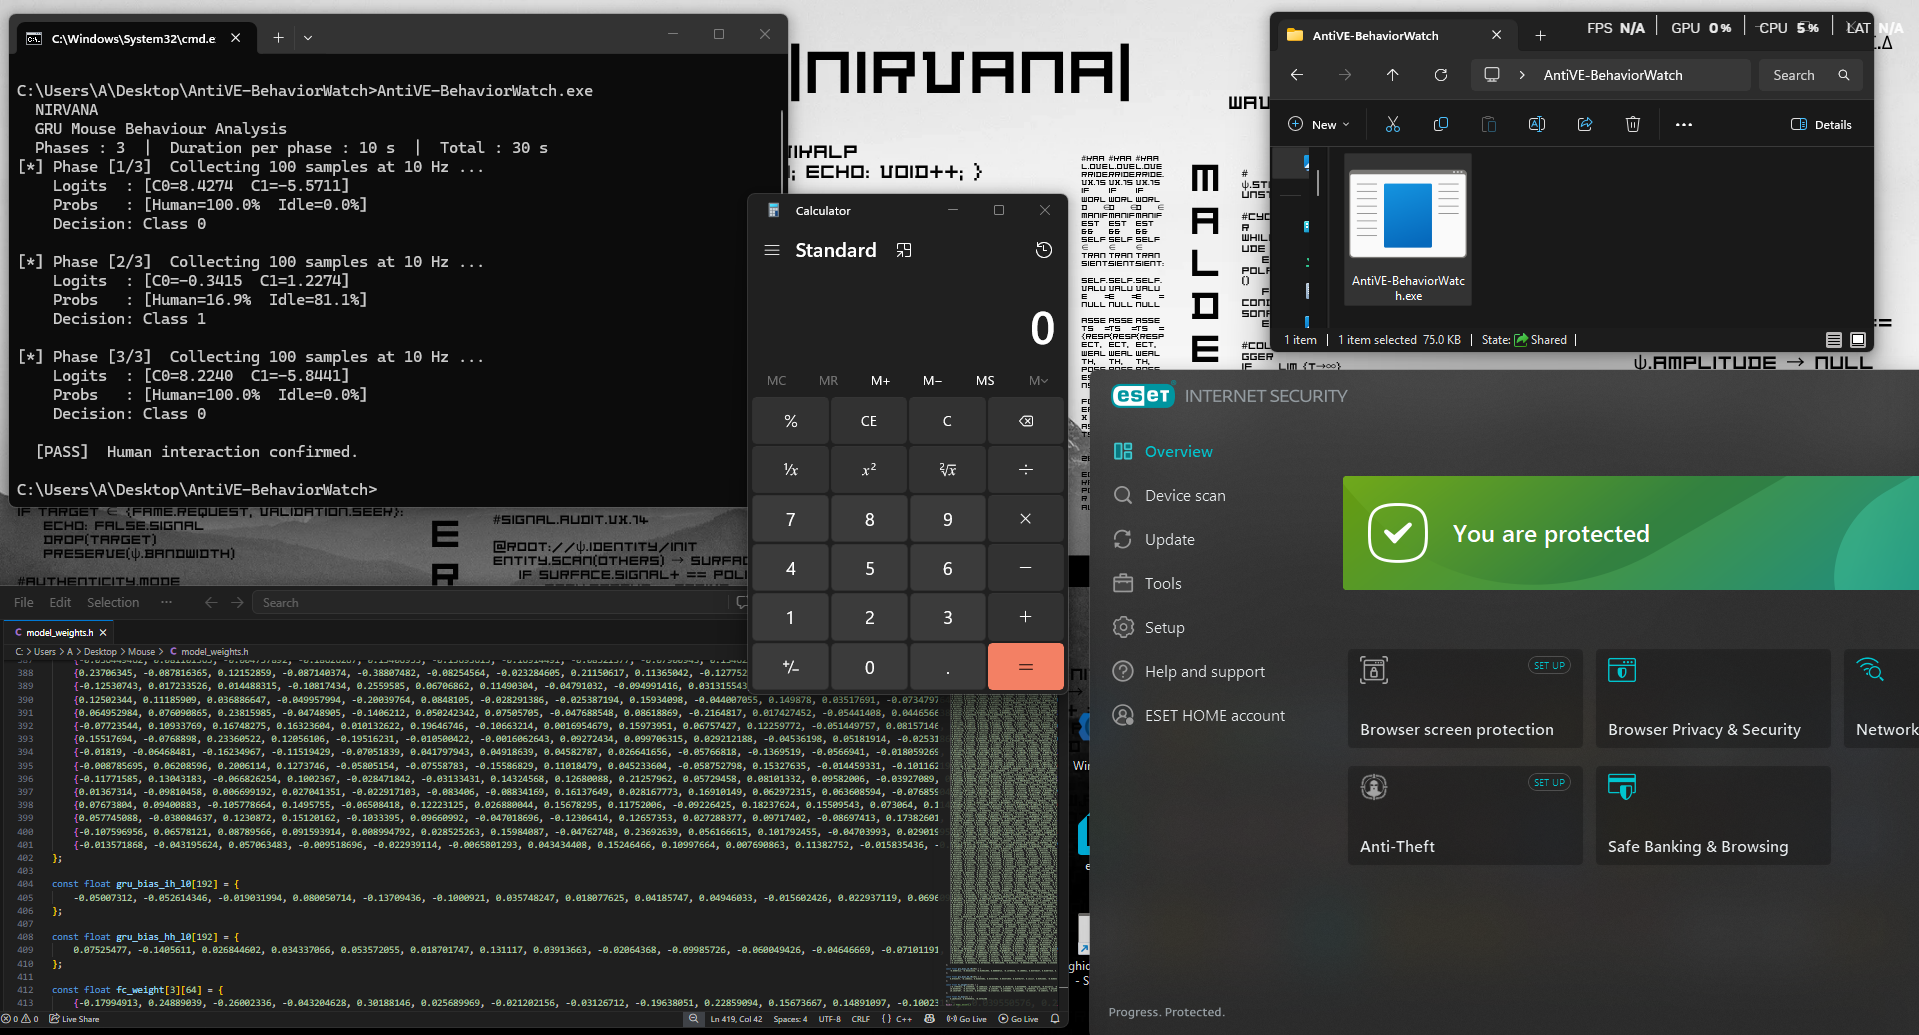
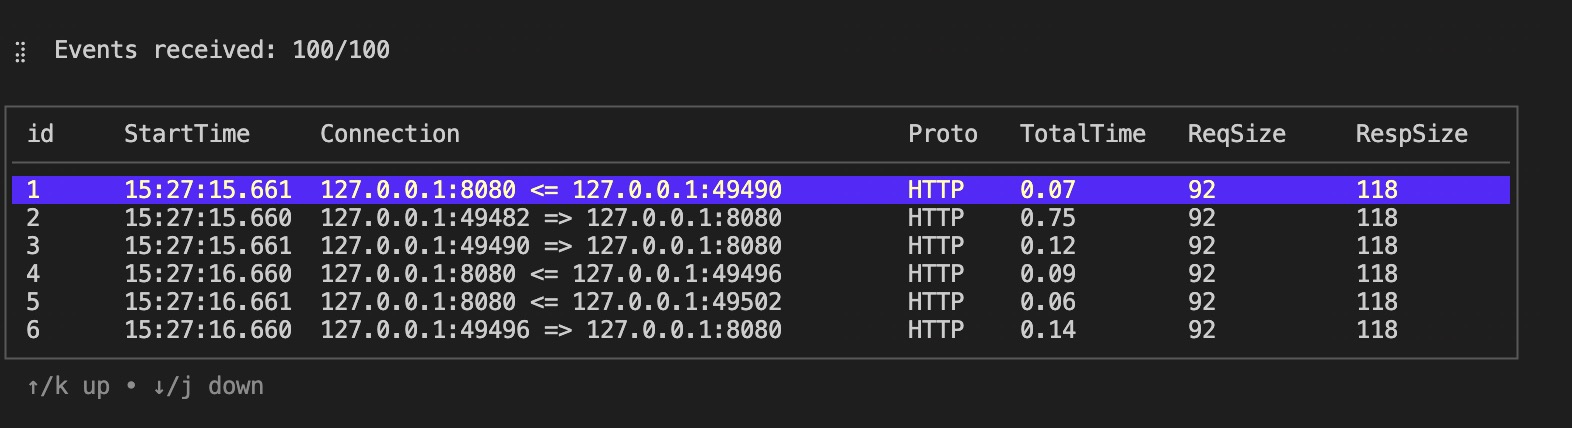
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
anti-botdynamic-analysis-sandboxingids-ips-evasion+3
402 months ago
kyanos preview

kyanos

GitHubhengyoush/kyanos

Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…

dns-analysisdynamic-analysis-sandboxinglog-analysis+3
5.1k3 months ago
ghidra preview

ghidra

GitHubnationalsecurityagency/ghidra

Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
81.2k1 day ago
kata-containers preview

kata-containers

GitHubkata-containers/kata-containers

Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…

cloud-infrastructure-securitycloud-securitycontainer-escape+4
8.9k13h 58m ago
dexcalibur preview

dexcalibur

GitHubreversenseorg/dexcalibur

[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
android-securitybinary-analysisdebuggers+5
1.2k5 days ago
guarddog preview

guarddog

GitHubdatadog/guarddog

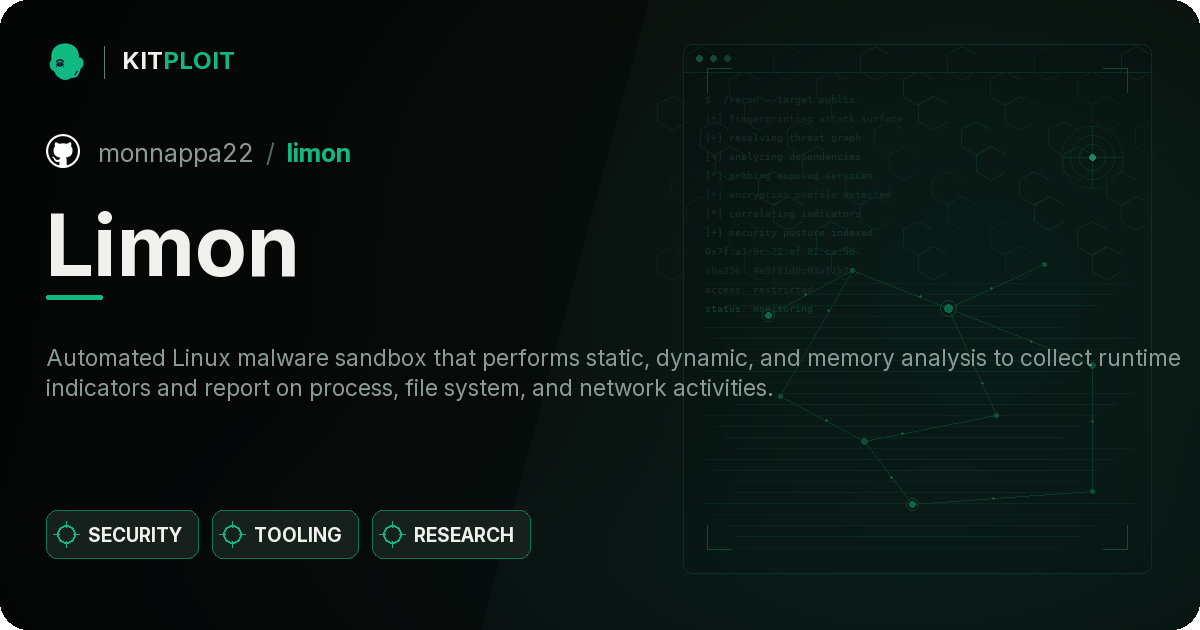
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
code-analysisdevsecopsdynamic-analysis-sandboxing+6
1.2k1 month ago
Limon preview

Limon

GitHubmonnappa22/limon

Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…

dynamic-analysis-sandboxingmalware-analysismemory-forensics+1
40510 years ago
Previous12…15Next