
kyanos
 hengyoush/kyanos
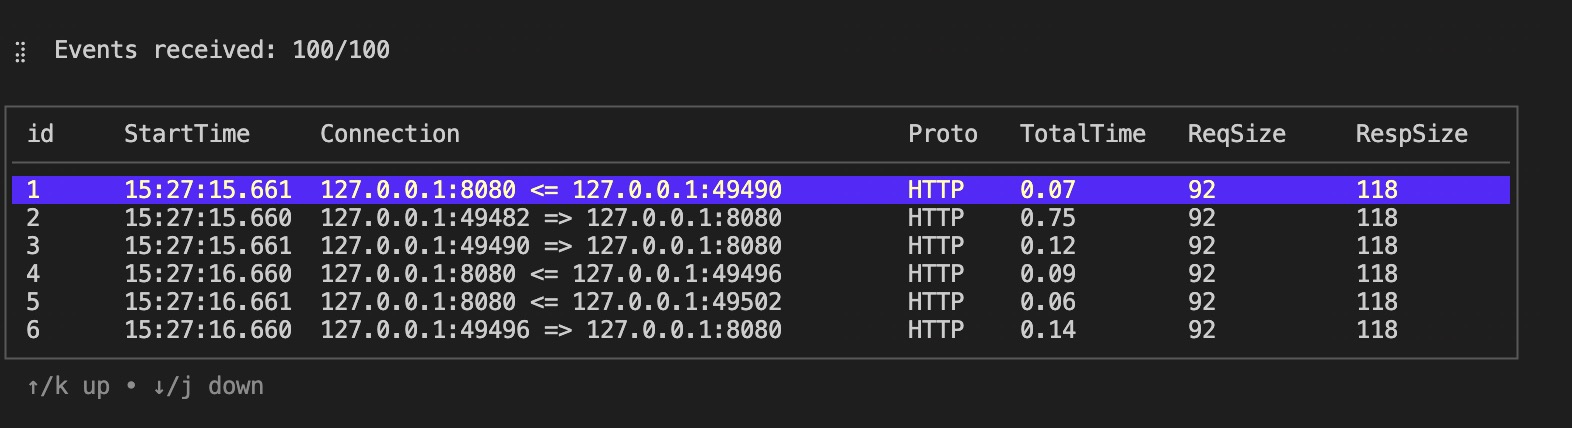
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
dns-analysisdynamic-analysis-sandboxinglog-analysis+3
5.1k
hengyoush/kyanosKyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 pjlantz/droidbox
Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
 4ier/neo
Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.
 hamz-a/frida-android-libbinder
PoC Frida script to view Android libbinder traffic
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 zeromemoryex/c2-hunter
Real-time C2 traffic extractor for malware analysts. Hooks Win32 connection APIs to intercept and analyze command-and-control communication,…
 quarkslab/peetch
eBPF-based toolkit for sniffing network traffic, extracting OpenSSL TLS keys, and intercepting/decrypting TLS 1.2 connections in real time using…
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
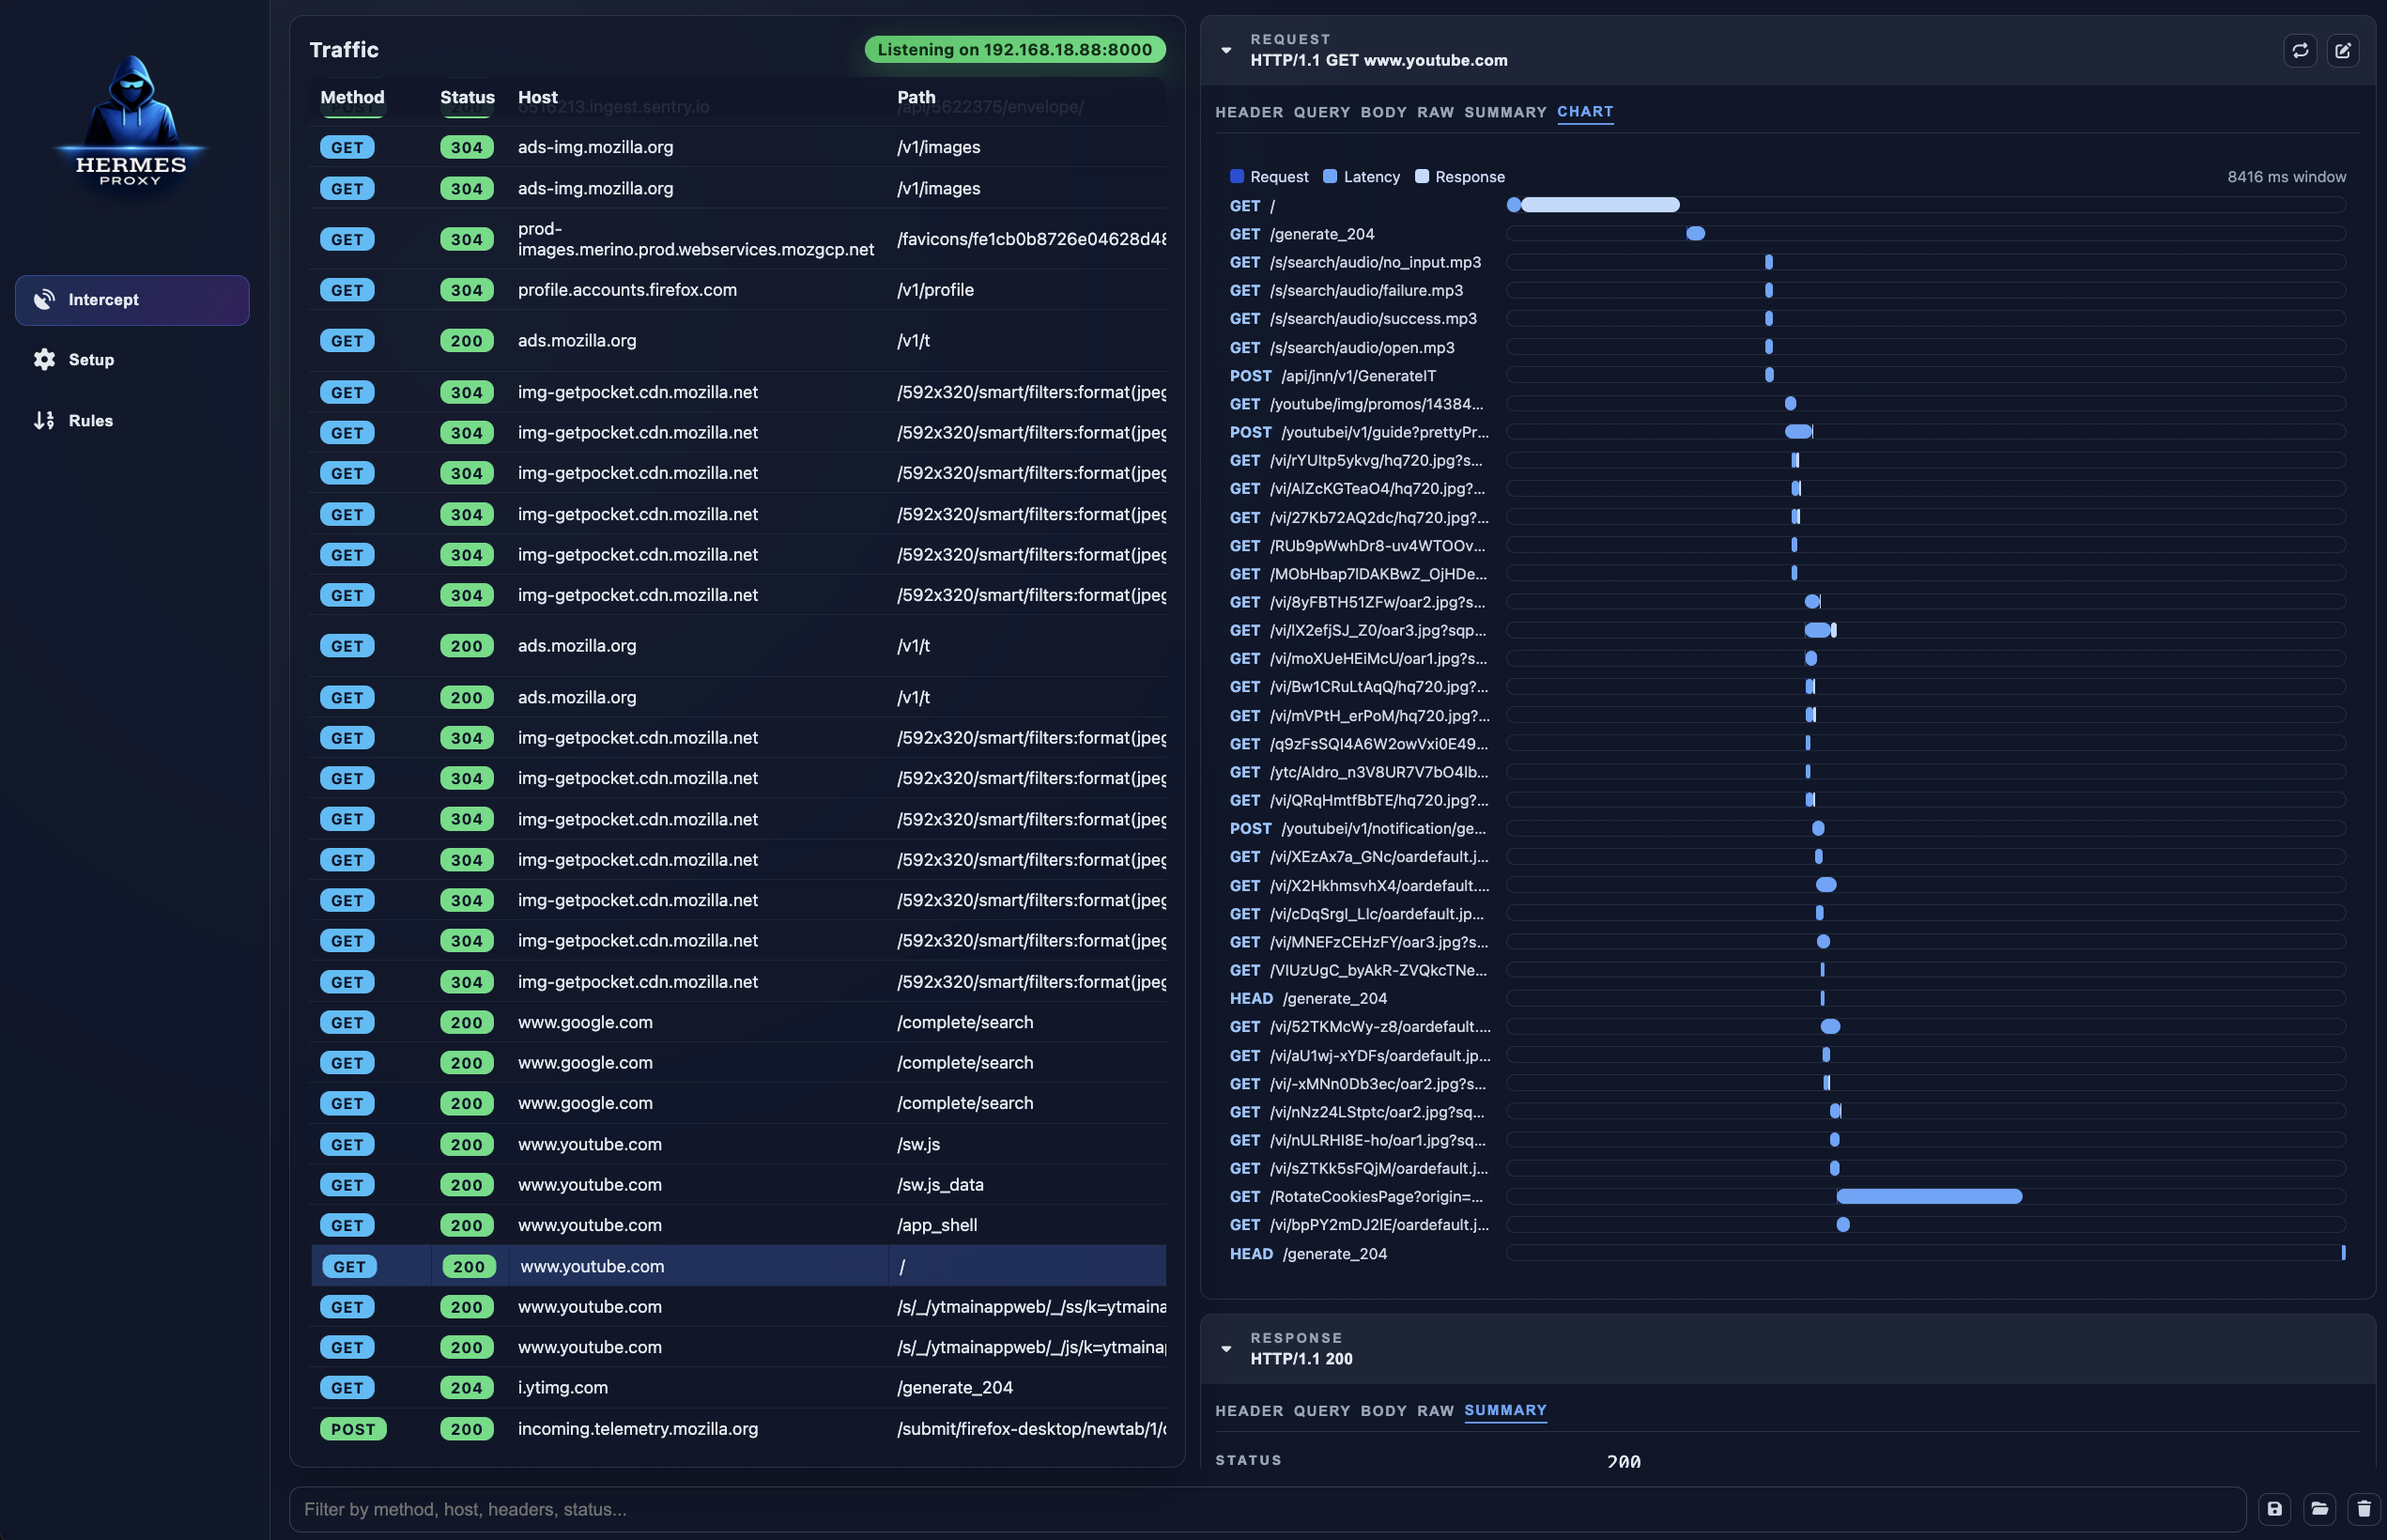 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 detuxsandbox/detux
The Multiplatform Linux Sandbox
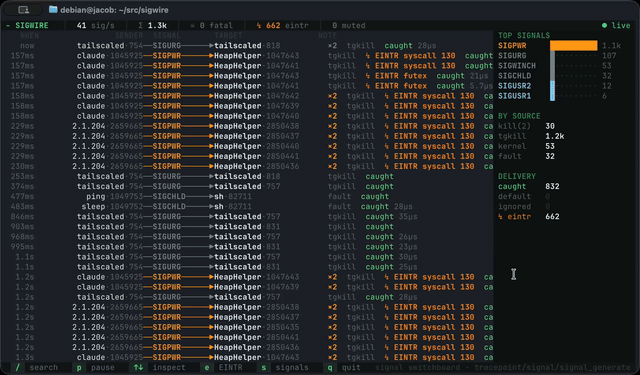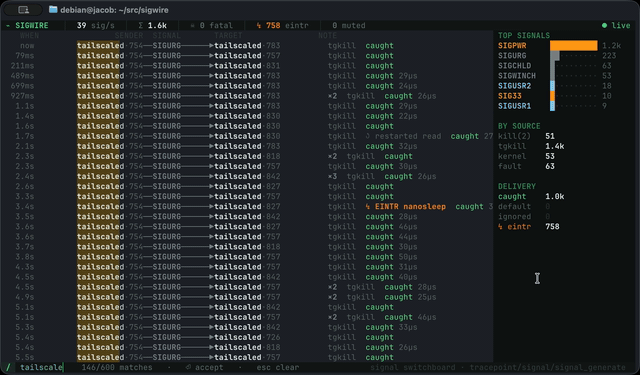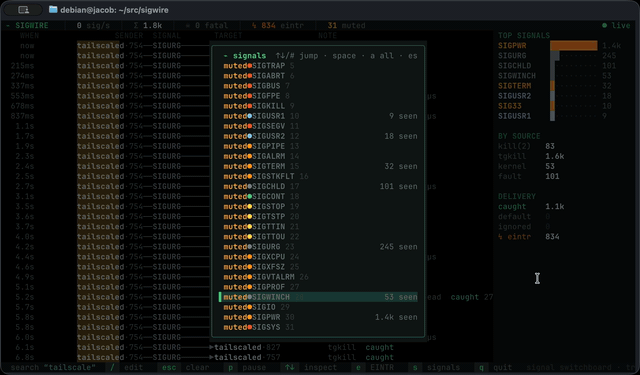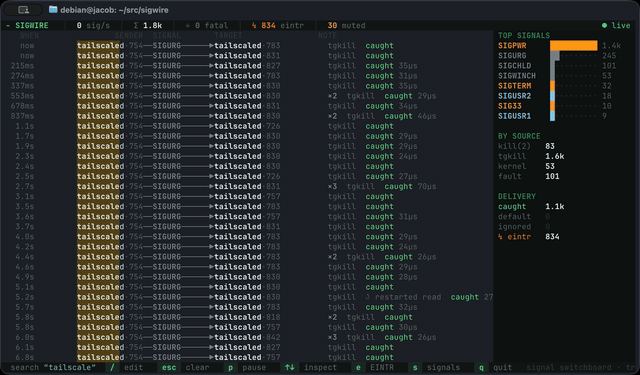 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
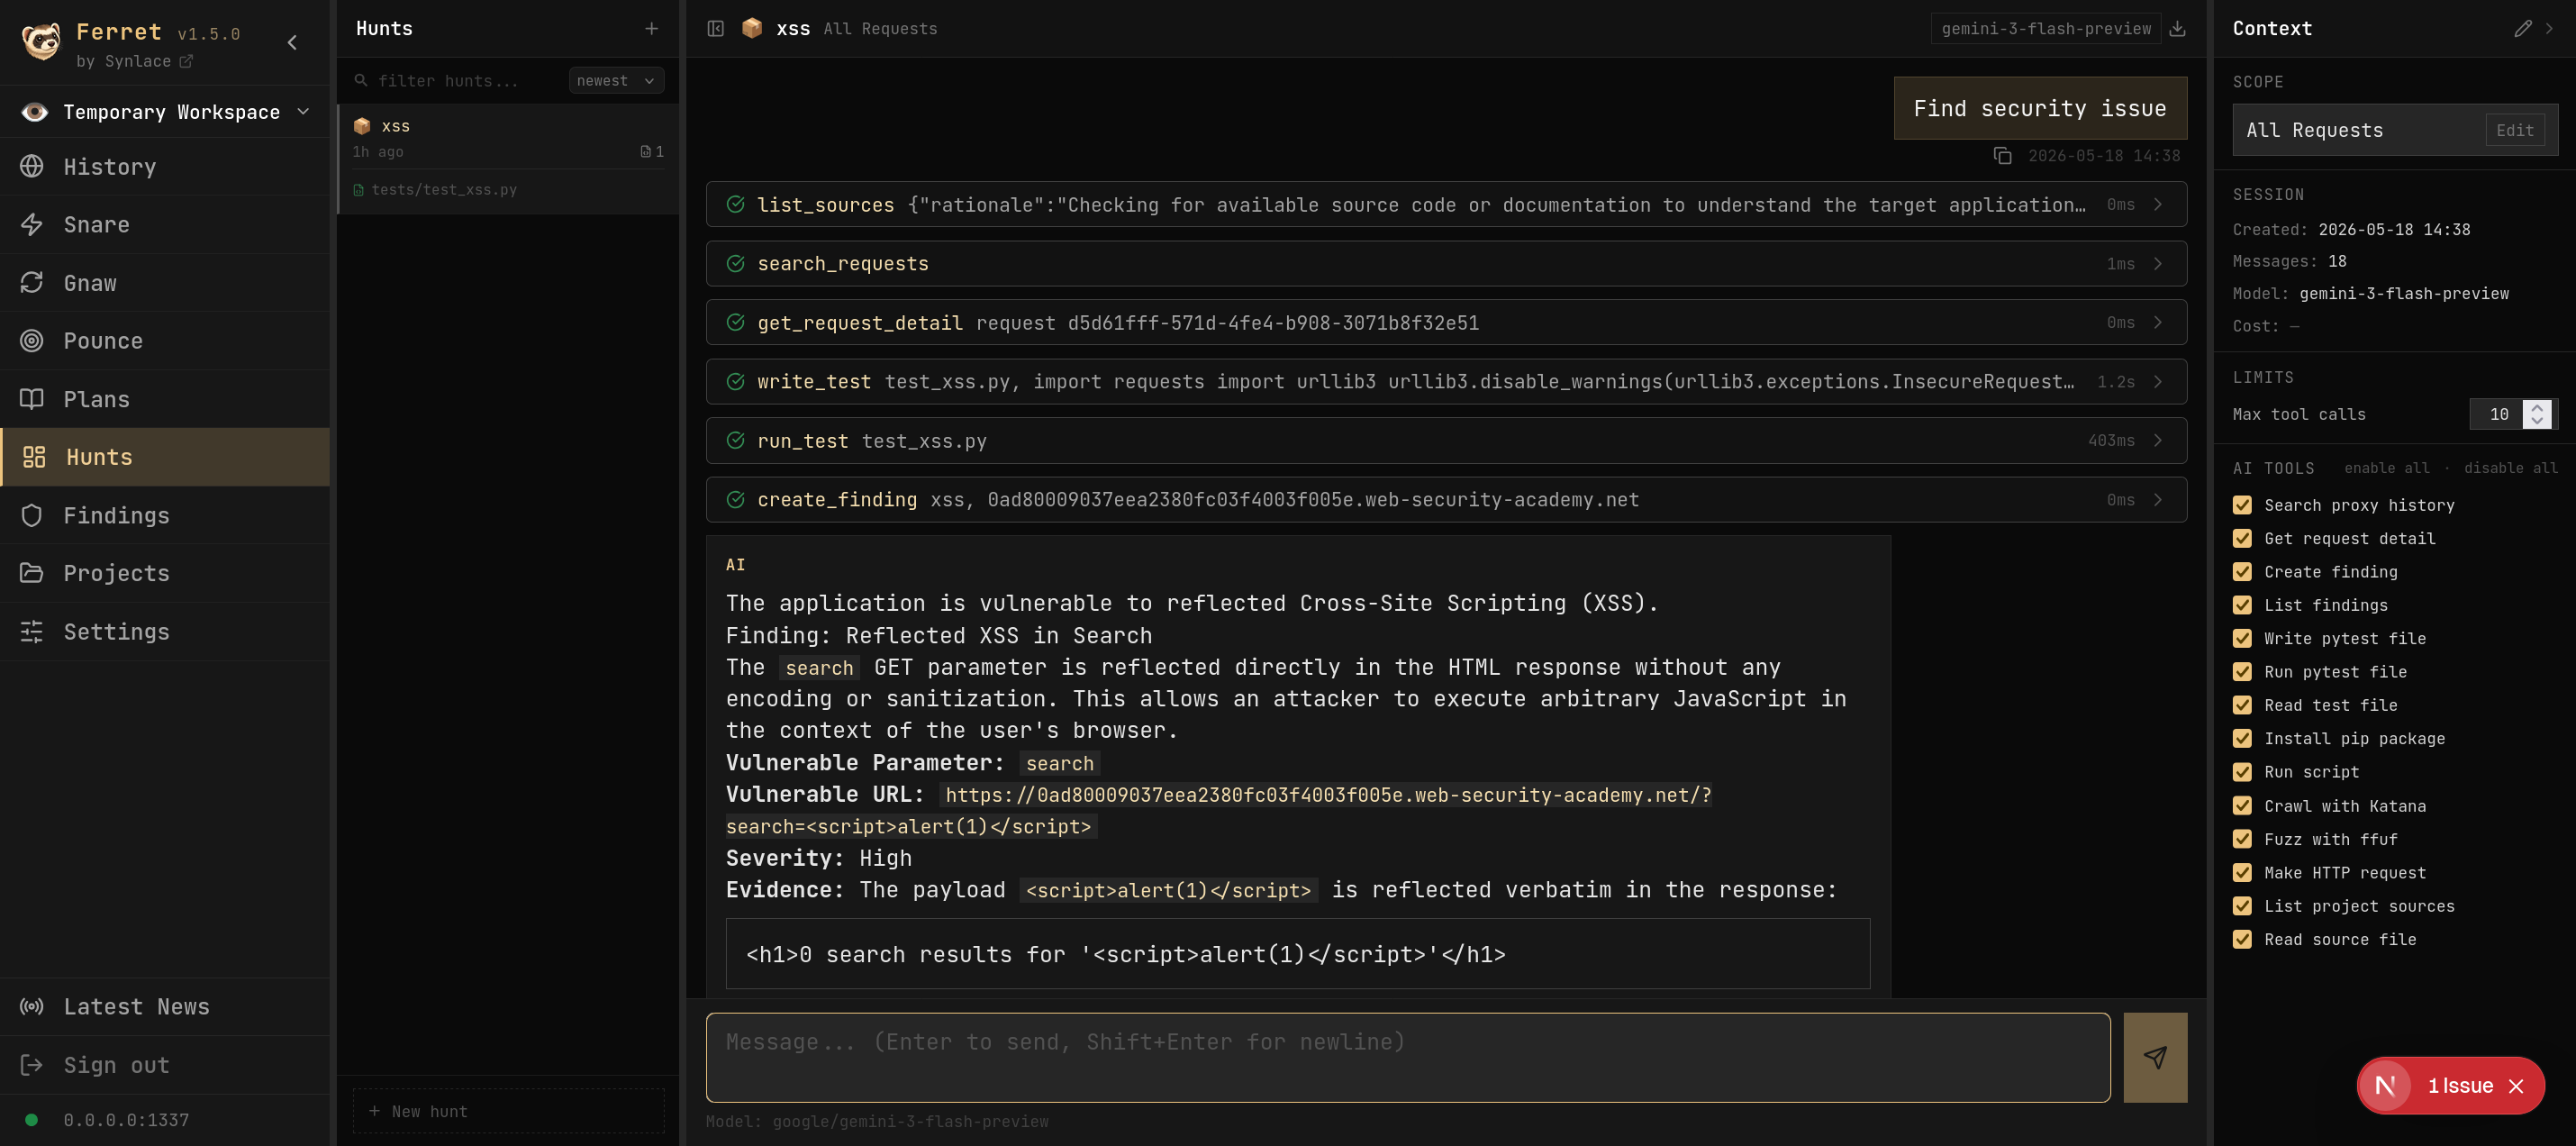 synlace/ferret
The collaborative web app pentest suite
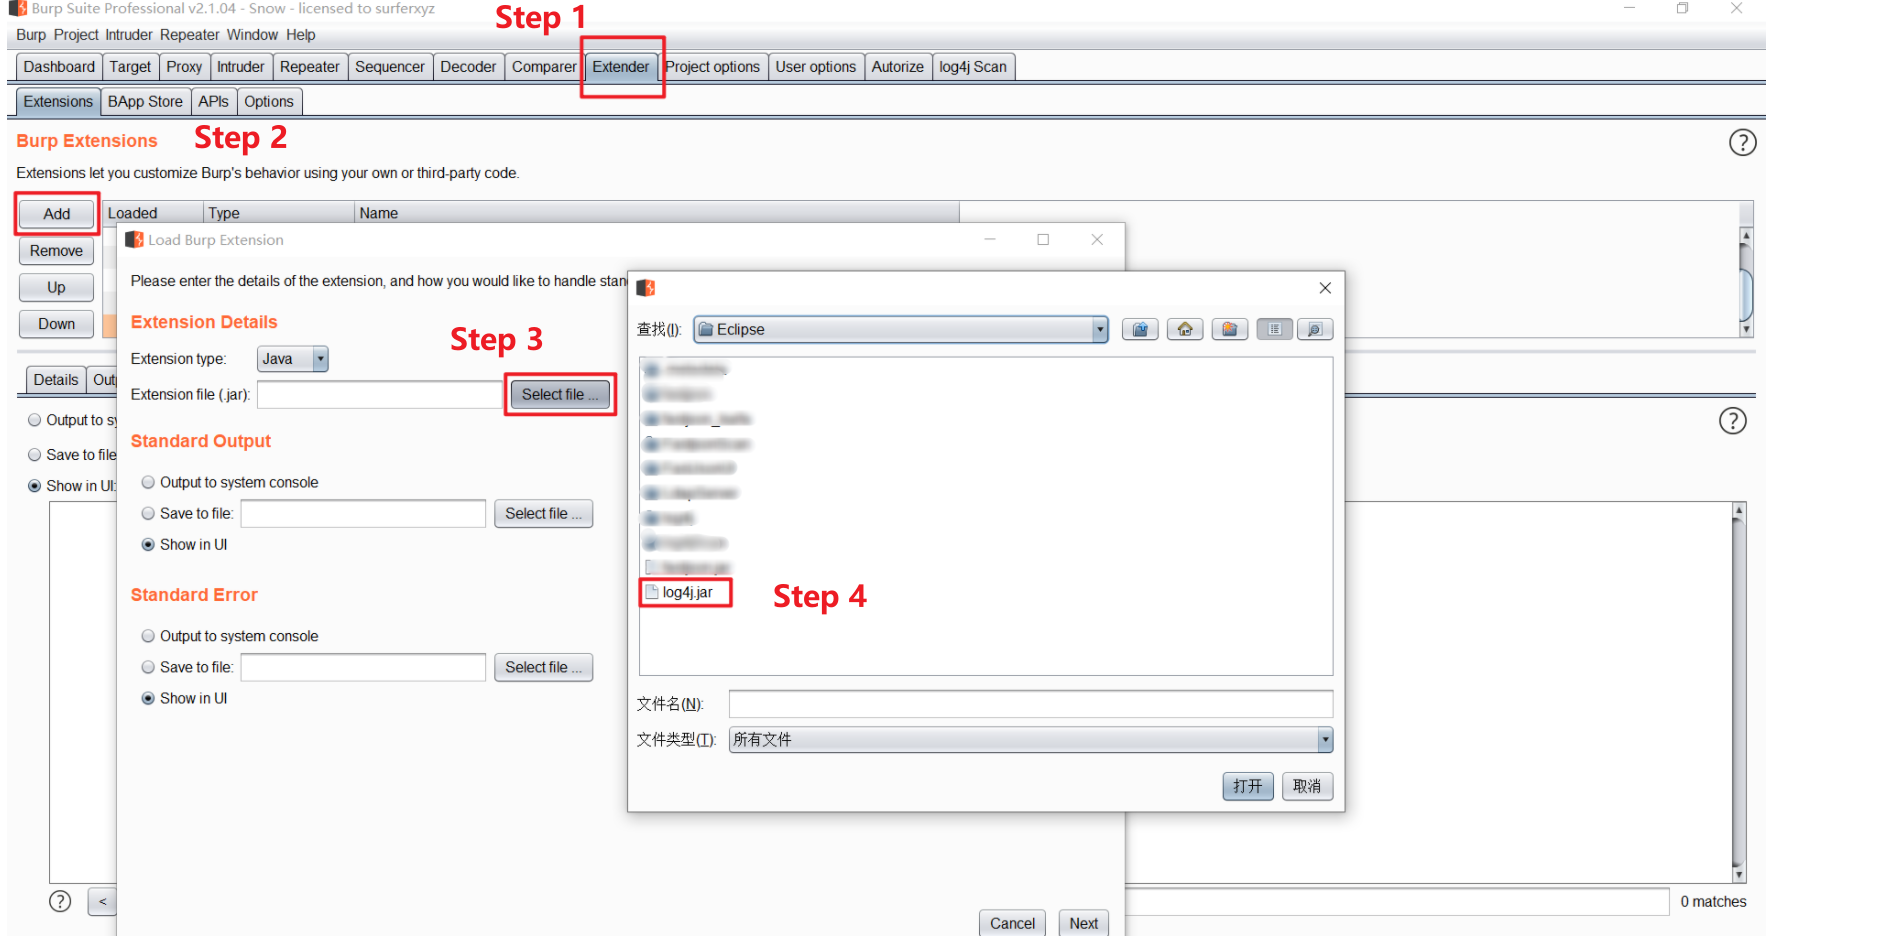 snow0715/log4j-scan-burpsuite
Log4j漏洞(CVE-2021-44228)的Burpsuite检测插件
 benrich127n/react2shell_analyzer
a dart package to analyze CVE-2025-55182 react2shell