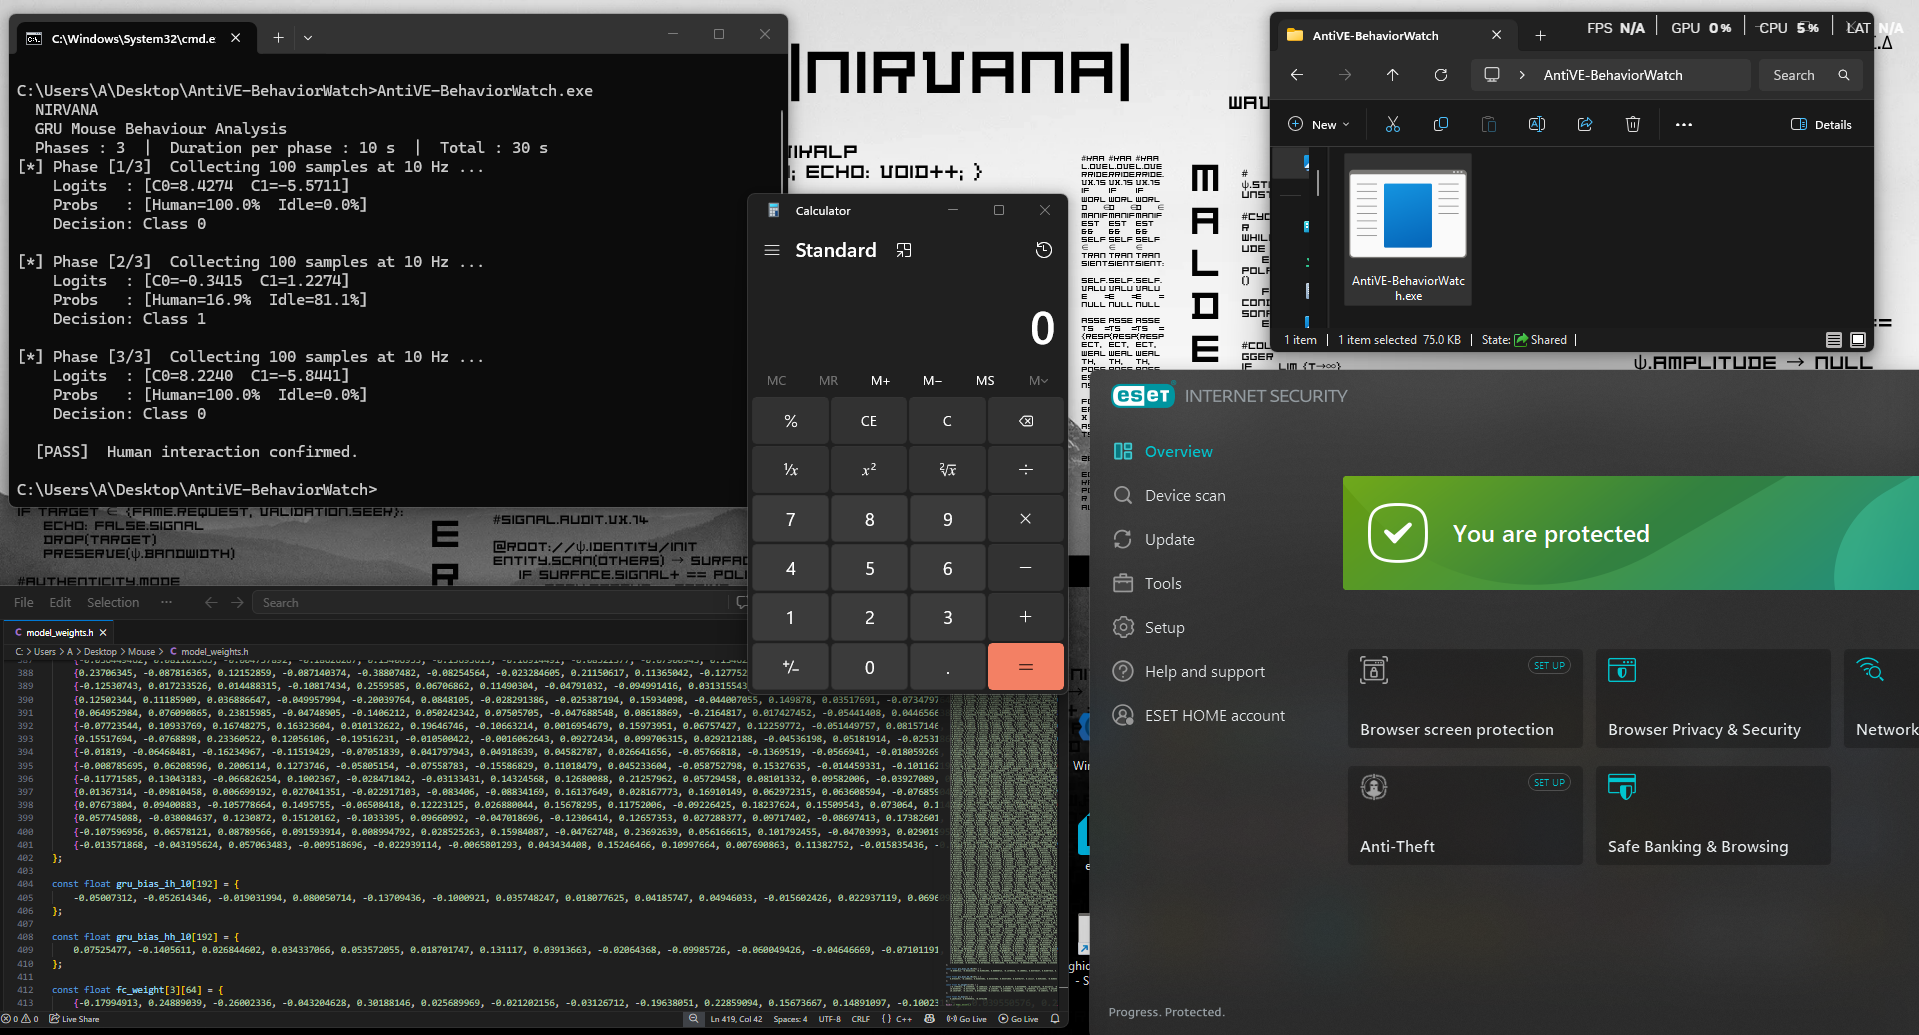
AntiVE-BehaviorWatch

Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…

Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…

Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…

Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.

C++ tool for detecting AnyRun sandbox environments, enabling malware to evade dynamic analysis and automated sandboxing systems.

Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…

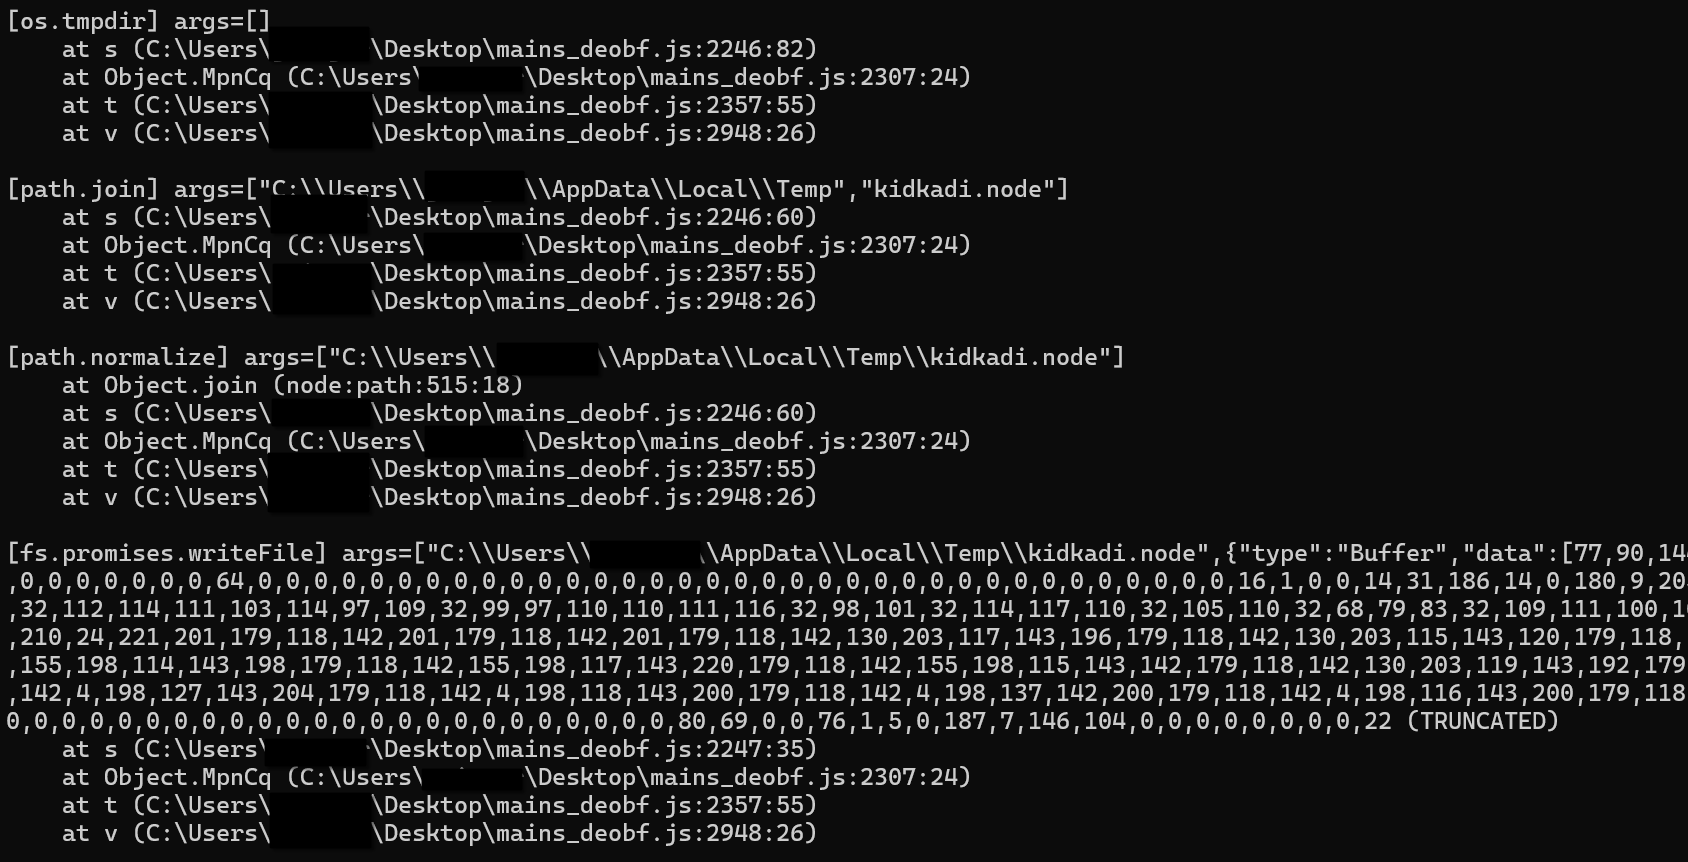
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…

Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…

Adaptive web scraping framework with anti-bot bypass, automatic element relocation, concurrent crawling, proxy rotation, and browser automation for…

makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]

Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering

Reverse engineering the new Datadome VM 🔥

The world's fastest agentic crawler. Reclaimed. Reinvented. Ready for war.

Reverse engineering toolkit for PerimeterX's bytecode VM, featuring a CFG-based disassembler, 5-layer decryption pipeline, opcode table…

Neutralize KEPServerEX anti-debugging techniques

A program written in C++ for remotely dumping manual mapped modules.

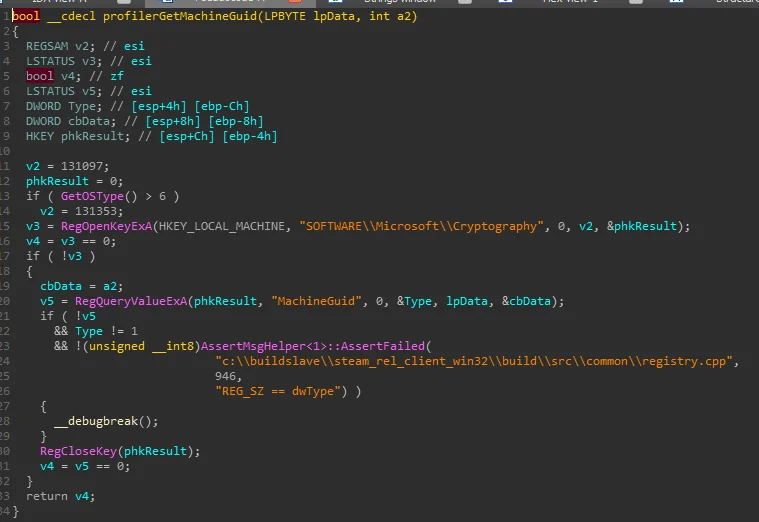
Work-in-progress library injected into Steam to block the hidden CFillMachineInfoThread that collects HWID, disk, network adapter, and registry…

Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…