
dynmx
 0x534a/dynmx
Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!
dynamic-analysis-sandboxingmalware-analysis
0x534a/dynmxSignature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
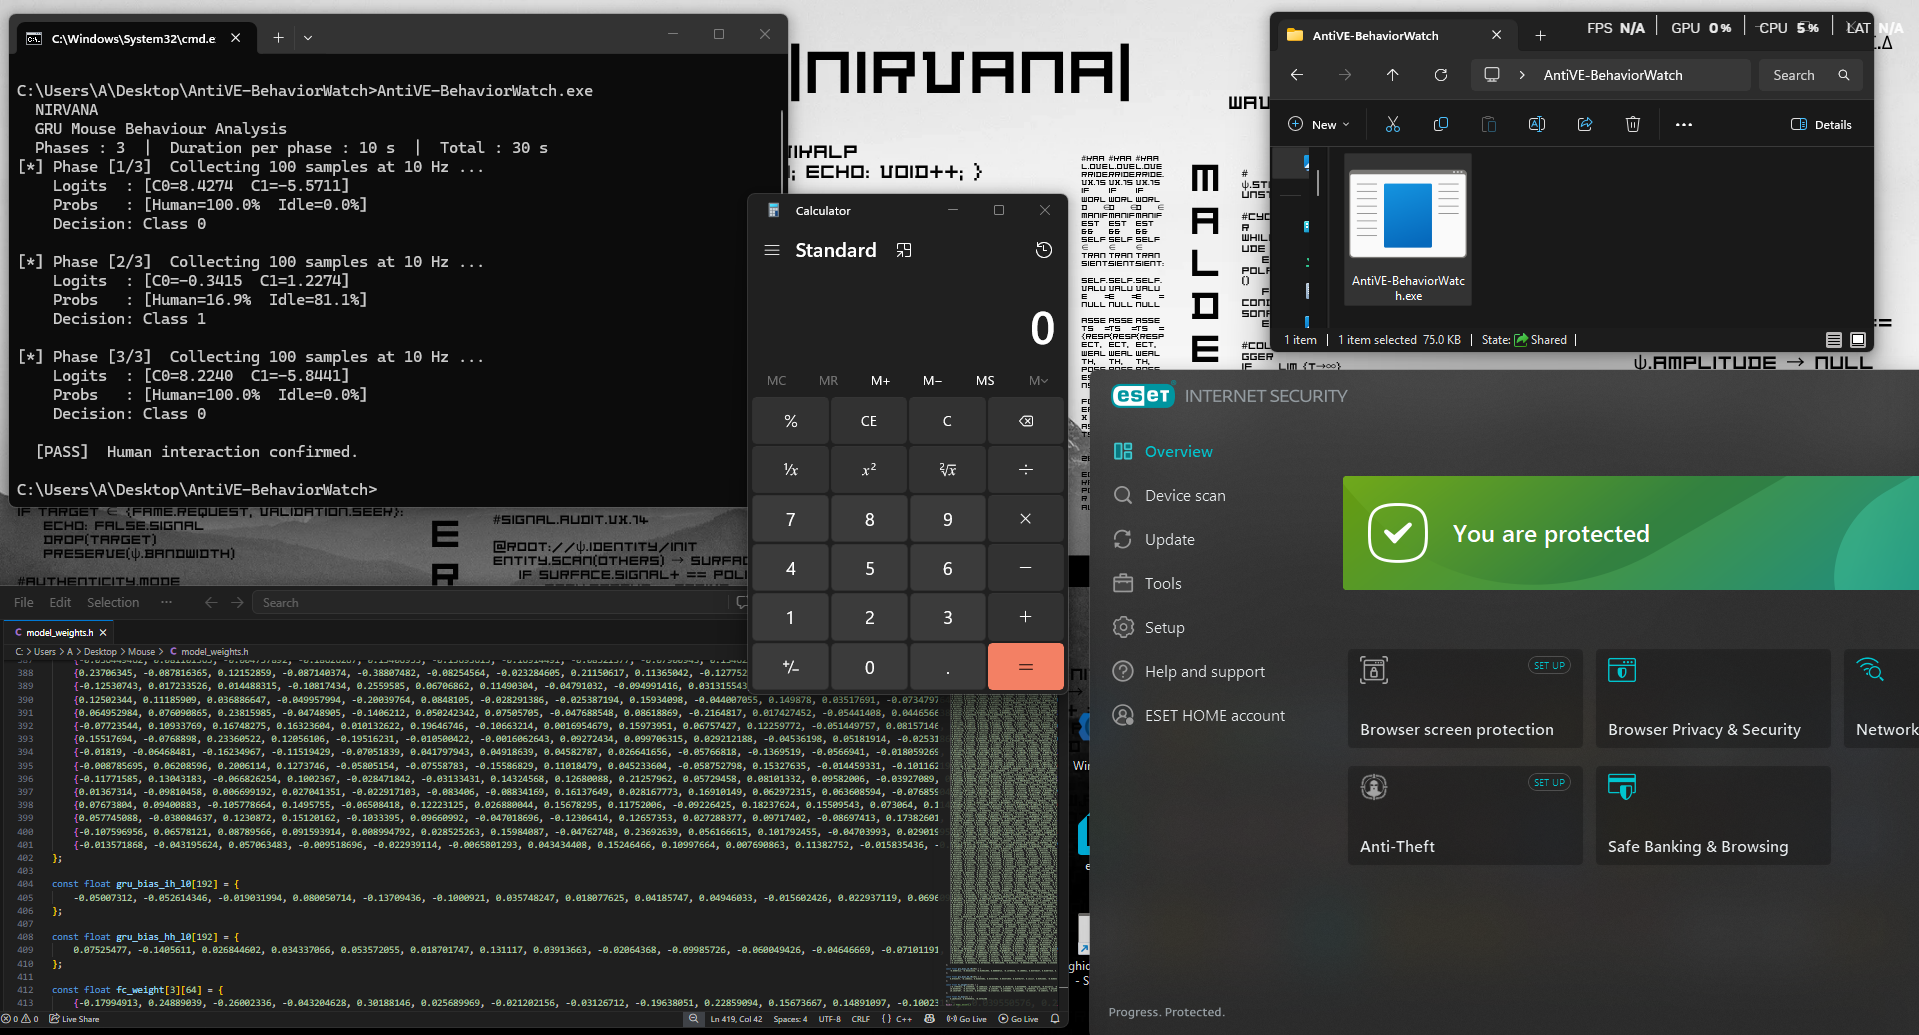 nirvanaon/antive-behaviorwatch
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
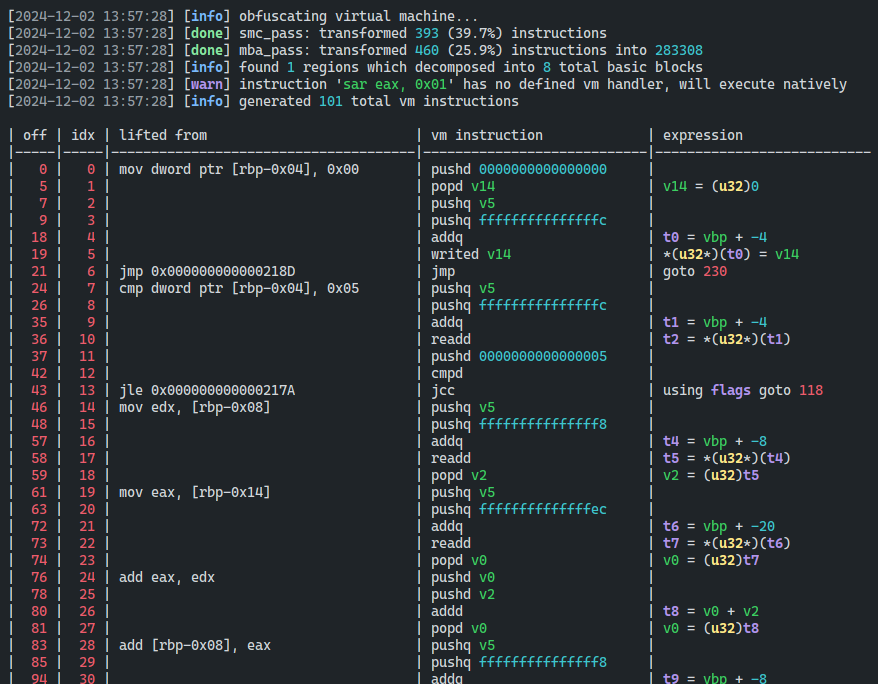 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
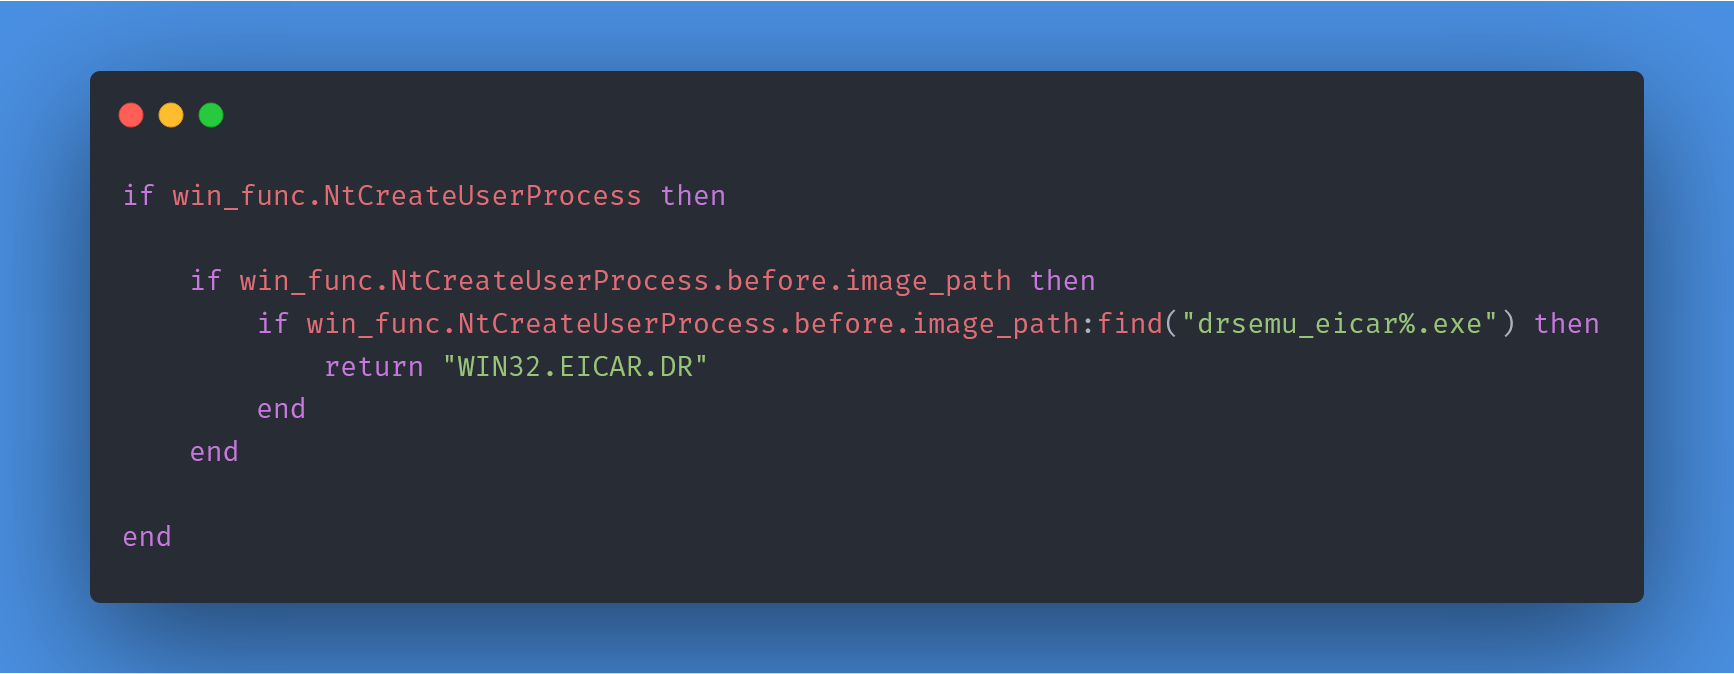 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 oalabs/frida-wshook
Script analysis tool based on Frida.re
 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 gmh5225/ntstrace
frida-stalker based system call tracer on windows(x64).