

Archived
Phantom-Evasion
 oddcod3/phantom-evasion
Python antivirus evasion tool
dynamic-analysis-sandboxingexploit-frameworkspayload-development+6
oddcod3/phantom-evasionPython antivirus evasion tool
 salaheldinfikri/kalim_backdoor
Kalim backdooe Malware Report
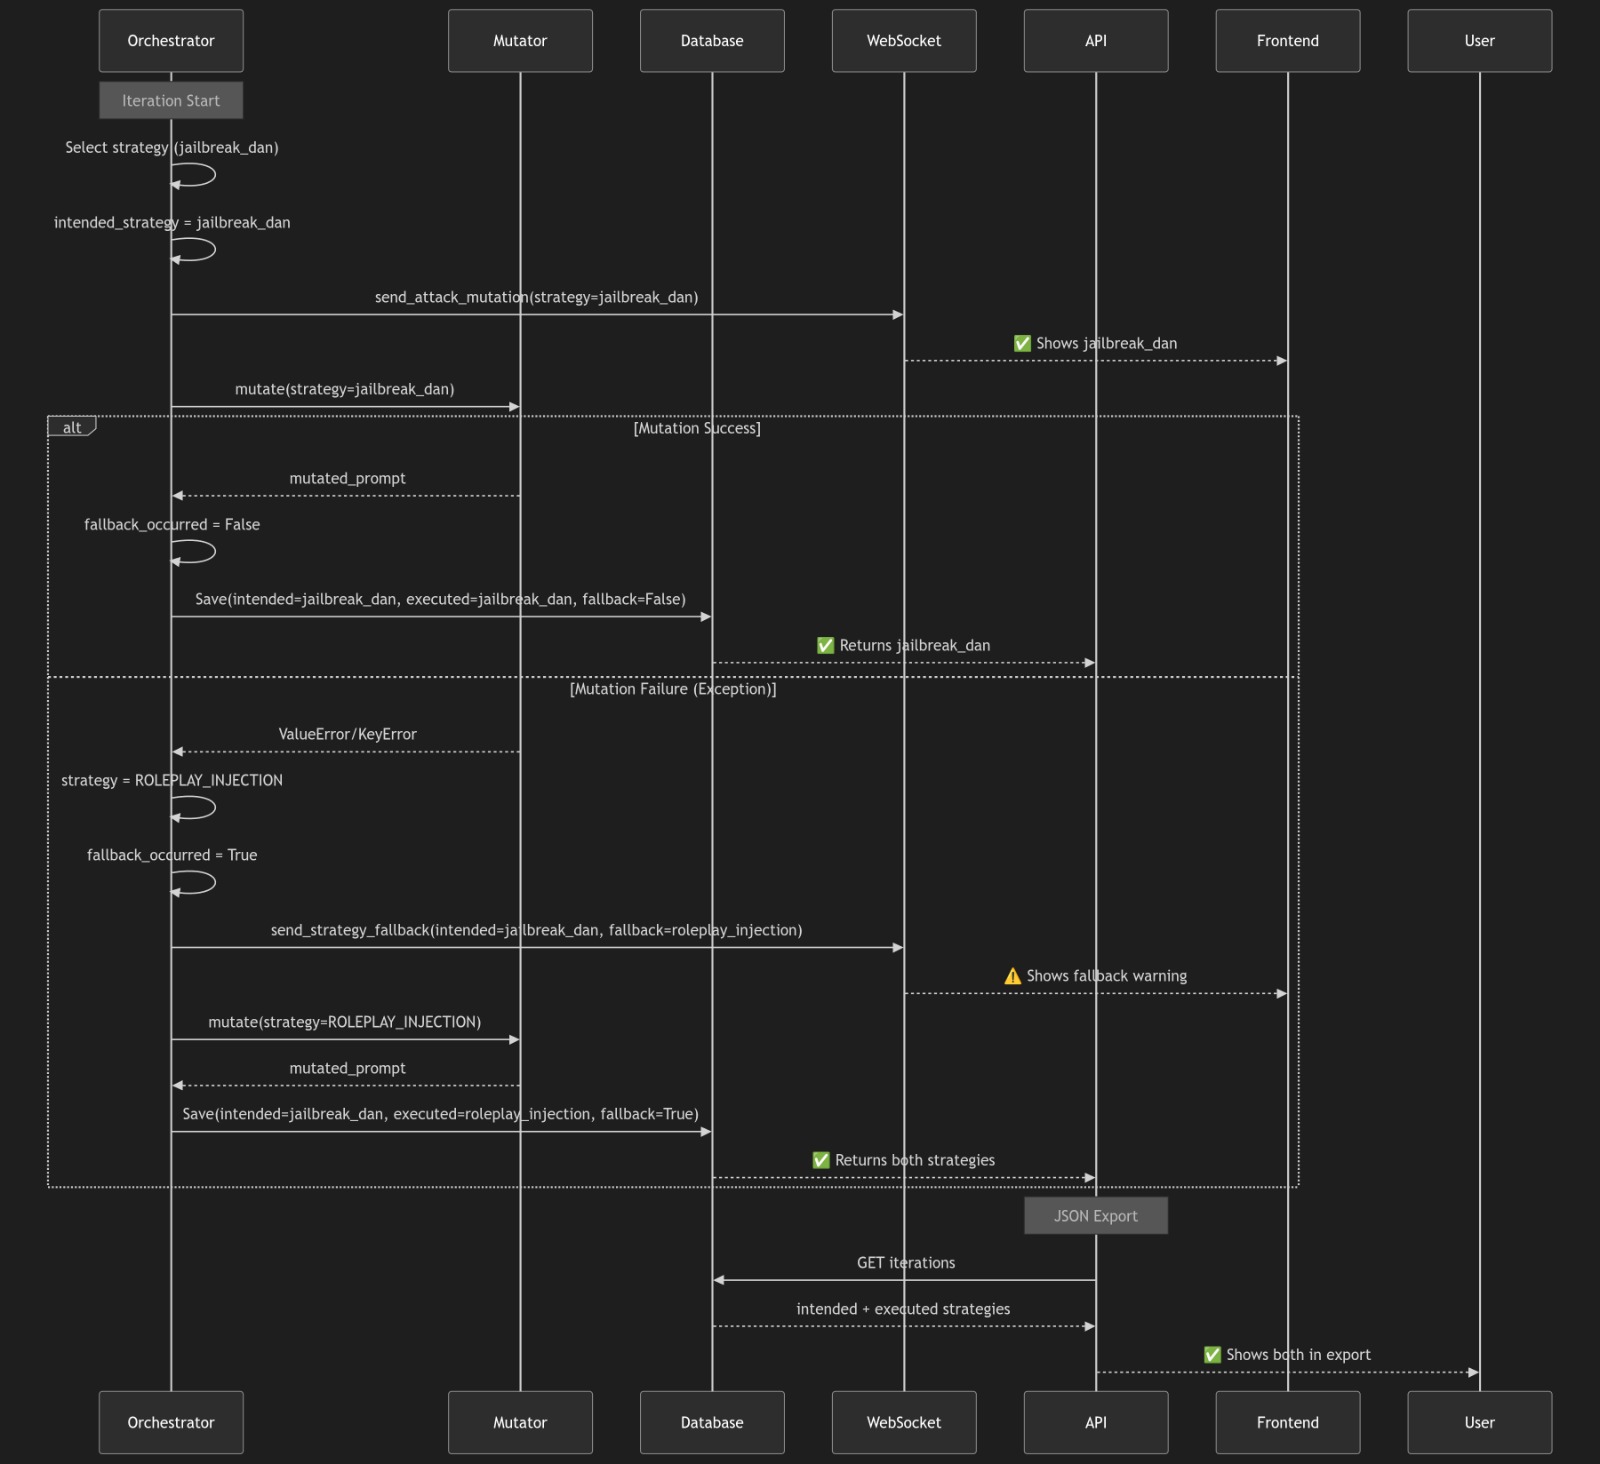 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 angr/angr
A powerful and user-friendly binary analysis platform!
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 darthton/blackbone
Windows memory hacking library
 rapid7/metasploitable3
Metasploitable3 is a VM that is built from the ground up with a large amount of security vulnerabilities.
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
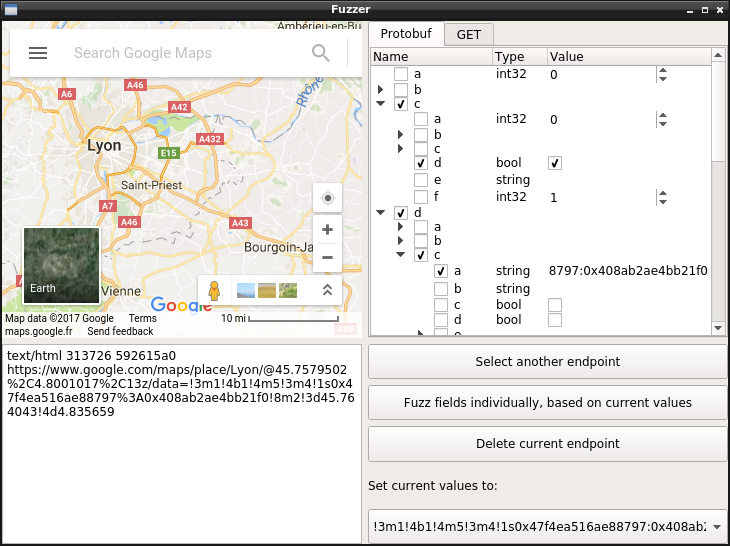 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 ax/apk.sh
Makes reverse engineering Android apps easier, automating repetitive tasks like pulling, decoding, rebuilding and patching an APK.
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
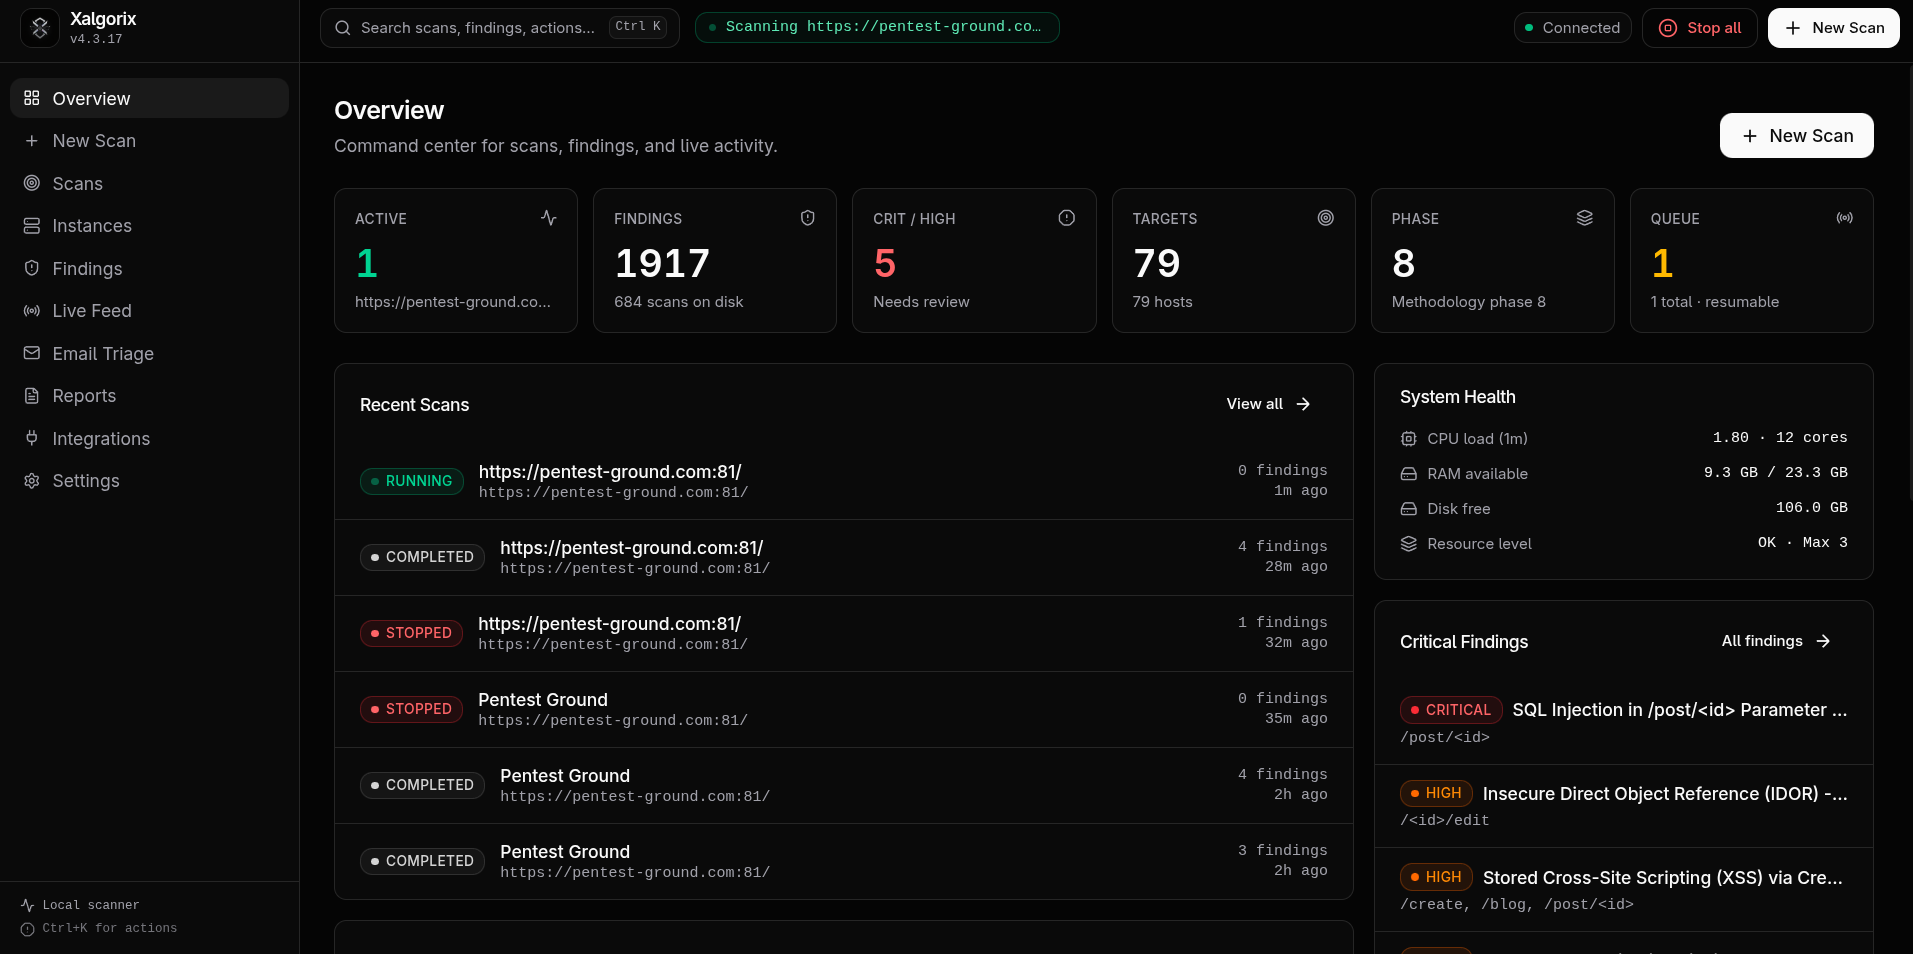 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.