

wtf
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
binary-analysisdynamic-analysis-sandboxingexploitation+2
1.8k
0vercl0k/wtfDistributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
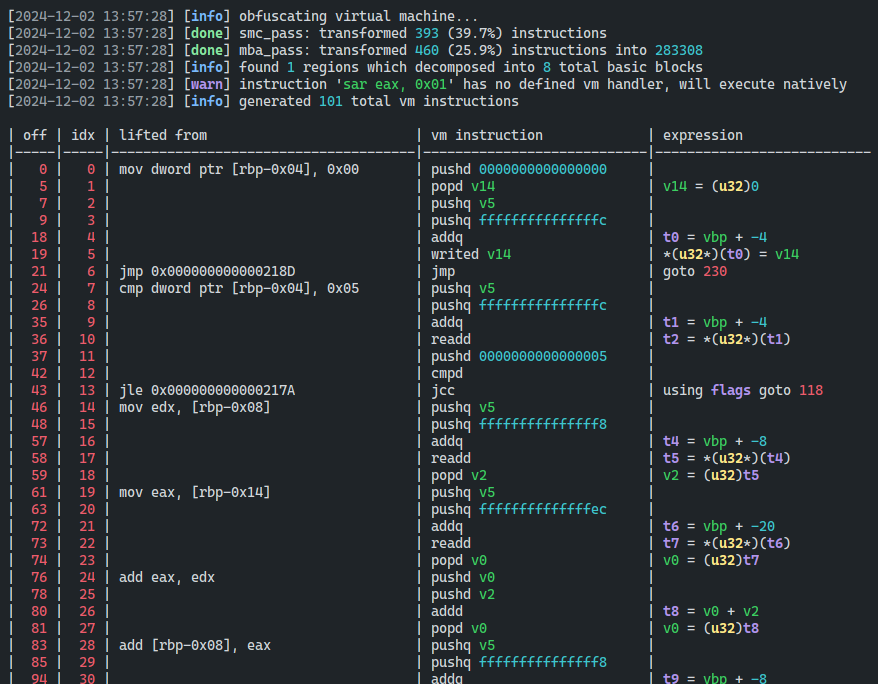 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 mxmssh/drafl
AFL + DynamoRIO = fuzzing binaries with no source code on Linux
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
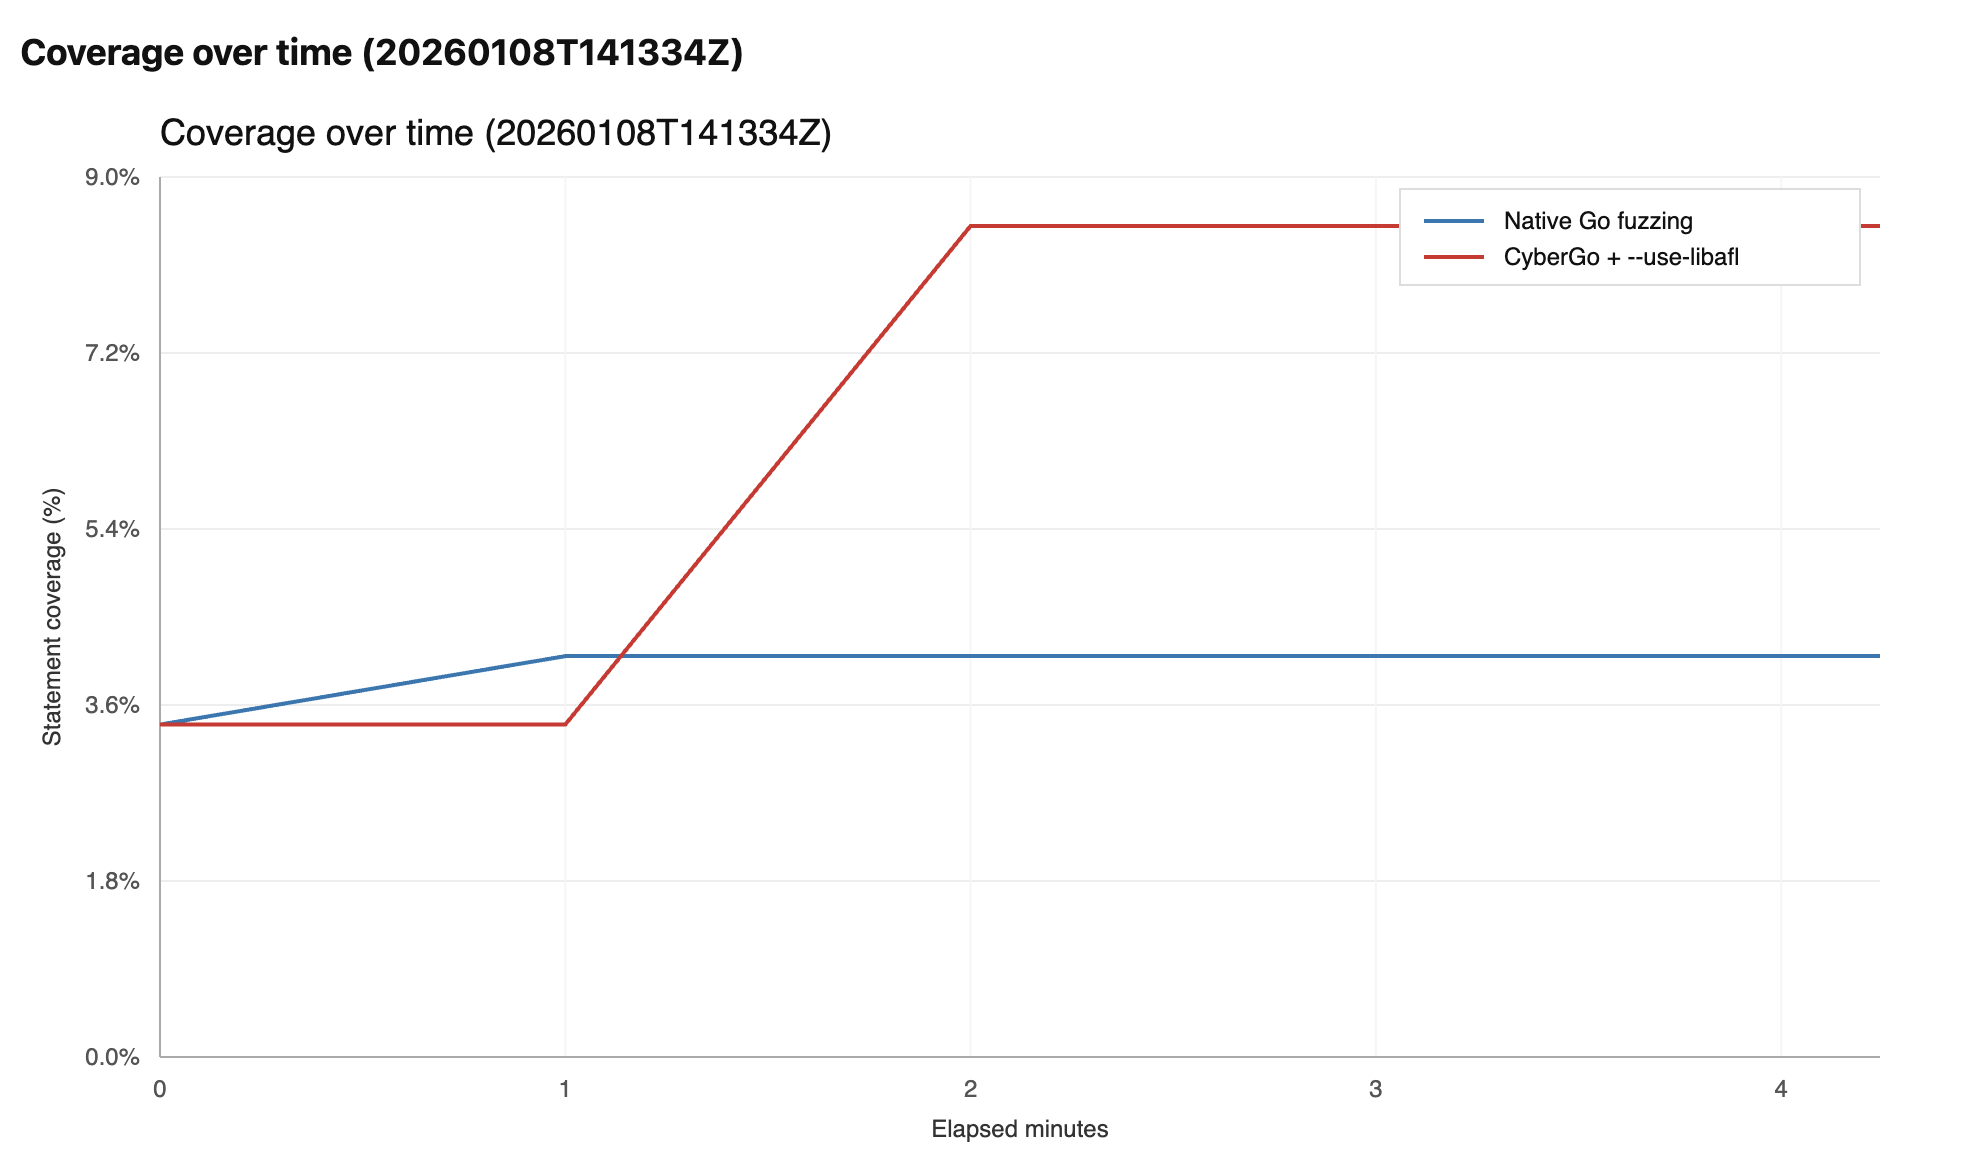 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 giovannigatti/cve-bench
A benchmark for evaluating AI agents on fixing real-world security vulnerabilities.
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 shoucheng3/x-stream__xstream_cve-2020-26217_1-4-14-java77
Java library for XML serialization and deserialization, with a focus on the CVE-2020-26217 deserialization vulnerability exploit.
 shoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1
Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…
 anthropics/defending-code-reference-harness
Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
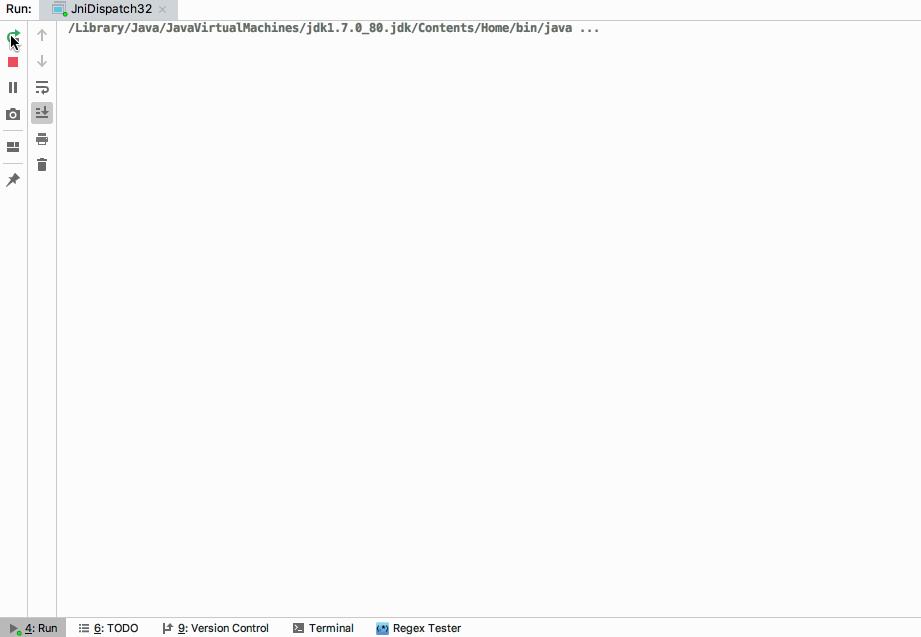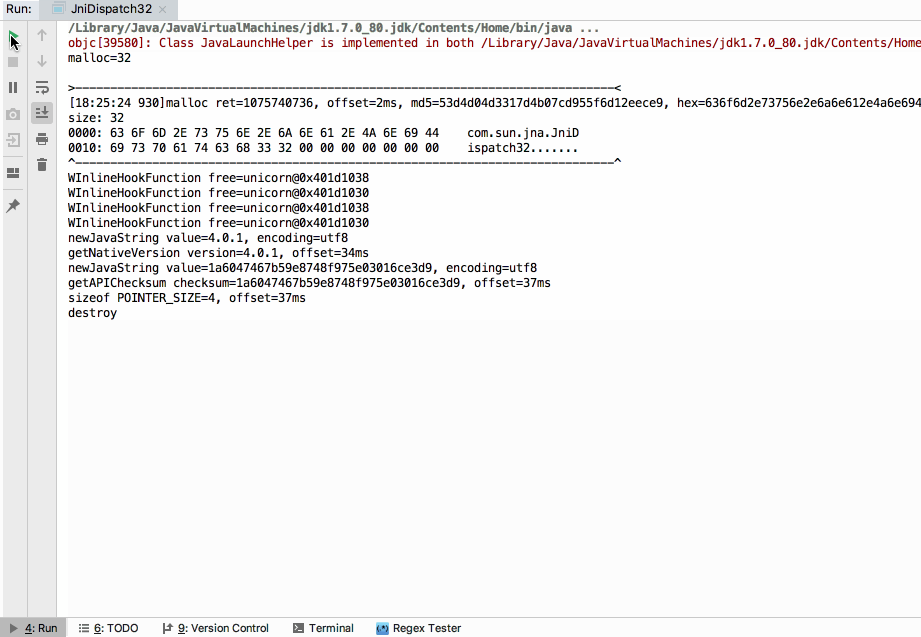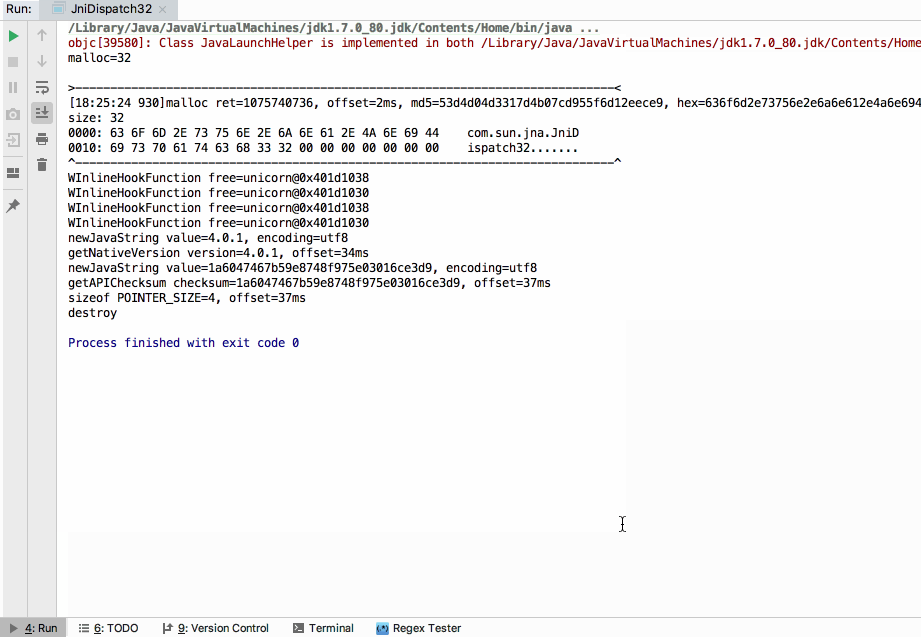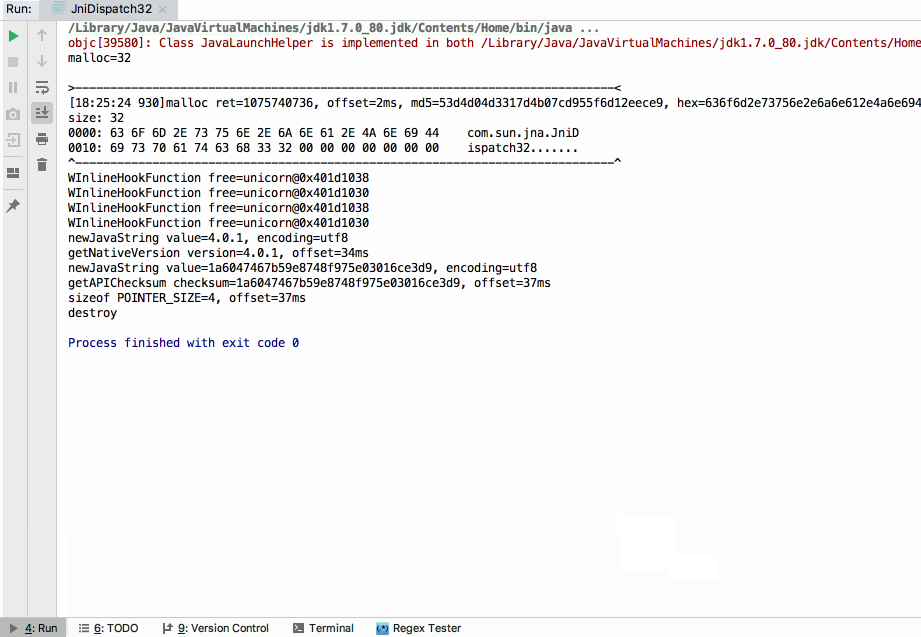 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation