

apiscope
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
kaisonox/apiscopeAn API hooking framework for intercepting and monitoring Windows applications
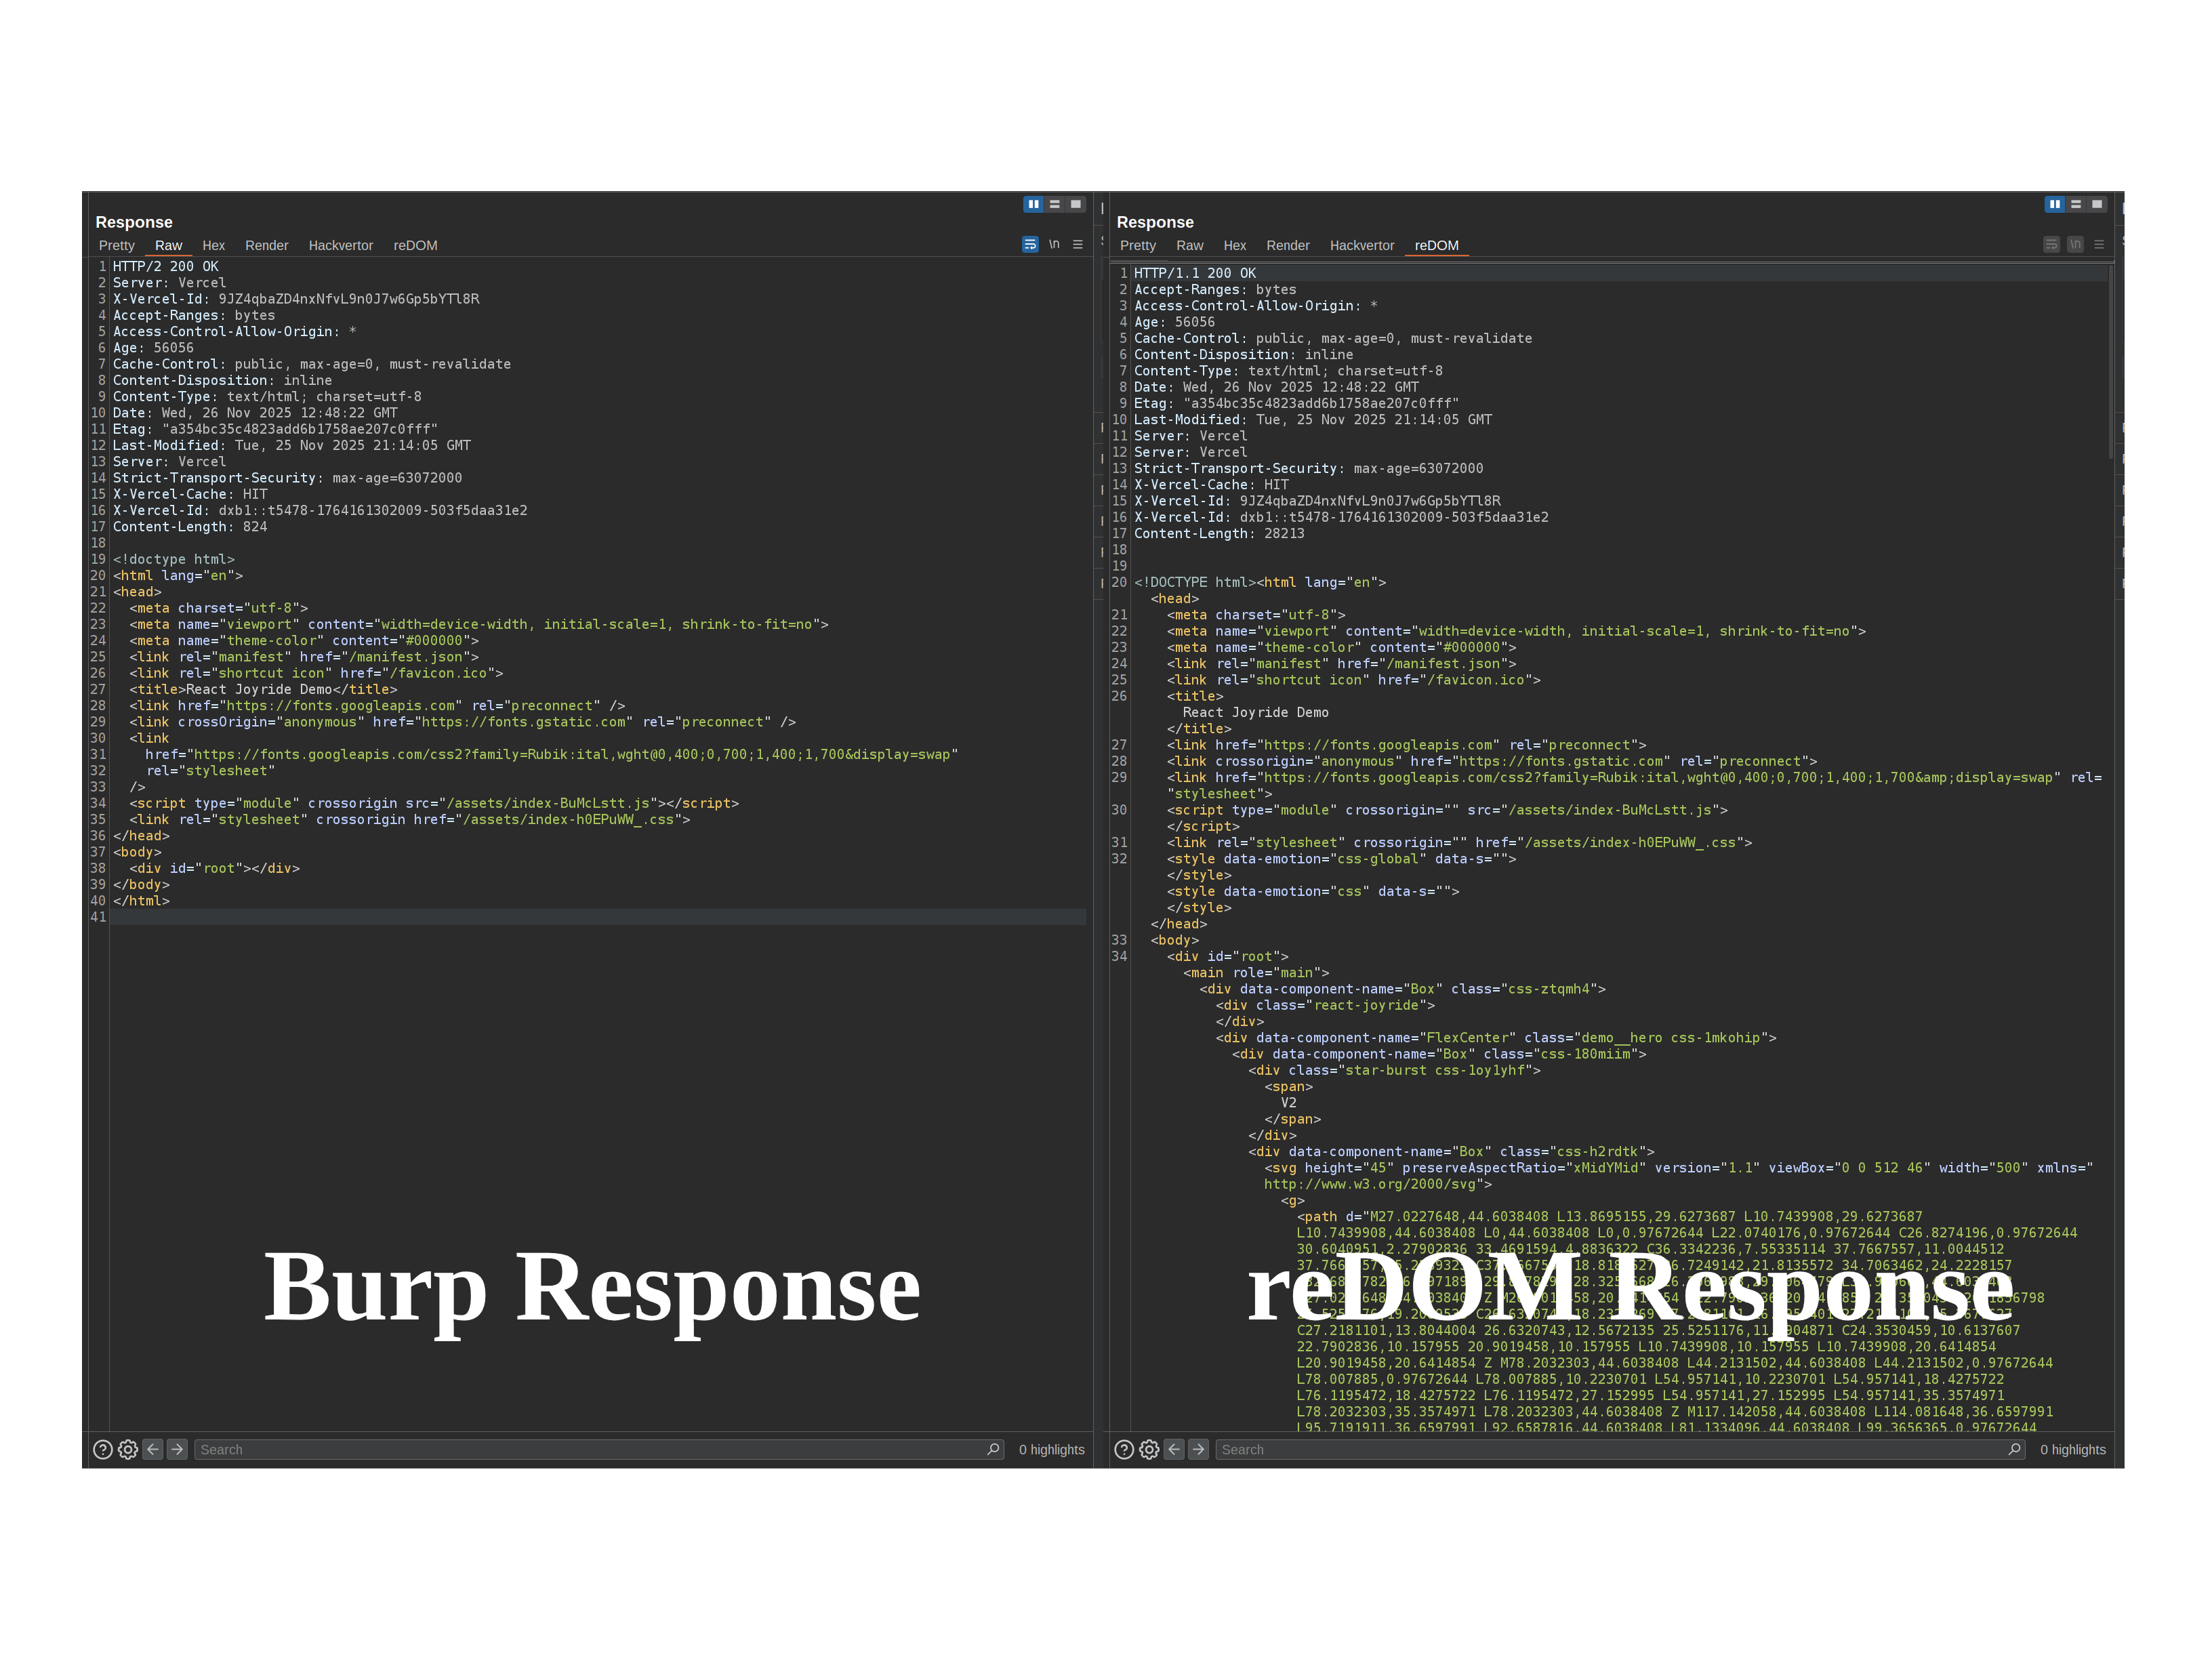 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
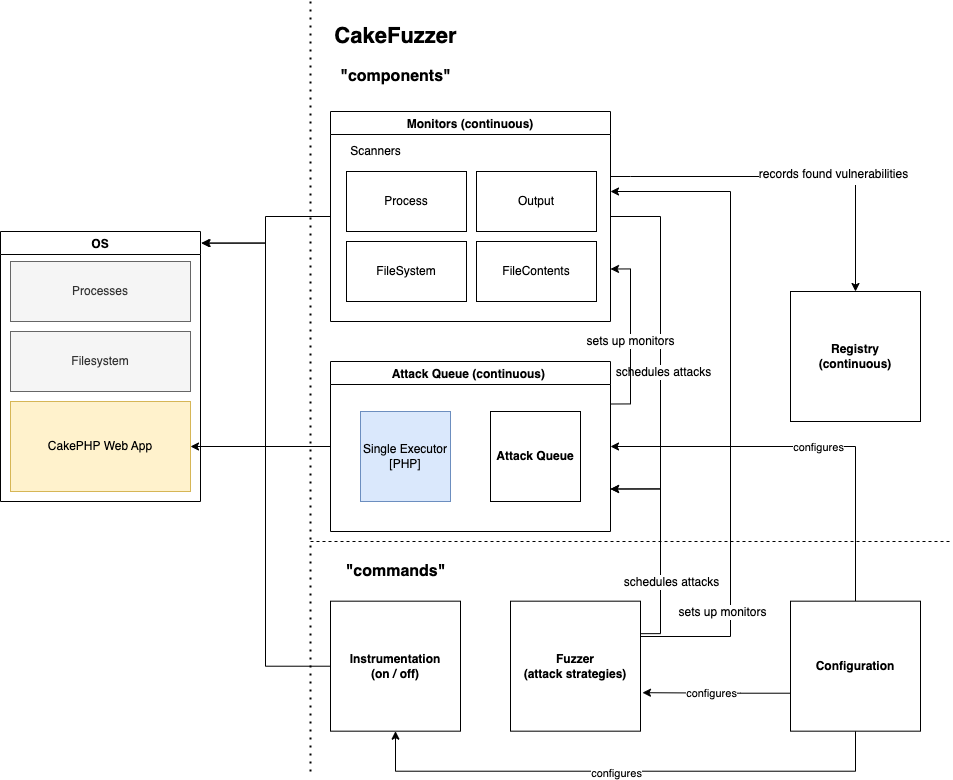 zigrin-security/cakefuzzer
Cake Fuzzer is a project that is meant to help automatically and continuously discover vulnerabilities in web applications created based on specific…
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
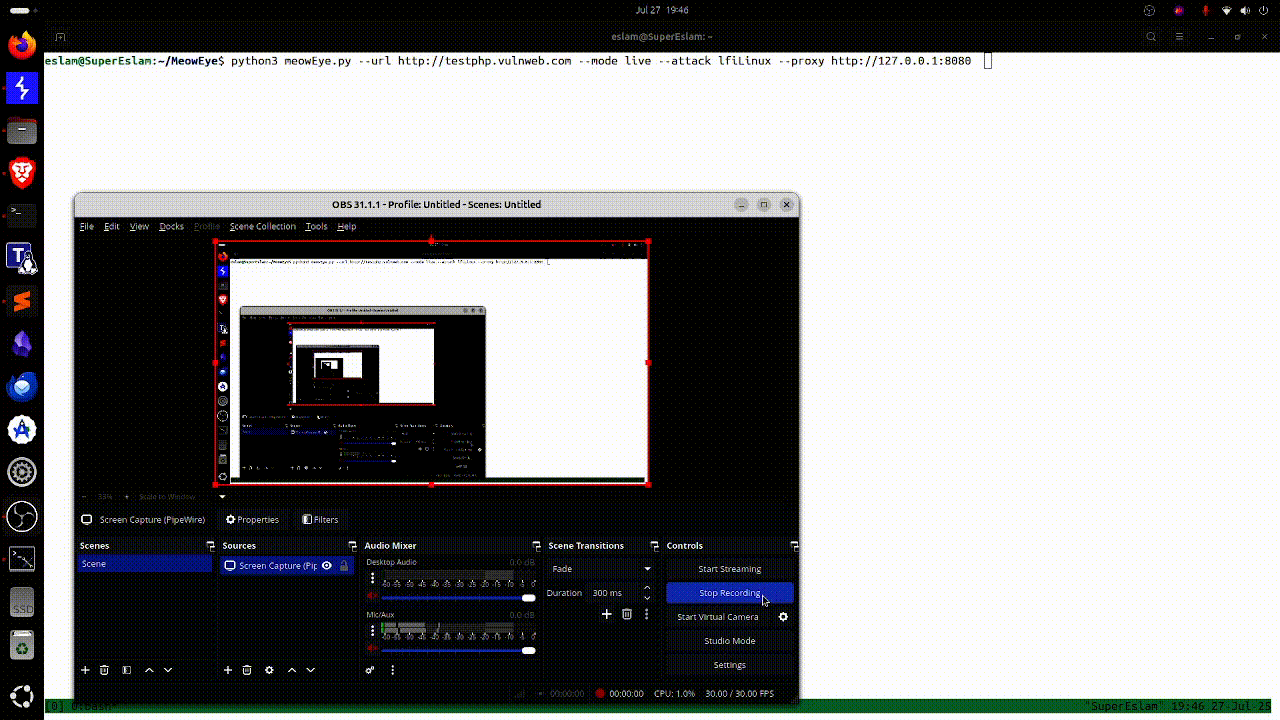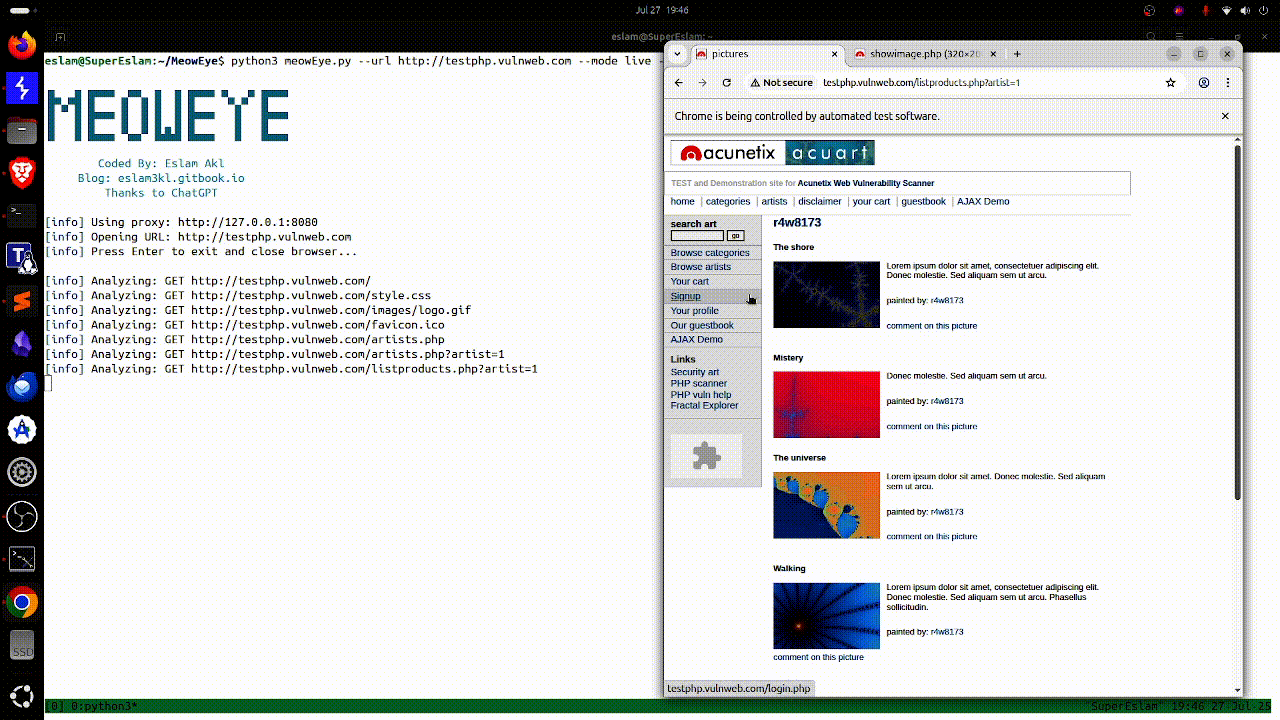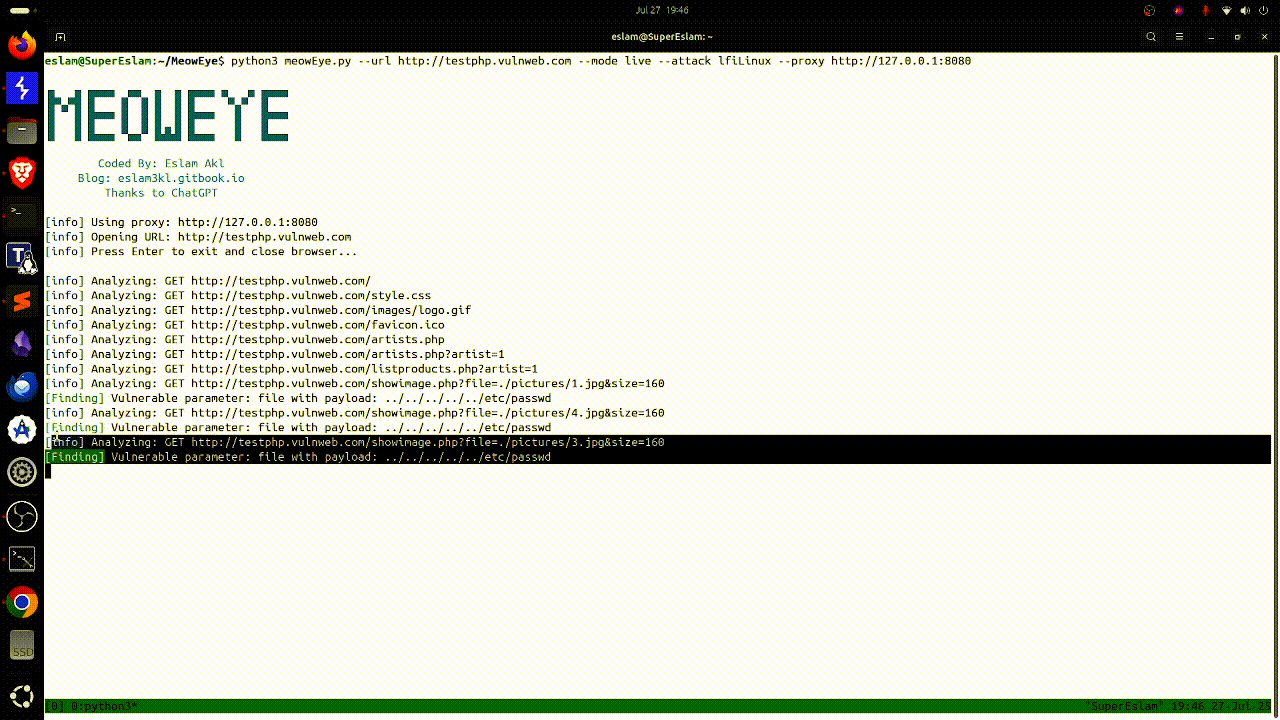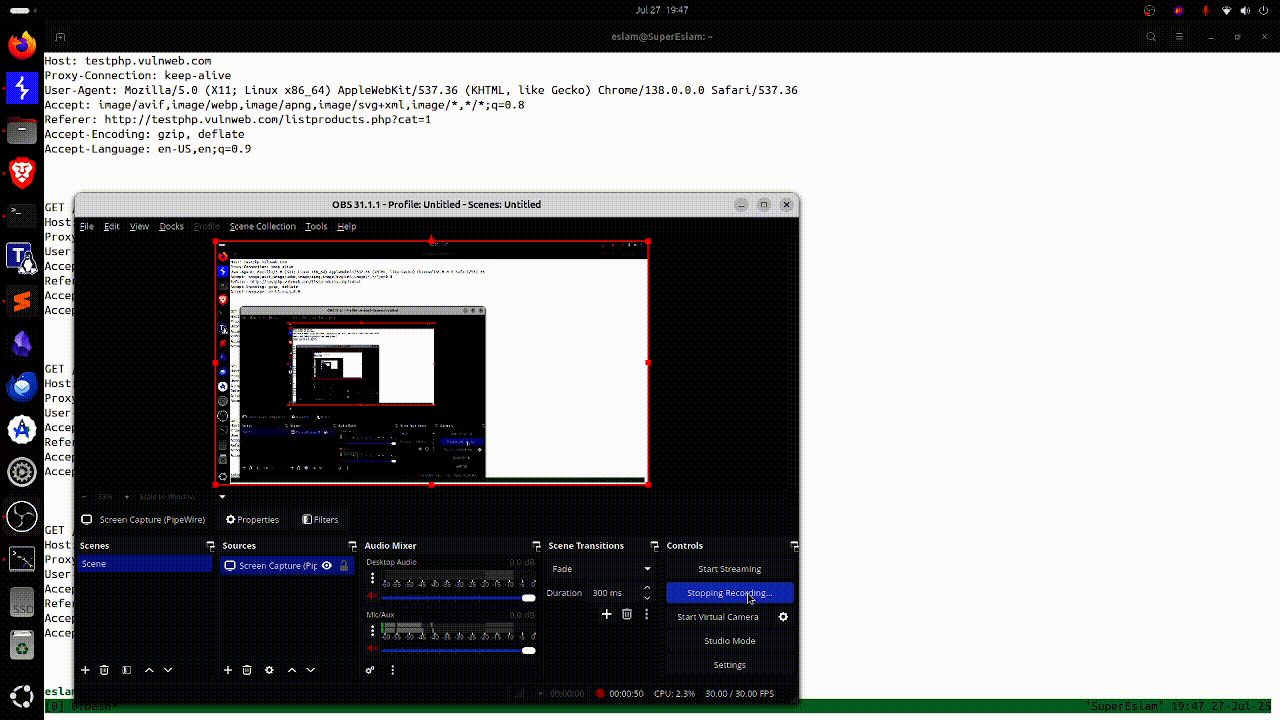 eslam3kl/meoweye
MeowEye is a real-time scanner for identifying multiple web vulnerabilities in live applications.
 fcavallarin/domdig
DOM XSS scanner for Single Page Applications
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 hxsecurity/dongtai
Open-source Interactive Application Security Testing (IAST) tool that passively instruments Java applications to detect vulnerabilities and…
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
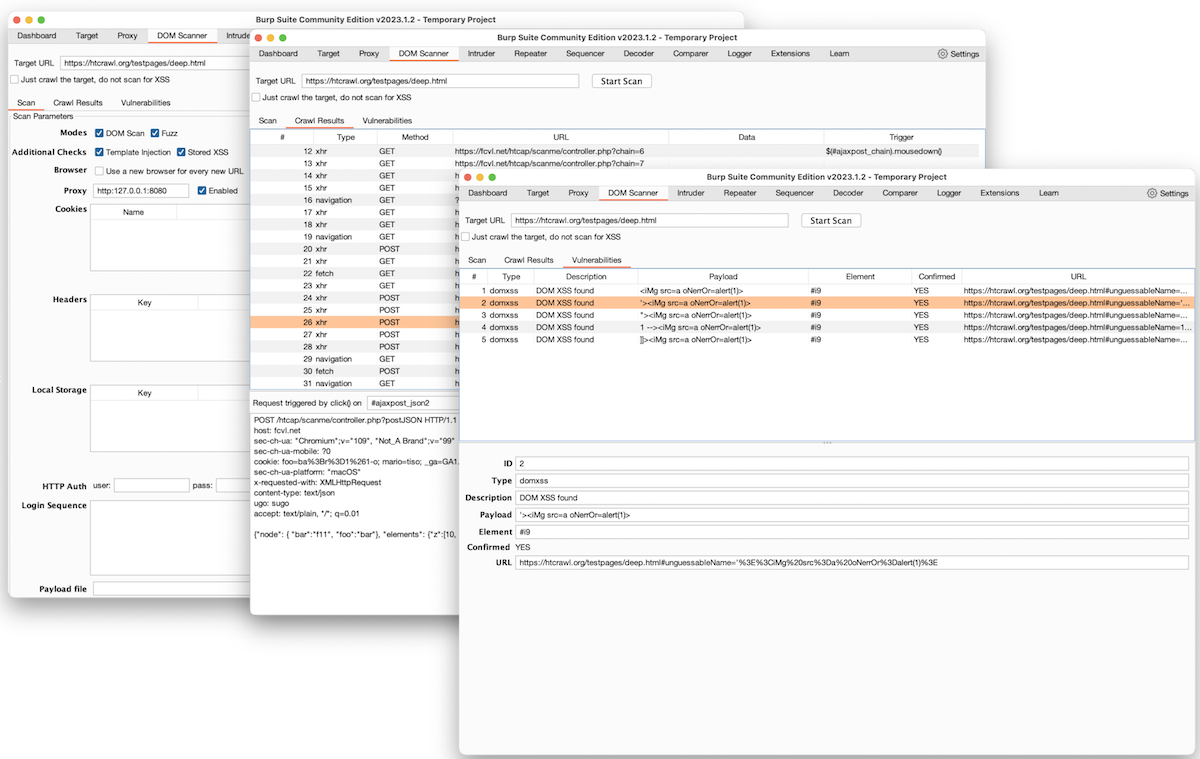 fcavallarin/burp-dom-scanner
Burp Suite's extension to scan and crawl Single Page Applications
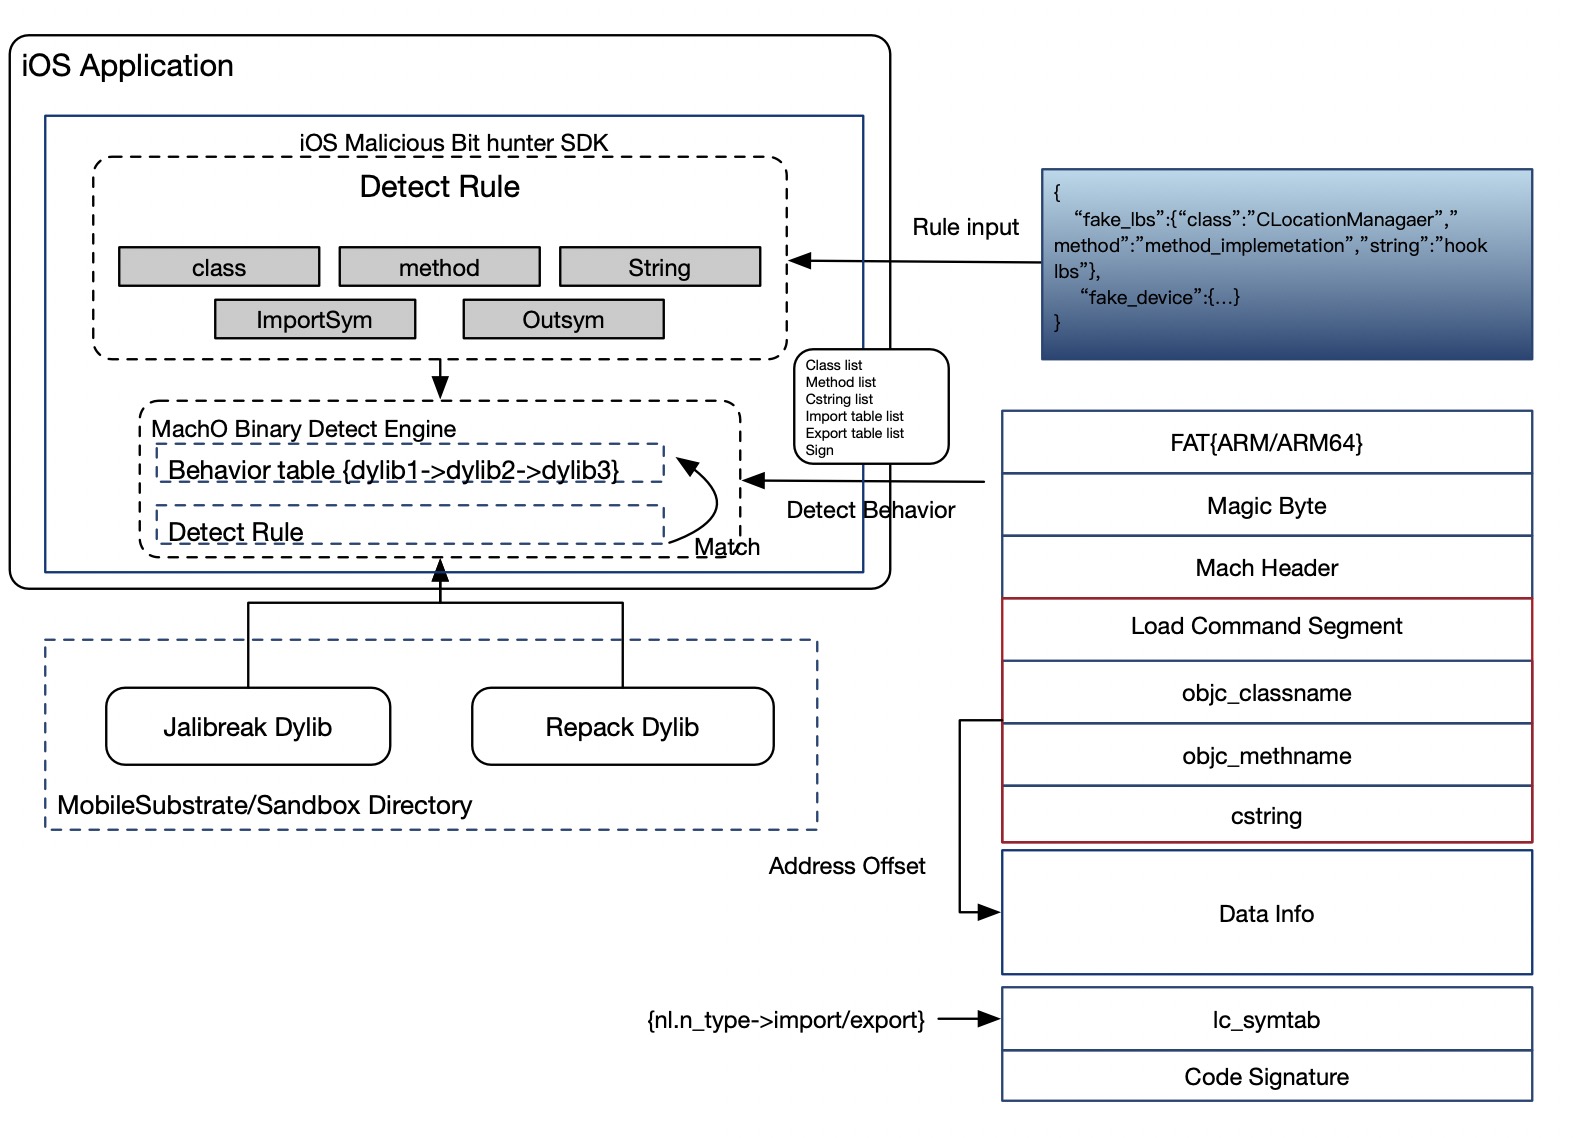 alipay/ios-malicious-bithunter
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…
 h1nayoshi/smalien
Information flow analysis tool for Android applications
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
 trixsec/cve-2025-55182-scanner
A hybrid security scanner for detecting CVE-2025-55182 in Next.js and Waku applications. Features combined static code analysis and safe dynamic…
 lohanichaten/log4j-cve-2021-44228
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) targeting Java applications via JNDI injection for remote code execution.
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)