
processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…

Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…

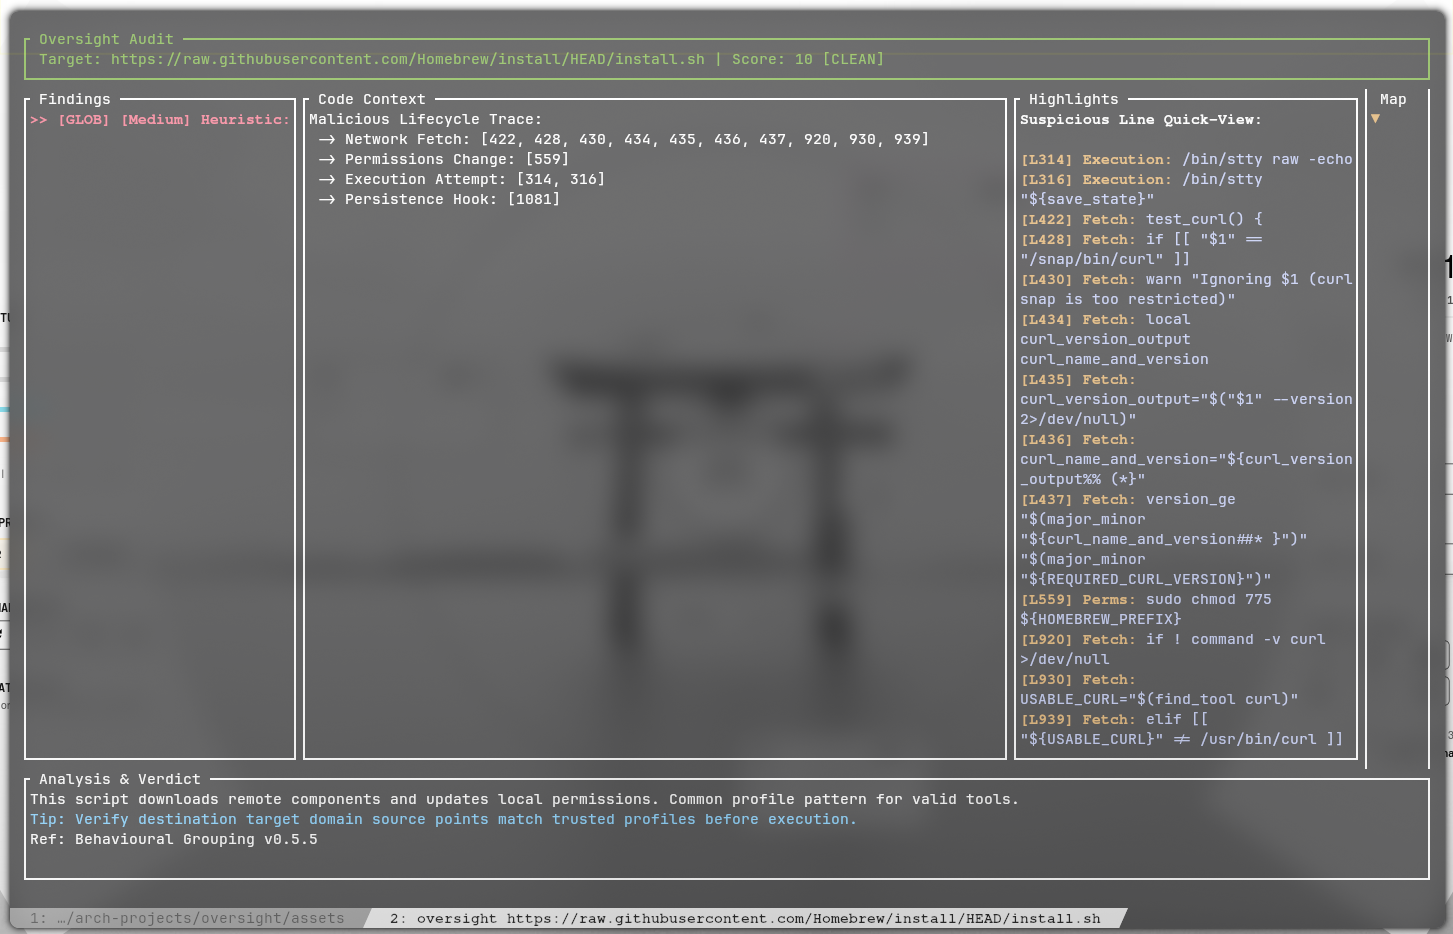
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…

Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…

Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.

End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…

Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.

A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…

Secure and fast microVMs for serverless computing.

Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…

Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

Policy-driven, layered isolation and containment

Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.

Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…

Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…

Executes untrusted Python, JavaScript, and Bash in a hardened jail with 5-second, 128 MB, 0.5-core, PID and output limits.

FastGPT Python sandbox escape chain audit tool (CVE-2026-32128 related, v4.14.8 inspect chain)

Agent-based JMX access via JSON/HTTP with bulk requests, fine-grained security policies, and proxy mode for remote MBeanServer monitoring and…