
WFH
 conscioushacker/wfh
Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
binary-analysisdynamic-analysis-sandboxingexploitation+1
437
conscioushacker/wfhFrida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
 4ier/neo
Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.
 mxmssh/drafl
AFL + DynamoRIO = fuzzing binaries with no source code on Linux
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 nccgroup/umap2
Umap2 is the second revision of NCC Group's python based USB host security assessment tool.
 trailofbits/test-fuzz
Rust macros and Cargo subcommand to automate fuzzing with afl.rs, including corpus generation and harness implementation, integrated with Rust's…
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
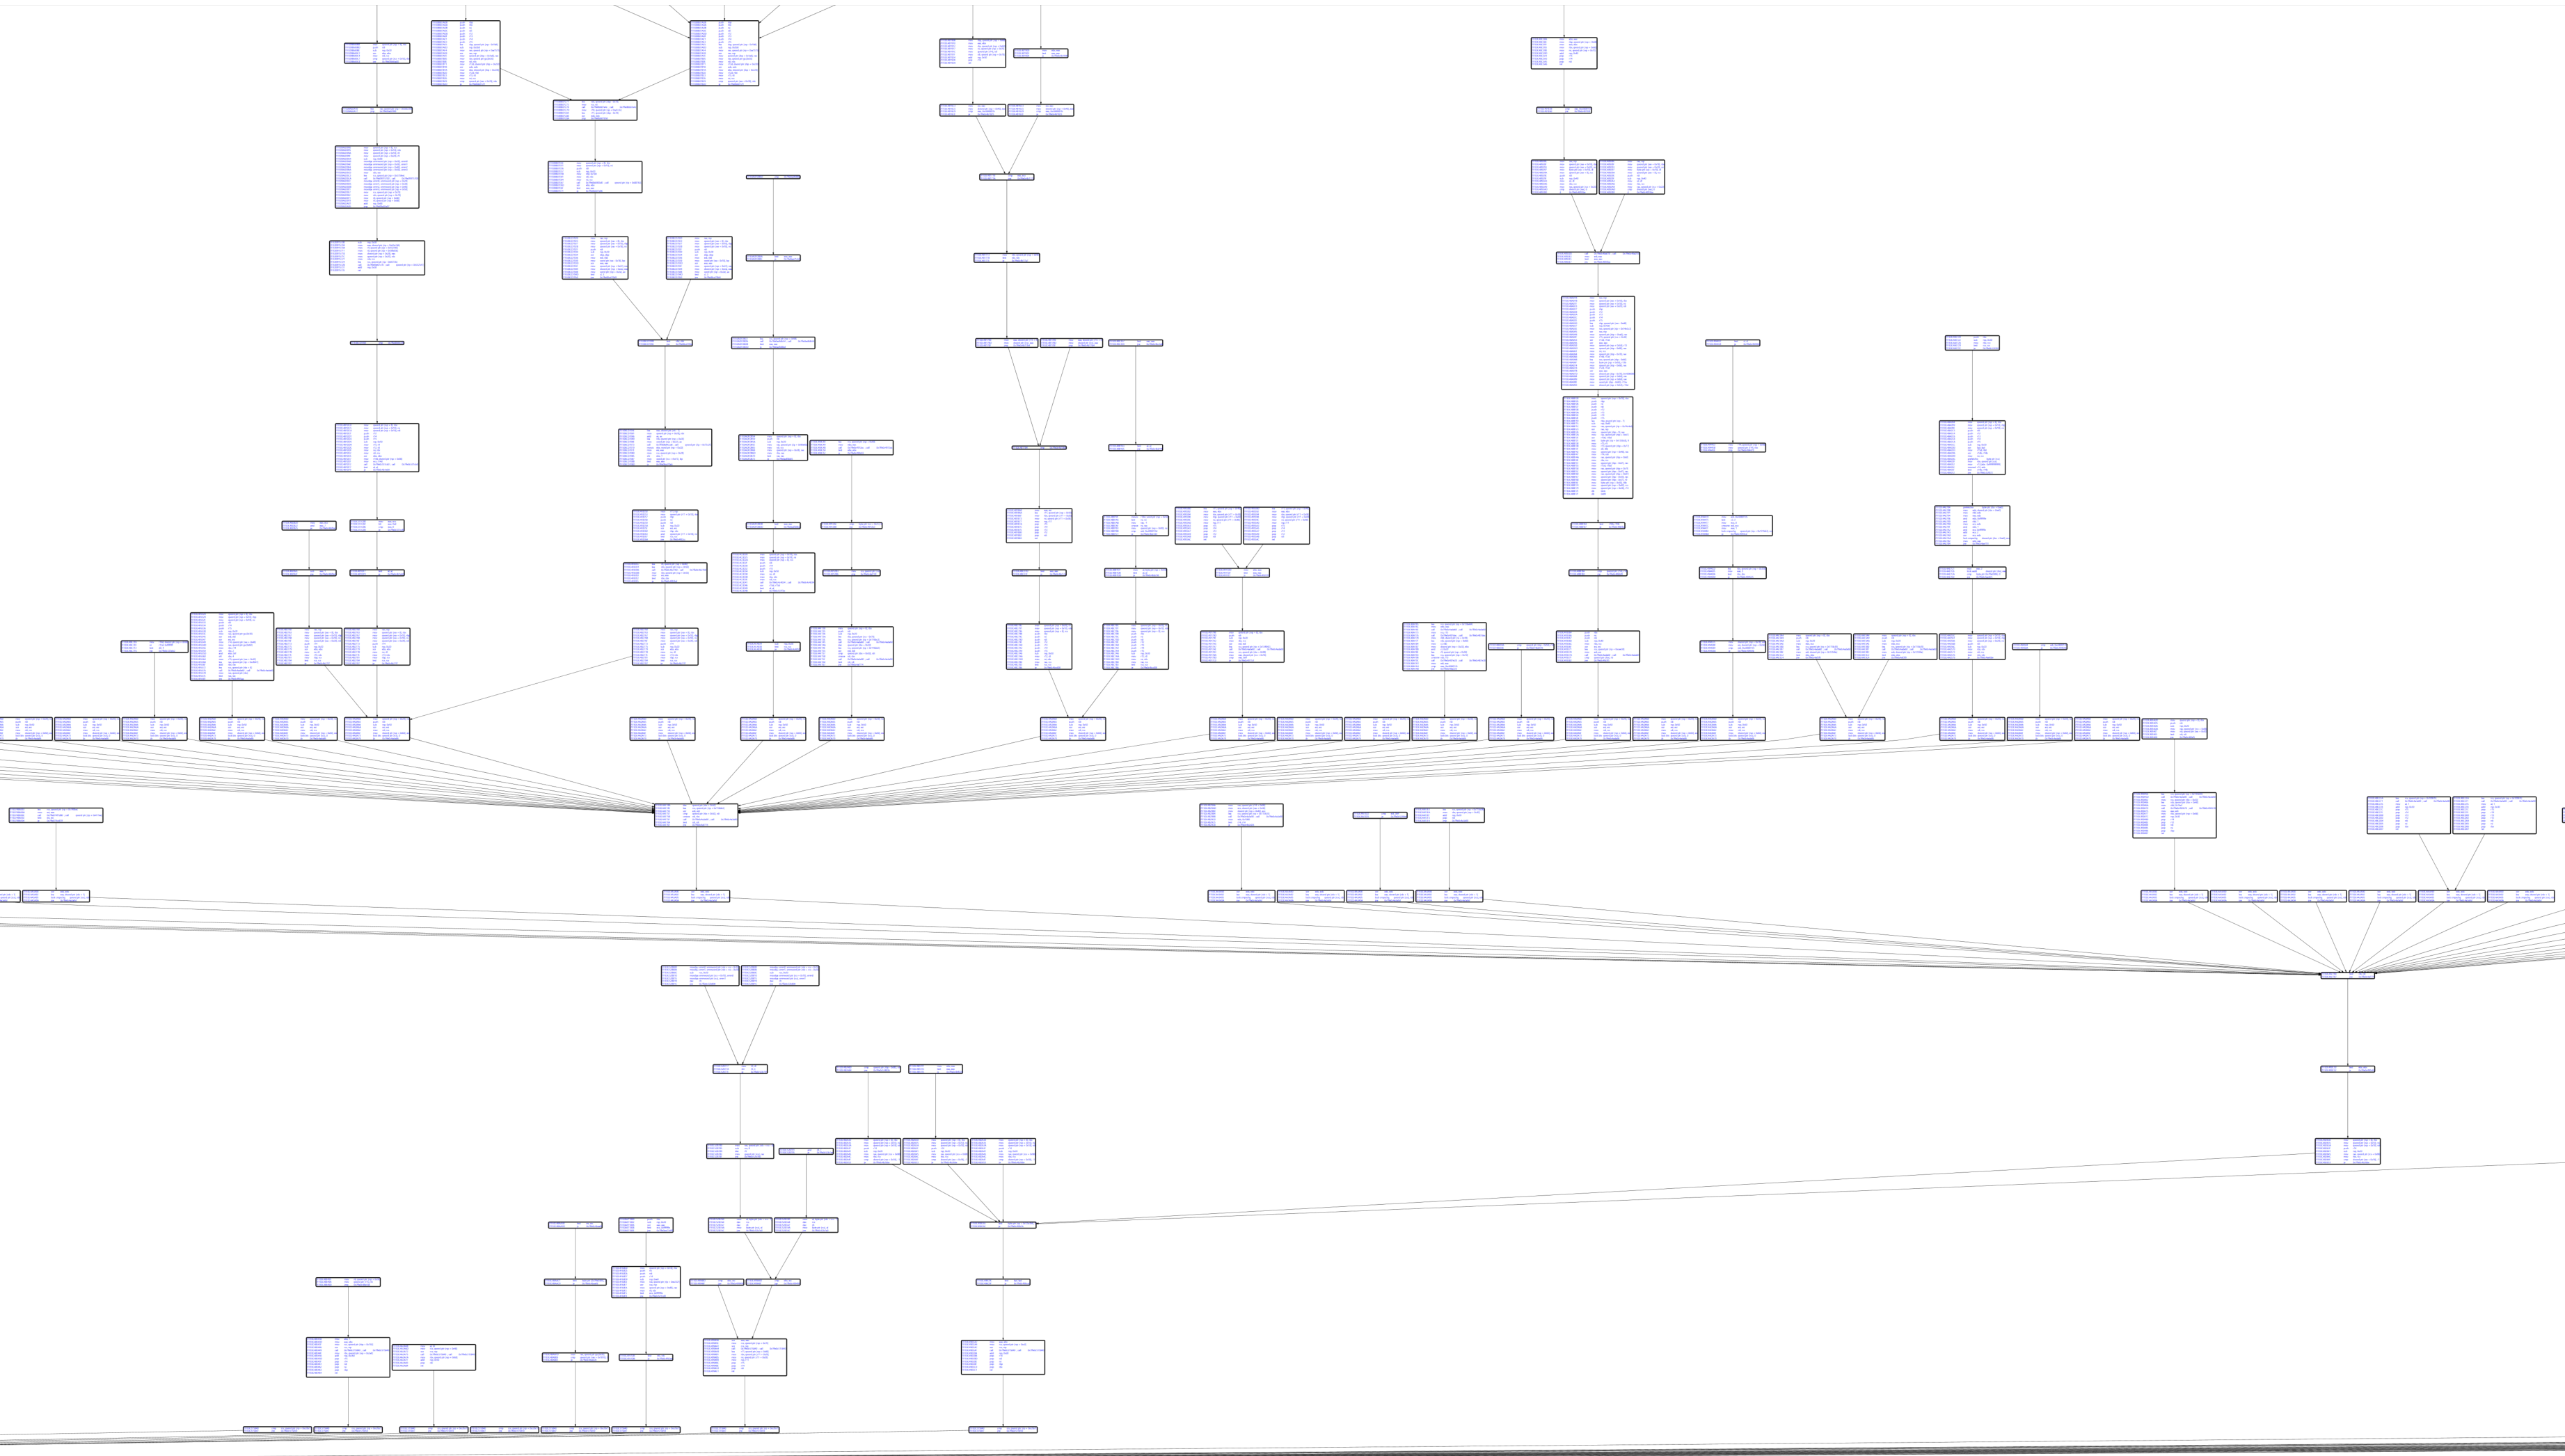 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 fcavallarin/domdig
DOM XSS scanner for Single Page Applications
 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
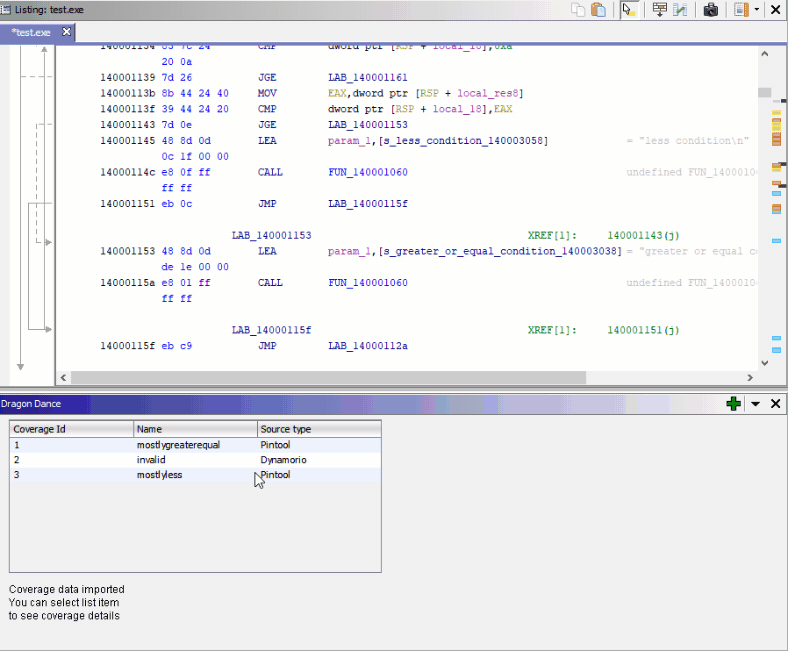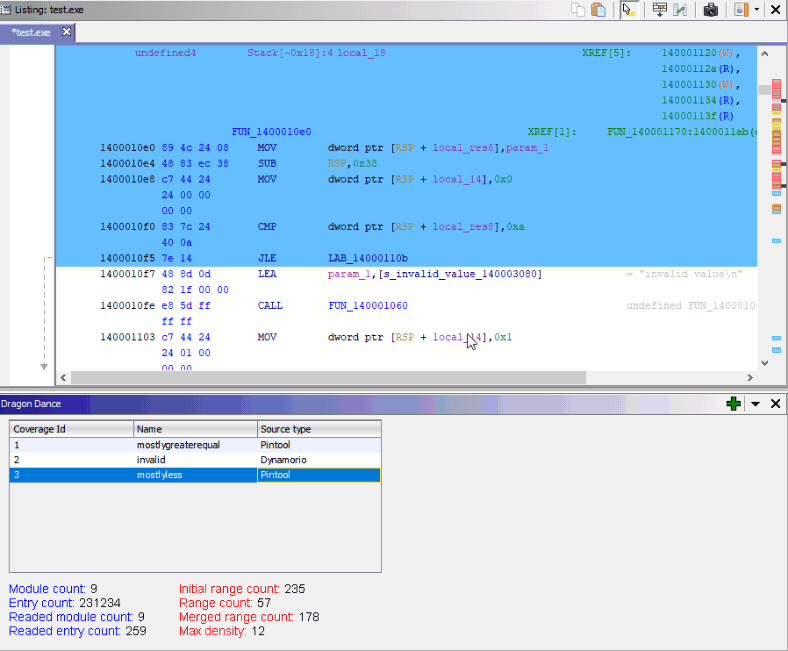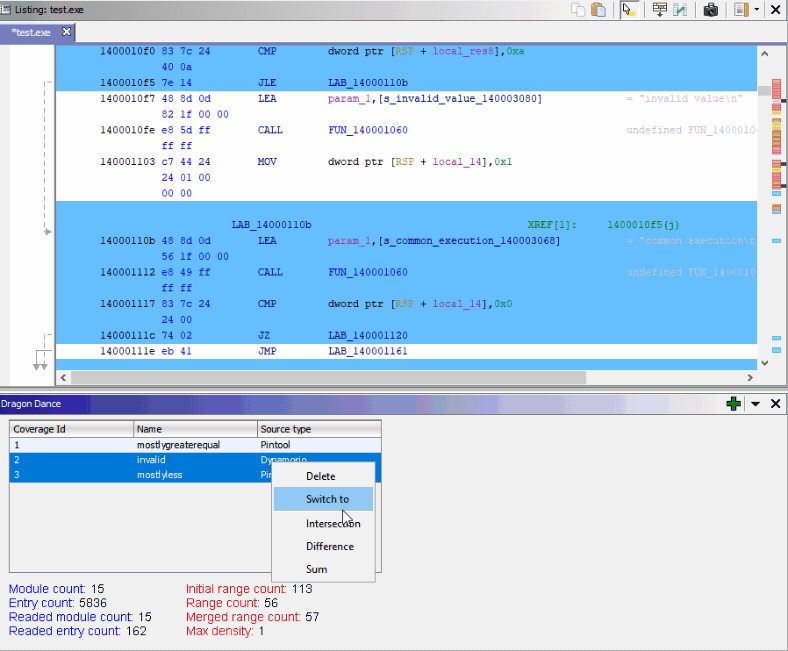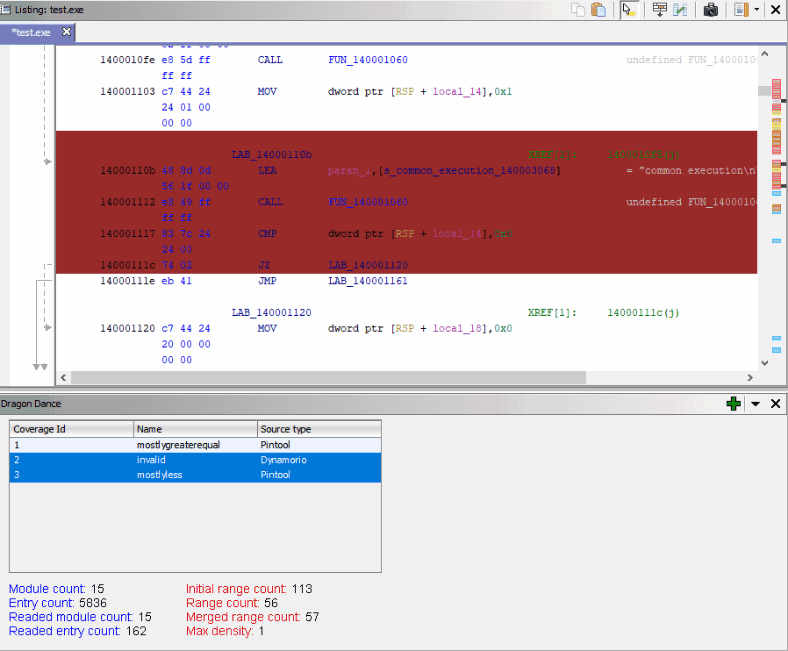 0ffffffffh/dragondance
Binary code coverage visualizer plugin for Ghidra
 amossys/memitm
Tool to make in memory man in the middle
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.