
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
109 results
ioctlance preview

ioctlance

GitHubzeze-zeze/ioctlance

A tool that is used to hunt vulnerabilities in x64 WDM drivers
binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
474
3 months ago
binder-trace preview

binder-trace

GitHubfoundryzero/binder-trace

Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".

android-securitybinary-analysisdynamic-analysis-sandboxing+3
7701 year ago
WSSAT preview

WSSAT

GitHubyalcinyolalan/wssat

WEB SERVICE SECURITY ASSESSMENT TOOL
api-security-testingdynamic-analysis-sandboxinginformation-gathering+3
3885 years ago
EhTrace preview

EhTrace

GitHubk2/ehtrace

ATrace is a tool for tracing execution of binaries on Windows.
binary-analysiscode-analysisdebuggers+4
24510 months ago
spamscanner preview

spamscanner

GitHubspamscanner/spamscanner

Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…
anti-botdynamic-analysis-sandboxingemail-security+6
3749 months ago
frida-extract preview

frida-extract

GitHuboalabs/frida-extract

Frida.re based RunPE (and MapViewOfSection) extraction tool
binary-analysisdynamic-analysis-sandboxingeducation+3
1159 years ago
sigwire preview

sigwire

GitHubyeet-src/sigwire

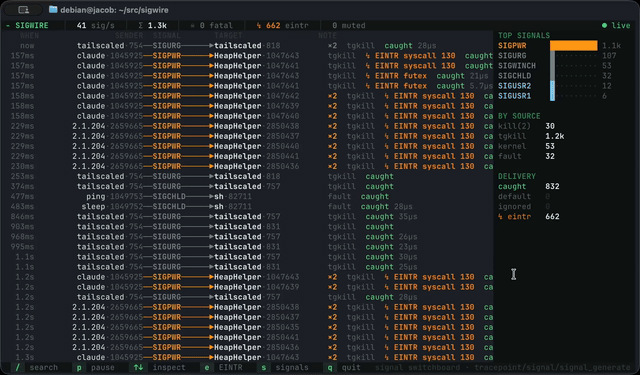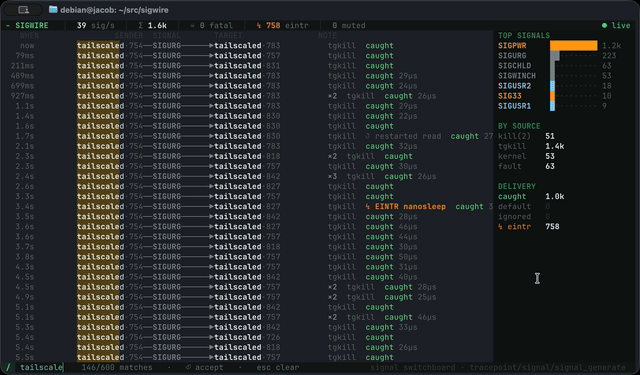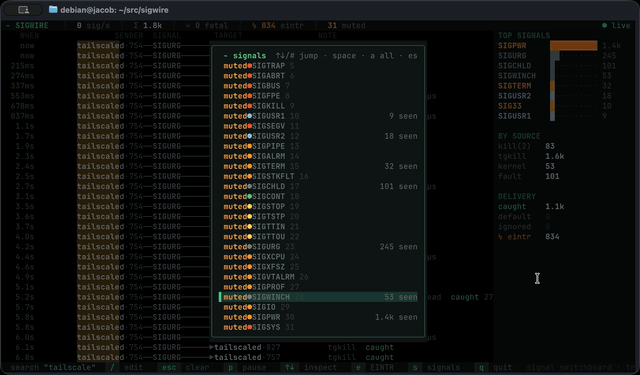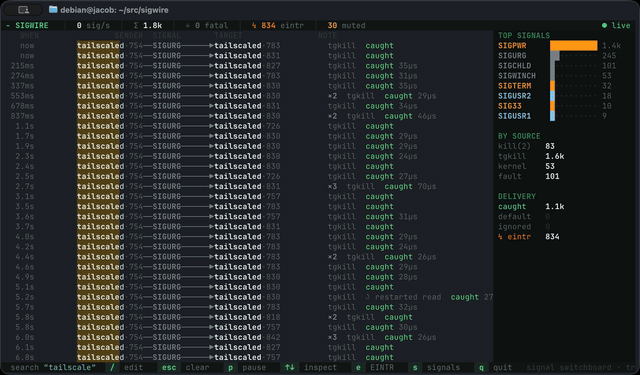
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
debuggersdynamic-analysis-sandboxingforensics+2
1611 month ago
Squalr preview

Squalr

GitHubsqualr/squalr

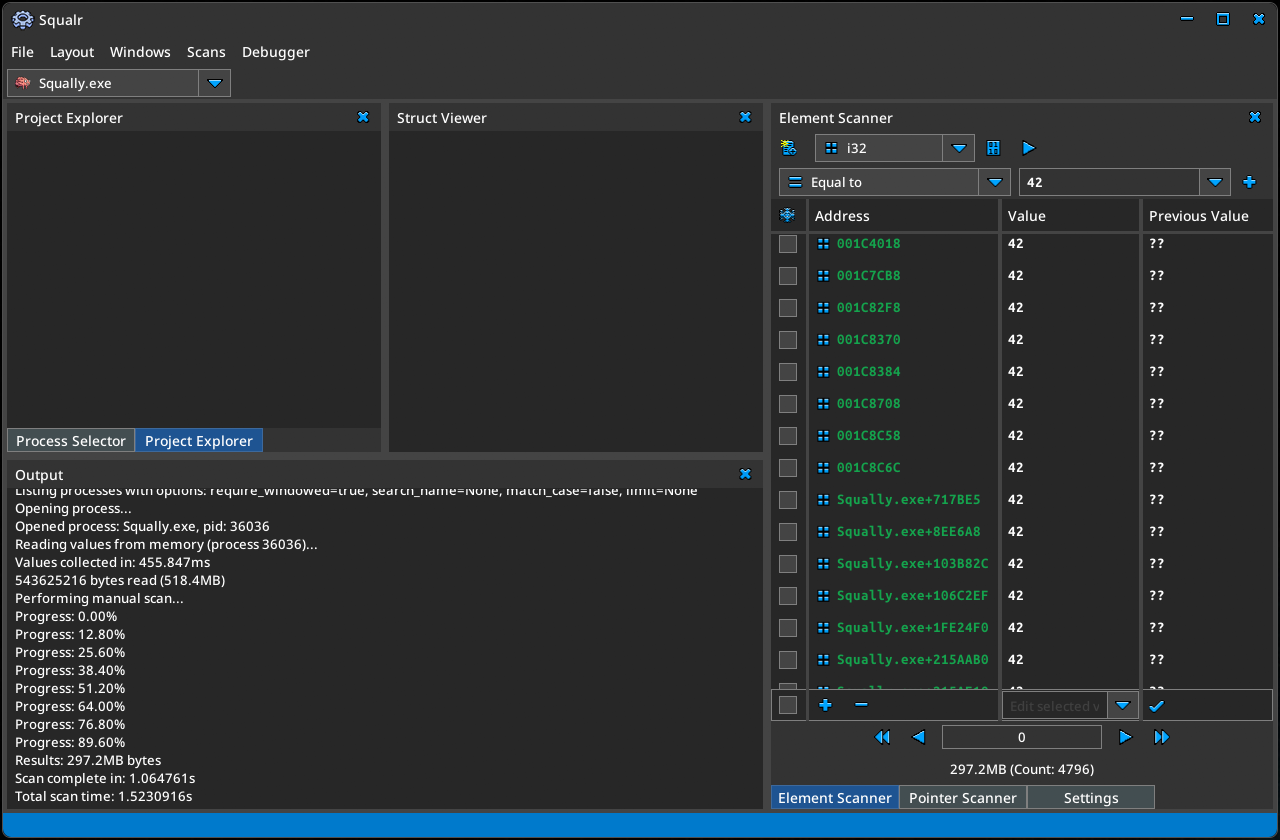
A generic game/software hacking tool written from the ground up in Rust.
binary-analysisdebuggersdynamic-analysis-sandboxing+5
1773 months ago
gftrace preview

gftrace

GitHubleandrofroes/gftrace

A command line Windows API tracing tool for Golang binaries.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
1592 years ago
PulseAPK-Core preview

PulseAPK-Core

GitHubdeemoun/pulseapk-core

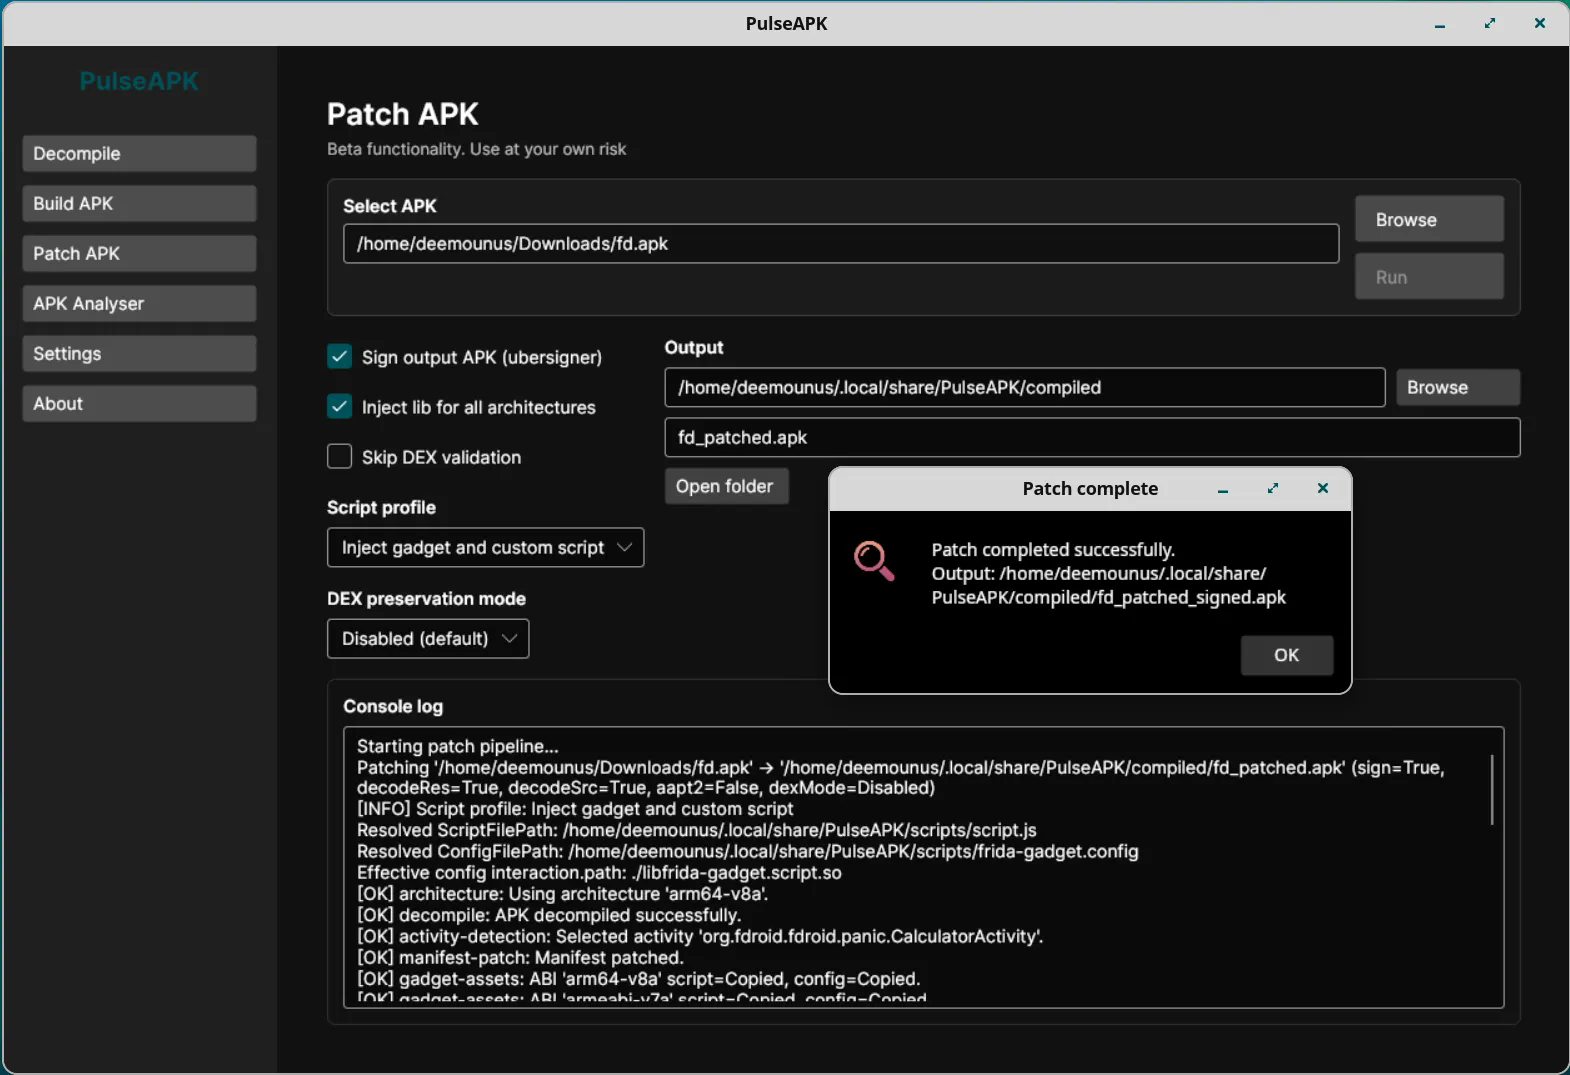
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building

android-securitybinary-analysisdynamic-analysis-sandboxing+8
1222 months ago
aDLL preview

aDLL

GitHubideaslocas/adll

Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…
binary-analysisdynamic-analysis-sandboxingexploitation+1
735 years ago
noia preview

noia

GitHub0x742/noia

Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
android-securitydynamic-analysis-sandboxingforensics+3
1285 years ago
incarcero preview

incarcero

GitHub0x48piraj/incarcero

Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…

cloud-securitycurated-resourcesdynamic-analysis-sandboxing+4
932 years ago
Shinigami preview

Shinigami

GitHubbuzzer-re/shinigami

A dynamic unpacking tool
binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
1523 years ago
OpenClawMachines preview

OpenClawMachines

GitHubmathaix/openclawmachines

Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives

ai-securityauthenticationcloud-security+6
582 months ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
672 months ago
vmprotect-research preview

vmprotect-research

GitHubrasetsuu/vmprotect-research

Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…
binary-analysisbinary-exploitationdebuggers+6
623 months ago
mnemosyne preview

mnemosyne

GitHubnccgroup/mnemosyne

A Generic Windows Memory Scraping Tool

dynamic-analysis-sandboxingfuzzinginformation-gathering+2
699 years ago
Previous1234567Next