
barf-project
 programa-stic/barf-project
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
binary-analysisdynamic-analysis-sandboxingeducation+5
1.5k
programa-stic/barf-projectBARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
 openrce/paimei
A reverse engineering framework written in Python.
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 adshao/flounder
Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
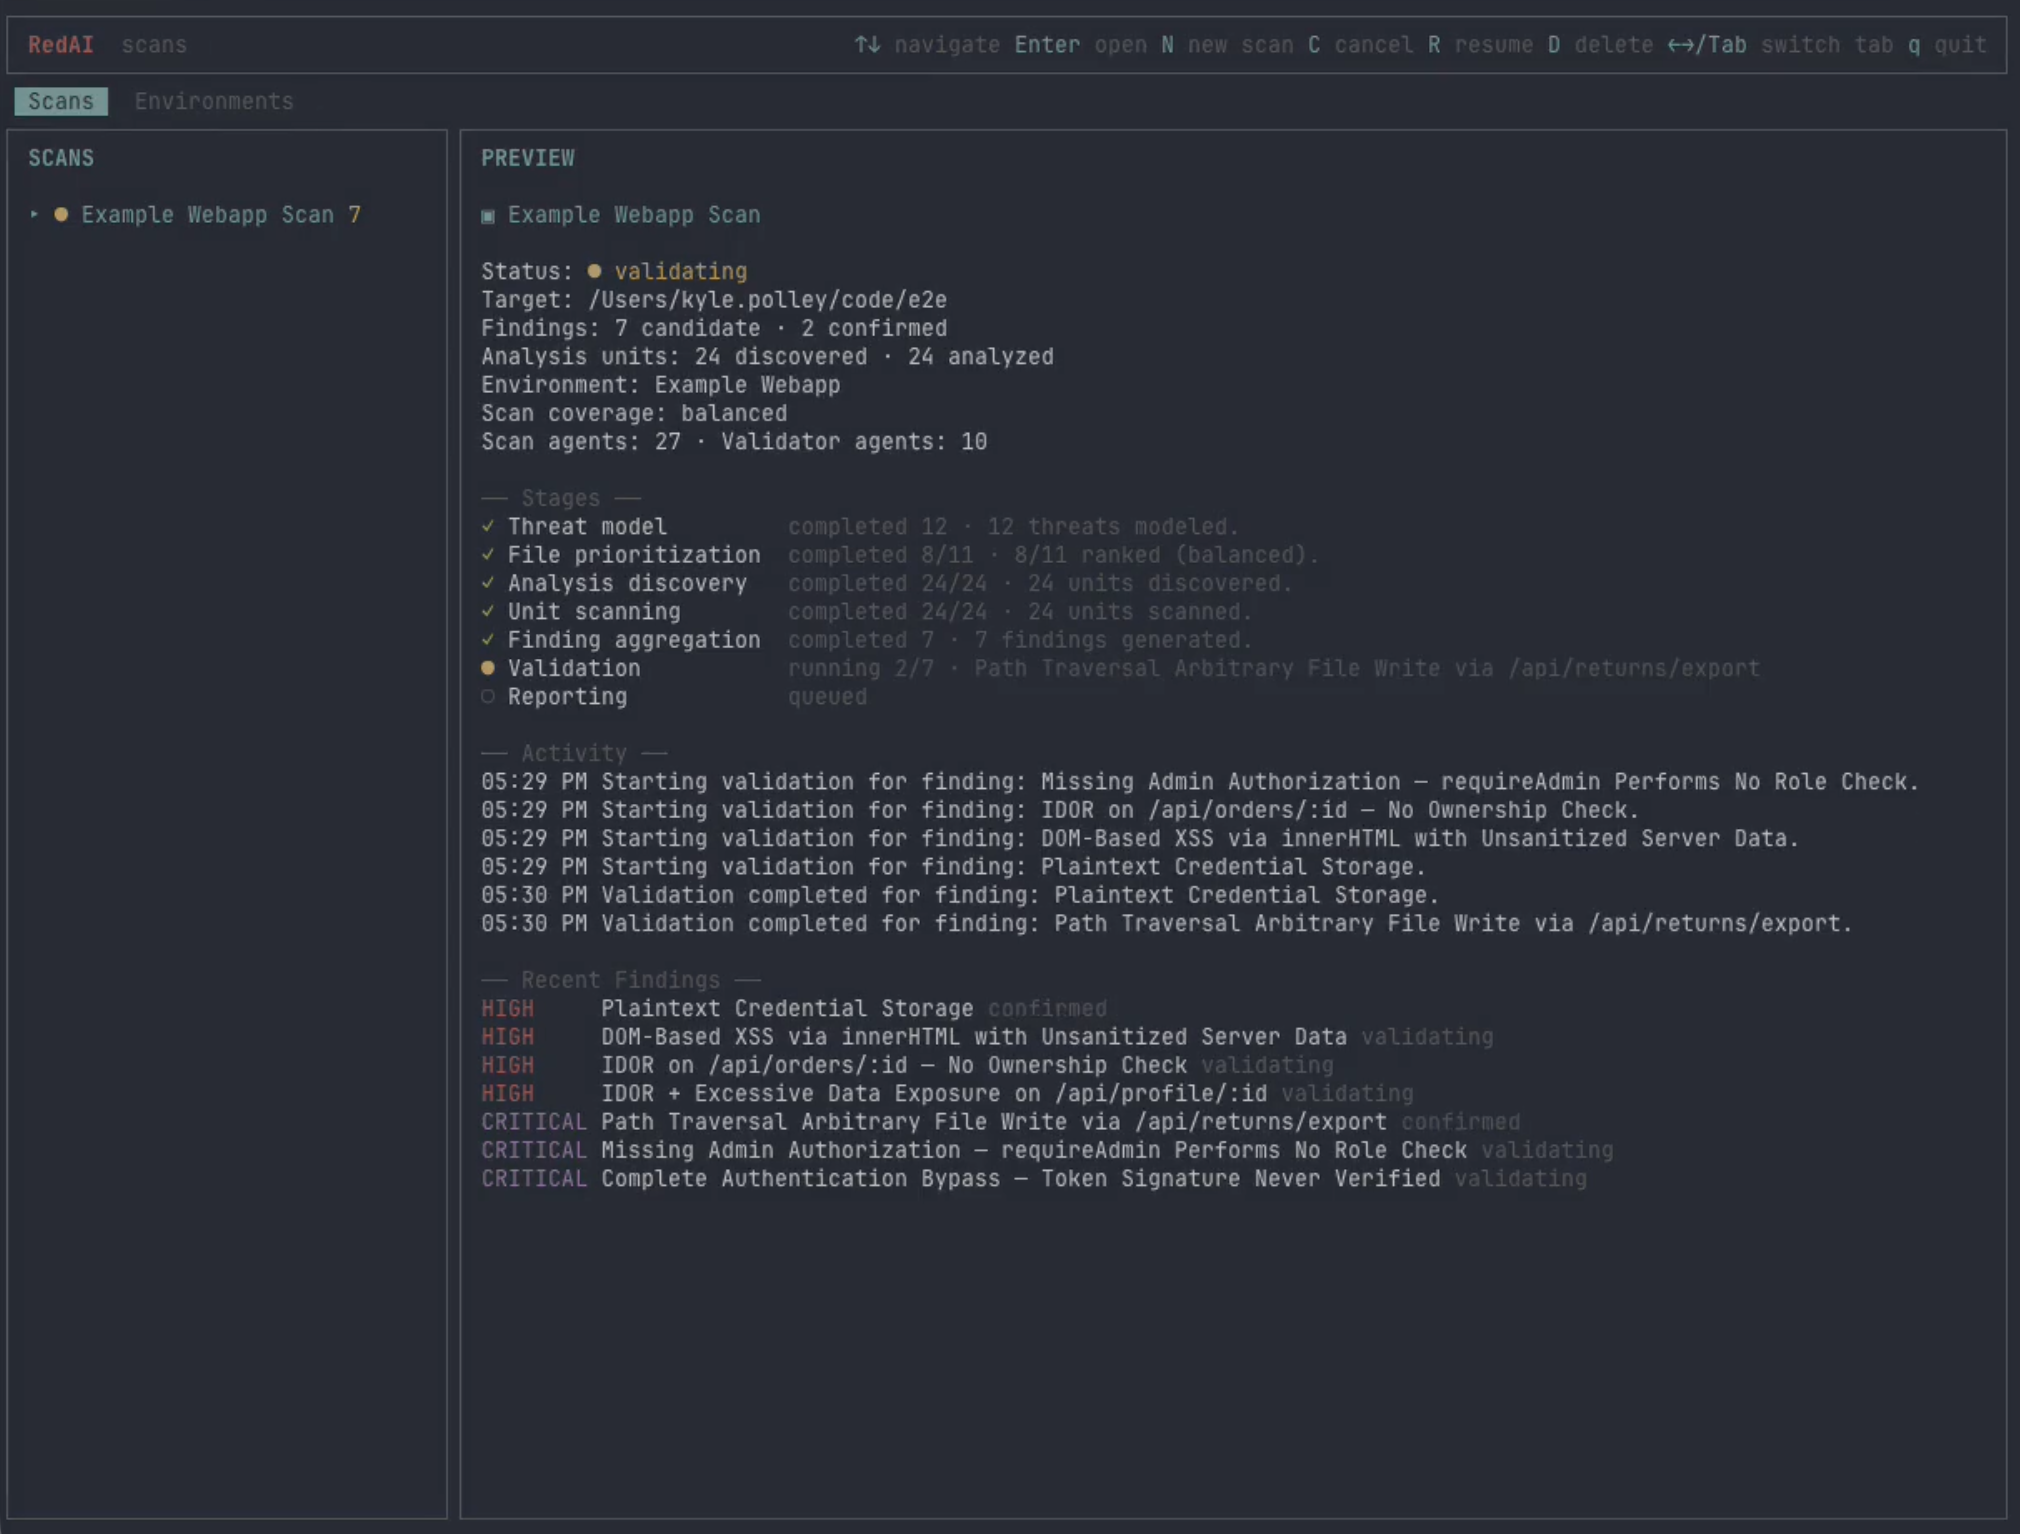 kpolley/redai
AI-driven vulnerability discovery and live validation
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 ikkisoft/bradamsa
Burp Suite extension to generate Intruder payloads using Radamsa
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool