
poc-cve-2025-55182
 koadt/poc-cve-2025-55182
This repository contains a POC of CVE-2025-55182, a critical (CVSS score 10.0) pre-authentication remote code execution vulnerability affecting React…
code-analysisctfdynamic-analysis-sandboxing+7
15
koadt/poc-cve-2025-55182This repository contains a POC of CVE-2025-55182, a critical (CVSS score 10.0) pre-authentication remote code execution vulnerability affecting React…
 captain4554/cve-2025-55182-scanner
🛡️ Scan and assess vulnerabilities in Next.js/Waku with the CVE-2025-55182-Scanner, combining static and dynamic analysis for robust security.
 trixsec/cve-2025-55182-scanner
A hybrid security scanner for detecting CVE-2025-55182 in Next.js and Waku applications. Features combined static code analysis and safe dynamic…
 vesjolyjd/kaspersky_cve-2024-3094
Security review of CVE-2024-3094 (XZ Utils backdoor) including threat modeling, static/dynamic code analysis, fuzzing with AFL++, and a…
 shoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1
Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…
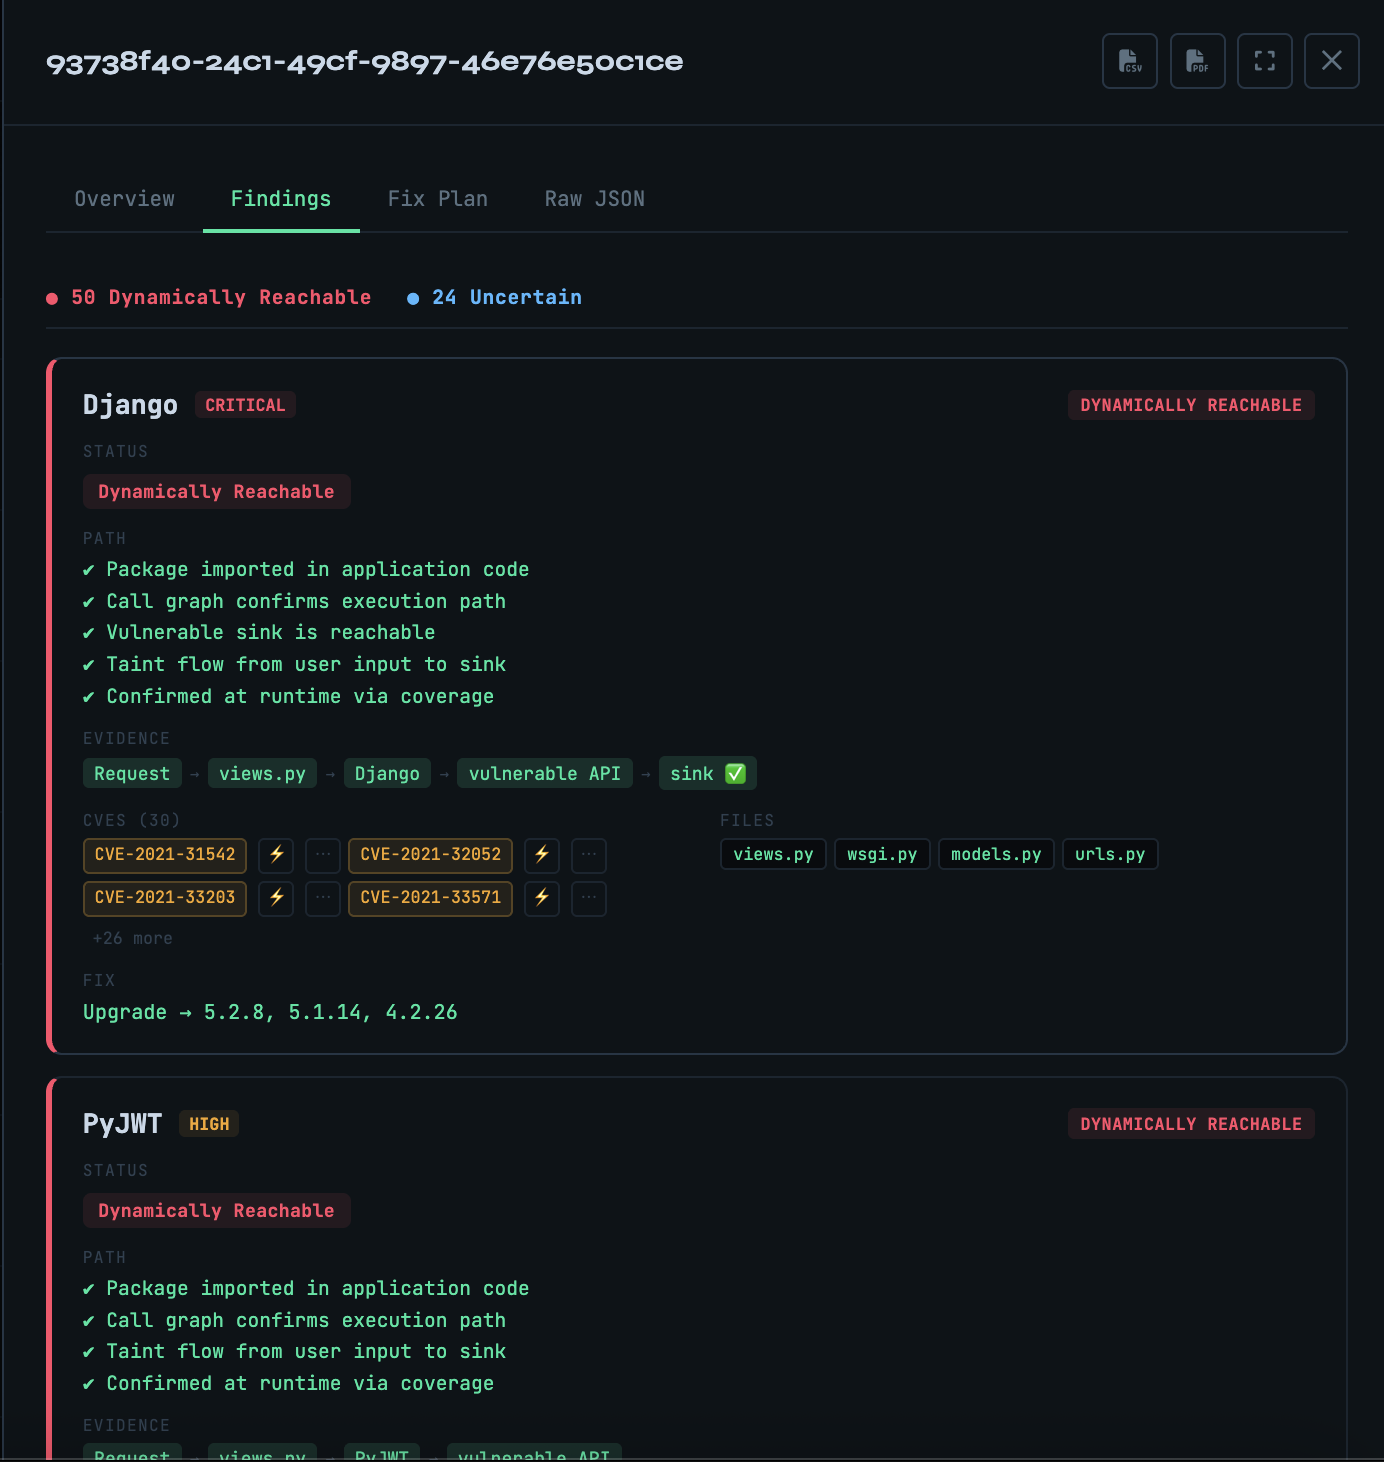 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
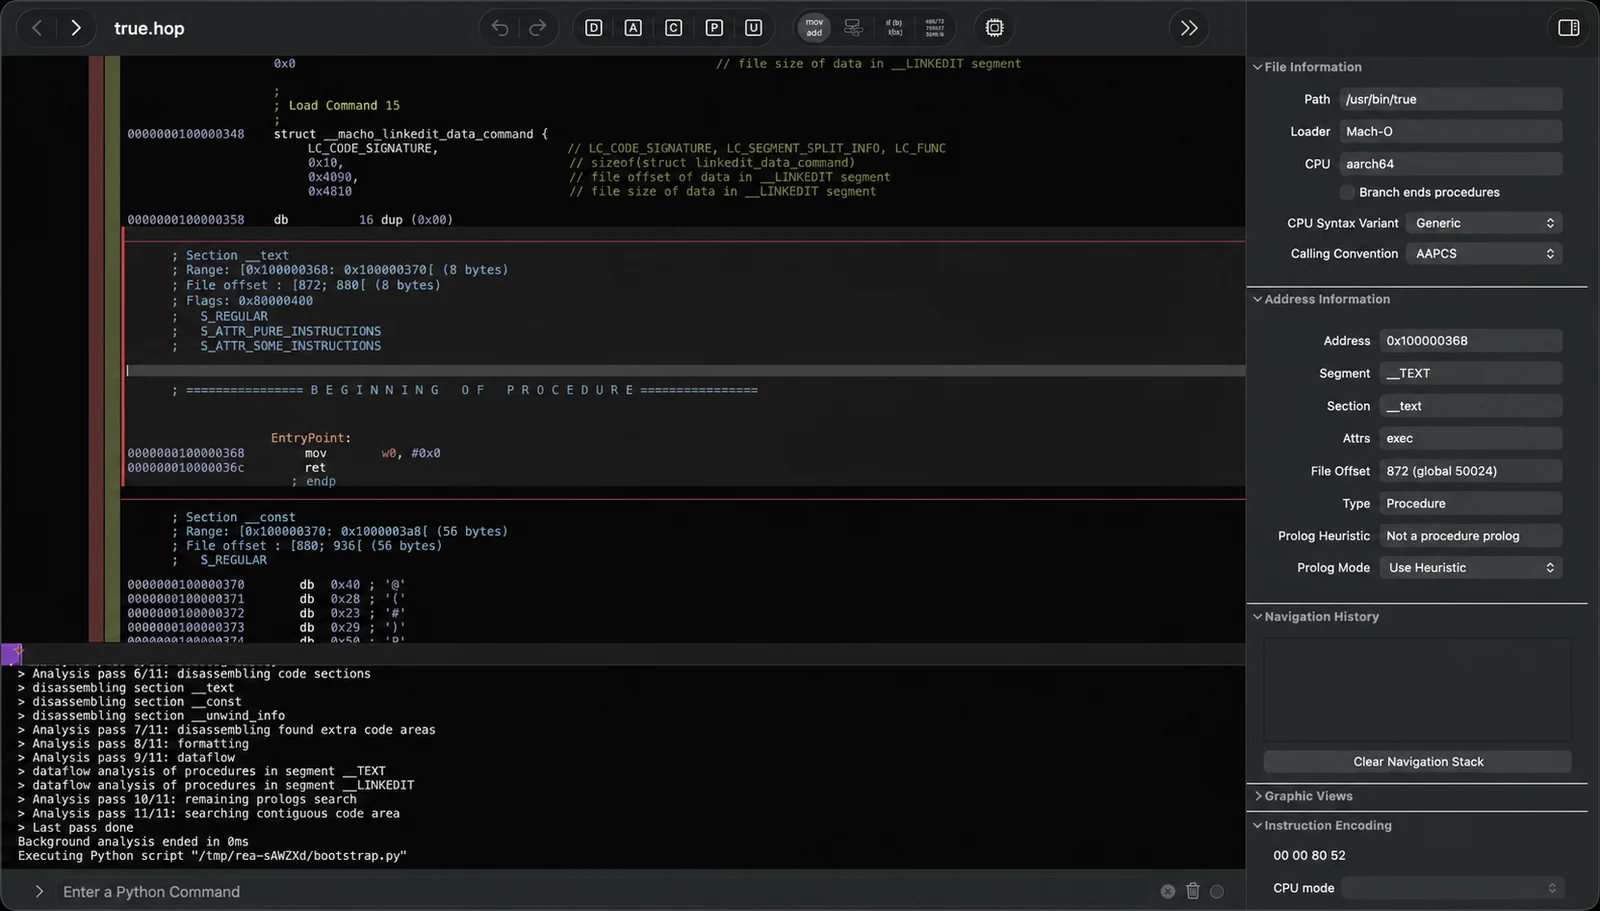 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
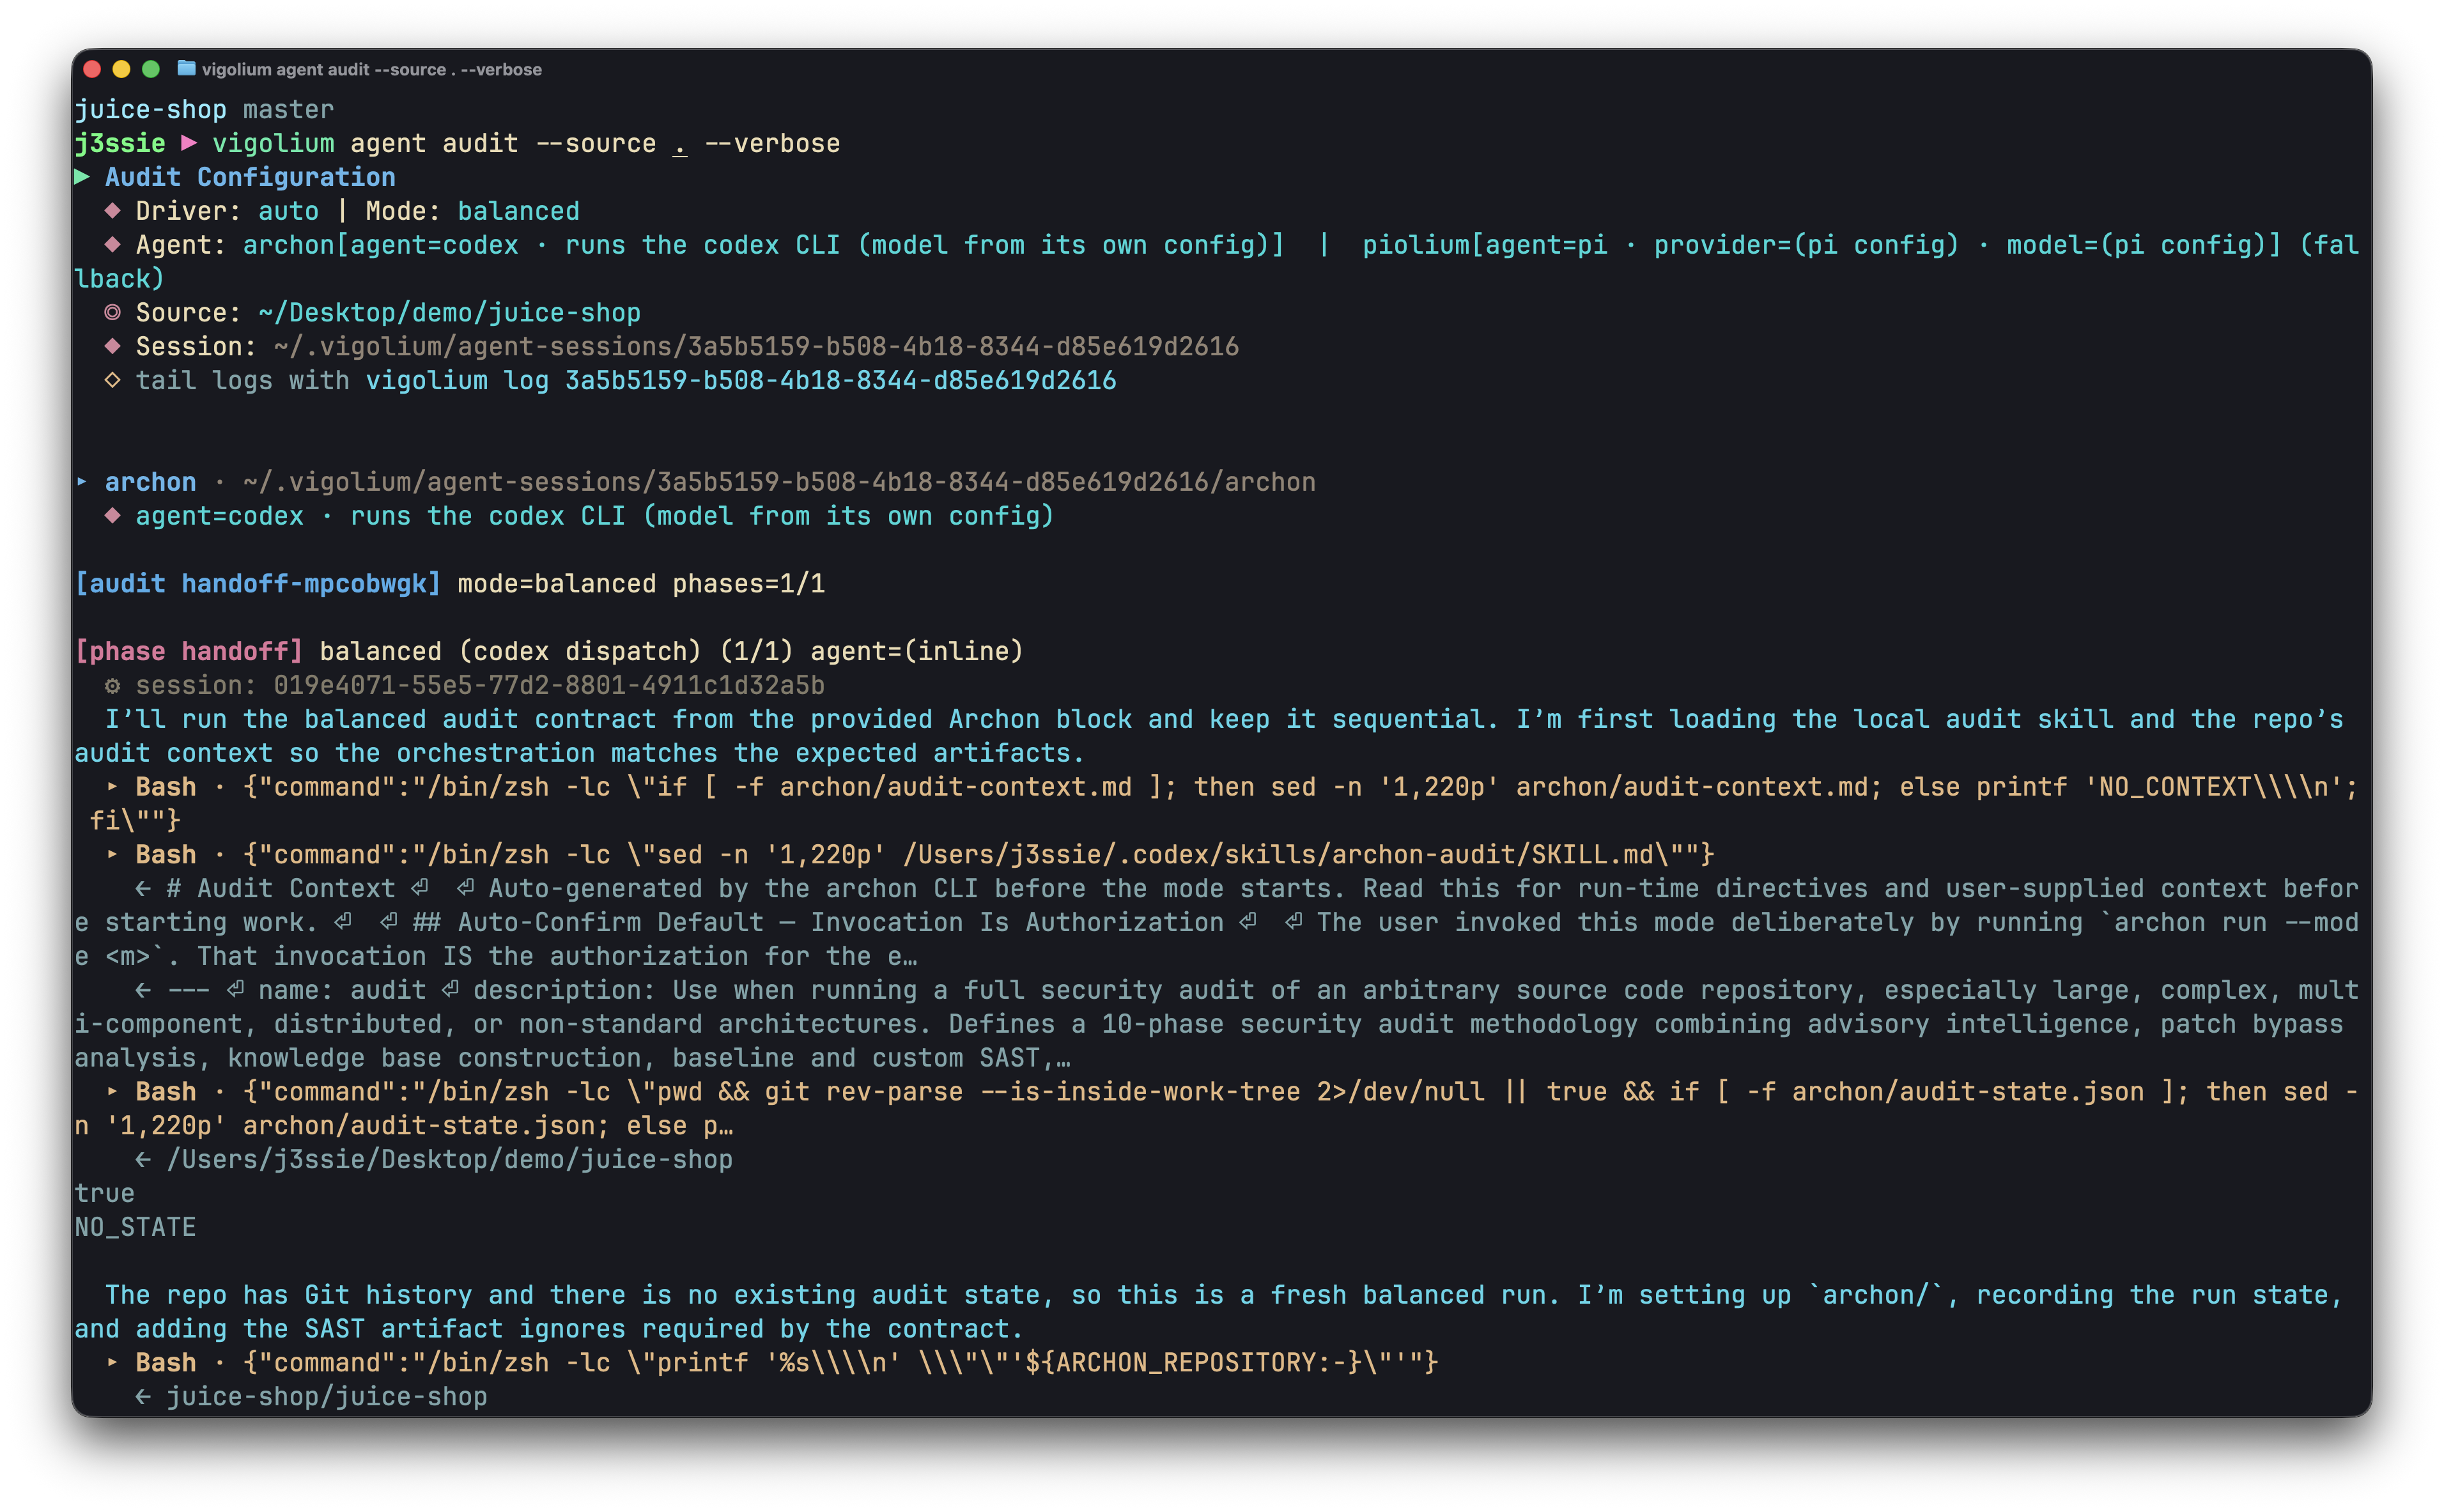 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…