

frida
 frida/frida
Main repo for hosting release binaries
android-securitybinary-analysiscode-analysis+9
frida/fridaMain repo for hosting release binaries
 structio-labs/n0xis
Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…
 androguard/androguard
Reverse engineering and pentesting for Android applications
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
 neurosaki987/qvm-tool
Static analysis and structure recovery toolkit for ACE .qvm0-protected PE images
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
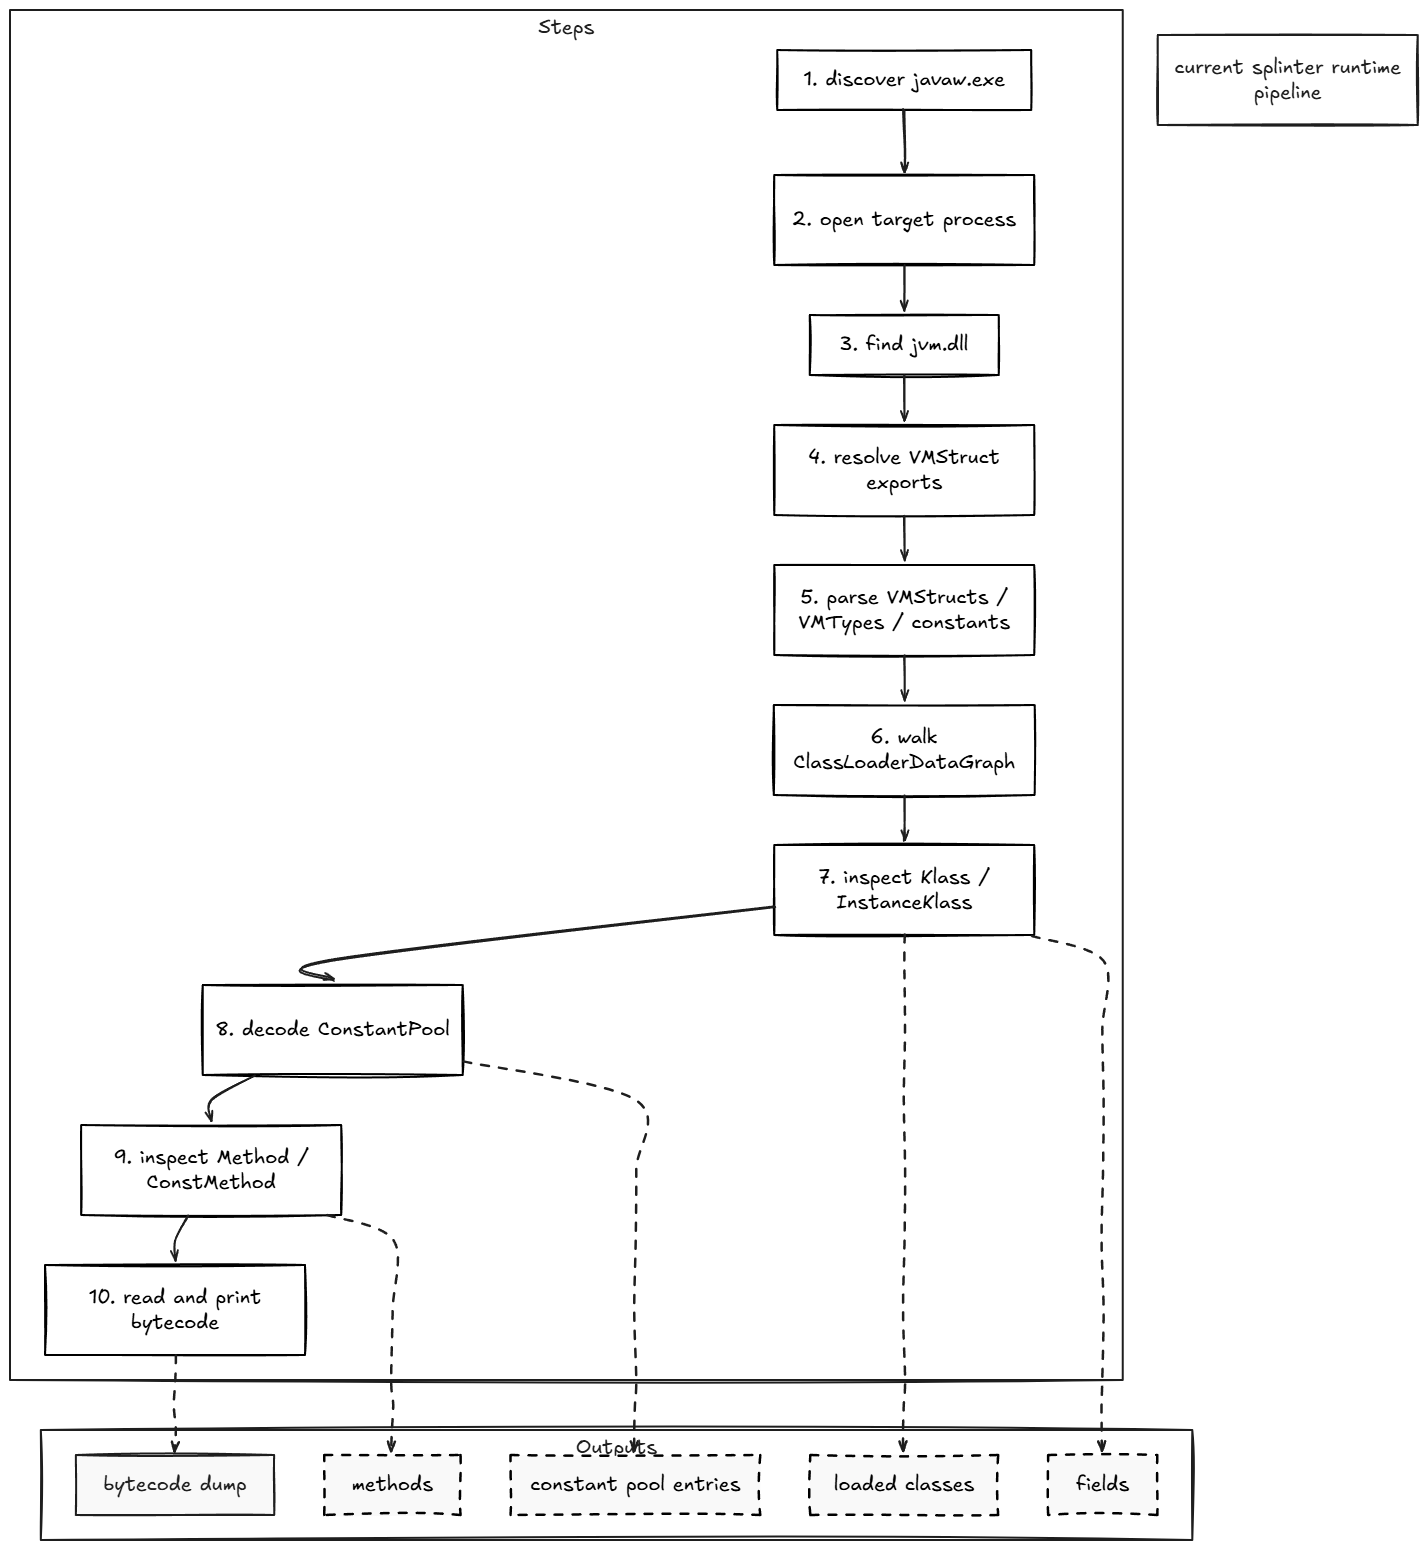 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
 b9ph0met/px-vm
Reverse engineering toolkit for PerimeterX's bytecode VM, featuring a CFG-based disassembler, 5-layer decryption pipeline, opcode table…
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit