recurse
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
ai-assisted-reversingai-securitybinary-analysis+7
214
recurse-labs/recurseAgentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
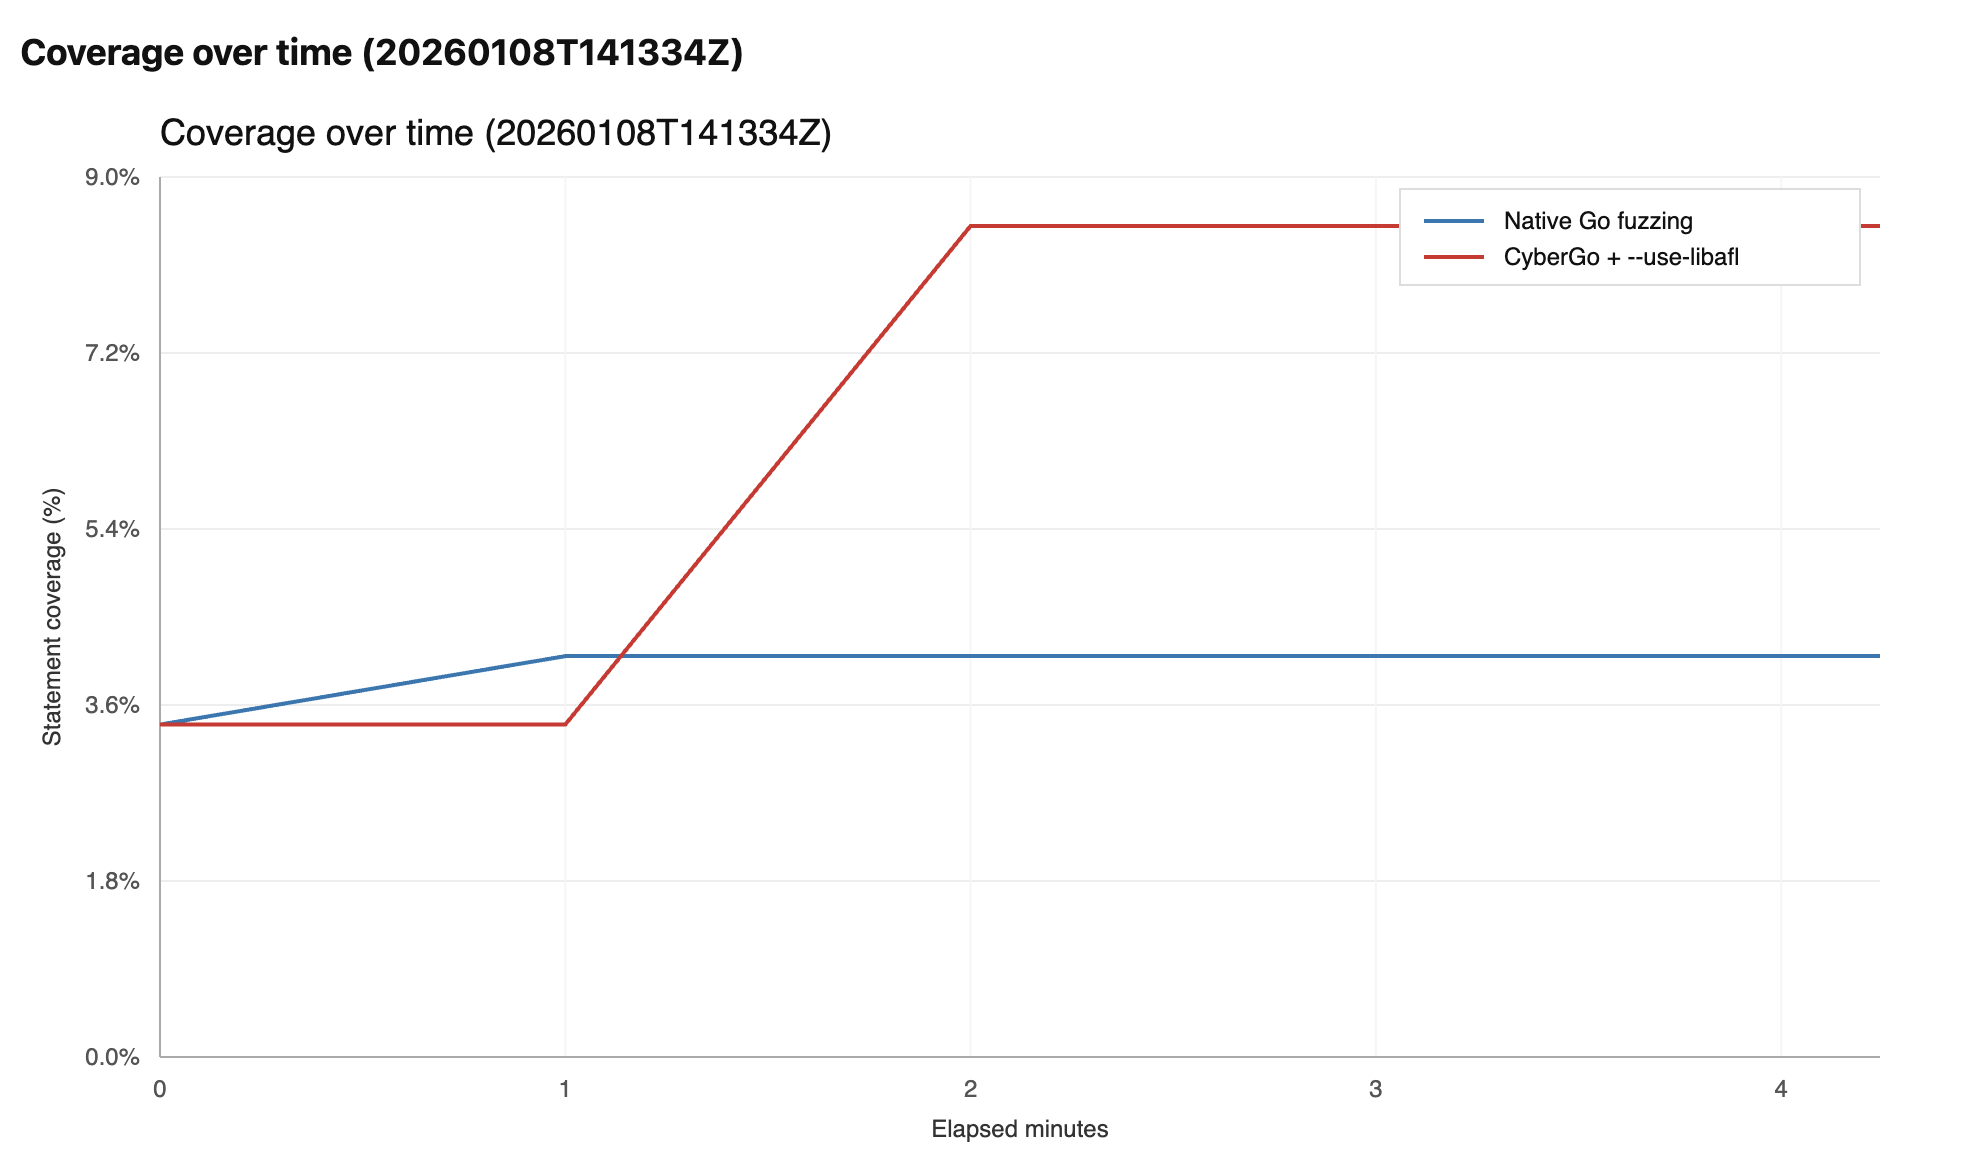 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
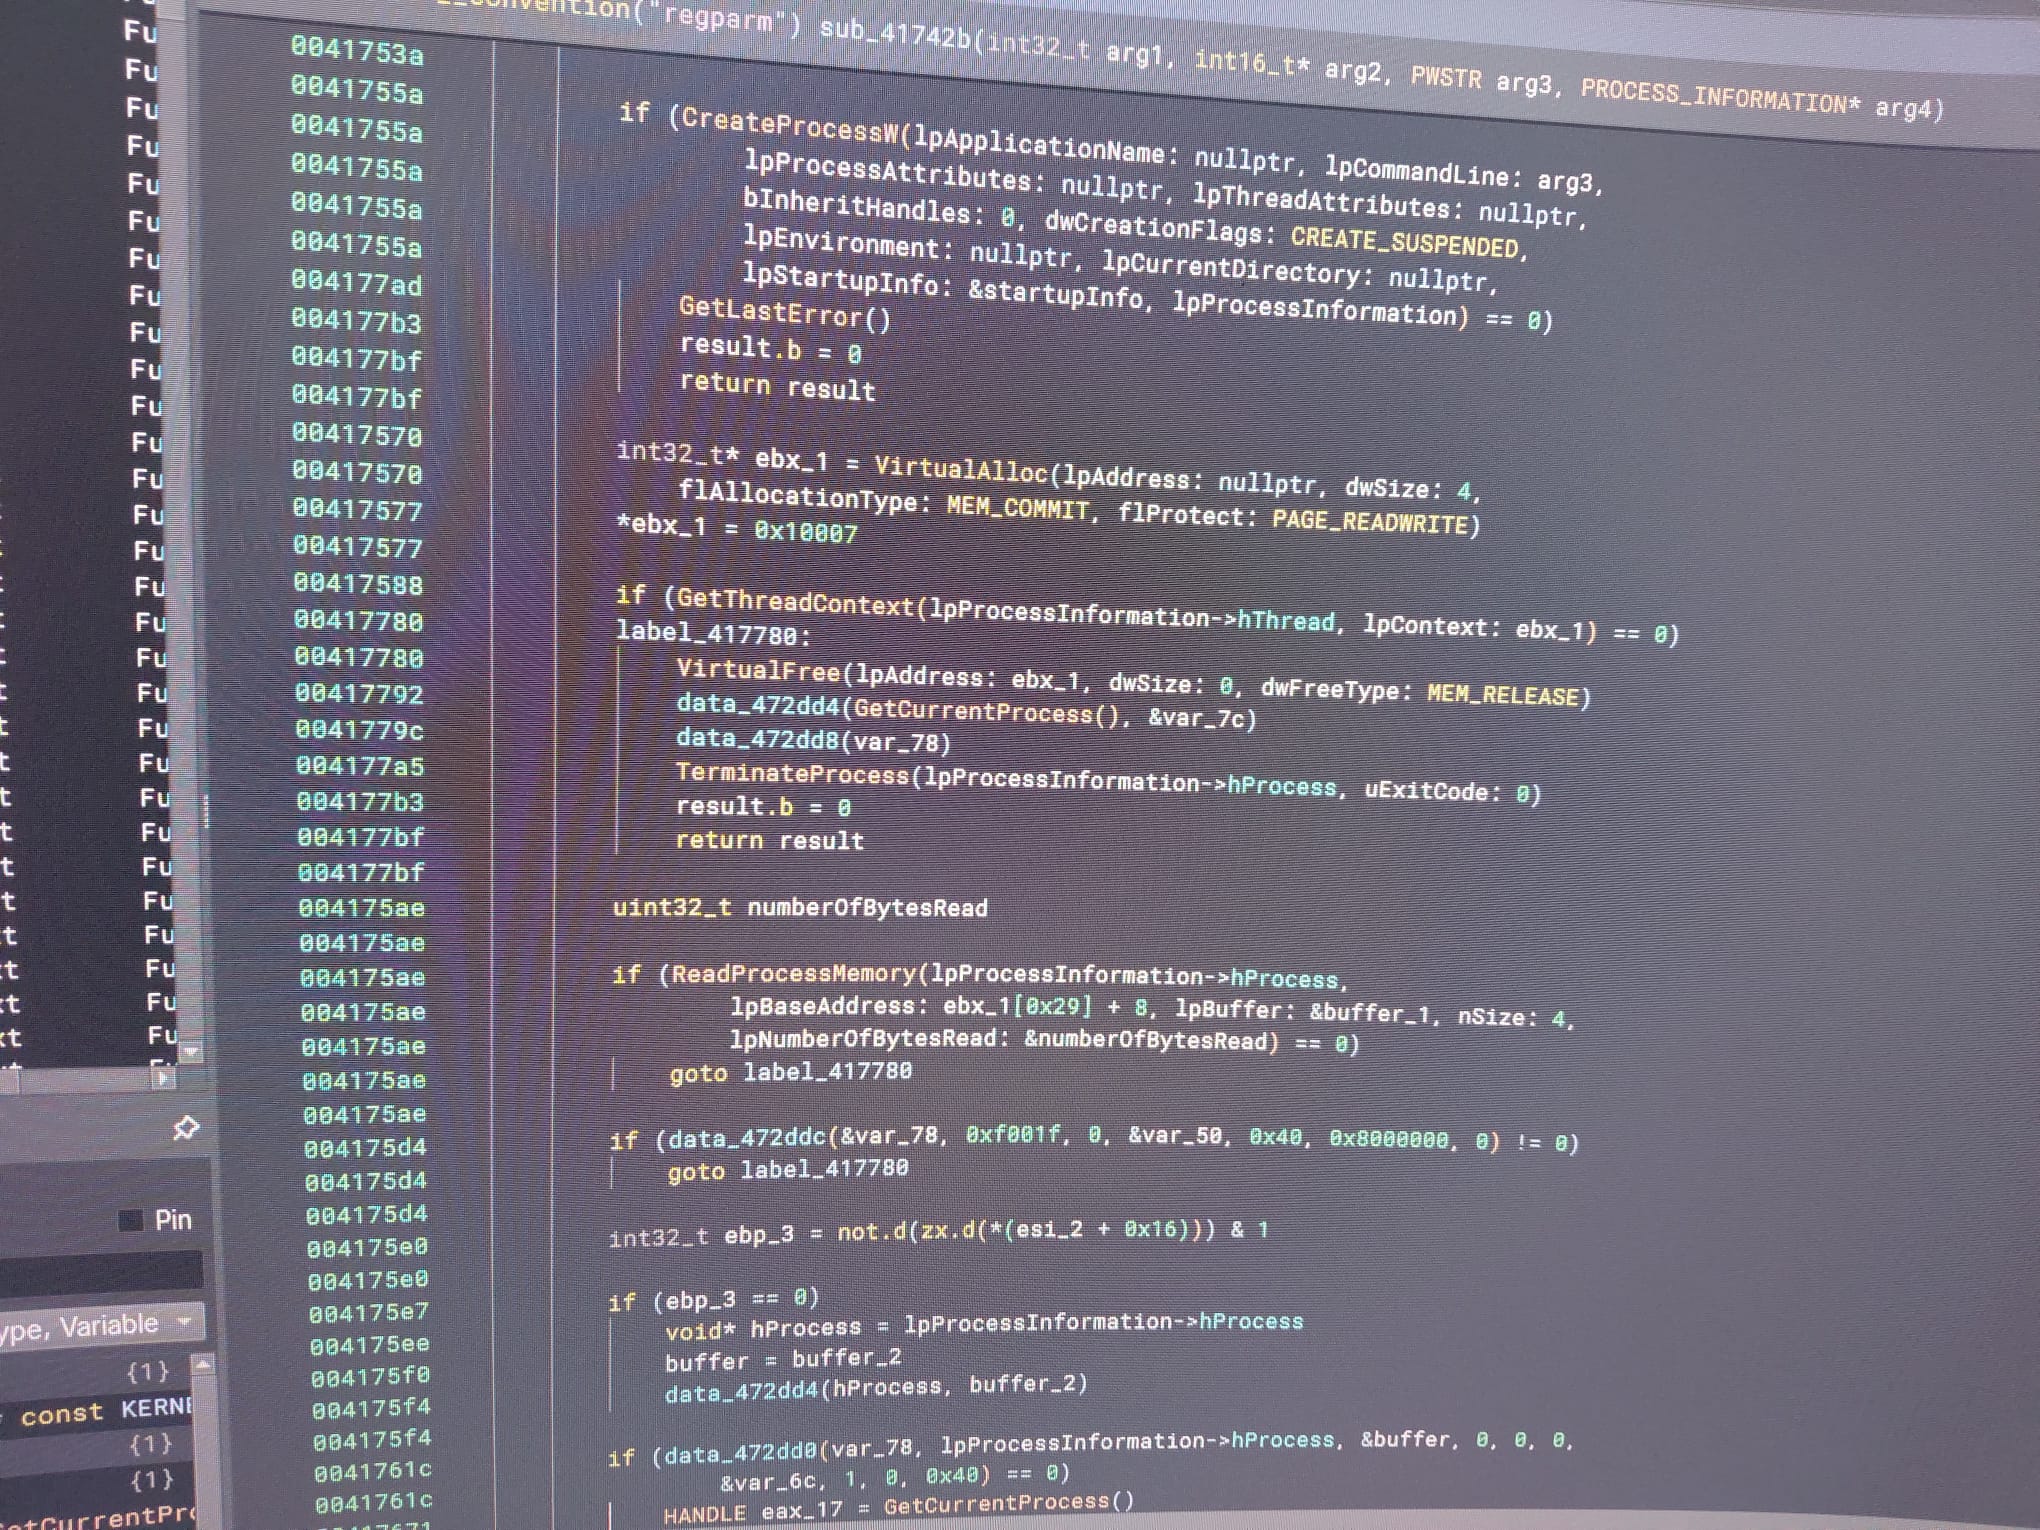 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
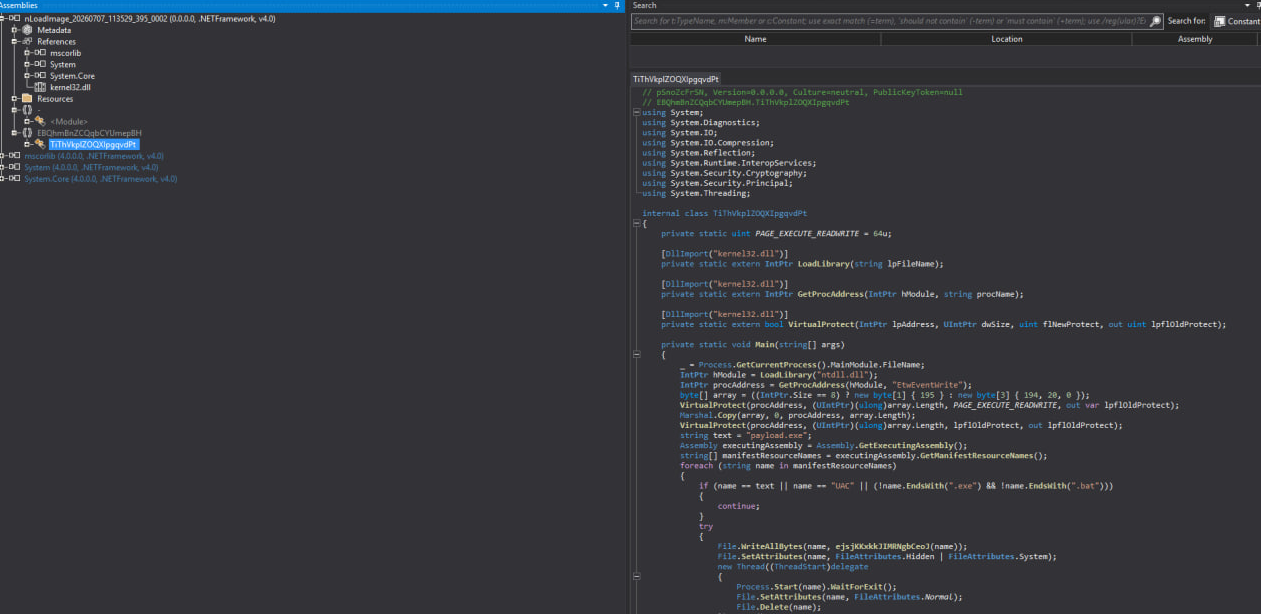 zypherion-technologies/nemesis
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 t0thkr1s/frida
Frida scripts for mobile application dynamic-analysis.
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…