

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.6k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 e-m-b-a/emba
EMBA - The firmware security analyzer
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…
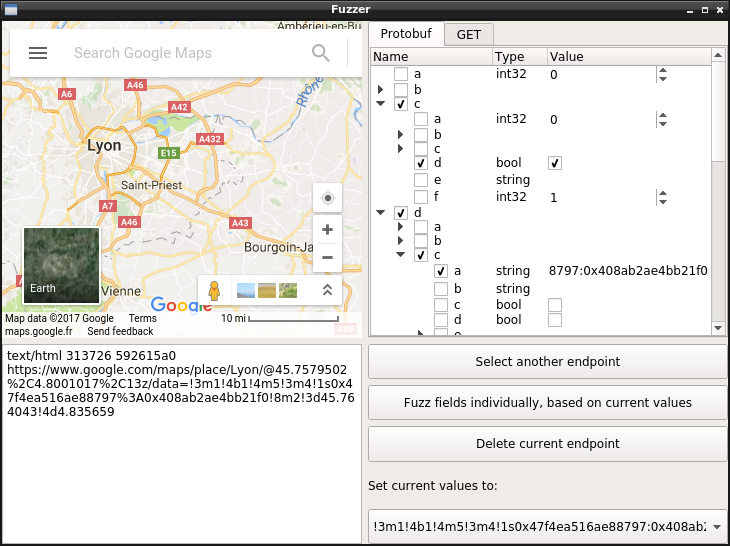 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 frida/frida
Main repo for hosting release binaries
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
 ashishb/android-security-awesome
A collection of android security related resources
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 nowsecure/r2frida
Radare2 and Frida better together.
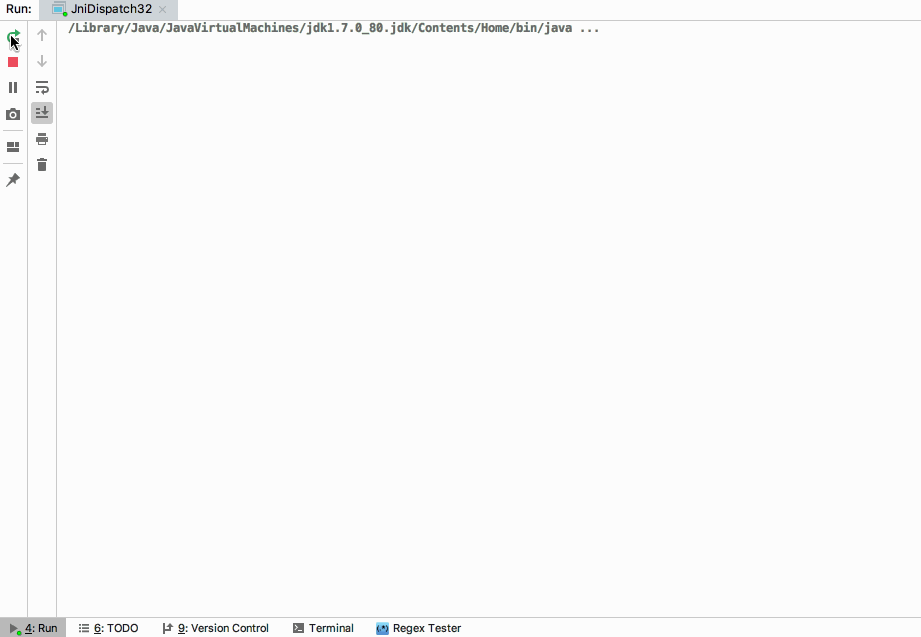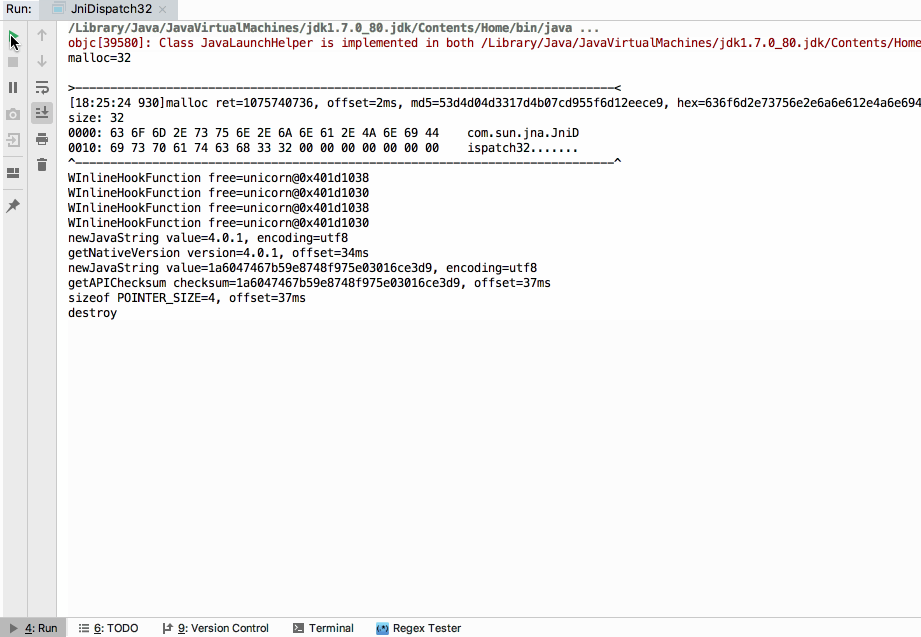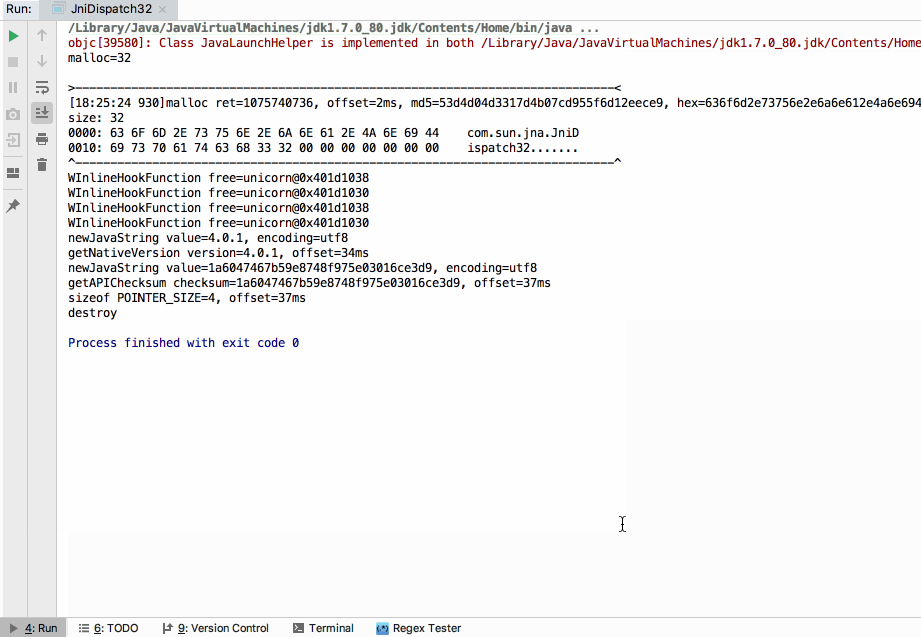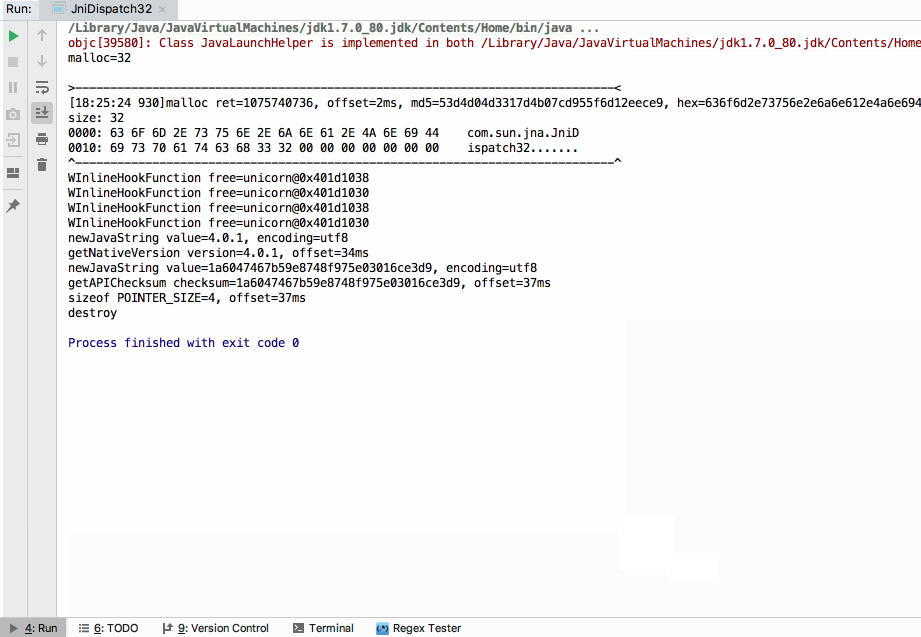 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
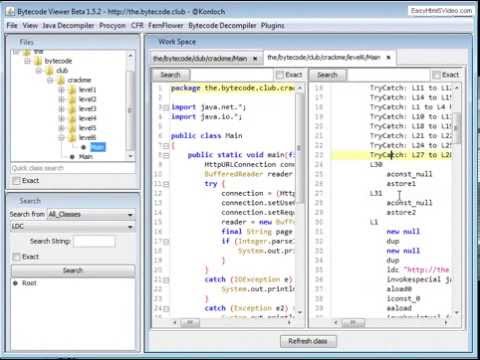 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)