
CVE-2026-32945
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
binary-analysisdynamic-analysis-sandboxingexploitation+2
johanneslks/cve-2026-32945PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
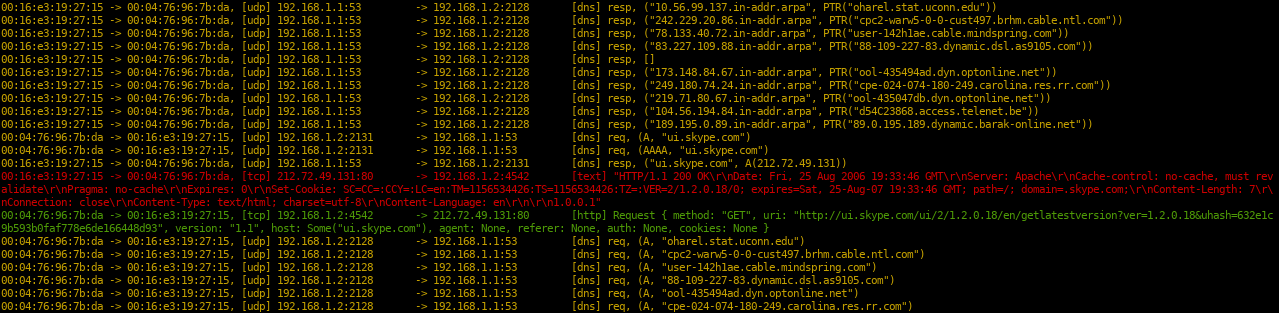 kpcyrd/sniffglue
Secure multithreaded packet sniffer
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
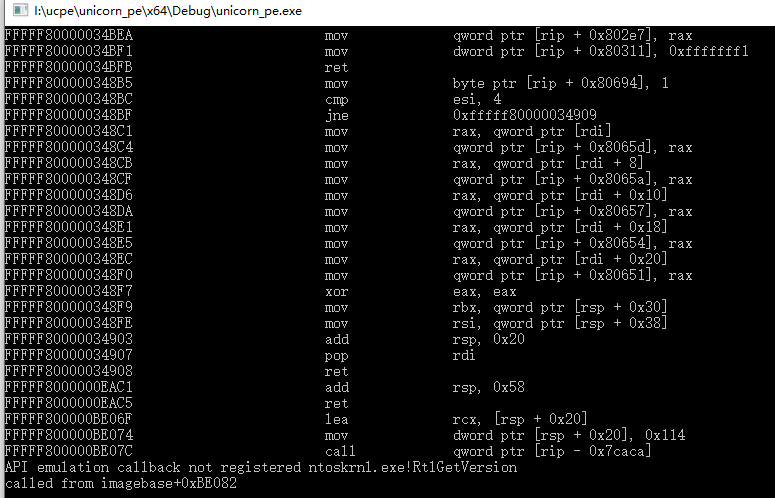 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.