
seclab-taskflows-fuzzing
 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
ai-securitycode-analysisdynamic-analysis-sandboxing+7
22
githubsecuritylab/seclab-taskflows-fuzzingAn LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 slyd0g/dylibhijacktest
Discover DYLD_INSERT_LIBRARIES hijacks on macOS
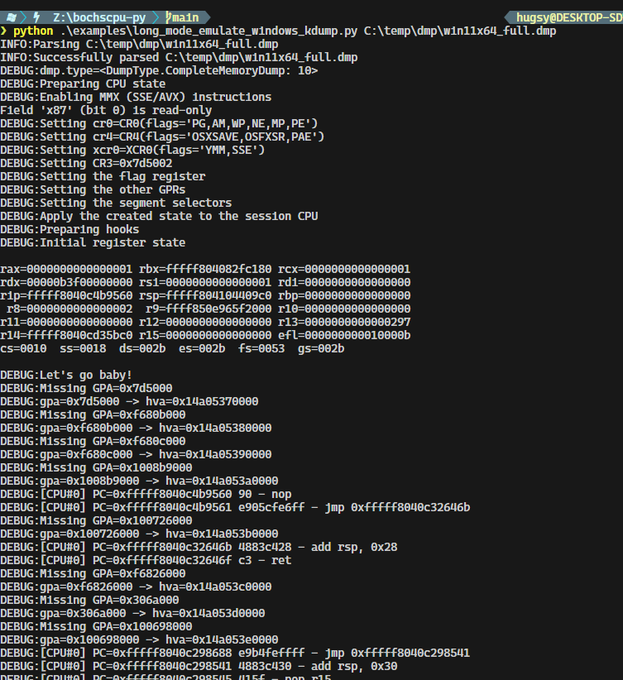 hugsy/bochscpu-python
Python bindings for BochsCPU
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava
 shcesama/cve-2023-4863-analysis
Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…