
mxc
 microsoft/mxc
Policy-driven, layered isolation and containment
cloud-infrastructure-securityconfiguration-auditingcontainer-security+3
1.3k
microsoft/mxcPolicy-driven, layered isolation and containment
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 borealisai/stepjack
Benchmarking framework for evaluating computer-use AI agents against multi-step indirect prompt injection, with automatic adversarial goal…
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 0x48piraj/incarcero
Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
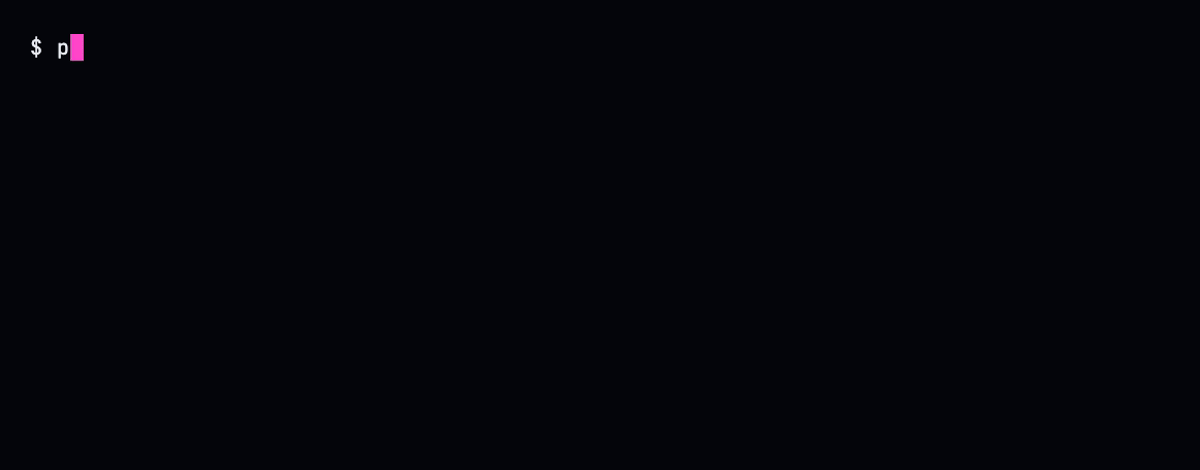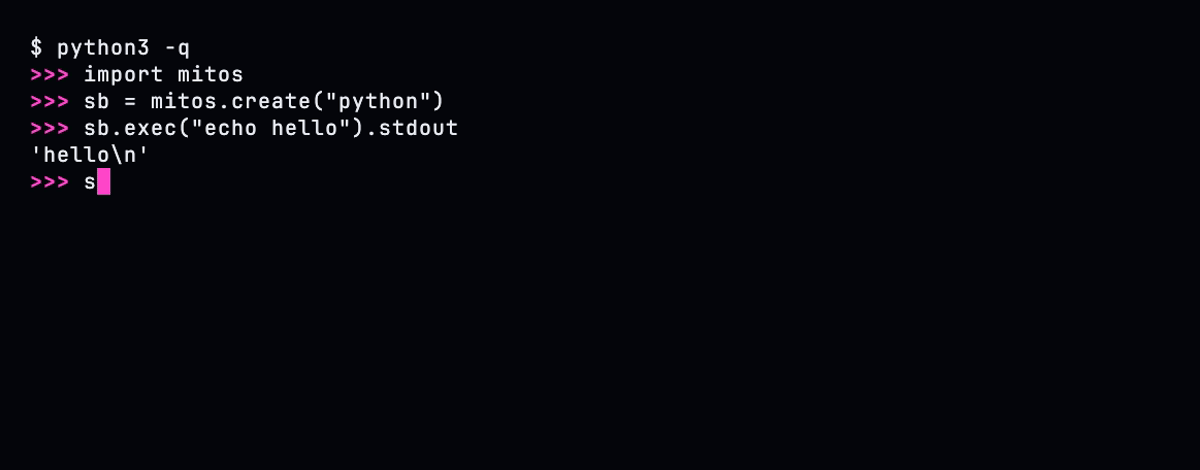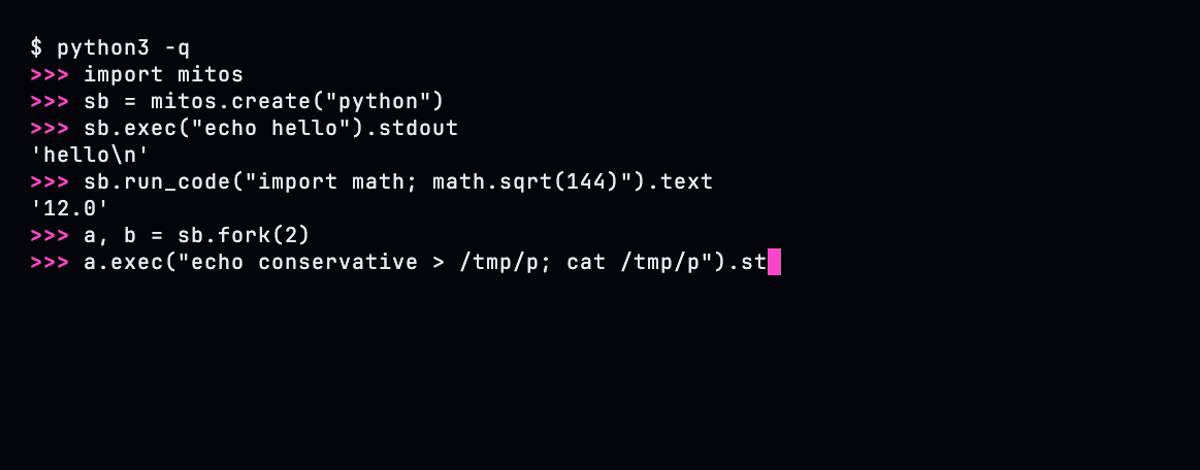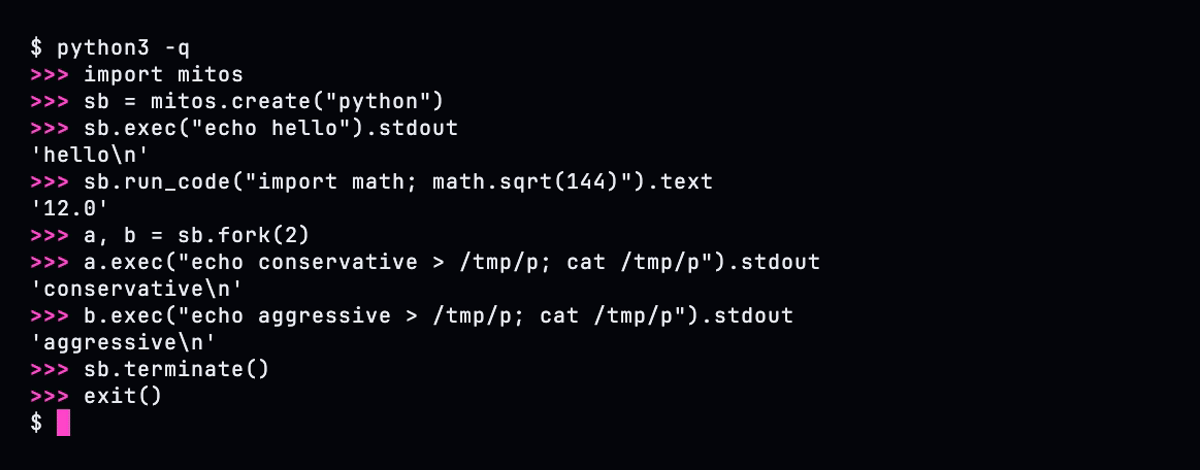 mitos-run/mitos
Millisecond microVM sandbox forking for AI agents on Kubernetes. Firecracker VMs that restore from memory snapshots in milliseconds, fork a running…
 pwnfunction/sandbox
Run untrusted AI code safely, fast
 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 calusdotai/anticipator
Anticipator is an open-source threat detection platform for multi-agent AI systems.
 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking