
test-fuzz
 trailofbits/test-fuzz
Rust macros and Cargo subcommand to automate fuzzing with afl.rs, including corpus generation and harness implementation, integrated with Rust's…
code-analysisdynamic-analysis-sandboxingfuzzing+1
208
trailofbits/test-fuzzRust macros and Cargo subcommand to automate fuzzing with afl.rs, including corpus generation and harness implementation, integrated with Rust's…
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
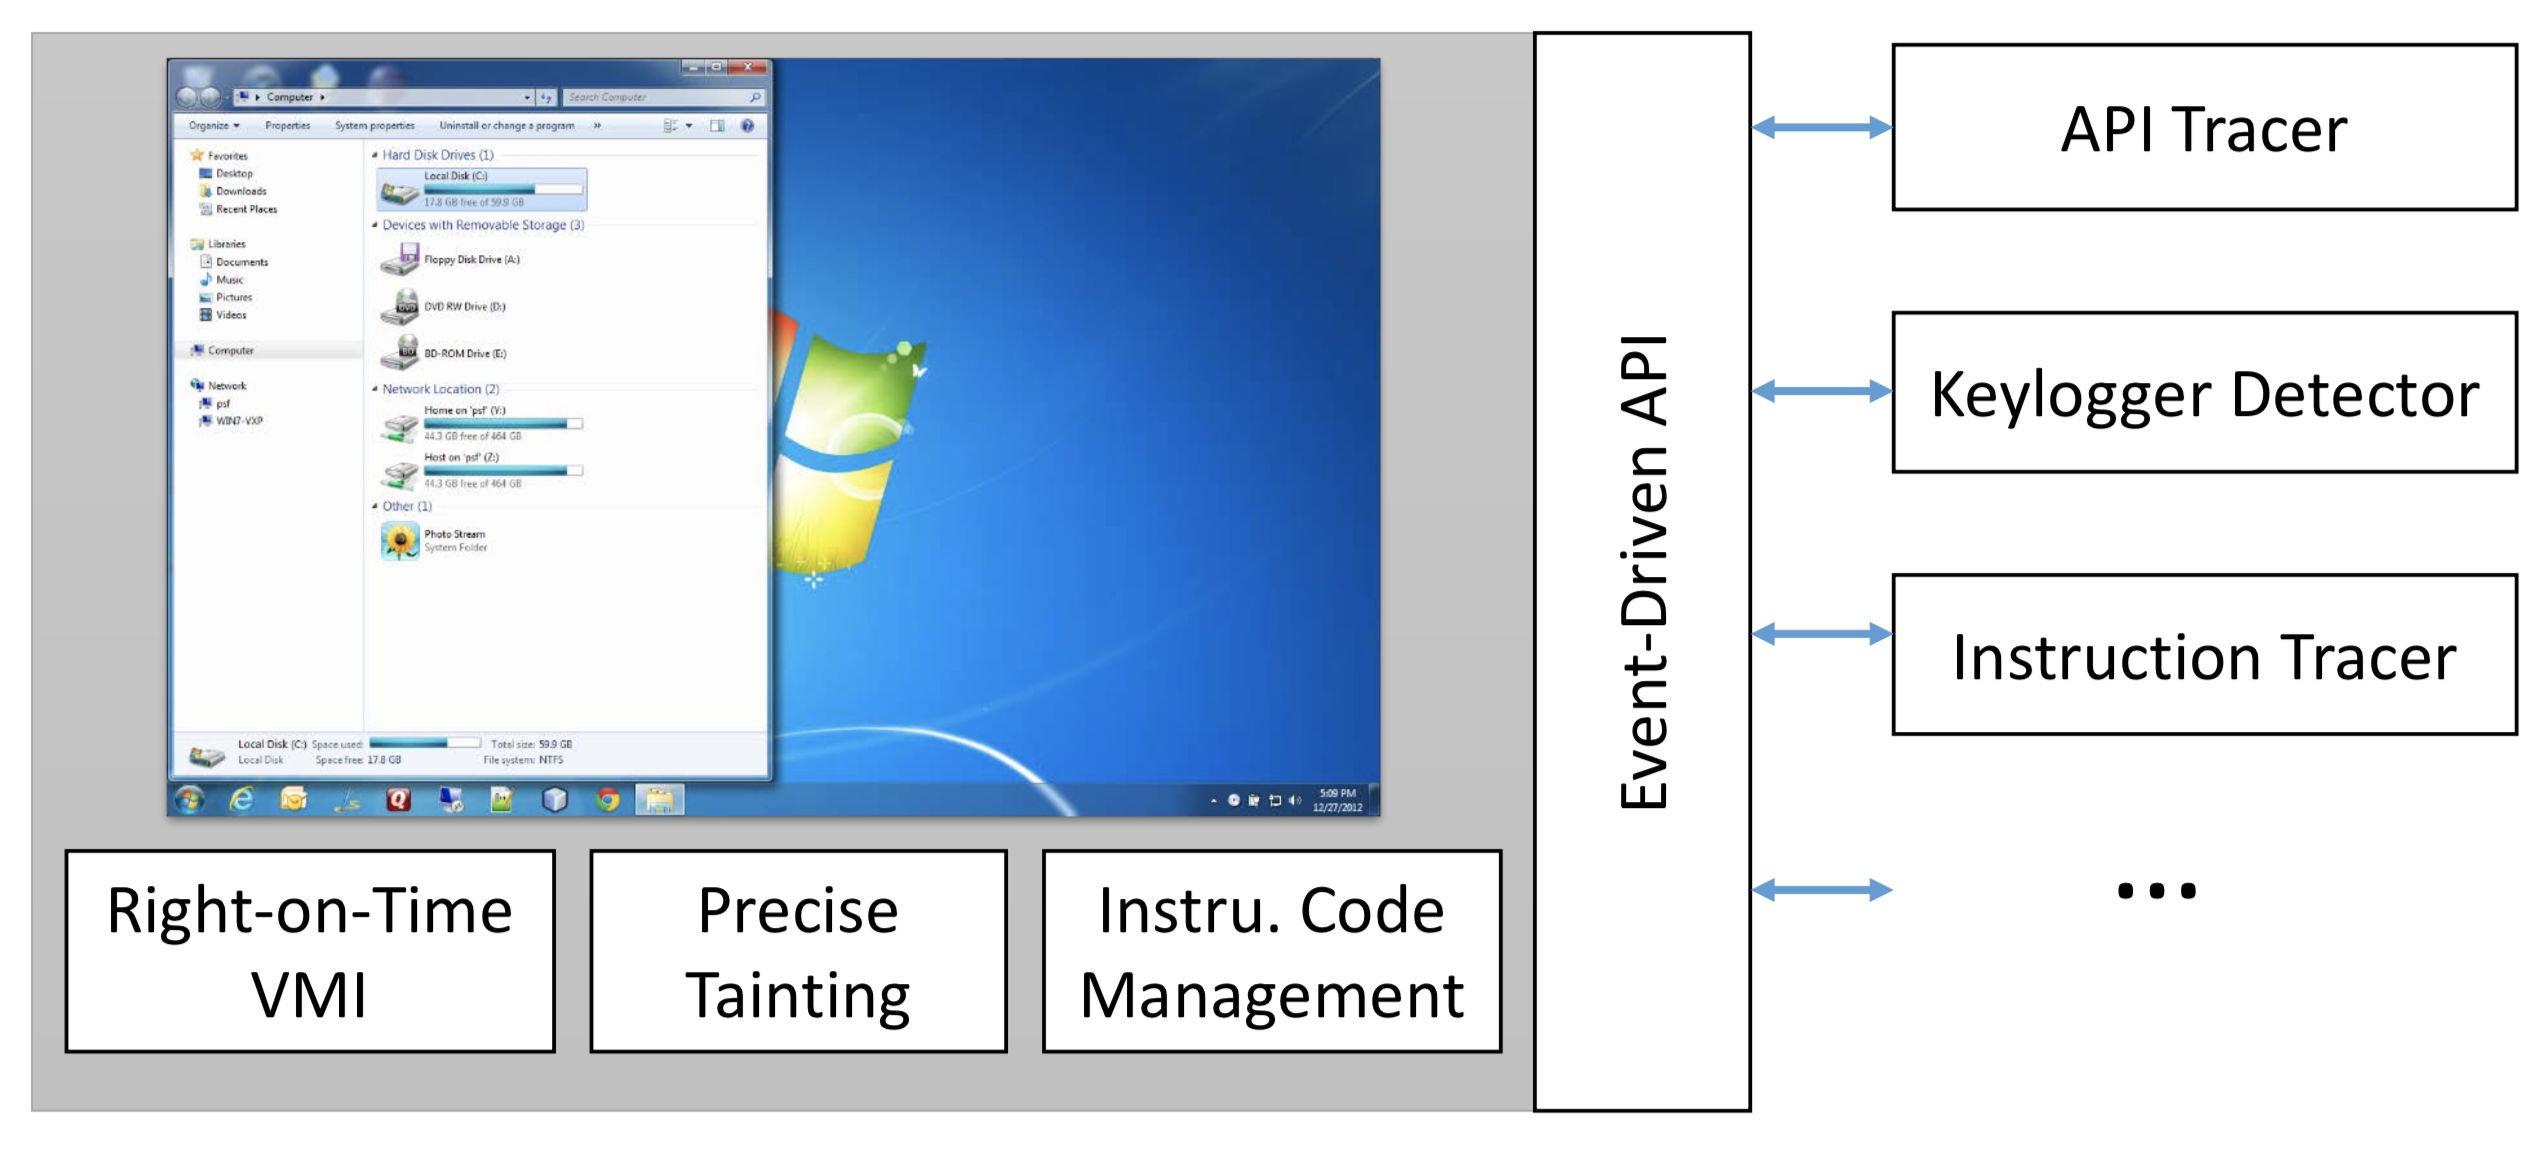 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
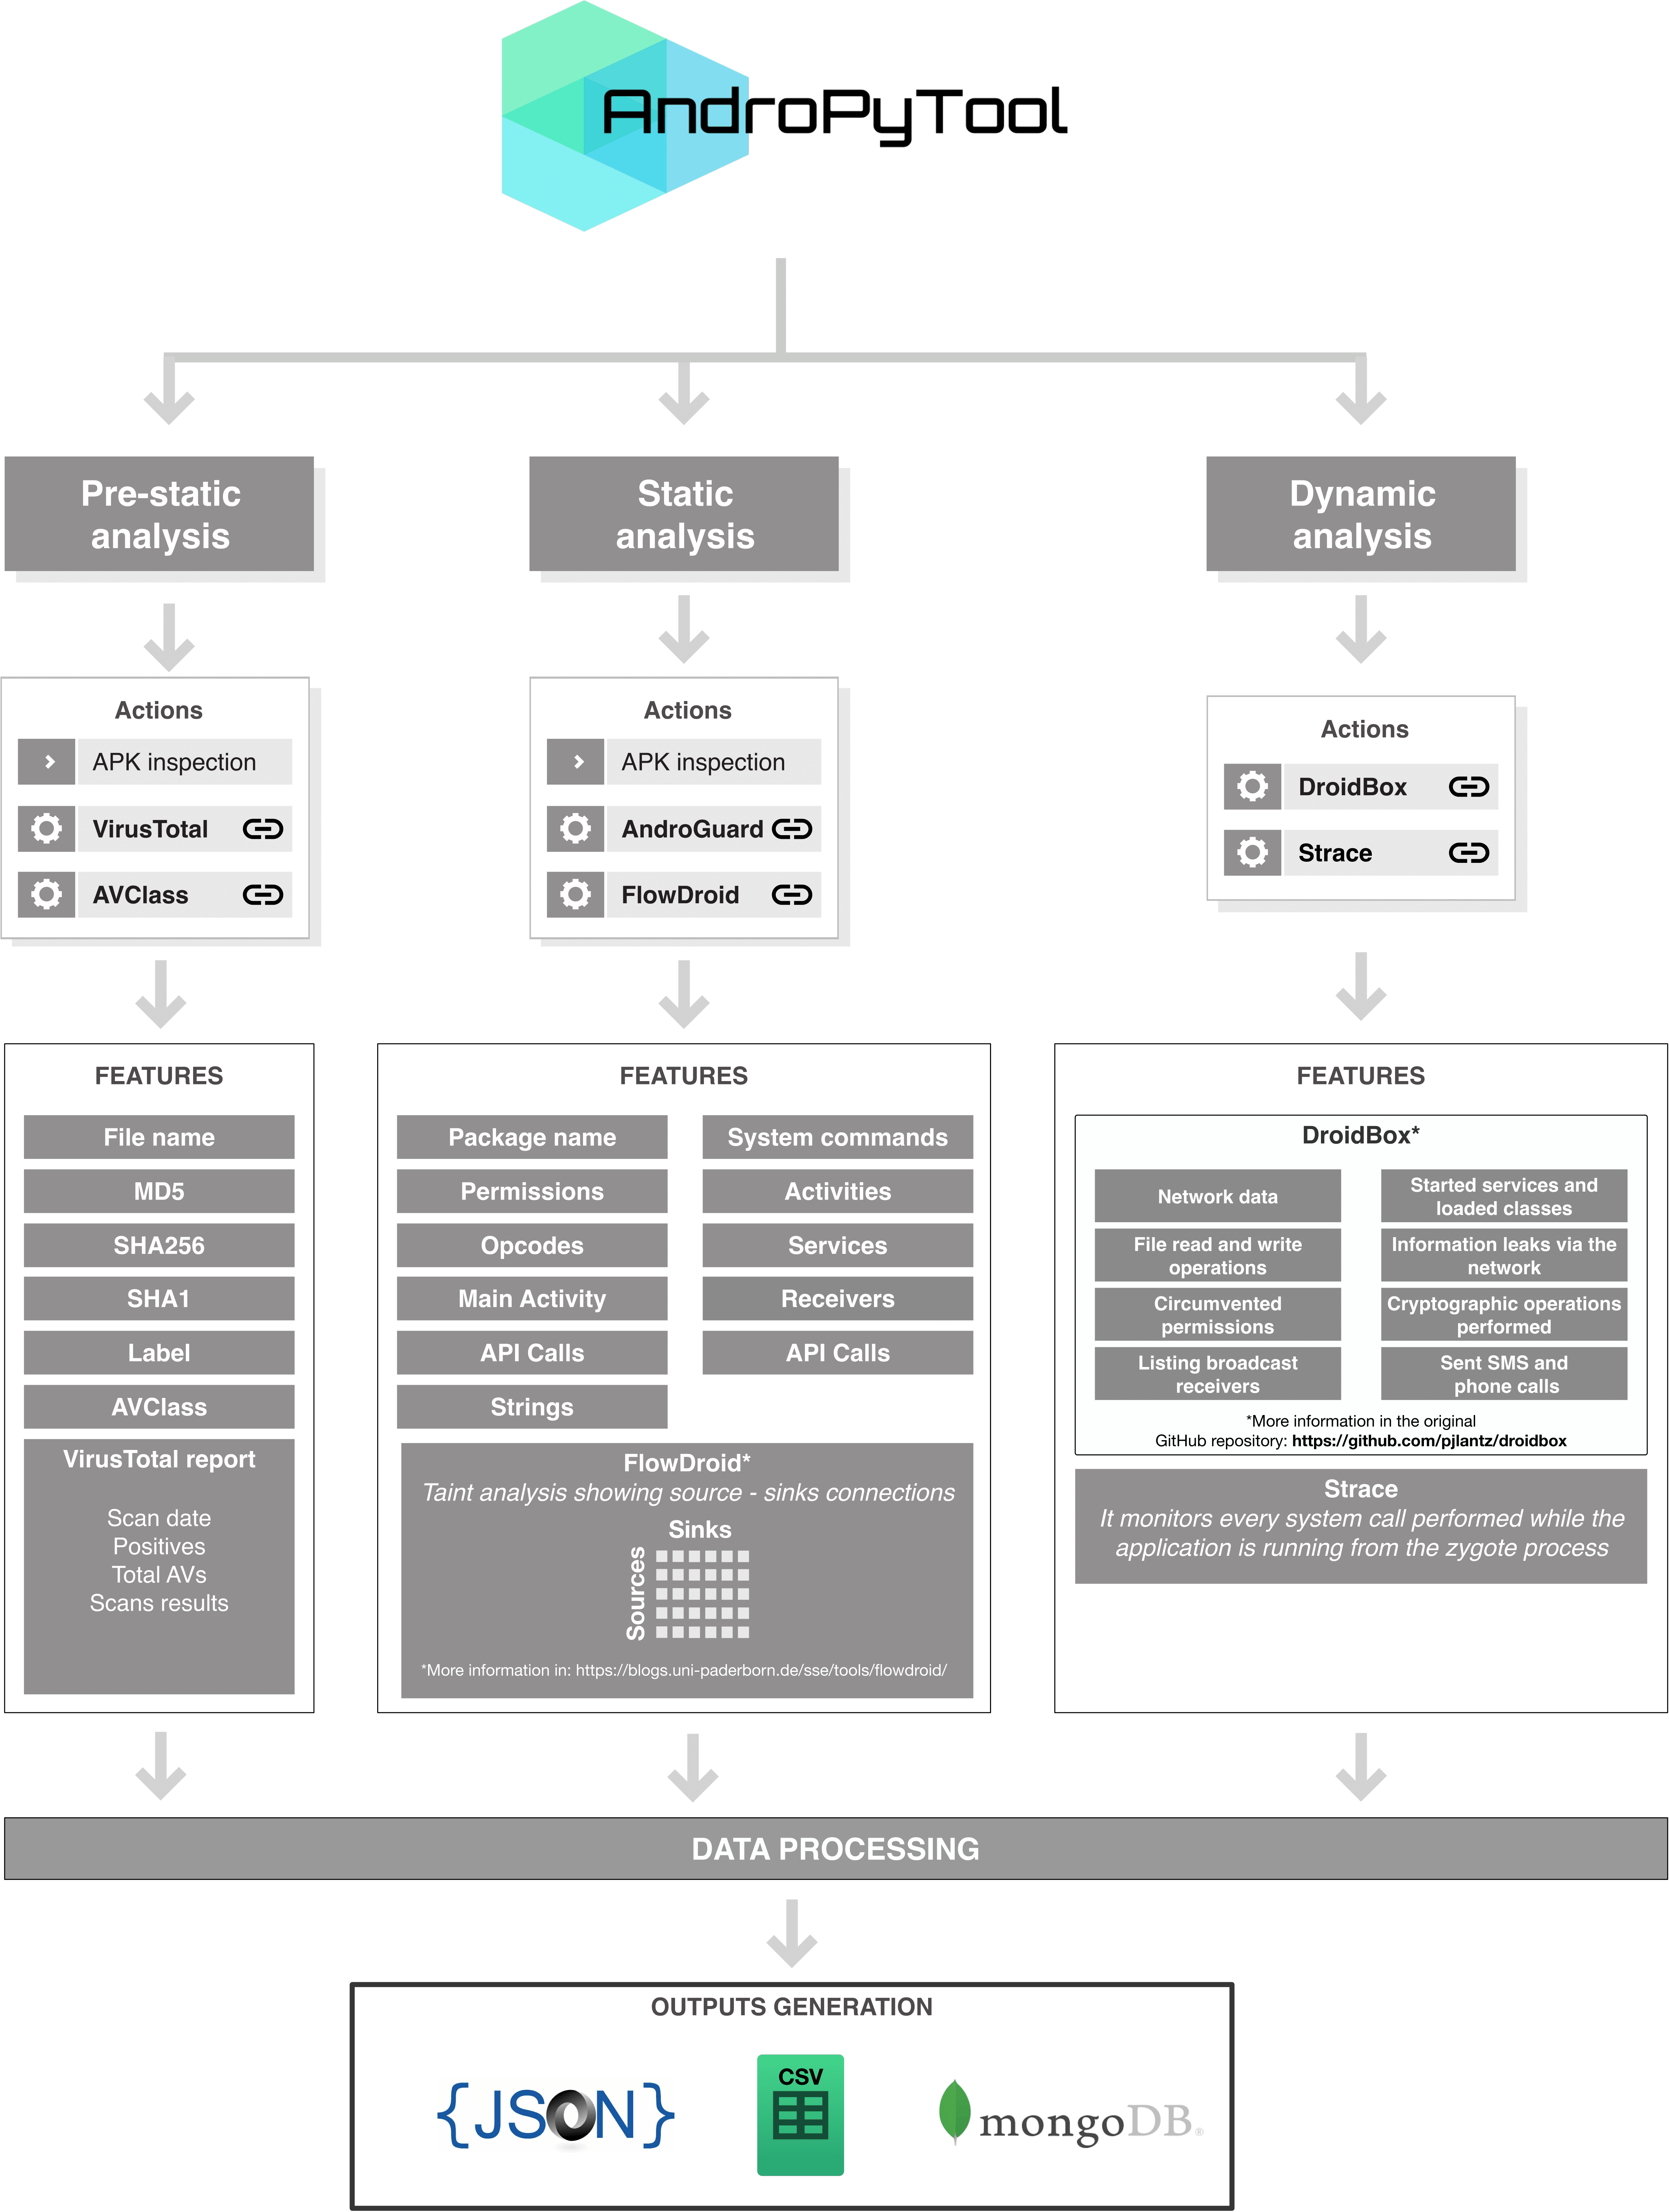 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
 d4vinci/scrapling
🕷️ An adaptive Web Scraping framework that handles everything from a single request to a full-scale crawl!
 stefan2200/aparoid
Static and dynamic Android application security analysis