HydraDragonAV-Mobile

Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware

Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware

High performance fuzzing using riscv to x86 binary translations and modern fuzzing techniques

Dynamic unpacker based on PE-sieve

Expose USB activity on the fly


Security research on Liferay CE 7.0.3 GA4: pre-auth RCE as root (CVE-2020-7961 class) reproduced end-to-end, plus 16 more findings — 8+ with no known…

A GUI-based USB device fuzzer

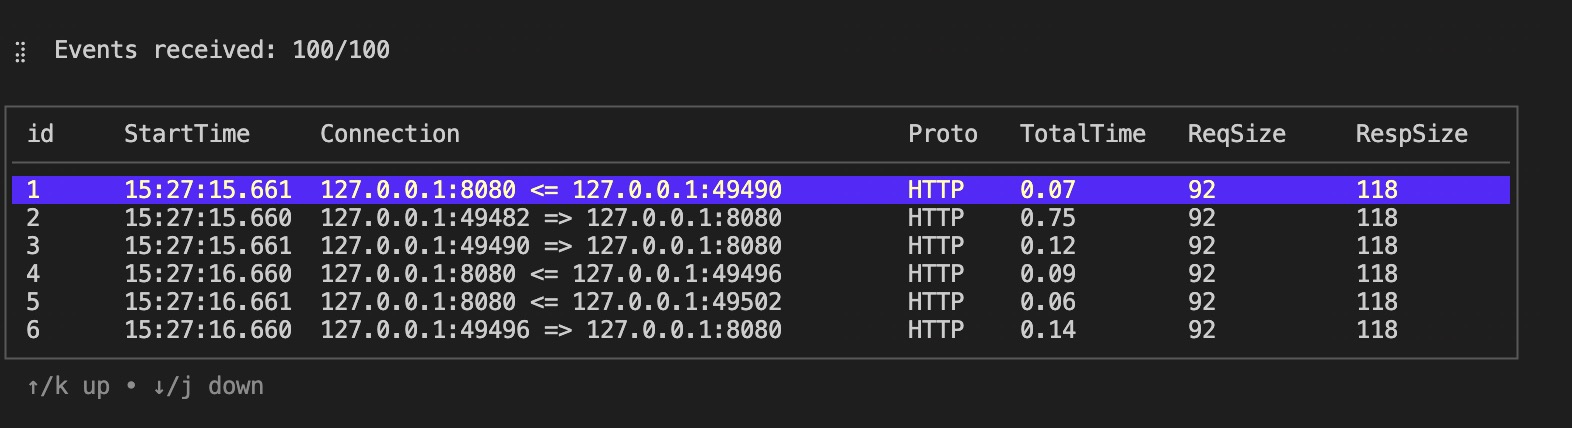
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…

A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…

C++ tool for detecting AnyRun sandbox environments, enabling malware to evade dynamic analysis and automated sandboxing systems.

Control flow hijack exploit for CVE-2020-13995 with Docker-based deployment and Mayhem fuzzing integration for automated vulnerability testing.

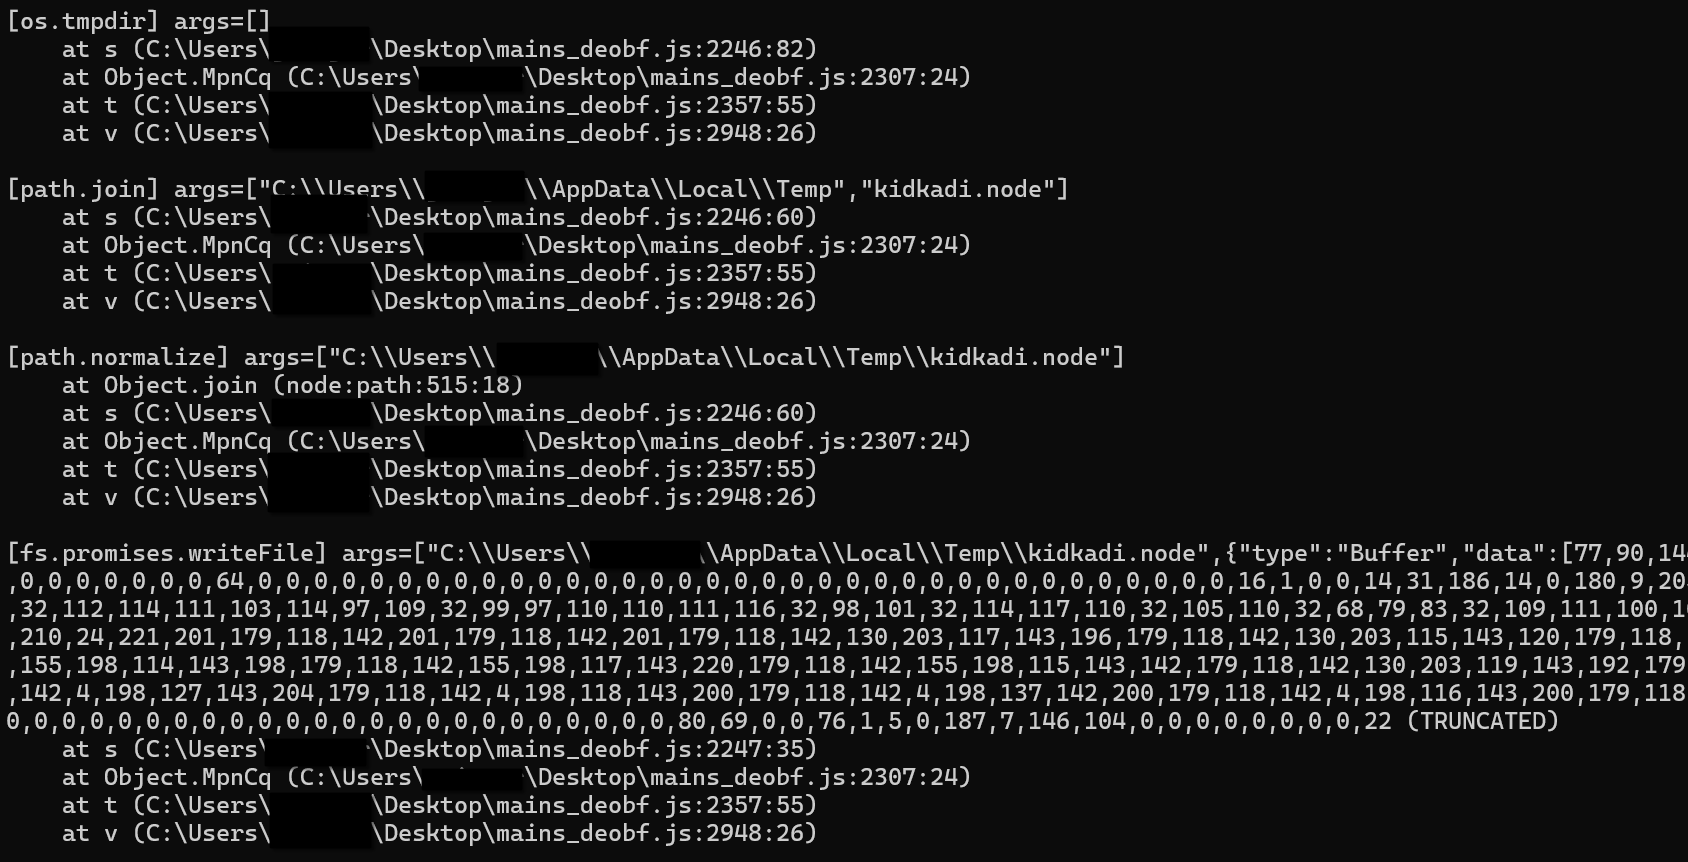
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…

Vulnerability scanner for Spring4Shell (CVE-2022-22965)

A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…

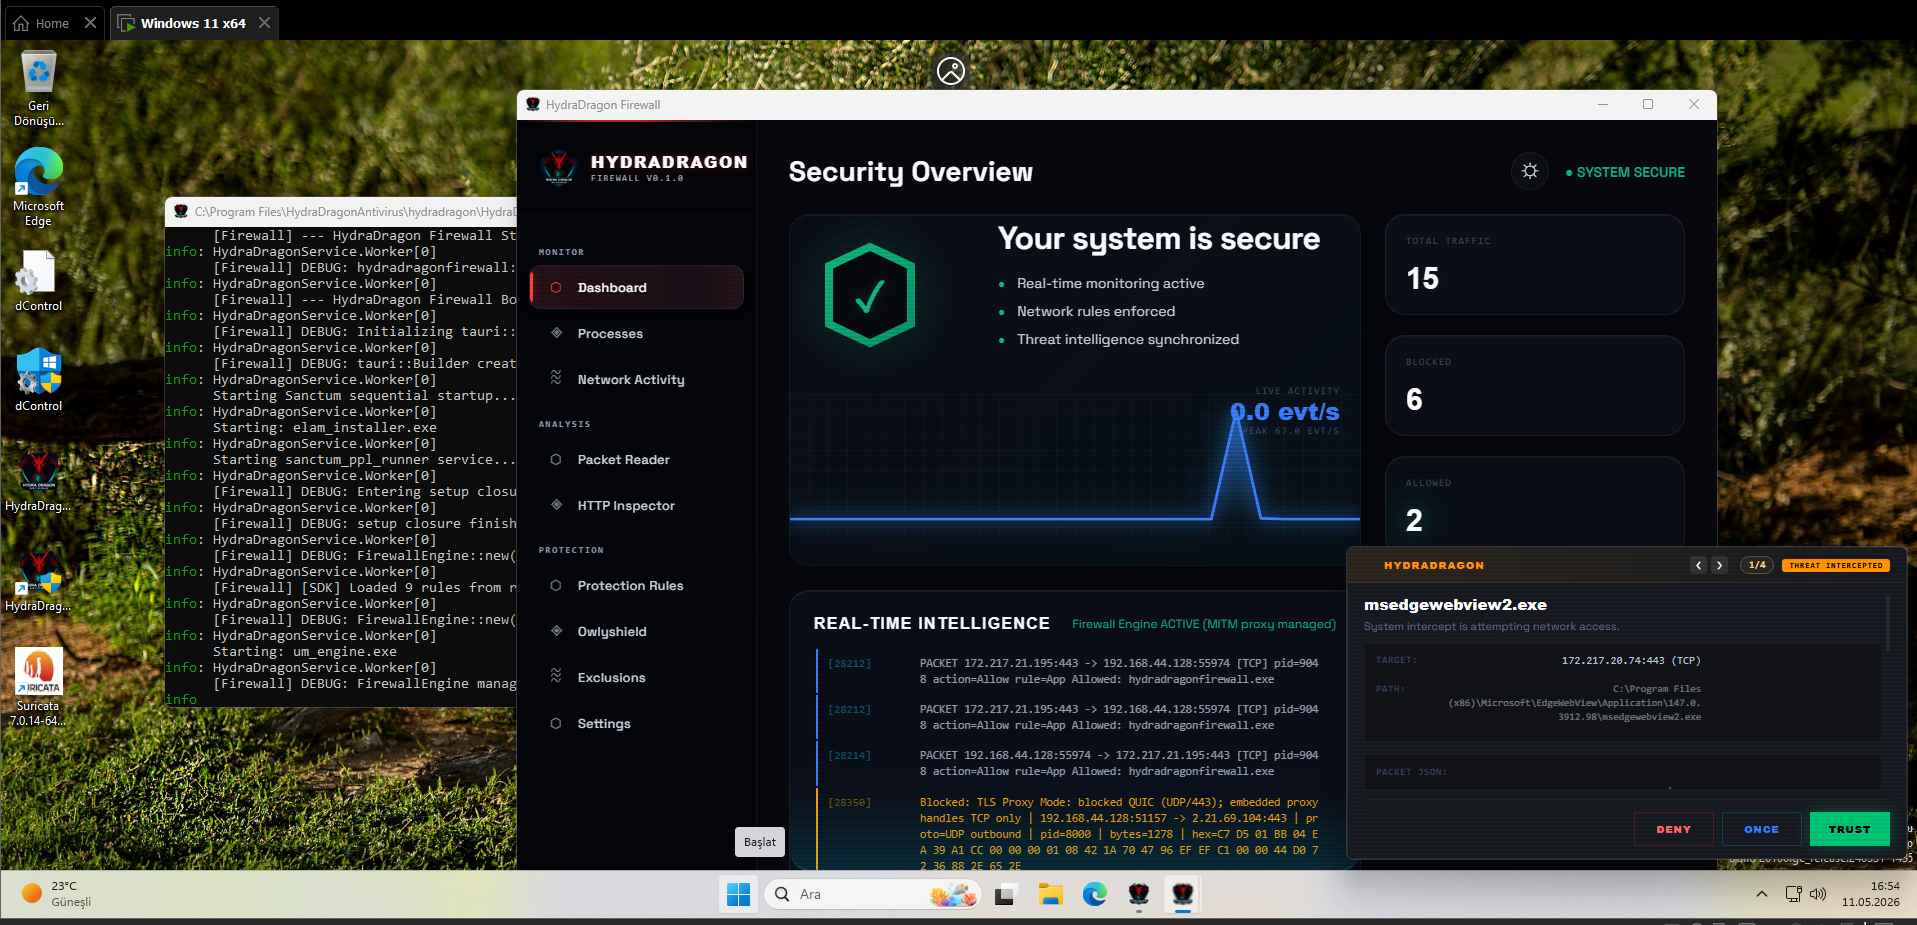
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…

a guard that blocks catastrophic agent actions

A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…

Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)