
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
16 results
redai preview

redai

GitHubkpolley/redai

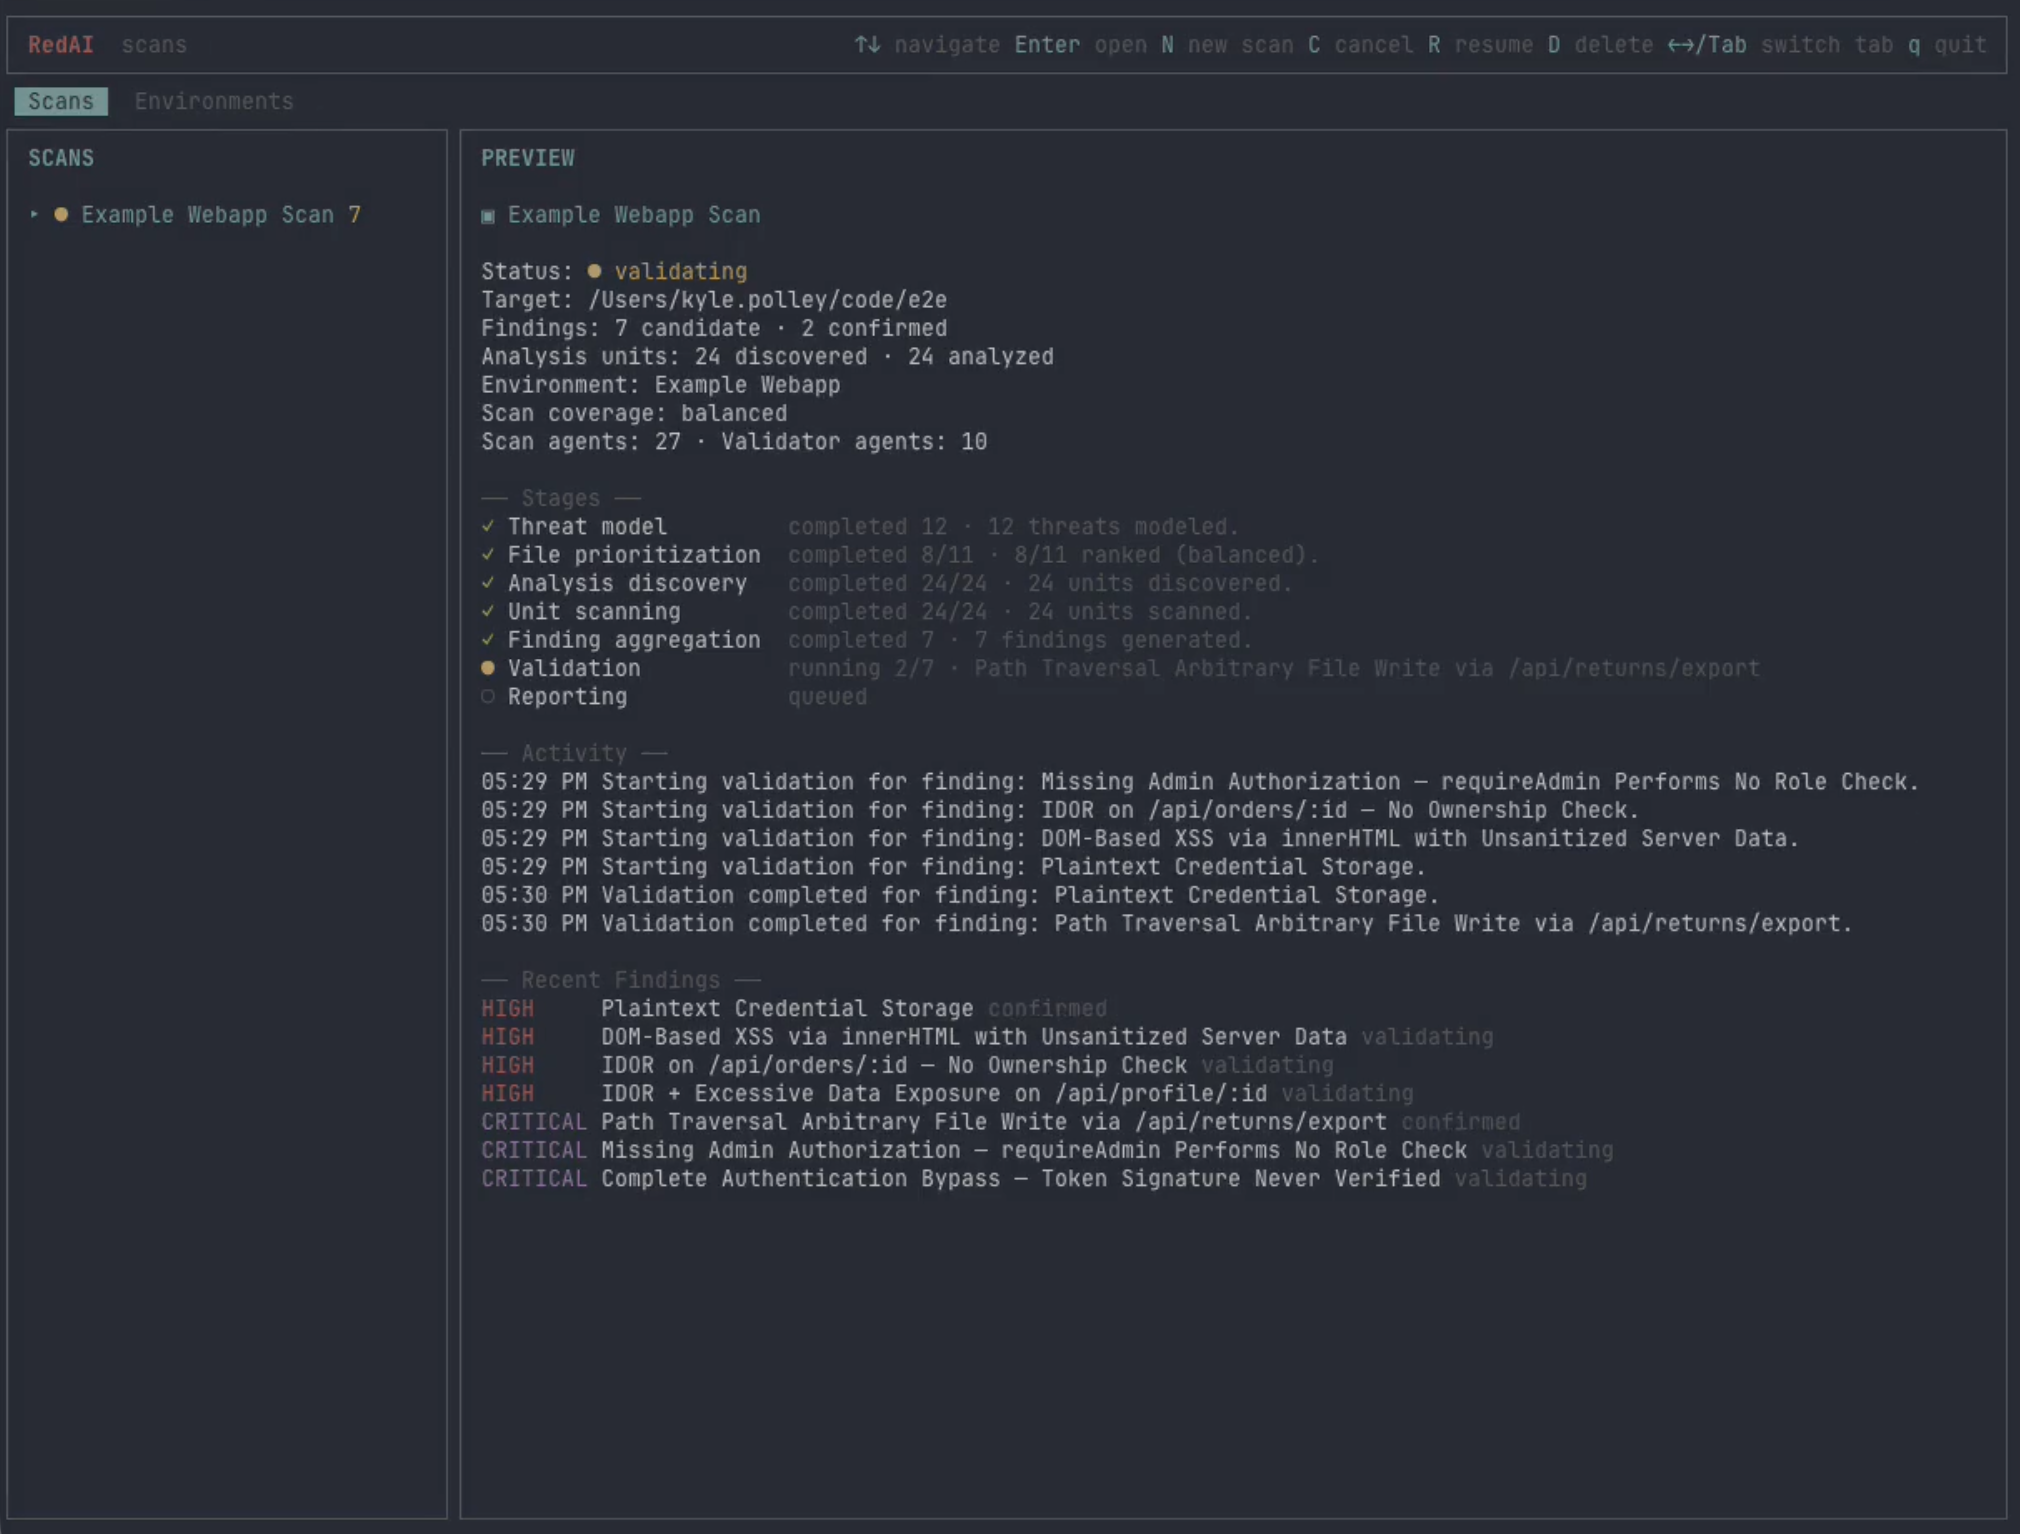
AI-driven vulnerability discovery and live validation

ai-securitydynamic-analysis-sandboxingeducation+6
3465 months ago
mcpsnoop preview

mcpsnoop

GitHubkerlenton/mcpsnoop

Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
api-security-testingdebuggersdynamic-analysis-sandboxing+5
35514 days ago
theZoo preview

theZoo

GitHubytisf/thezoo

Curated repository of live malware samples and source code for educational malware analysis and research, with an organized database and CLI tools…
curated-resourcesdynamic-analysis-sandboxingeducation+3
13.4k11 days ago
windbg-decompile-ext preview

windbg-decompile-ext

GitHubkernullist/windbg-decompile-ext

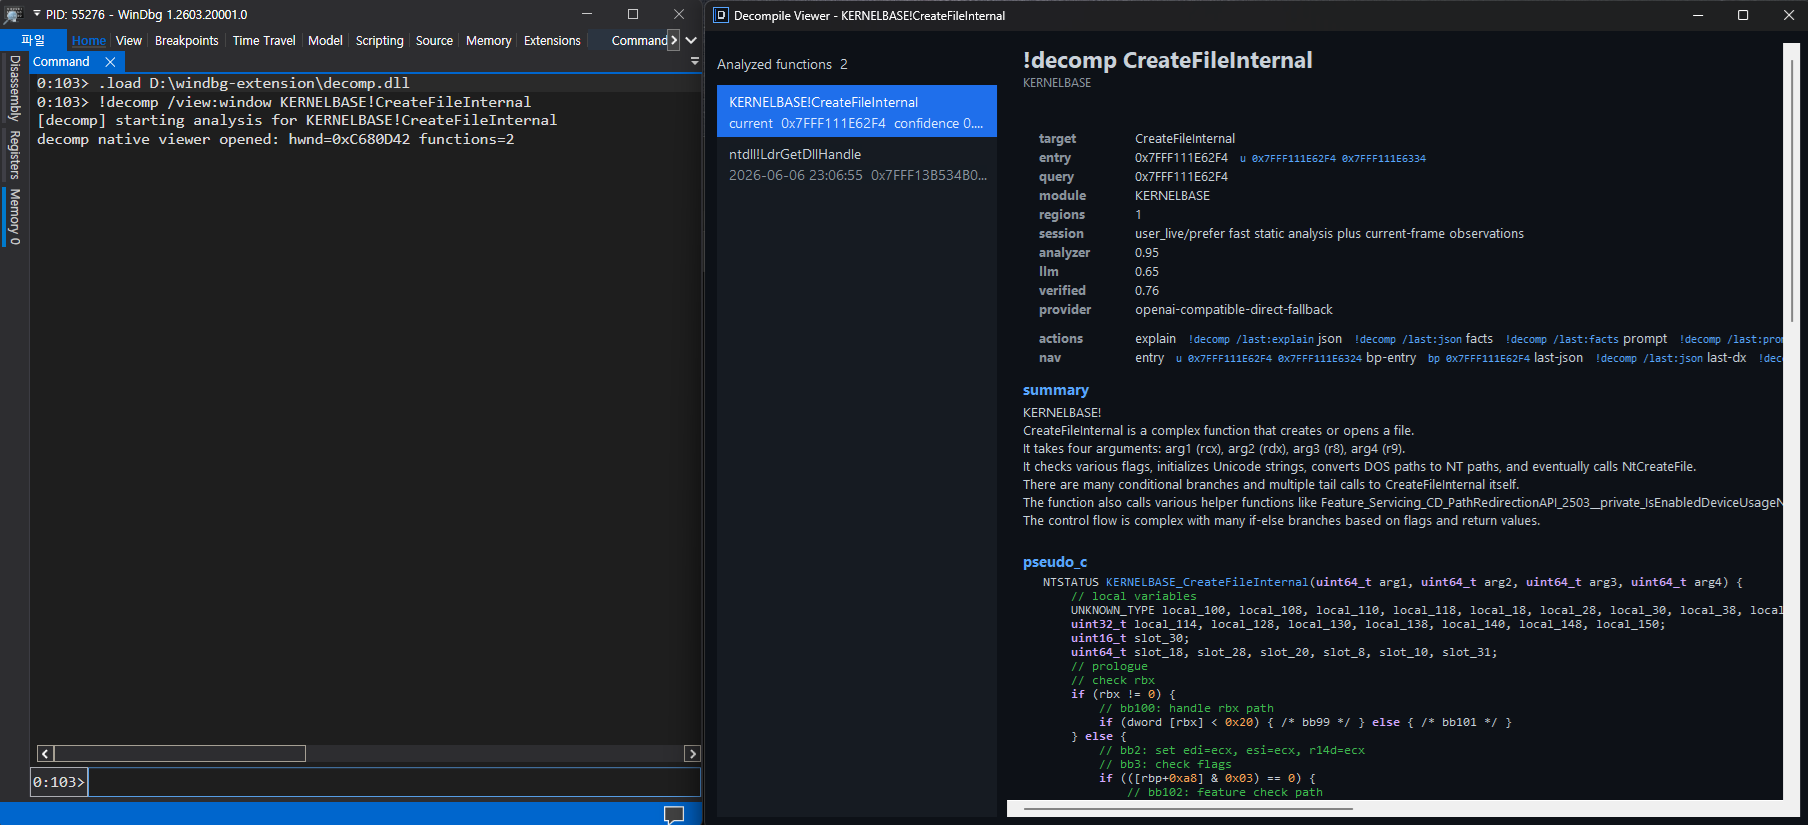
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
ai-assisted-reversingbinary-analysisbinary-exploitation+8
1103 months ago
rikune preview

rikune

GitHublast-emo-boy/rikune

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
binary-analysisdynamic-analysis-sandboxingeducation+8
2411 day ago
sigwire preview

sigwire

GitHubyeet-src/sigwire

Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
debuggersdynamic-analysis-sandboxingforensics+2
1611 month ago
ghidra-mcp preview

ghidra-mcp

GitHubbethington/ghidra-mcp

MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
ai-assisted-reversingbinary-analysisdebuggers+7
4.0k19h 59m ago
vpod preview

vpod

GitHubcapsulerun/vpod

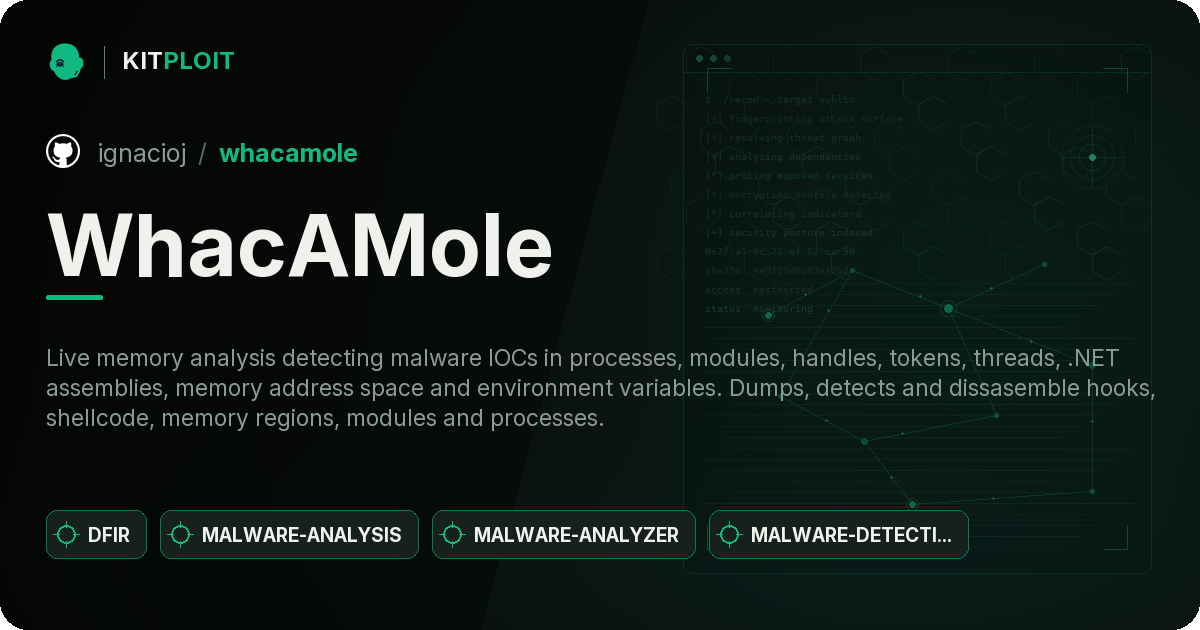
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
ai-securitycontainer-securitydefensive-tools+3
744 days ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
binary-analysisdebuggersdigital-forensics+9
442 years ago
tusk-cli preview

tusk-cli

GitHubuse-tusk/tusk-cli

Automated testing suite with live traffic record and replay
api-security-testingcode-analysisdevsecops+3
1434 months ago
ebpfmon preview

ebpfmon

GitHubredcanaryco/ebpfmon

Terminal UI for real-time monitoring and inspection of eBPF programs and maps using bpftool, enabling live debugging and analysis of kernel-level…
debuggersdynamic-analysis-sandboxingutilities-frameworks
903 years ago
meowEye preview

meowEye

GitHubeslam3kl/meoweye

MeowEye is a real-time scanner for identifying multiple web vulnerabilities in live applications.
dynamic-analysis-sandboxingfuzzingpenetration-testing+3
31 year ago
usbsnoop preview

usbsnoop

GitHubyeet-src/usbsnoop

Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…

debuggersdynamic-analysis-sandboxingembedded-systems-security+7
871 month ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
672 months ago
liferay-ga4-rce-research preview

liferay-ga4-rce-research

GitHubdinosn/liferay-ga4-rce-research

Security research on Liferay CE 7.0.3 GA4: pre-auth RCE as root (CVE-2020-7961 class) reproduced end-to-end, plus 16 more findings — 8+ with no known…

dynamic-analysis-sandboxingexploitationpapers-research+6
71 month ago
frida-medit preview

frida-medit

GitHubgmh5225/frida-medit

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…

binary-analysisdebuggersdynamic-analysis-sandboxing+3
3 years ago