
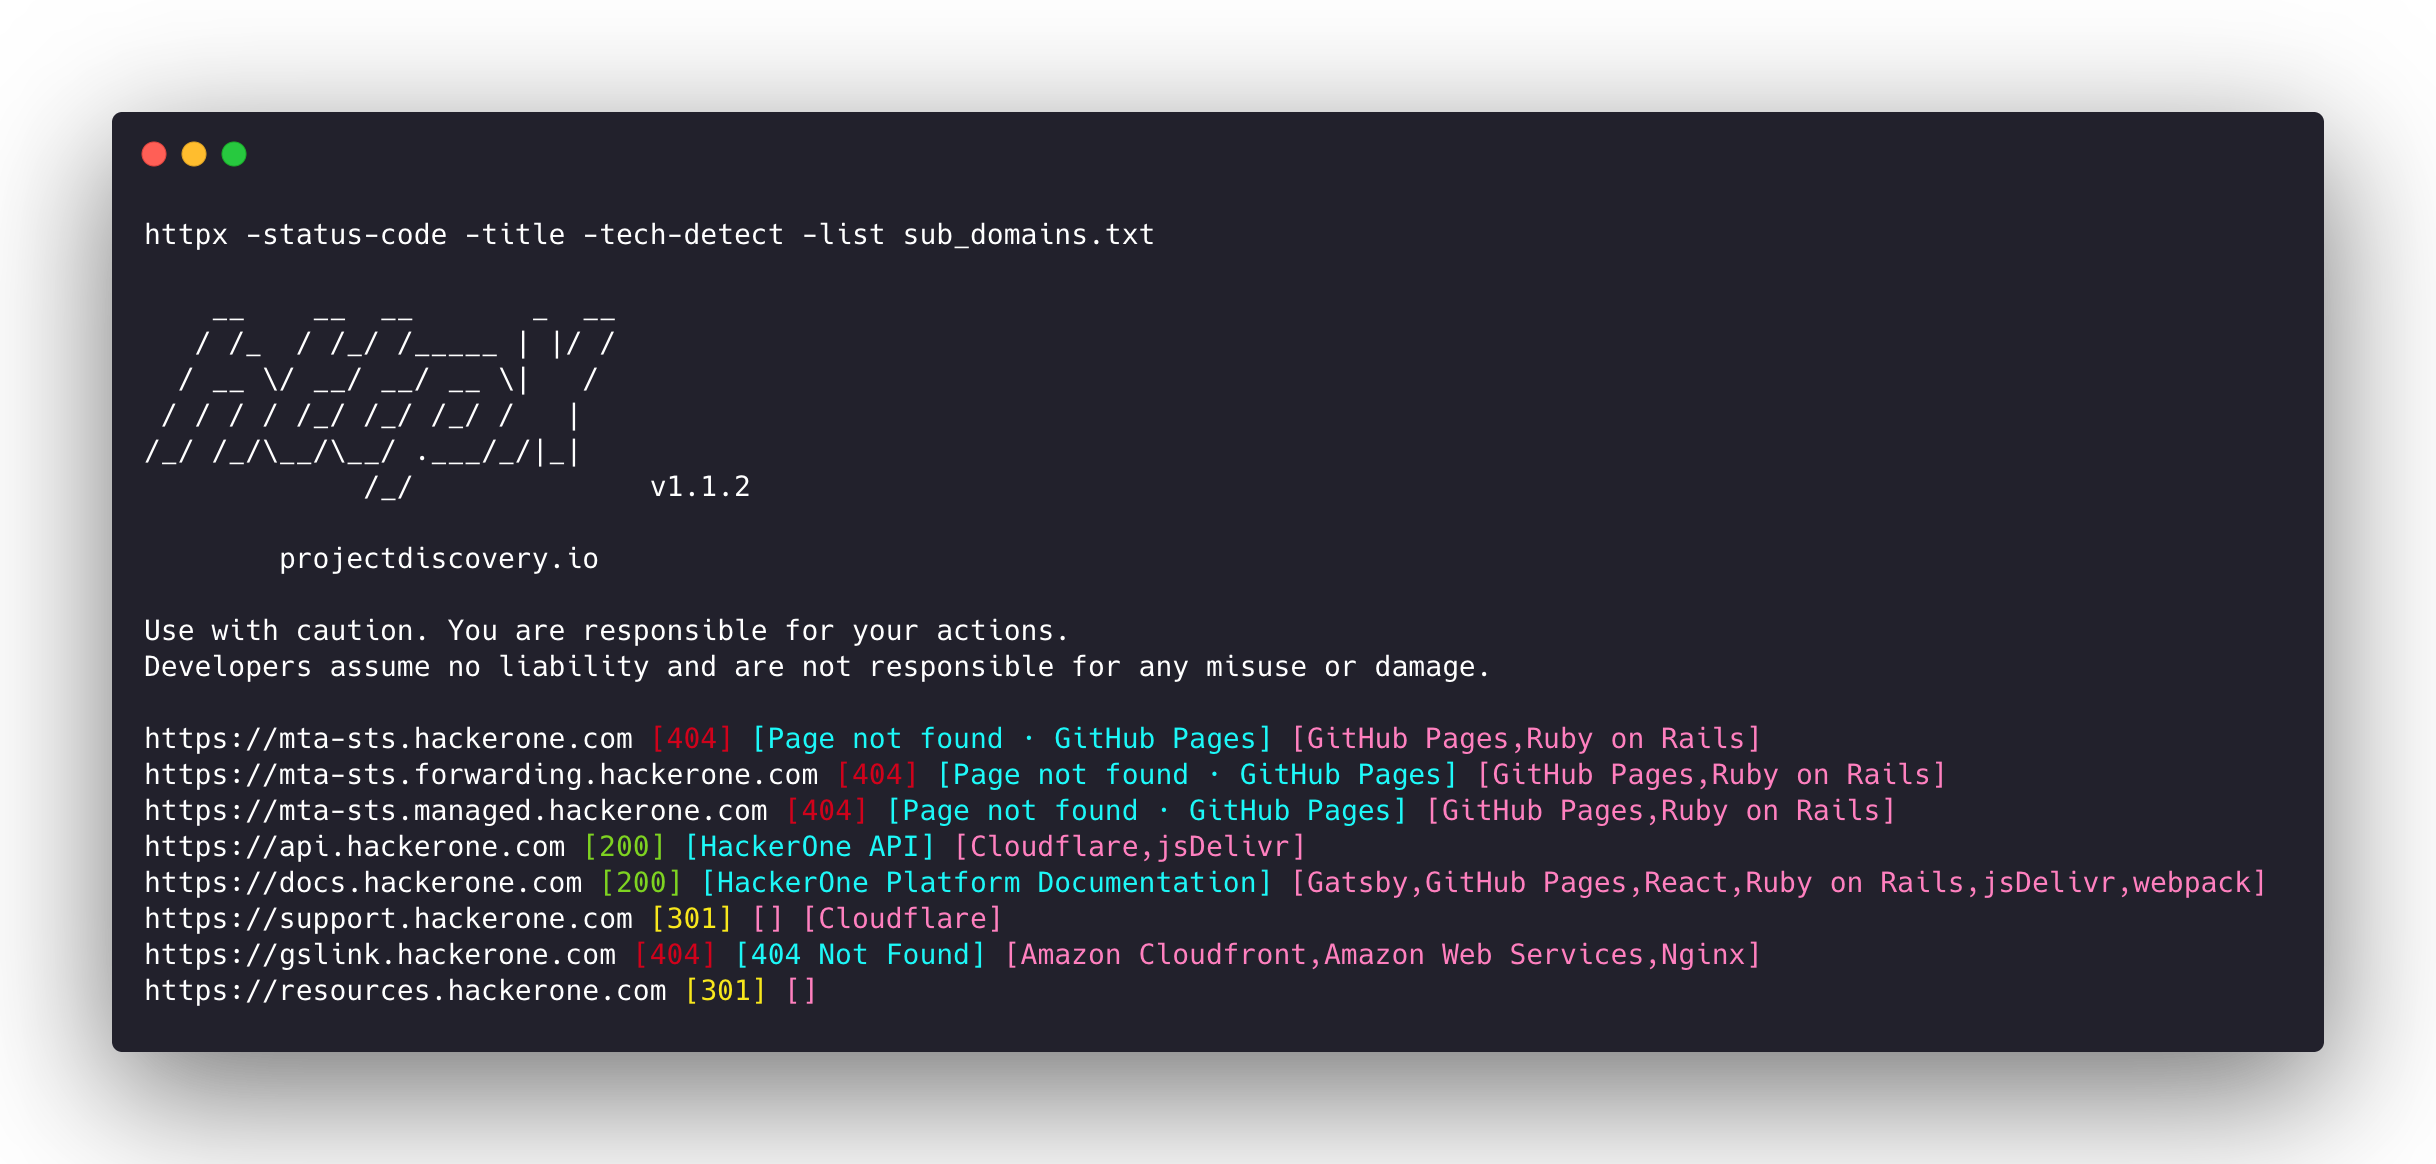
httpx
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
api-securityapi-security-testingcrawler+18
10.4k
projectdiscovery/httpxFast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
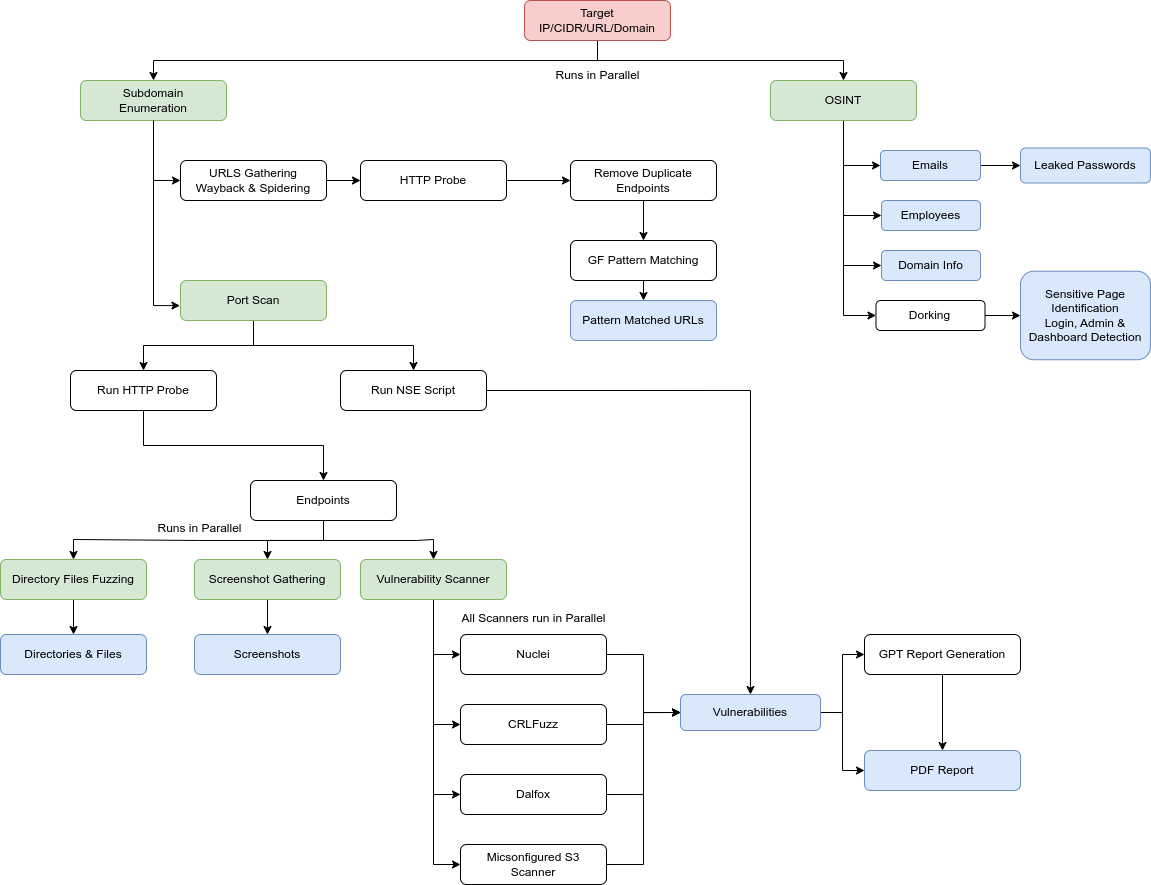 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…
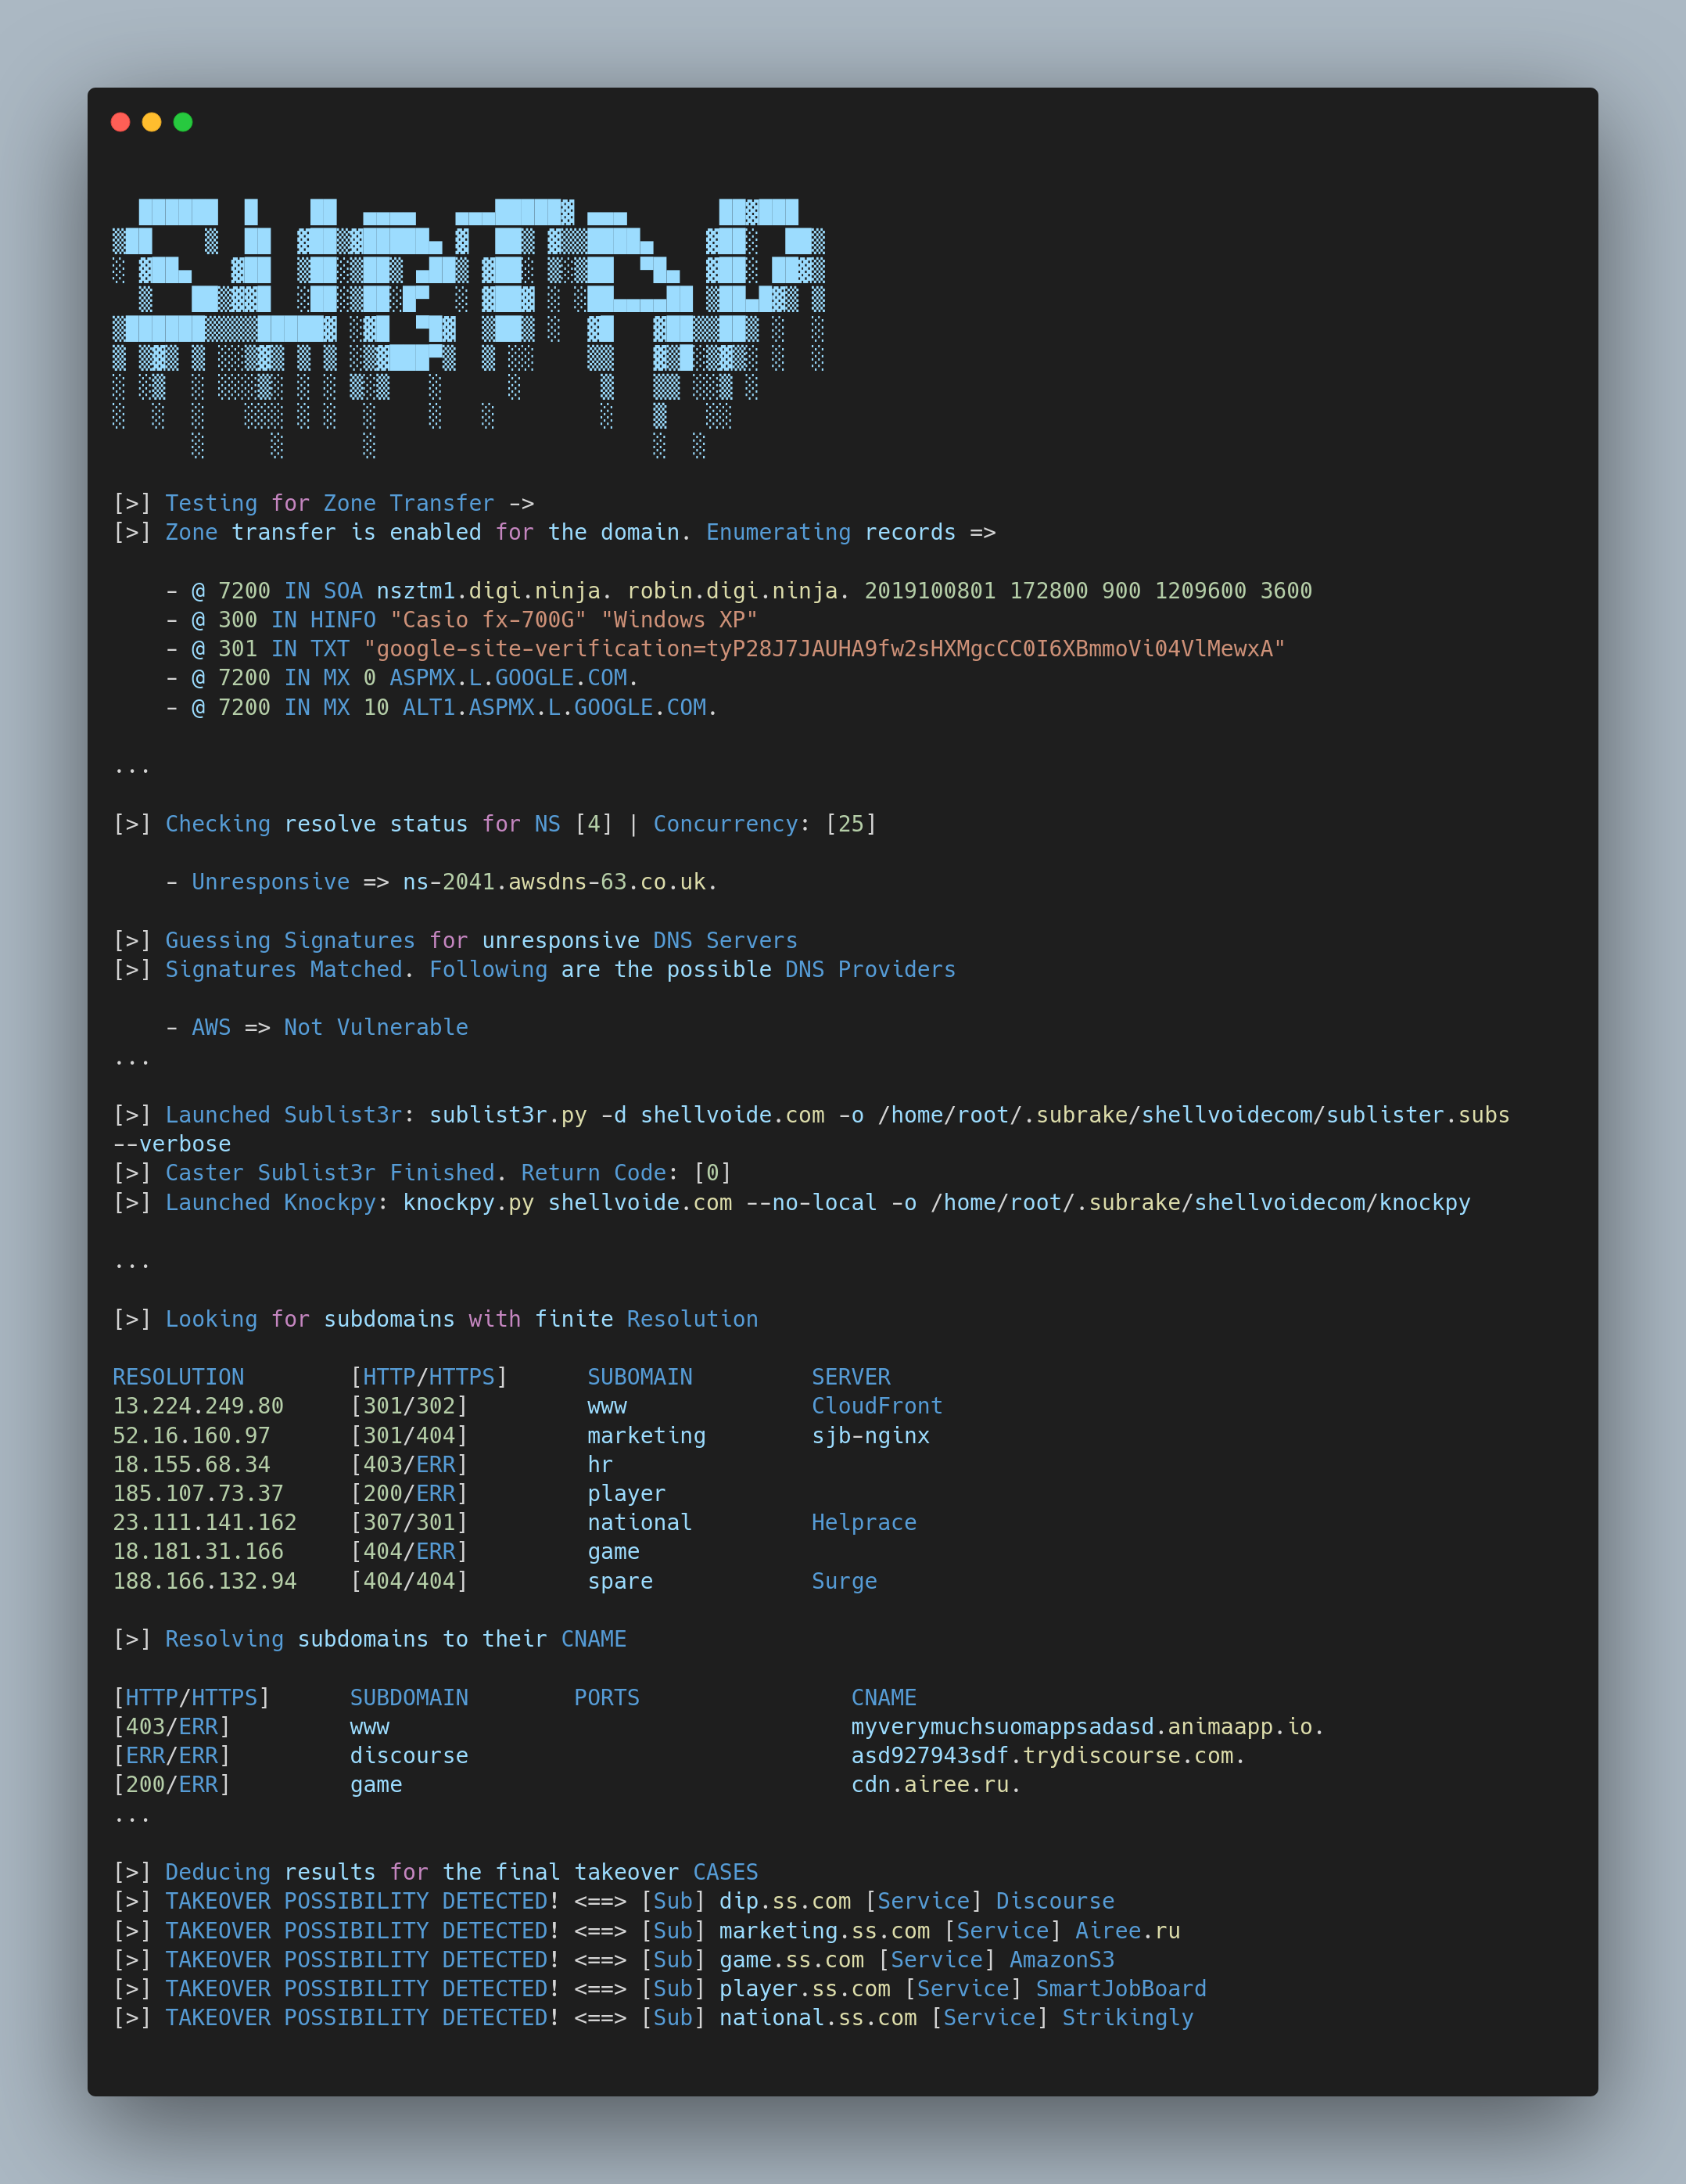 hash3lizer/subrake
🚀 A DNS automated scanner and tool 🖱️ (Zone Transfer, DNS Zone Takeover, Subdomain Takeover).
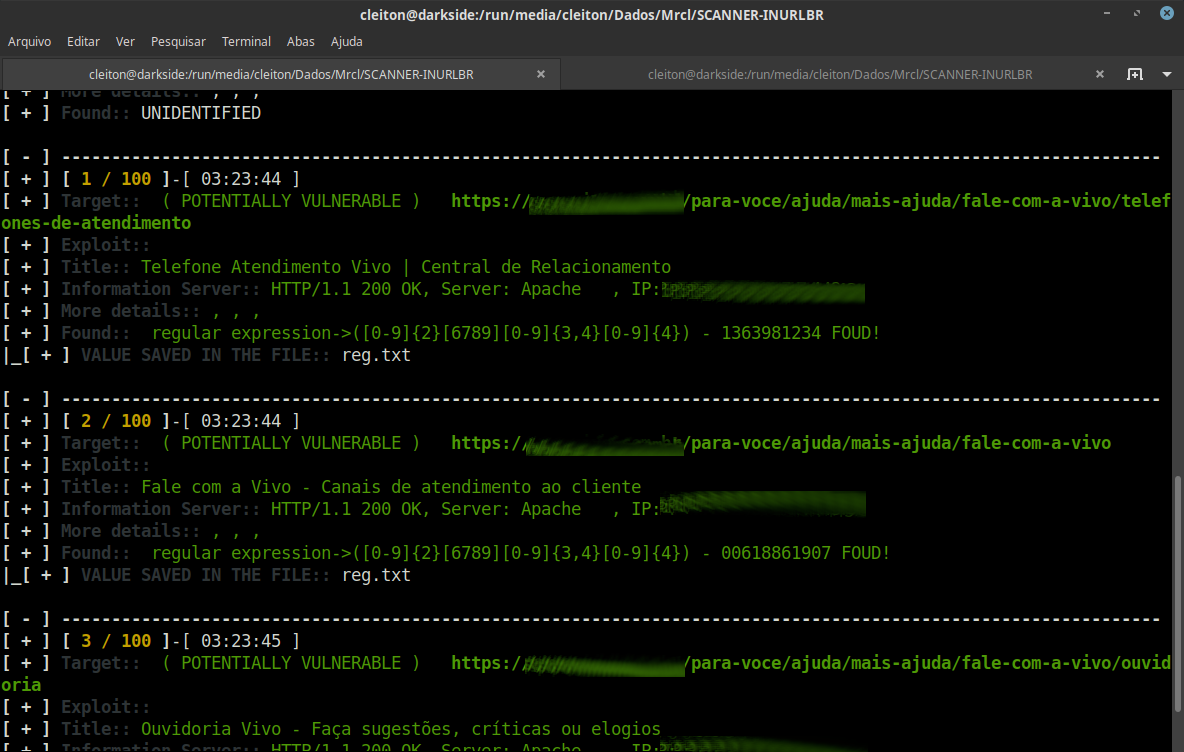 mrcl0wnlab/scanner-inurlbr
Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation…
 cyberdev.hacker/nsec3-x
The modern, high-speed successor to nsec3walker. A specialized NSEC3 forensics engine built in Go for rapid zone harvesting and automated hash…
 r3curs1v3-pr0xy/vajra
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…
 clouedoc/autosqli
An automatic SQL Injection tool which takes advantage of ~DorkNet~ Googler, Ddgr, WhatWaf and sqlmap.
 0x0fb0/pulsar
Network footprint scanner platform. Discover domains and run your custom checks periodically.
 apurvsinghgautam/dark-web-osint-tools
OSINT Tools for the Dark Web
 dwisiswant0/go-dork
The fastest dork scanner written in Go.
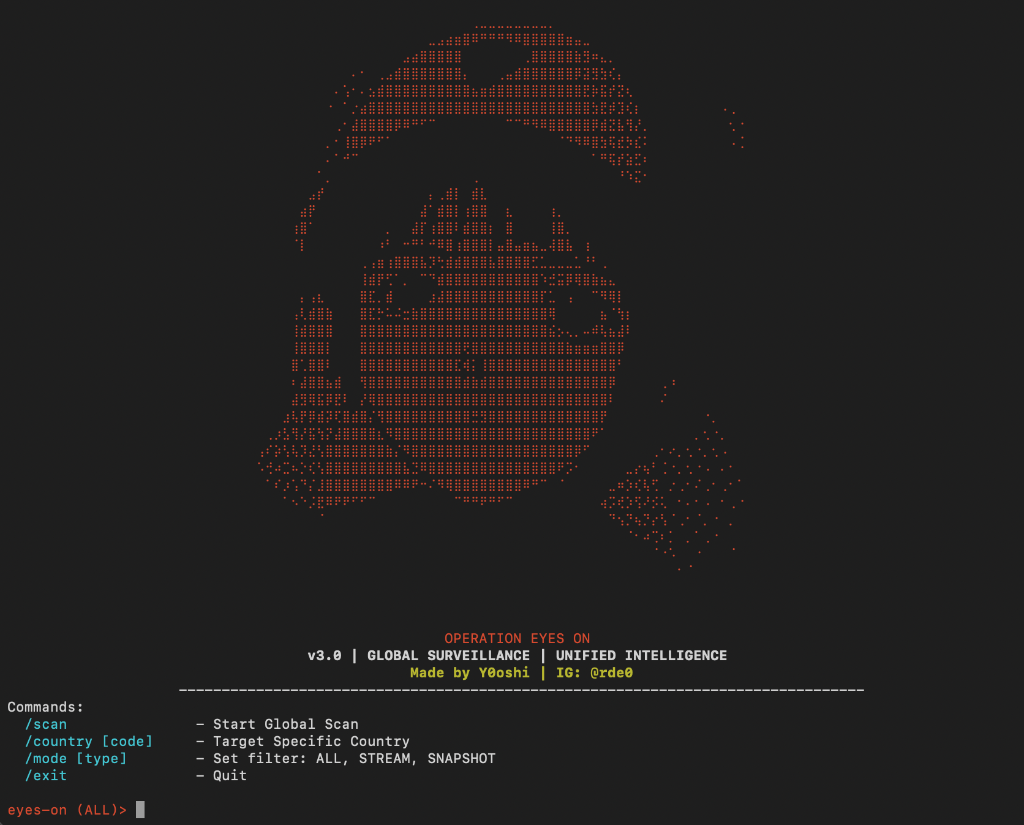 y0oshi/project-eyes-on
Project Eyes On is a high-speed, multi-threaded surveillance tool by Y0oshi (@rde0) for locating open IP cameras worldwide. Unifies Google Dorking…
 divinelabio/argus
The Ultimate Information Gathering Toolkit
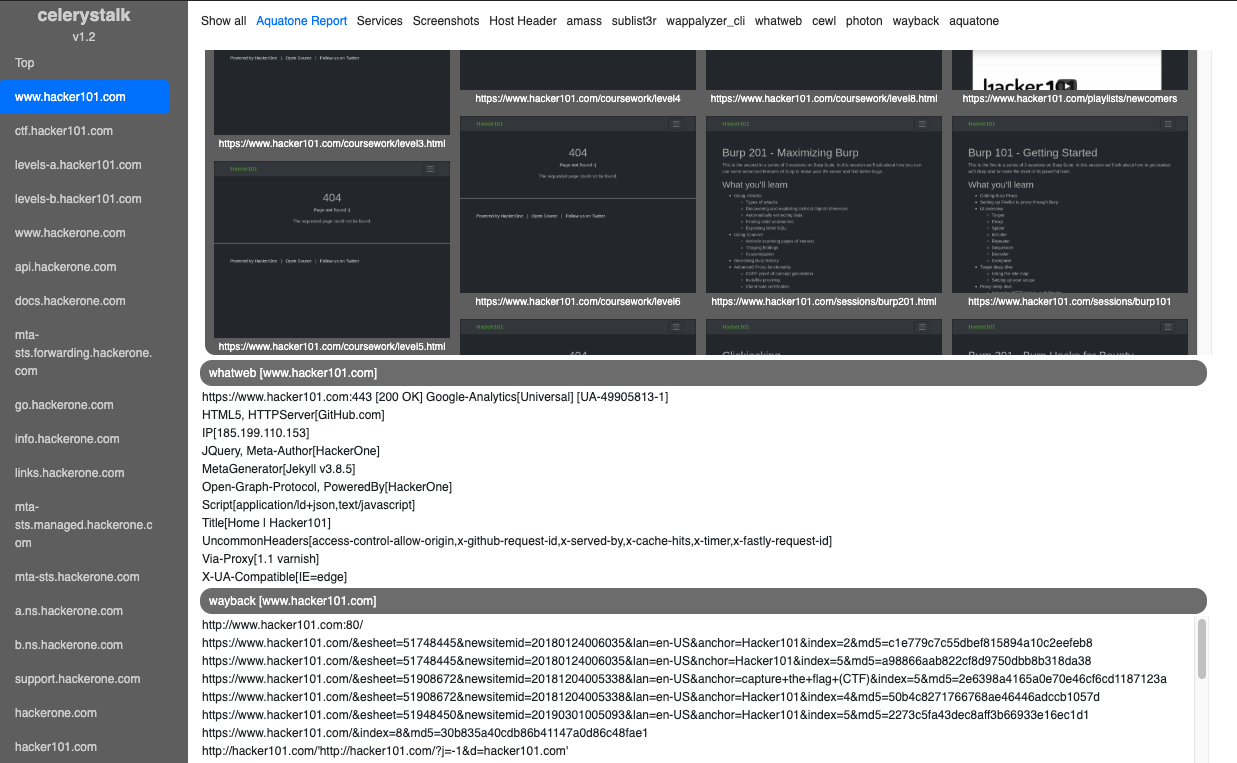 sethsec/celerystalk
An asynchronous enumeration & vulnerability scanner. Run all the tools on all the hosts.
 1n3/goohak
Automatically Launch Google Hacking Queries Against A Target Domain
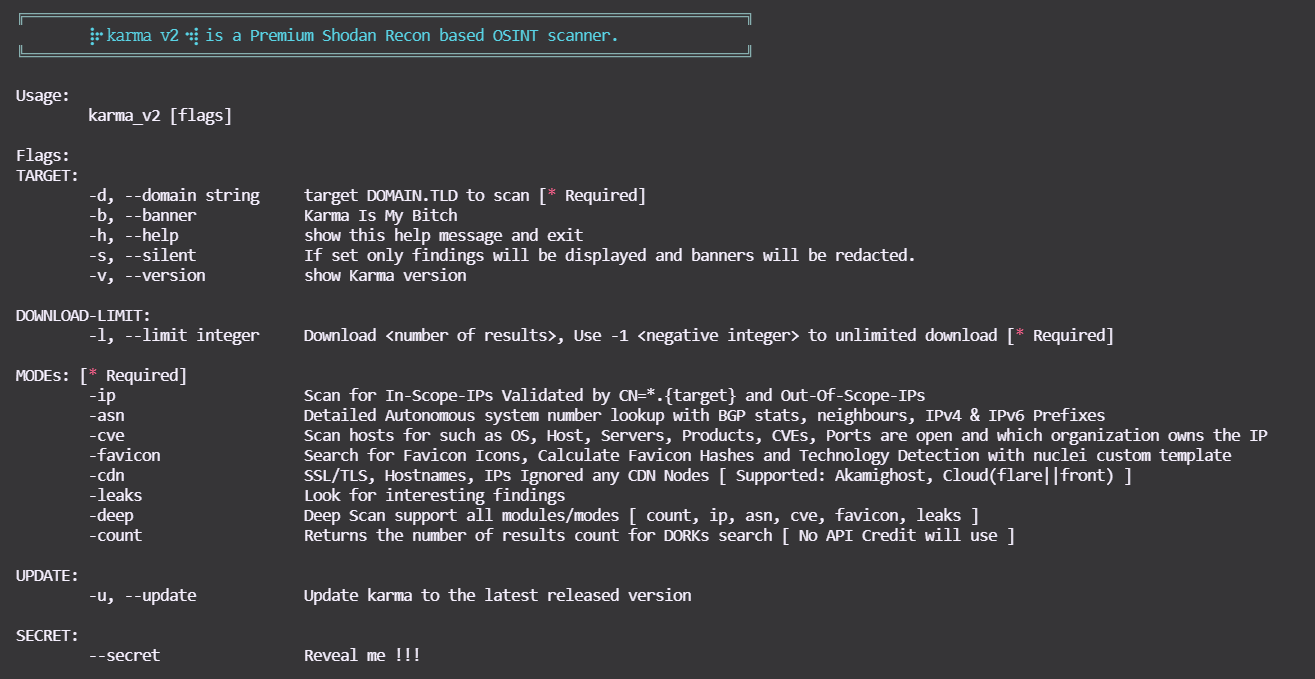 dheerajmadhukar/karma_v2
⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾ is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)