

chiasmodon
 chiasmod0n/chiasmodon
Chiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…
dns-subdomain-enumerationemail-harvestinginformation-gathering+5
703
chiasmod0n/chiasmodonChiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…
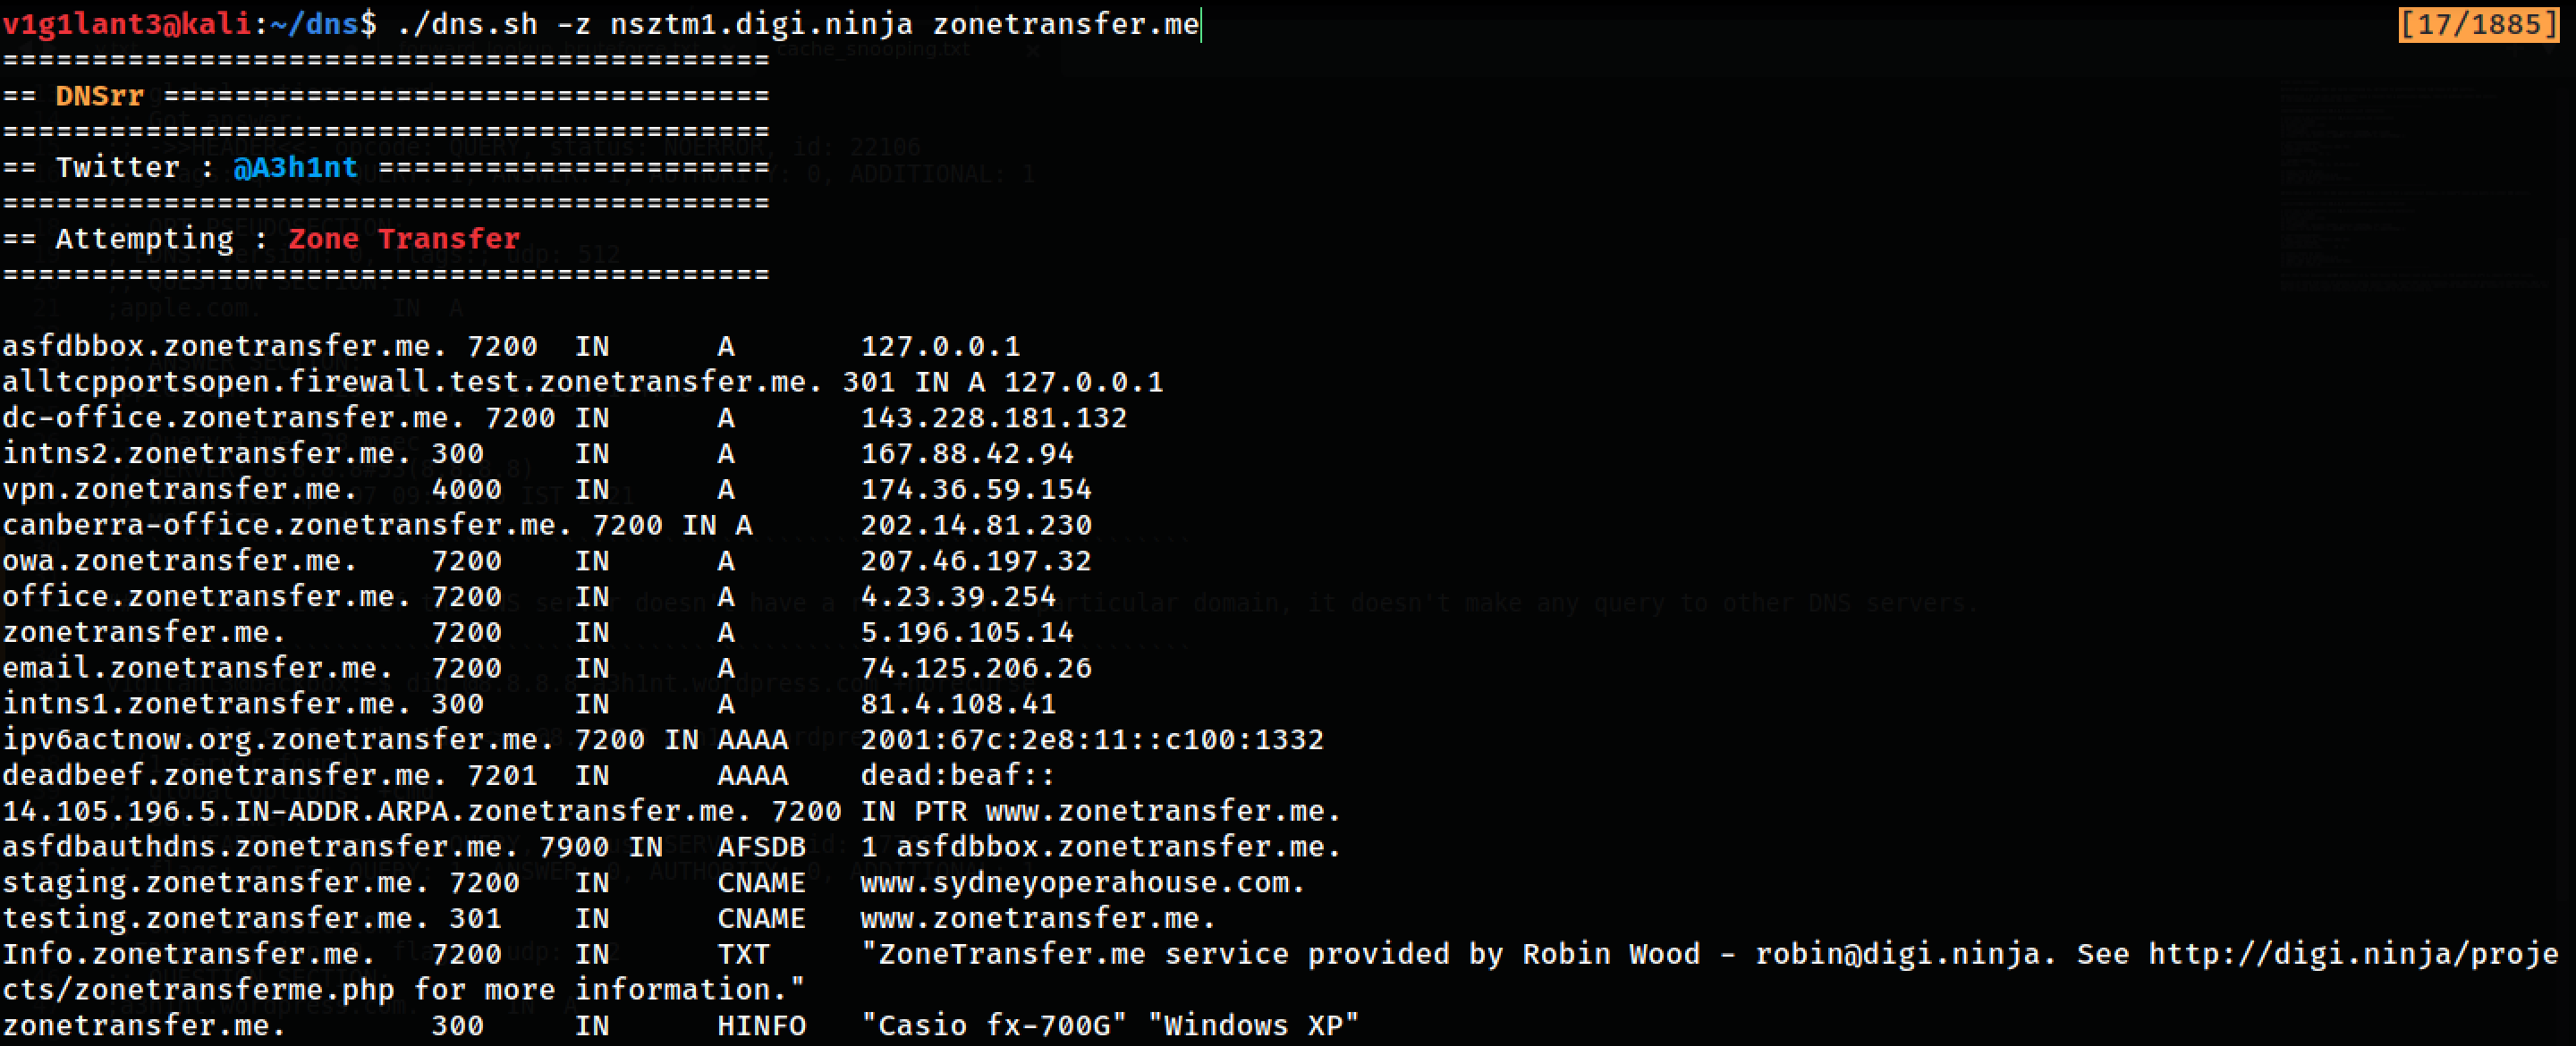 a3h1nt/dnsrr
Bash-based DNS enumeration tool performing forward/reverse bruteforce, cache snooping, and zone transfer to extract DNS records and subdomains.
 yassineaboukir/sublert
Sublert is a security and reconnaissance tool which leverages certificate transparency to automatically monitor new subdomains deployed by specific…
 hackplayers/iptodomain
This tool extract domains from IP address based in the information saved in virustotal.
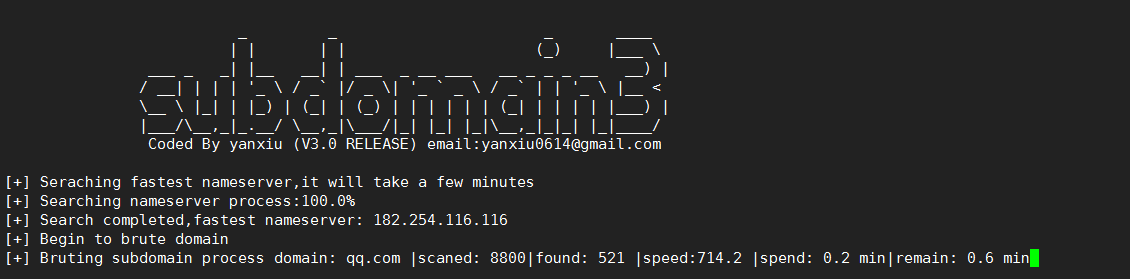 yanxiu0614/subdomain3
A new generation of tool for discovering subdomains( ip , cdn and so on)
 boy-hack/ksubdomain
Subdomain enumeration tool, asynchronous dns packets, use pcap to scan 1600,000 subdomains in 1 second
 ggusoft/inforfinder
Inforfinder is a tool to collect information of any domains pointing at some server (ip, domain, range, file). Is able to detect all domains pointing…
 unapibageek/ctfr
Abusing Certificate Transparency logs for getting HTTPS websites subdomains.
 m0rtem/cloudfail
Utilize misconfigured DNS and old database records to find hidden IP's behind the CloudFlare network
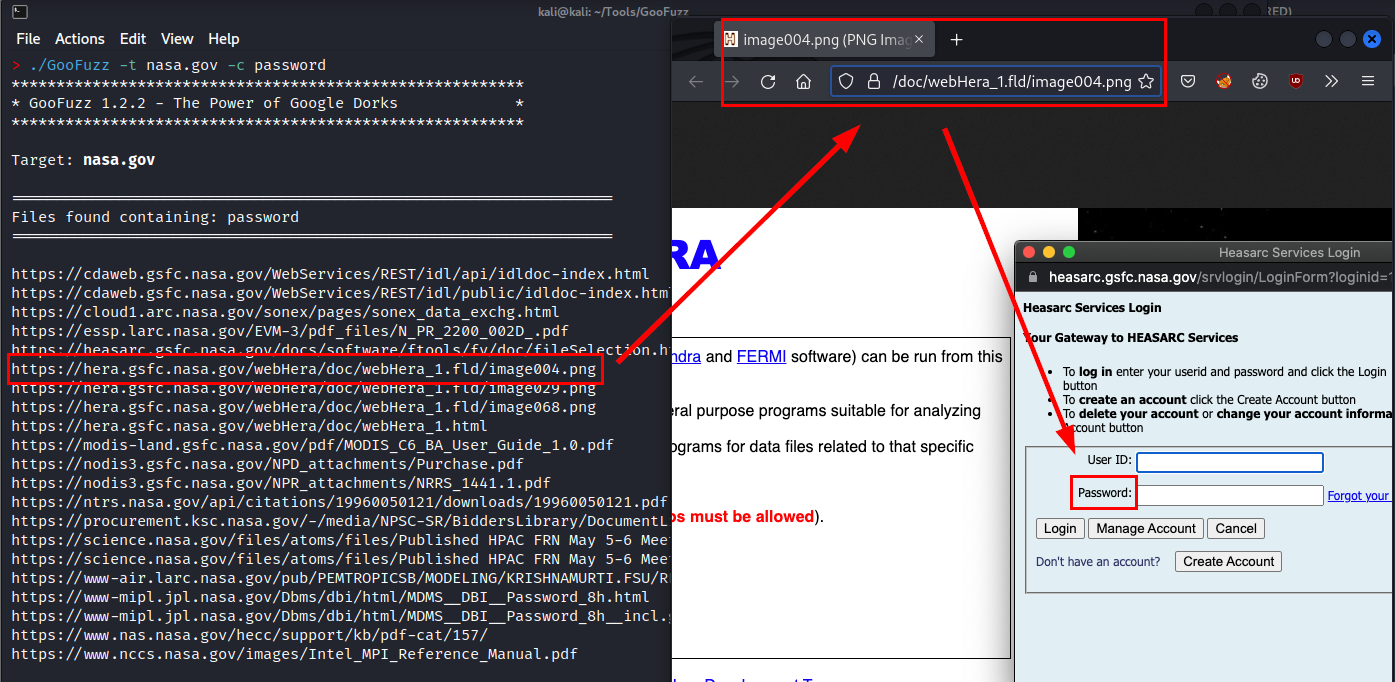 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
 hueristiq/xsubfind3r
Passive subdomain discovery tool that aggregates results from multiple online sources via CLI, supporting stdin/stdout, JSONL output, and API key…
 oj/gobuster
Directory/File, DNS and VHost busting tool written in Go
 sharadkumar97/osint-spy
Performs OSINT scan on email/domain/ip_address/organization using OSINT-SPY. It can be used by Data Miners, Infosec Researchers, Penetration Testers…
 projectdiscovery/shuffledns
MassDNS wrapper written in go to enumerate valid subdomains using active bruteforce as well as resolve subdomains with wildcard filtering and easy…
 elceef/dnstwist
Domain name permutation engine for detecting homograph phishing attacks, typo squatting, and brand impersonation
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
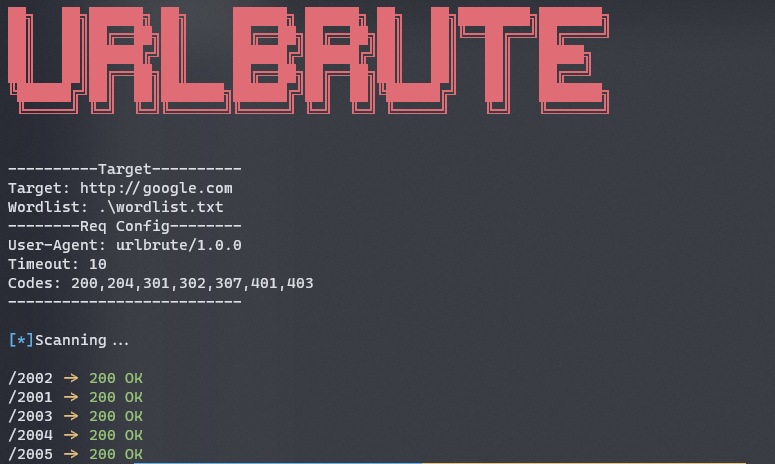 reddyyz/urlbrute
Directory/Subdomain scanner developed in GoLang.
 flipkart-incubator/rta
Red team Arsenal - An intelligent scanner to detect security vulnerabilities in company's layer 7 assets.