
Recon-Scan
 aarocy/recon-scan
Recon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
ai-securitydns-analysisdns-subdomain-enumeration+6
7
aarocy/recon-scanRecon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
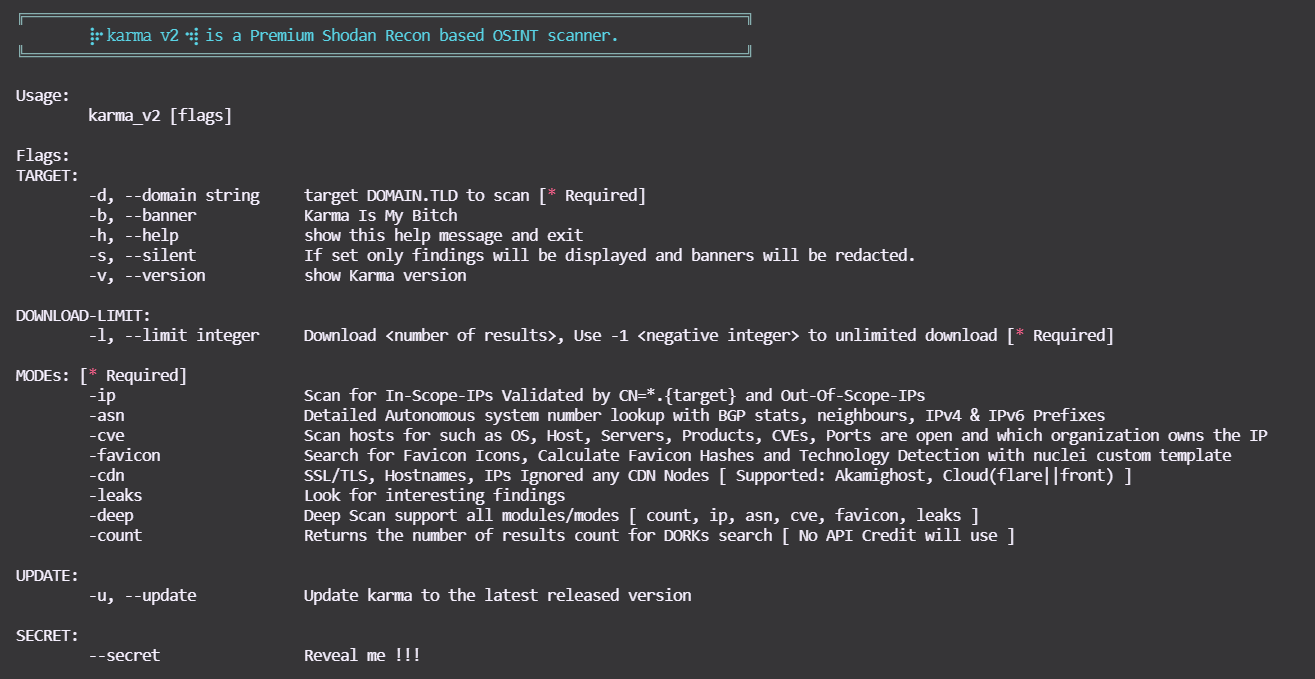 dheerajmadhukar/karma_v2
⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾ is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)

 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 guelfoweb/knockpy
Knock Subdomain Scan
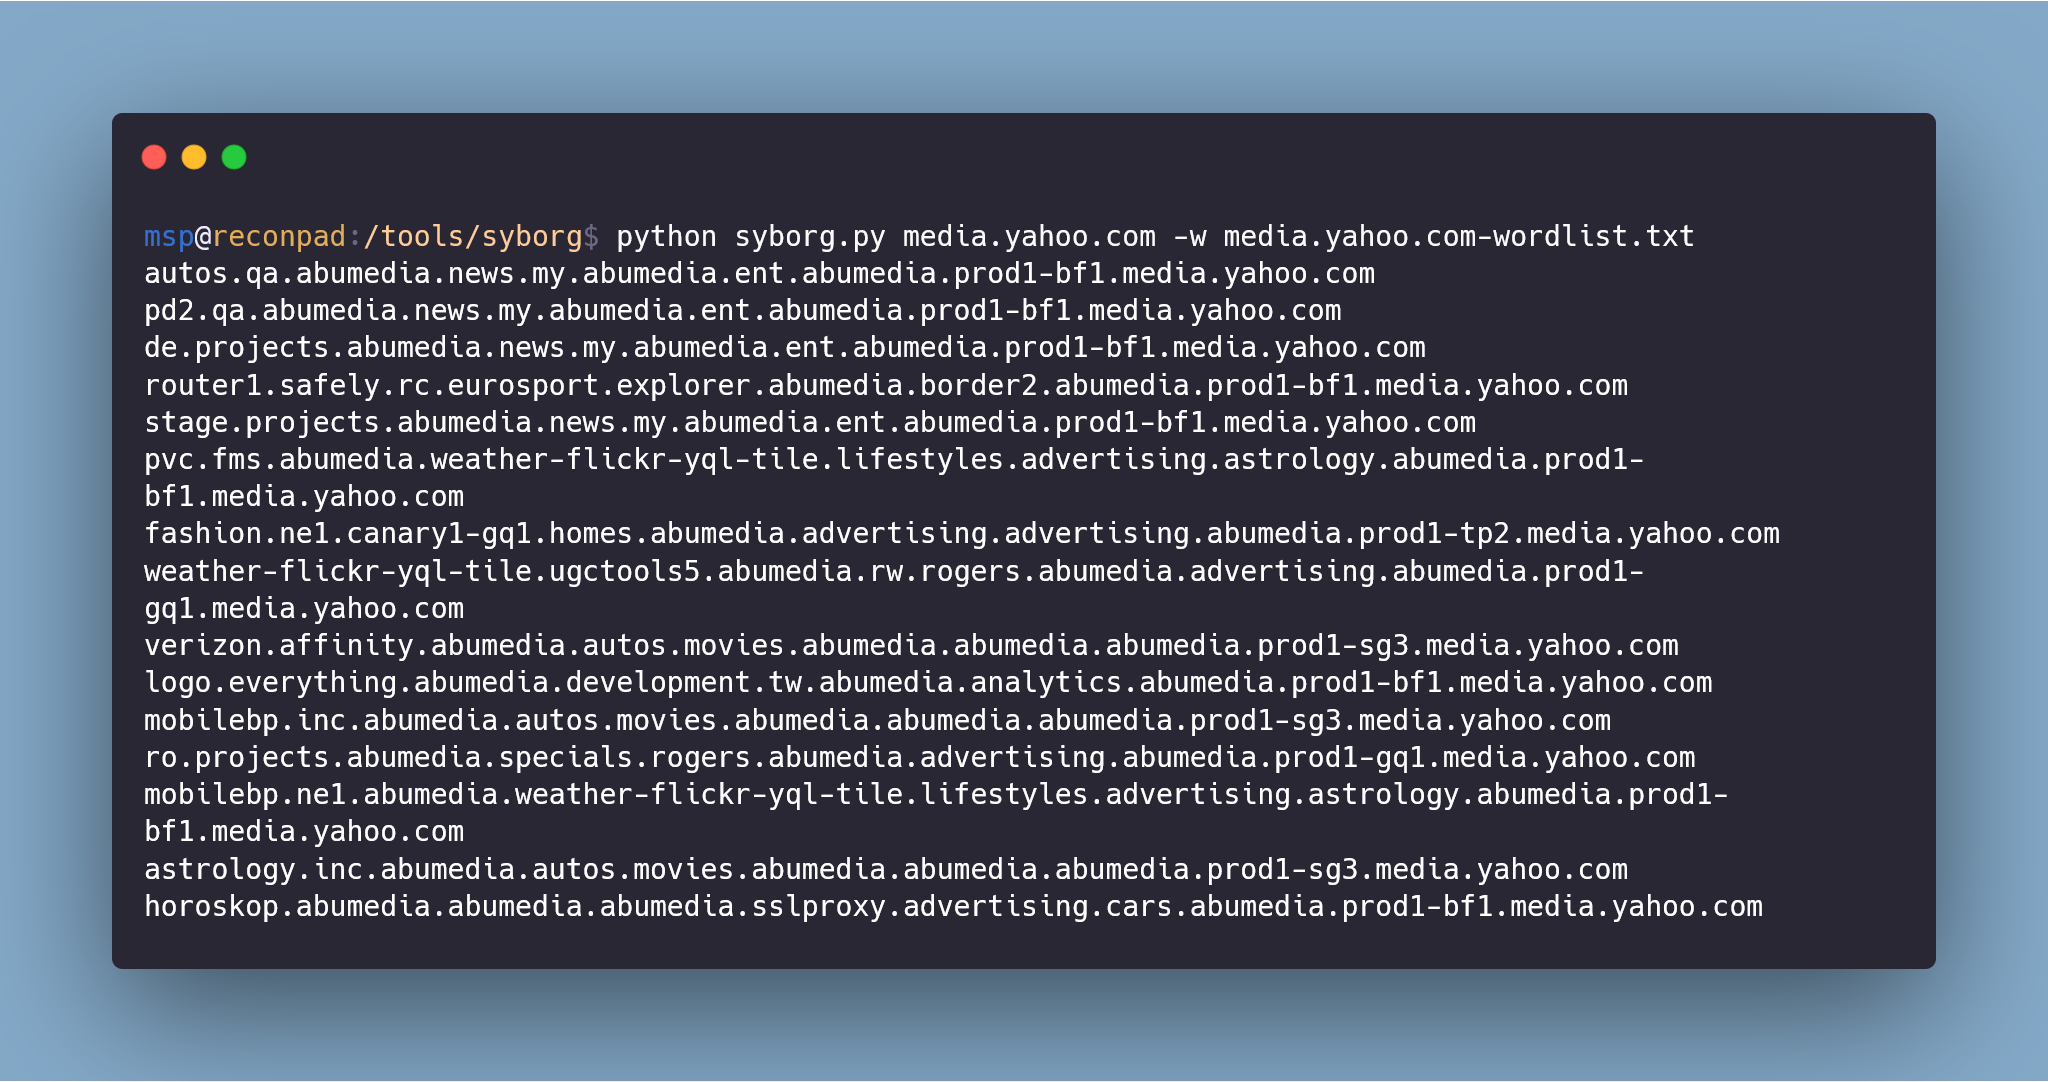 milindpurswani/syborg
Recursive DNS Subdomain Enumerator with dead-end avoidance system (BETA)
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.