
hermes-osint
 expert21/hermes-osint
Hermes — an ephemeral, Docker-powered OSINT framework for testing, tinkering, and secure investigative automation.
dns-subdomain-enumerationeducationemail-harvesting+6
42
expert21/hermes-osintHermes — an ephemeral, Docker-powered OSINT framework for testing, tinkering, and secure investigative automation.
 xssdoctor/vhostawesome
Concurrent virtual host scanner that brute-forces subdomains across multiple IPs on common web ports, filtering results by status codes and content…
 reddyyz/urlbrute
Directory/Subdomain scanner developed in GoLang.
 rapiddns/rapiddns-cli
A powerful command-line interface for interacting with the [RapidDNS API](https://rapiddns.io/help/api). This tool allows you to perform DNS…
 rxerium/bug-bounty-tools
A BASH Script to automate the installation of the most popular bug bounty tools
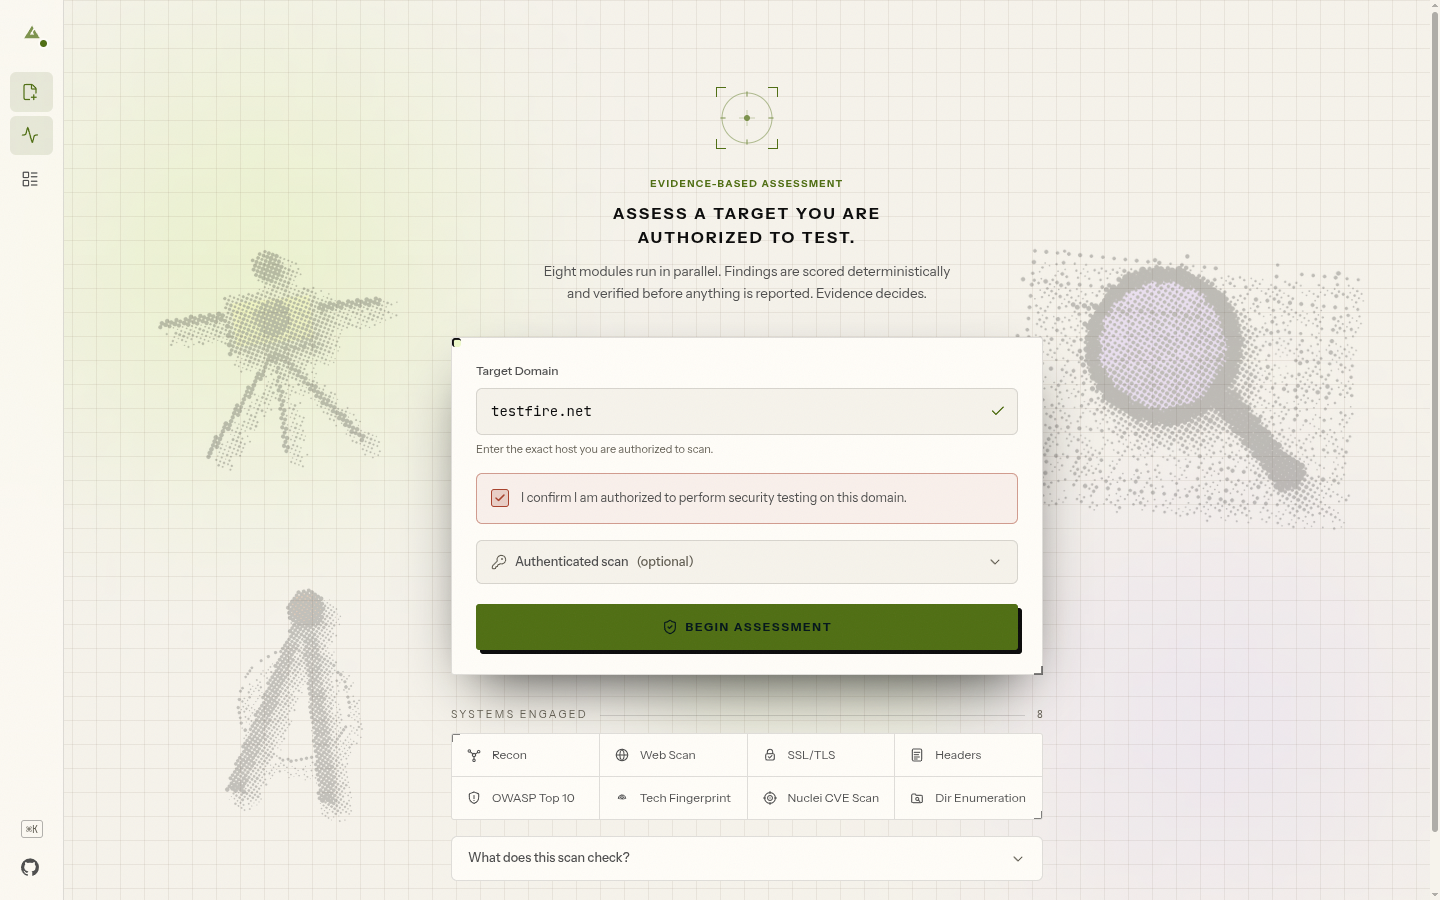 maverickaayush/onus
Locally-hosted, air-gapped VAPT platform that runs 8 parallel scanning modules, deterministically scores findings with CVSS v3.1, and generates PDF…
 hackplayers/iptodomain
This tool extract domains from IP address based in the information saved in virustotal.
 mrtdlgc/goodoldsearch-oss
Local static query builder for precise search across web engines, Shodan, crt.sh, and Wayback Machine. Supports Google dorks, filetype filters, date…
 pentestcore/cloudflare-bypass
Cloudflare Bypass tools | PentestCore
 aarocy/recon-scan
Recon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
 whitelisthackers/wosind
An OSINT tool for collecting public information.
 nccgroup/hostresolver
A Windows application to help out with external infrastructure scans.
 nu11secur1ty/complete-google-dorks
Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…
 d4rkcat/dnsbrute
Multi theaded DNS bruteforcing
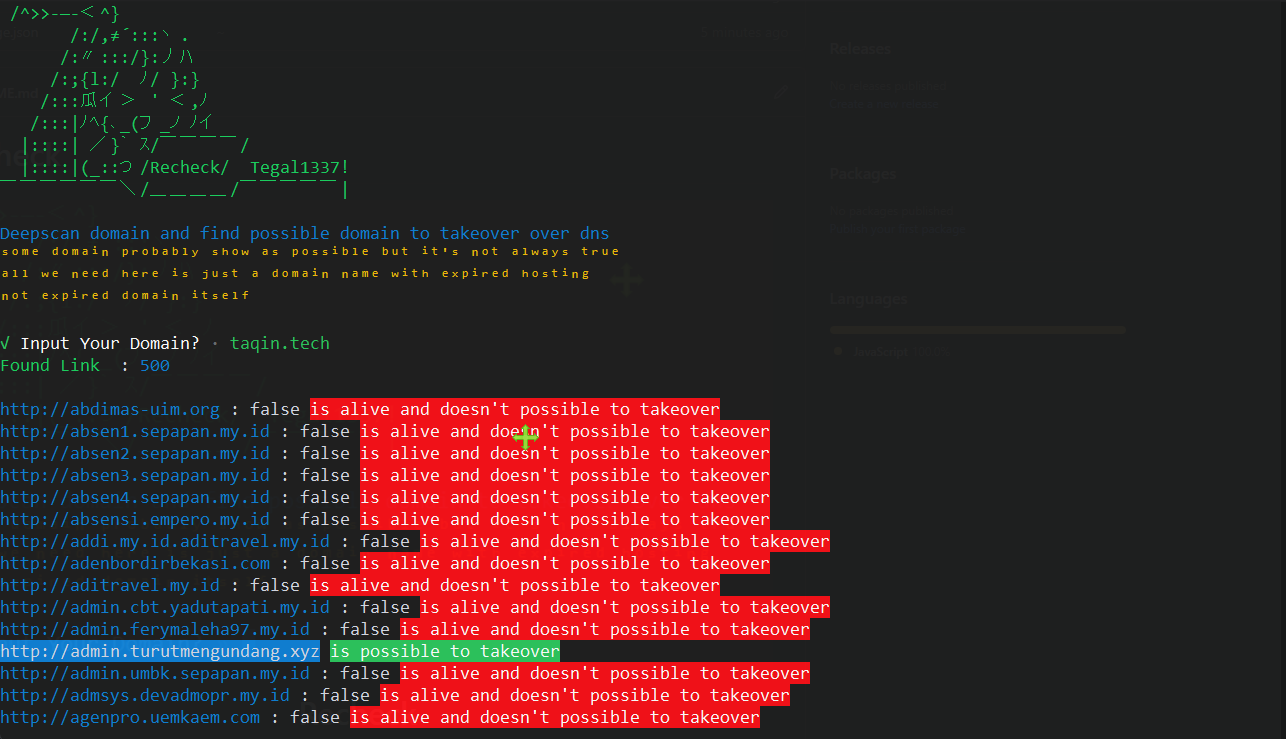 tegal1337/recheck
Deep scan domain and find all possible domain to takeover
 xpl0ited1/submonitor
Subdomain monitor with reporting capabilities to Slack, Discord and Telegram
 abaykan/getsubdomain
Get subdomain list and check whether they are active or not by each response code. Using API by c99.nl
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…